

csf
 armourbird/csf
ArmourBird CSF - Container Security Framework
api-securitycloud-infrastructure-securityconfiguration-auditing+4
44
armourbird/csfArmourBird CSF - Container Security Framework
 angelorc/vmsan
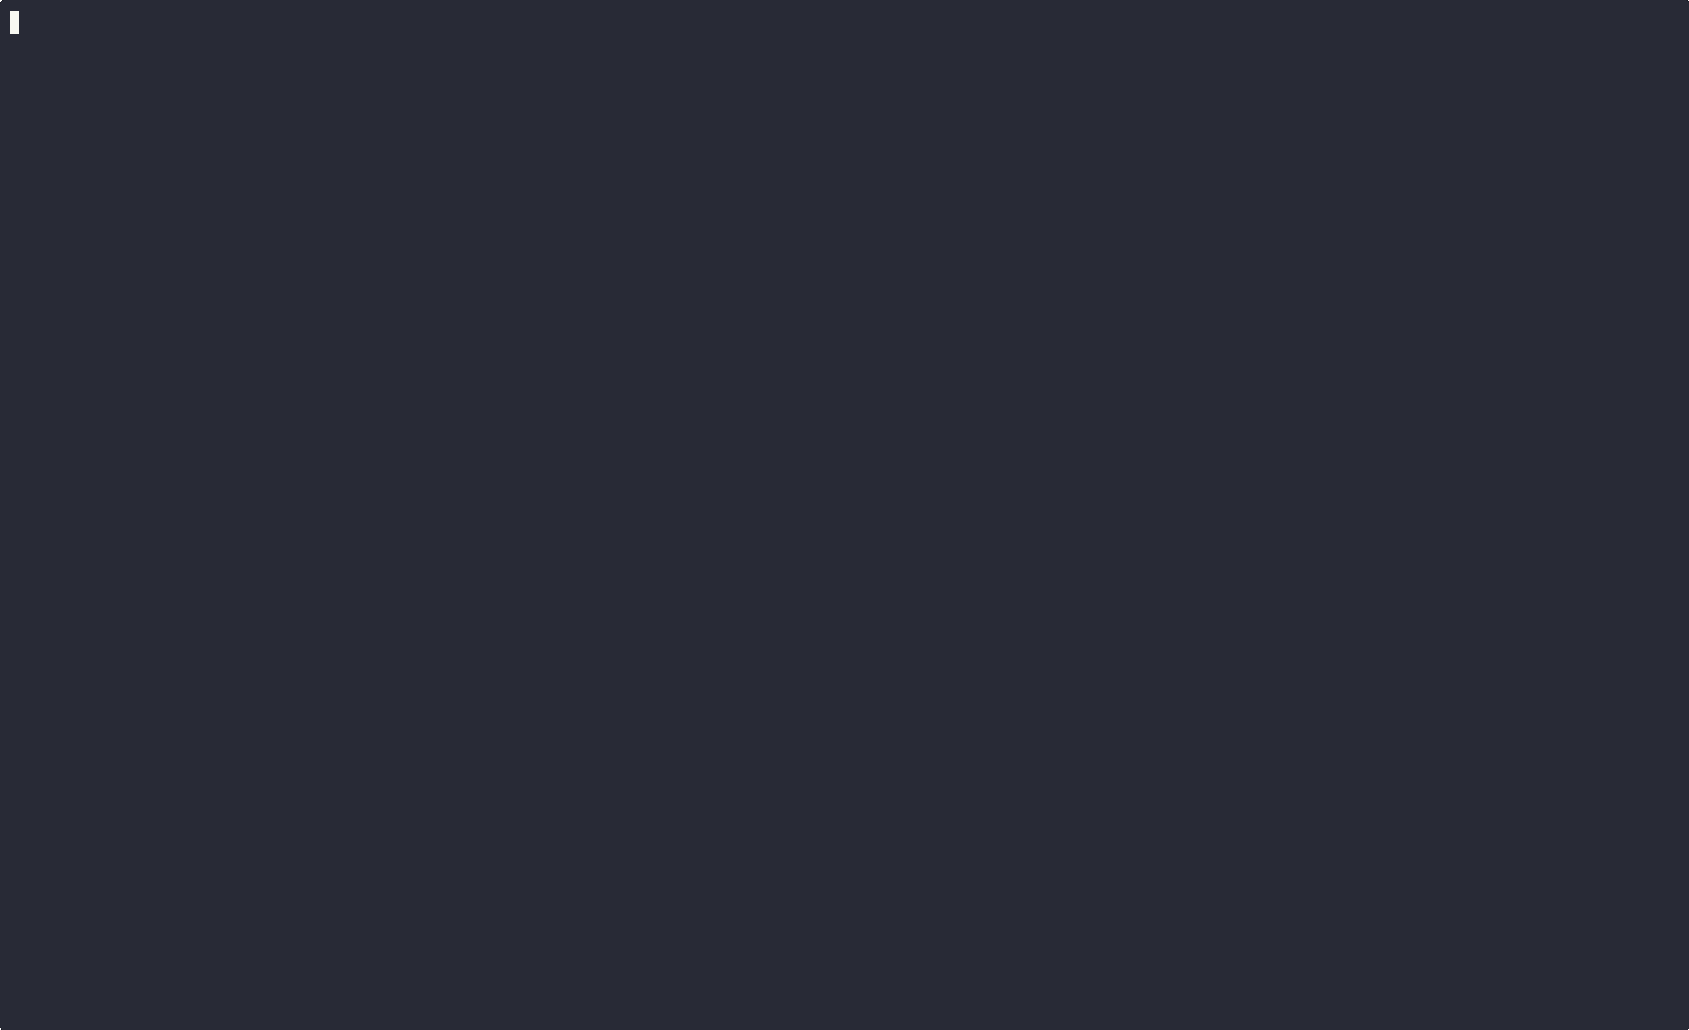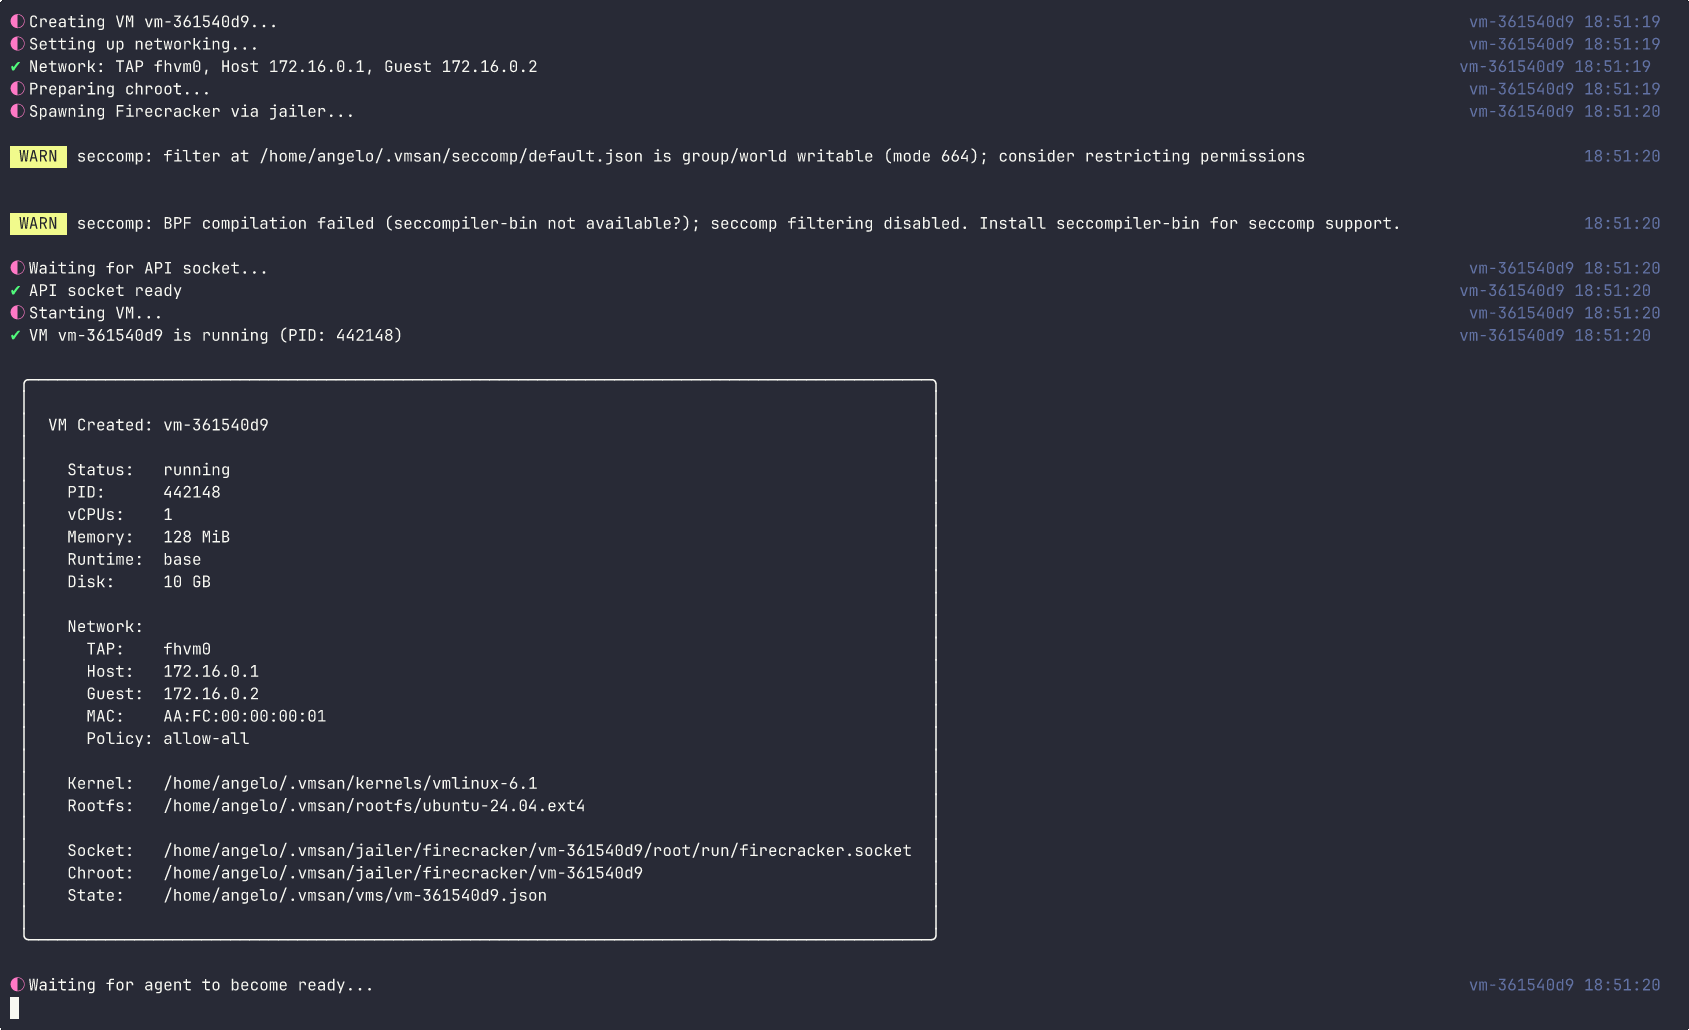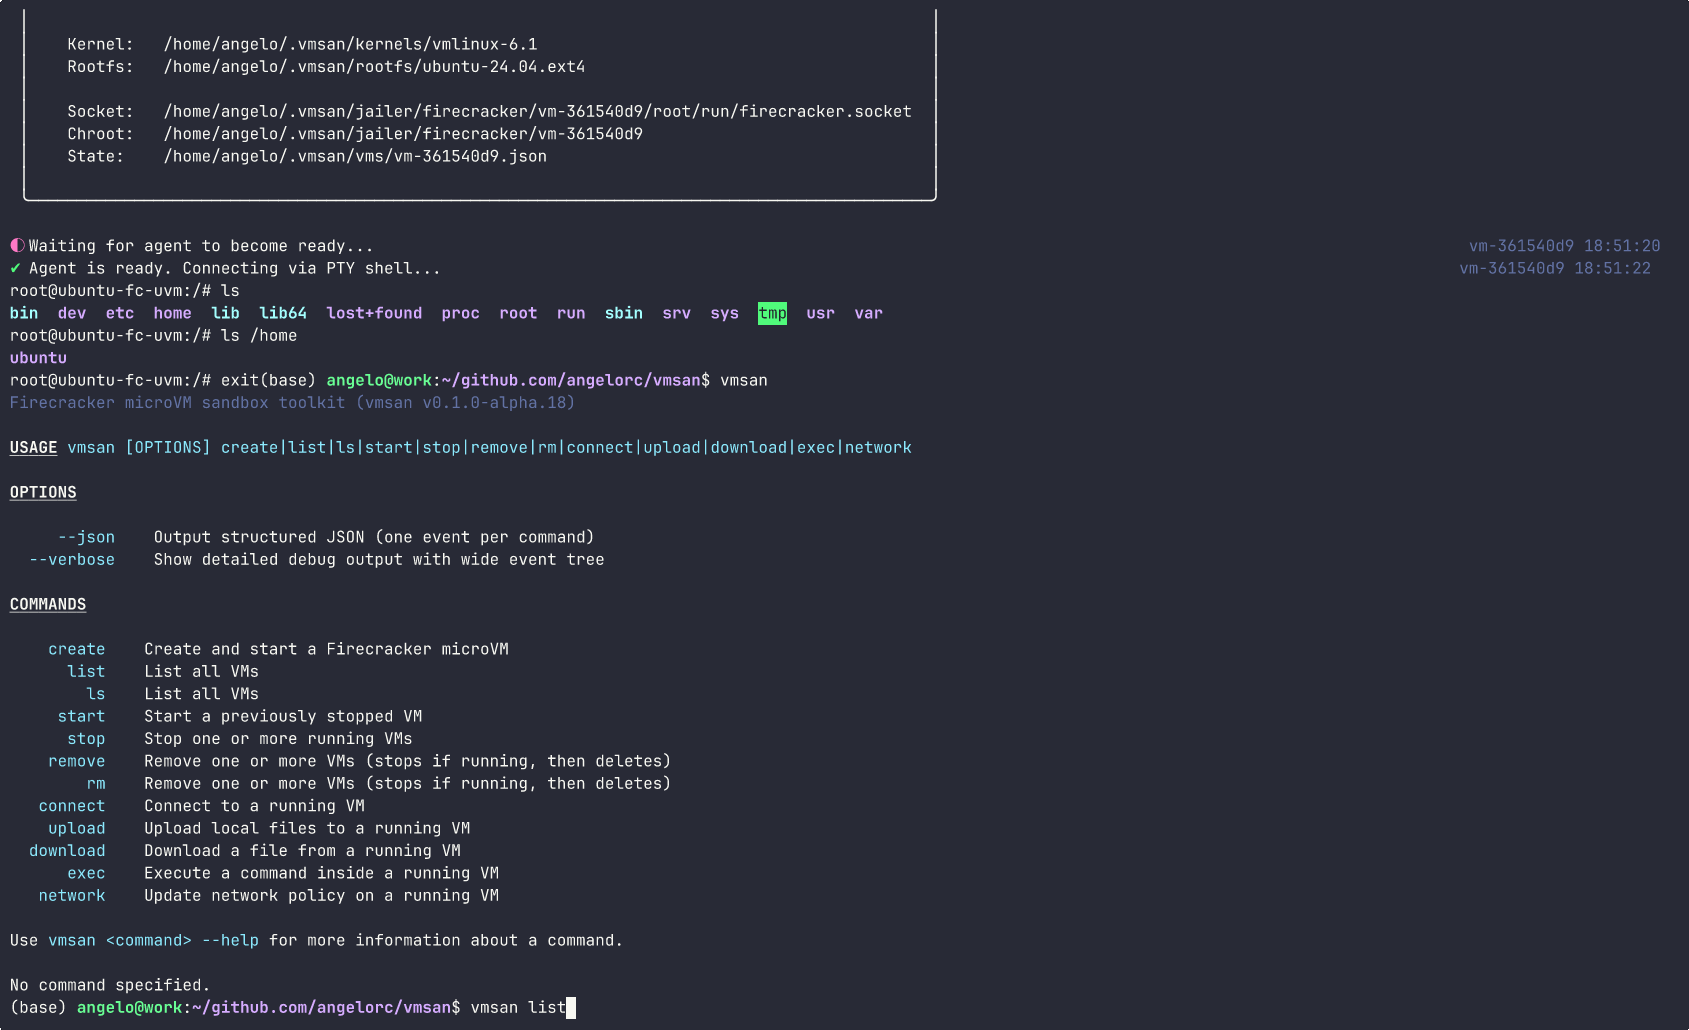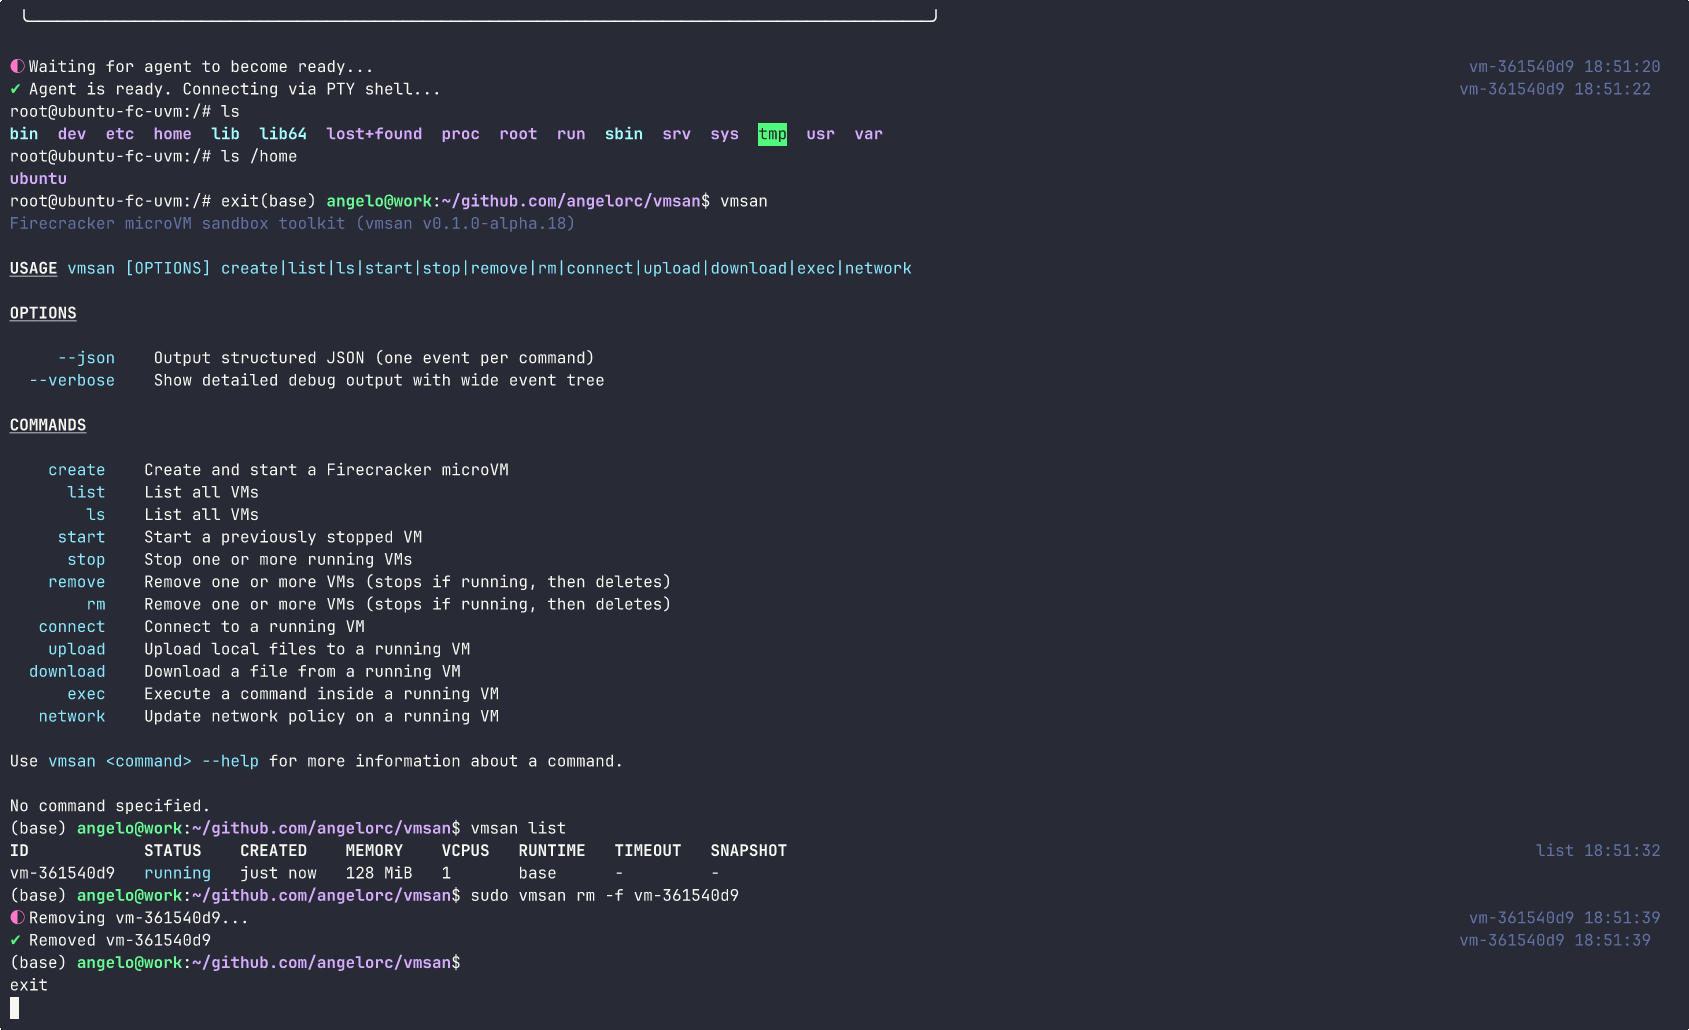
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 tdwyer/cve-2020-8559
This is a PoC exploit for CVE-2020-8559 Kubernetes Vulnerability
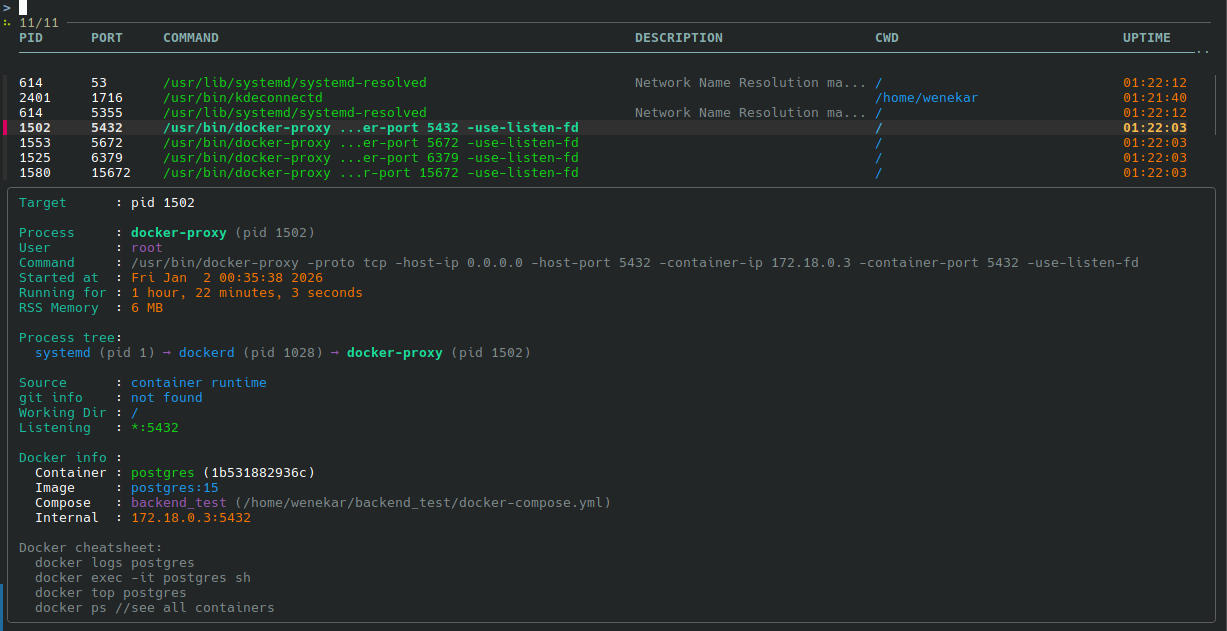 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
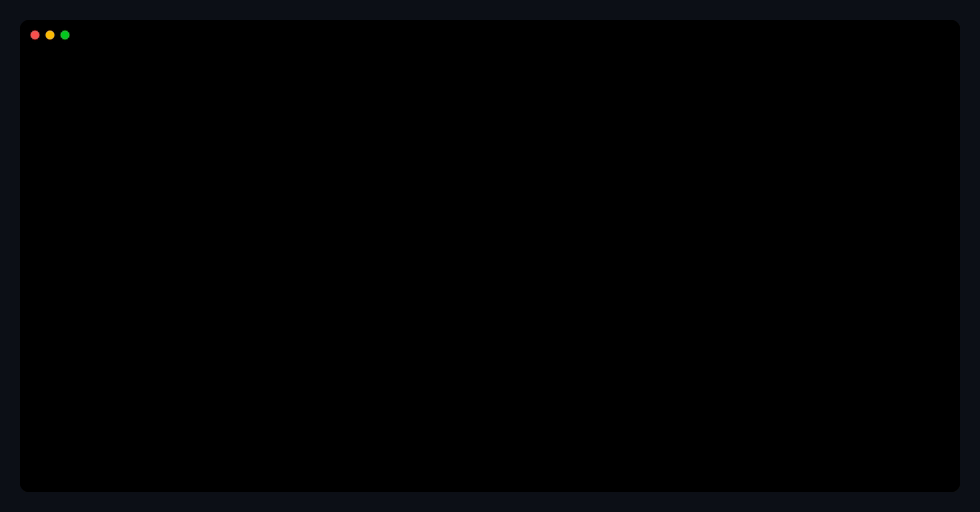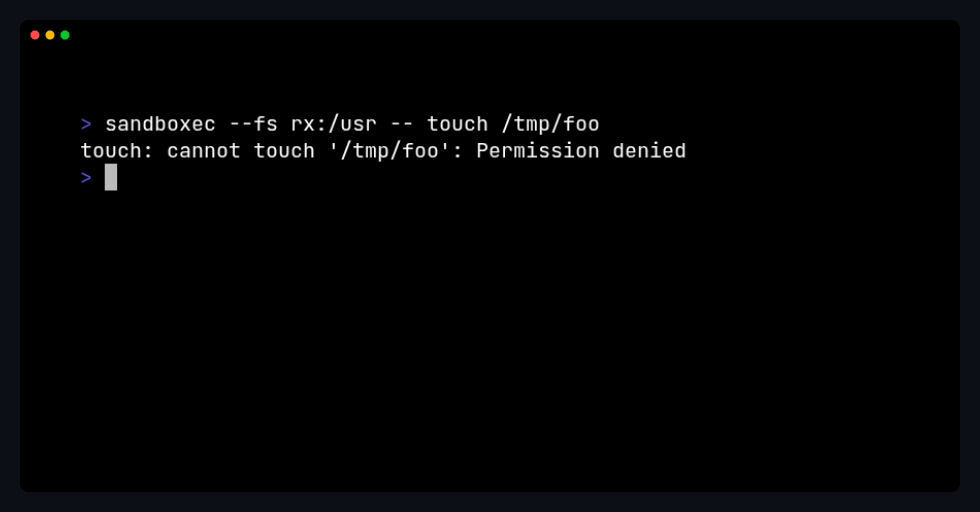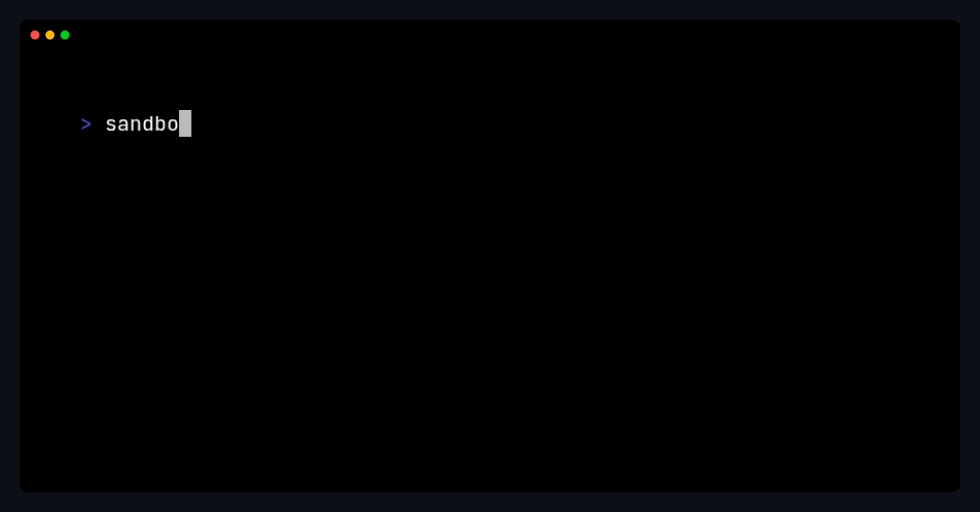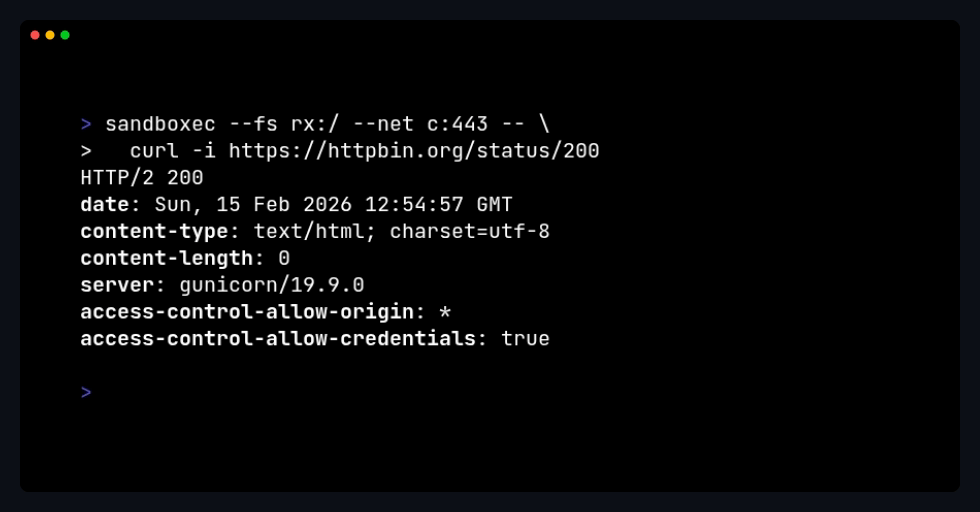 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 hmlio/vaas-cve-2014-0160
Vulnerability as a service: showcasing CVS-2014-0160, a.k.a. Heartbleed
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 jas502n/cve-2019-5736
Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.
 jq6l43d1/proxmox-lxc-docker-fix
Workaround for CVE-2025-52881: Fixes Docker/Podman breakage in Proxmox LXC containers caused by AppArmor incompatibility with runc 1.2.7+. Universal…
 mhaggis/package-inferno
A Public Package Scanner for The Community
 sixpacksecurity/cve-2021-40438
CVE-2021-40438 exploit PoC with Docker setup.
 mgrube/cve-2019-17633
Eclipse Che CSRF leading to RCE
 opsxcq/exploit-cve-2016-8016-25
McAfee Virus Scan for Linux multiple remote flaws (CVE 2016-8016, CVE 2016-8017, CVE 2016-8018, CVE 2016-8019, CVE 2016-8020, CVE 2016-8021, CVE…
 ashardev002/cve-2025-32463_chwoot
🔍 Demonstrate the CVE-2025-32463 privilege-escalation flaw in sudo's chroot feature with this minimal, reproducible proof of concept environment.