

limeyard
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
container-securitydevsecopsdns-subdomain-enumeration+8
1
clickswave/limeyardDeliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 snyk/leaky-vessels-dynamic-detector
eBPF-based runtime detector for container breakout vulnerabilities in runc and Docker, monitoring syscalls and Docker daemon calls to detect…
 flowerwitch/cve-2026-85706_docker_exp
Docker-based reproduction environment and PoC for CVE-2026-85706, demonstrating GitLab LFI bypass via .json suffix and trailing slash path tricks.
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 gravitational/cve-2018-1002105
Kubernetes cluster vulnerability scanner that detects CVE-2018-1002105 by testing for unauthenticated API access and privilege escalation via…
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 teyhouse/cve-2024-3094
K8S and Docker Vulnerability Check for CVE-2024-3094
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
 cado-security/varc
Volatile Artifact Collector collects a snapshot of volatile data from a system. It tells you what is happening on a system, and is of particular use…
 vmware-archive/lightwave
Identity services for traditional infrastructure, applications and containers.
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
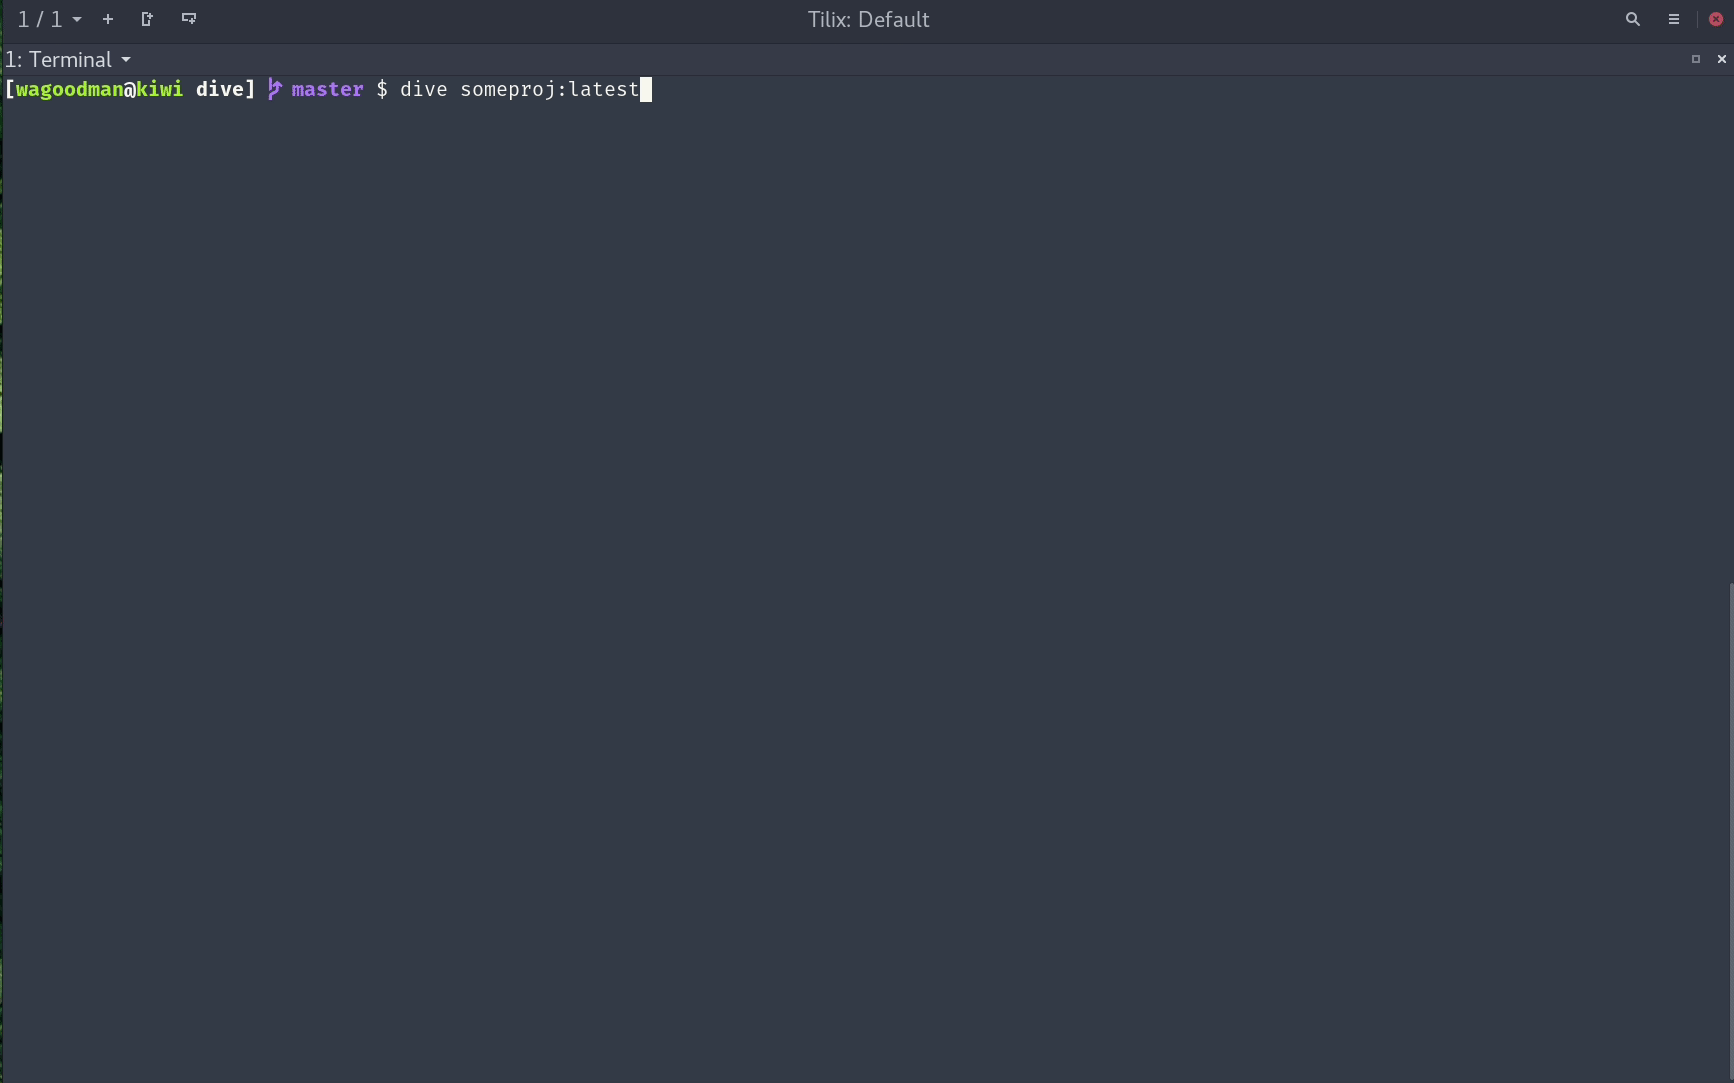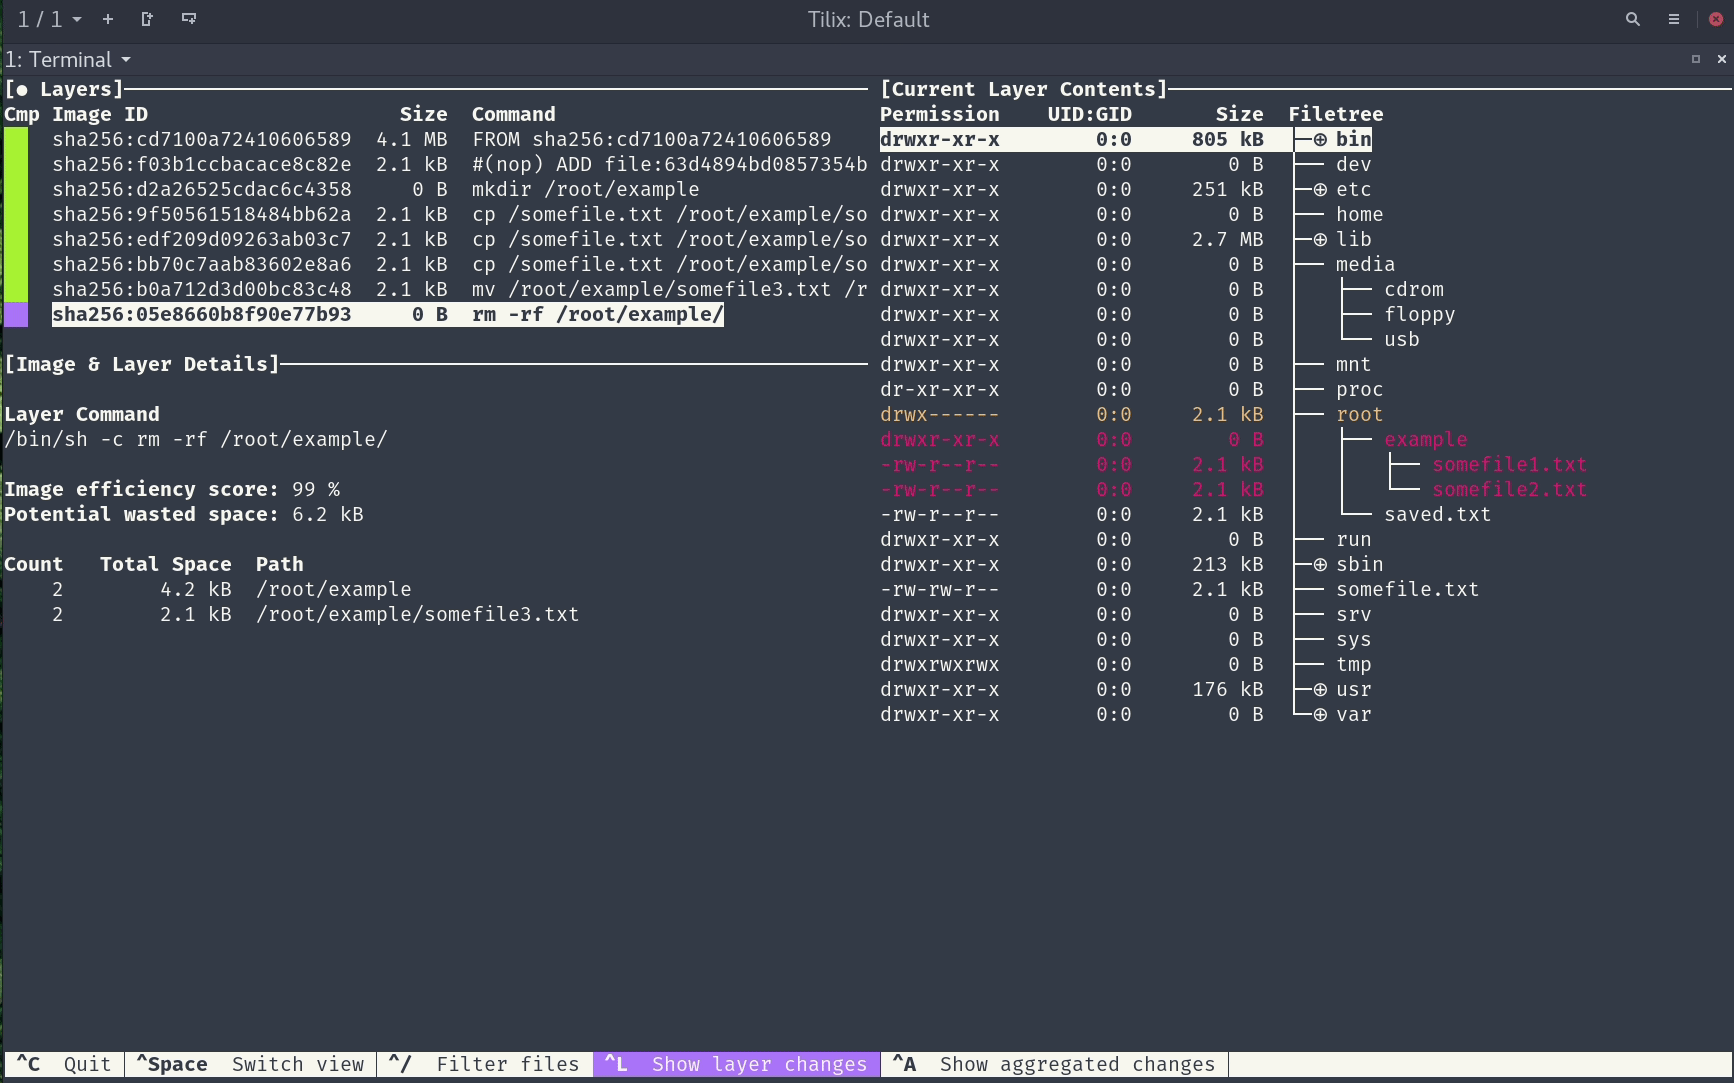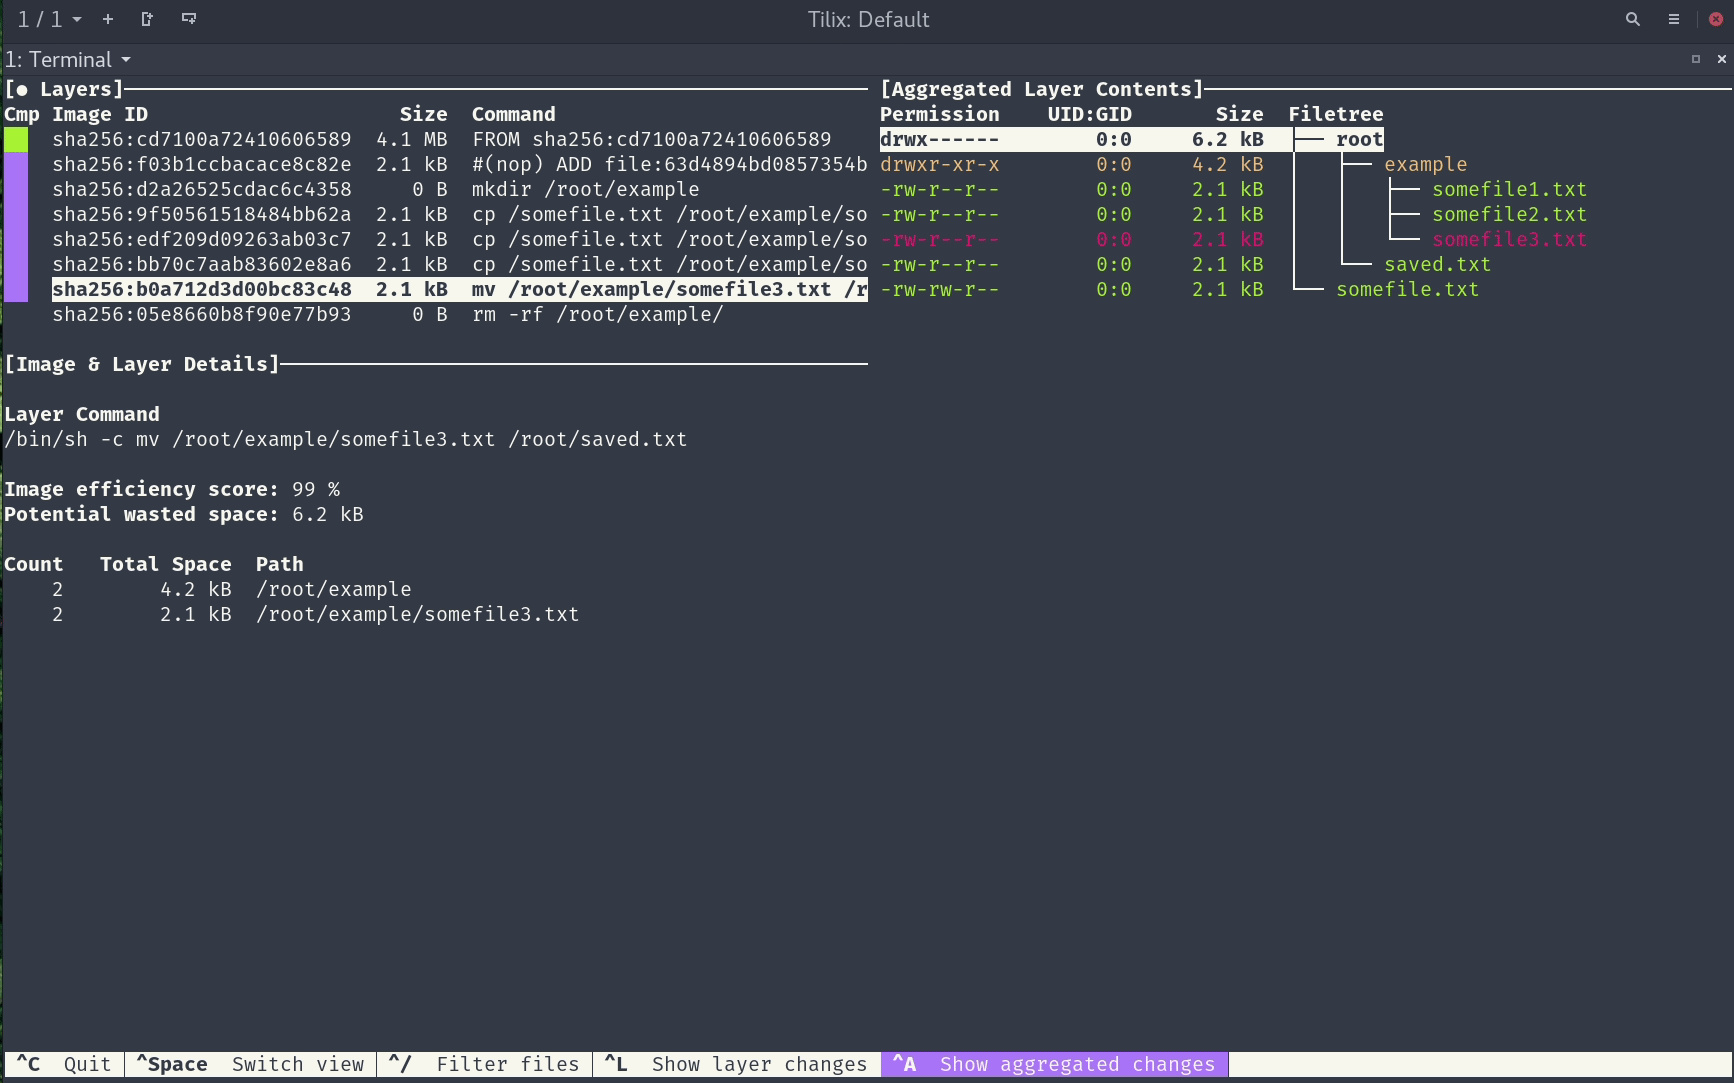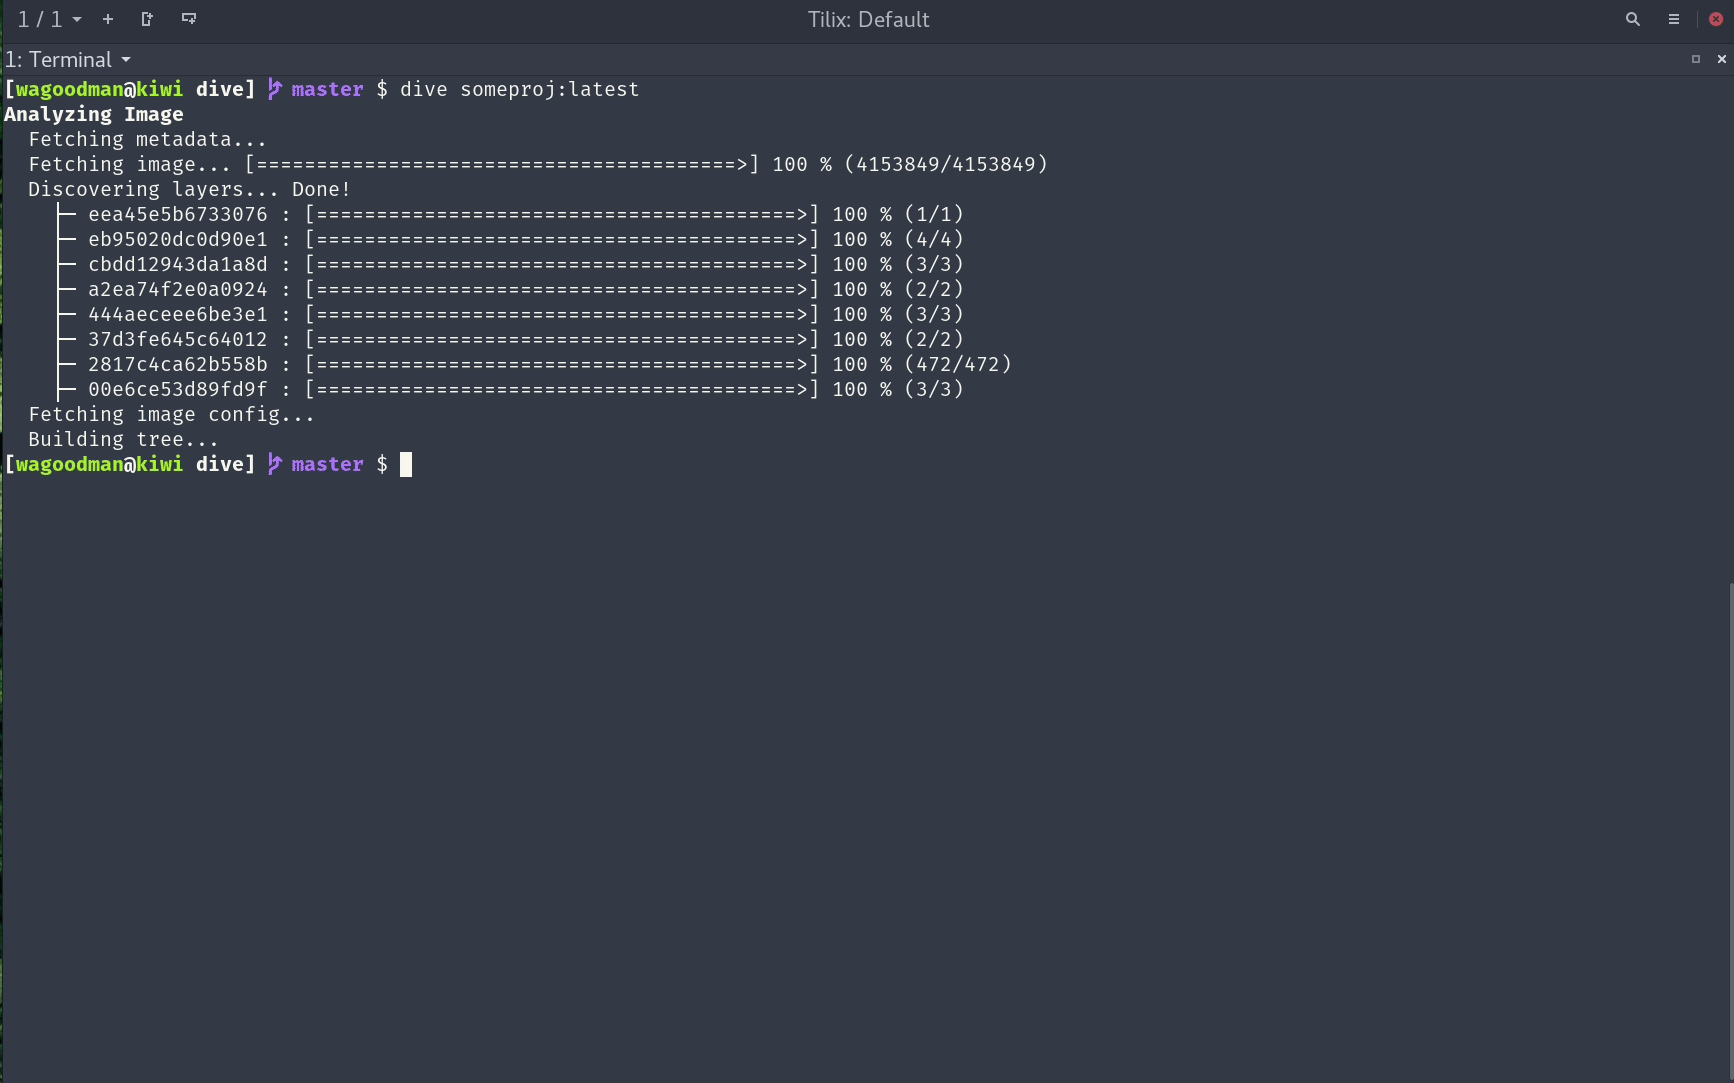 wagoodman/dive
A tool for exploring each layer in a docker image
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 smol-machines/smolvm
Branchable computing by using a portable, lightweight, self-contained virtual machine
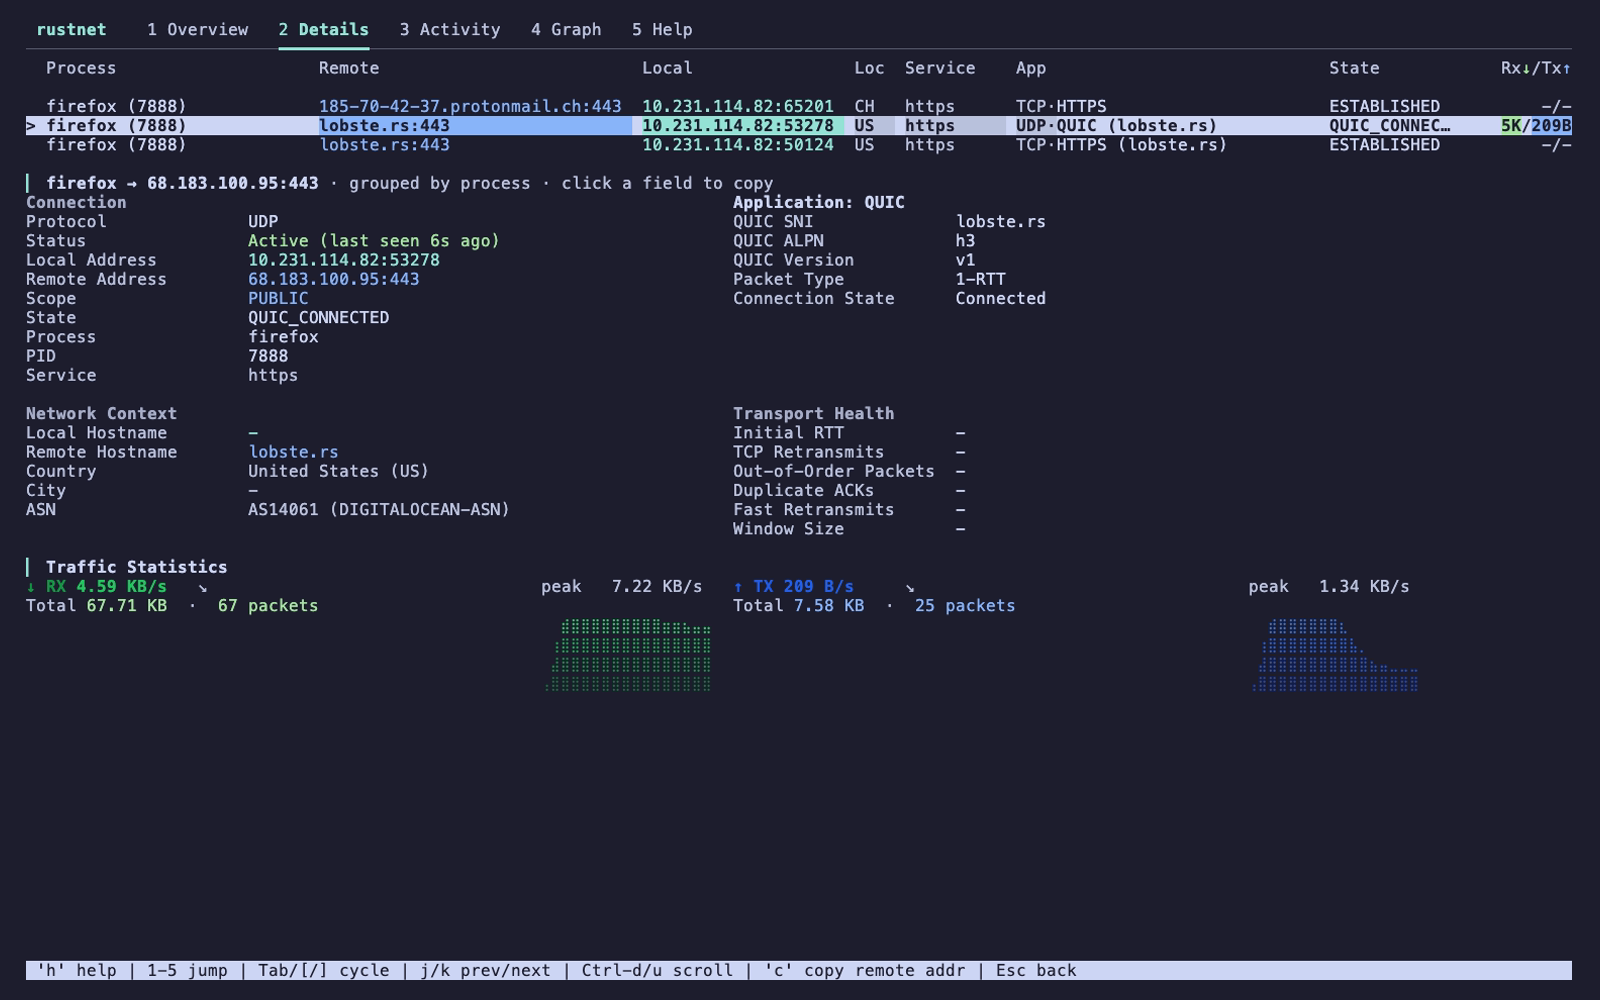 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.