

CVE-2024-1071-Docker
 matrexdz/cve-2024-1071-docker
Docker-based lab for practicing WordPress CVE-2024-1071 exploitation with automated PoC scripts and step-by-step setup instructions.
container-securityeducationexploitation+3
1
matrexdz/cve-2024-1071-dockerDocker-based lab for practicing WordPress CVE-2024-1071 exploitation with automated PoC scripts and step-by-step setup instructions.
 melmathari/dockercve-2024-835
Docker-based exploit for CVE-2024-835 vulnerability with automated deployment via docker-compose for penetration testing and security assessment.
 wshinkle/cve-2023-2982
Python exploit script for CVE-2023-2982, packaged in a Docker container for automated deployment and testing against vulnerable targets.
 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
 mafo-sec/mi-laboratorio-log4shell
Laboratorio automatizado Plug & Play en Docker para auditar y estudiar la vulnerabilidad Log4Shell (CVE-2021-44228)
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
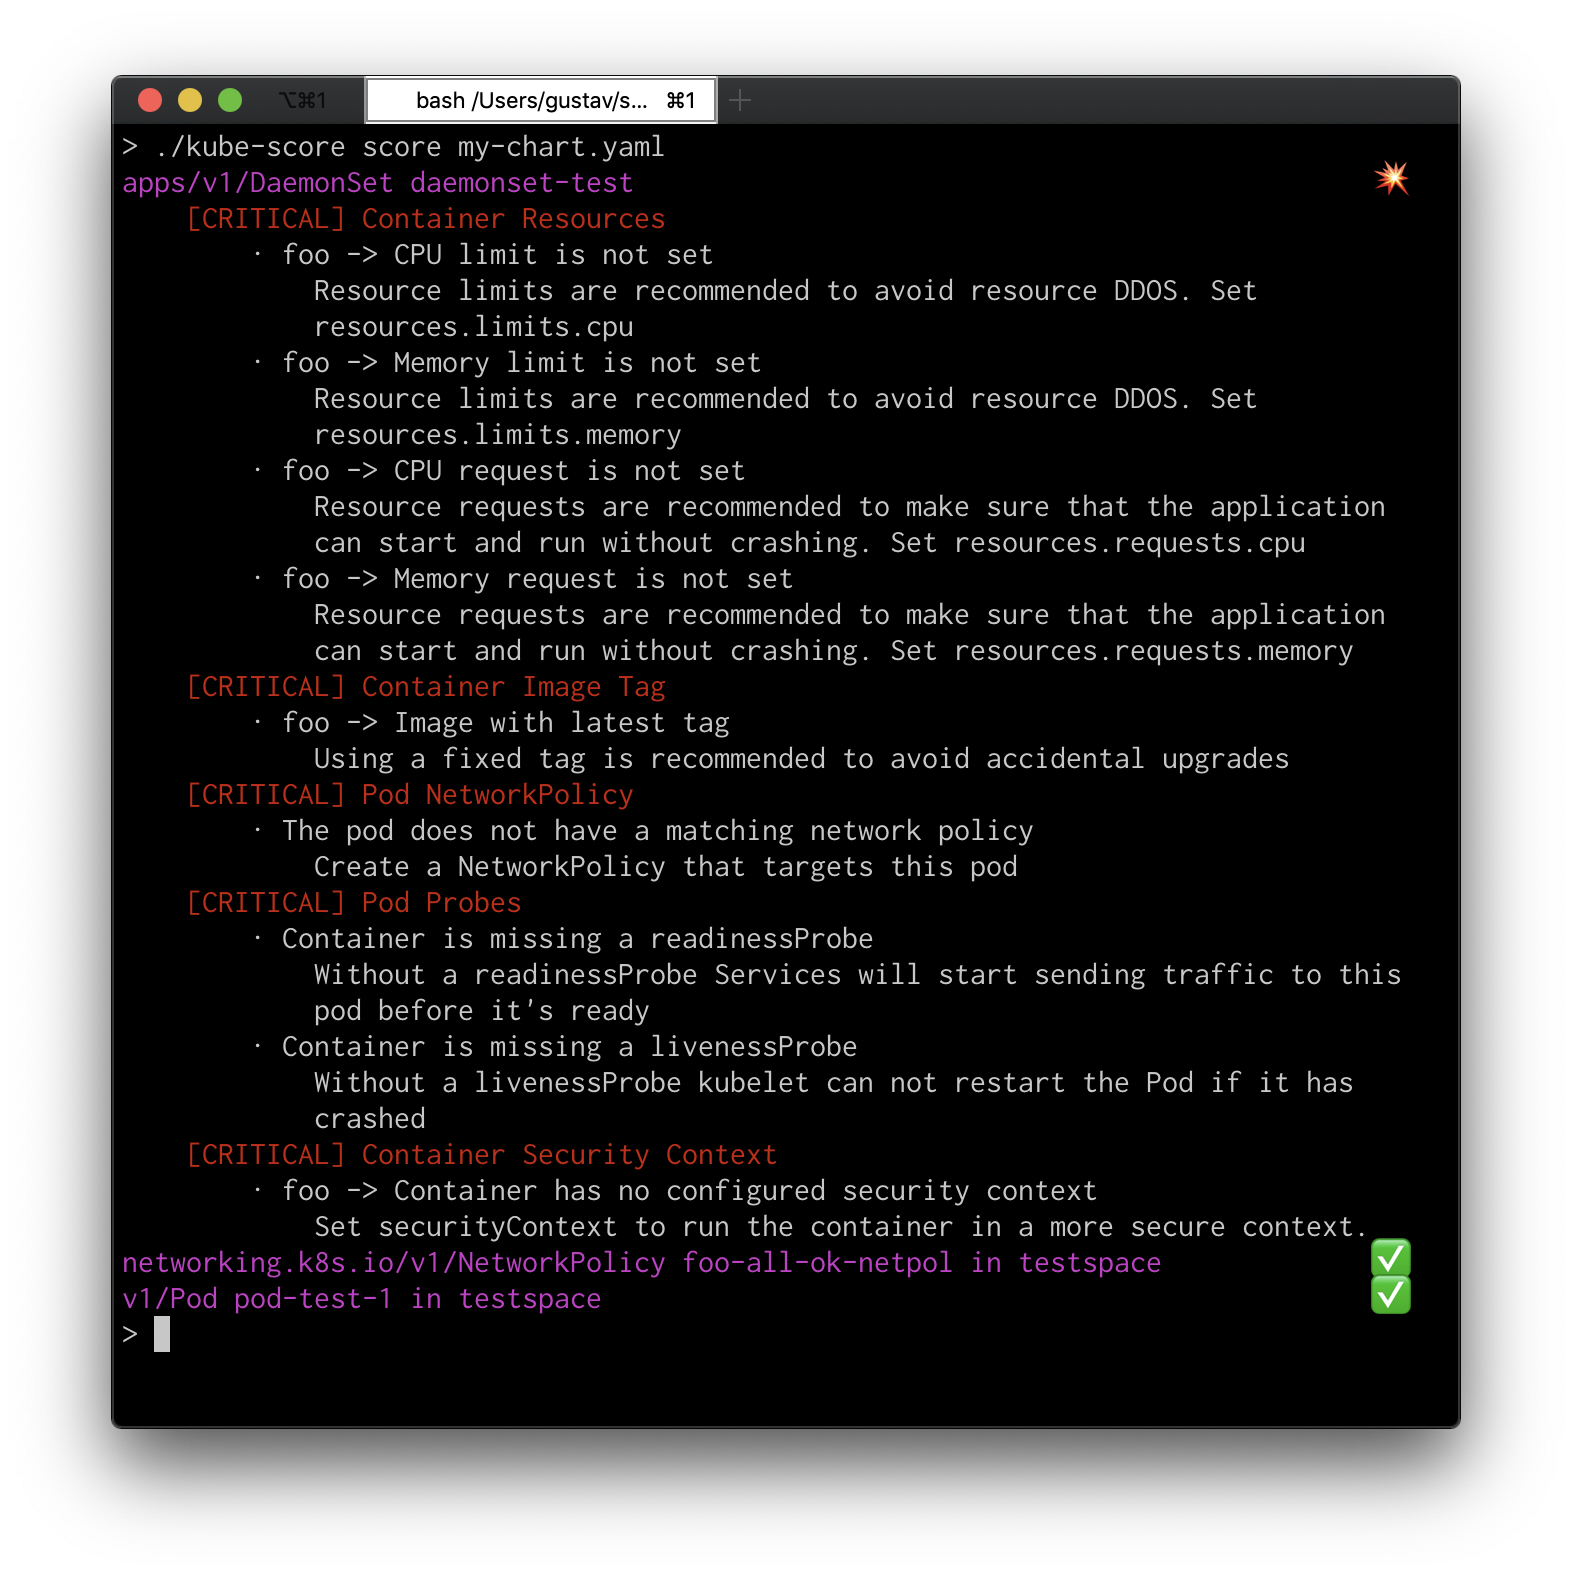 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
 quay/clair
Vulnerability Static Analysis for Containers
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 cartography-cncf/cartography
Pulls infrastructure assets and their relationships from 30+ cloud, identity, and SaaS platforms into a Neo4j graph for security queries and…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 aquasecurity/trivy-operator
Kubernetes-native security operator that automates vulnerability scanning, configuration auditing, secret detection, RBAC analysis, and compliance…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 owasp-dep-scan/dep-scan
Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 kunai-project/kunai
eBPF-based Linux security monitor and threat hunter providing chronologically ordered, container-aware events with on-host correlation for incident…
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.