
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
145 results
Wubes preview

Wubes

GitHubnccgroup/wubes

Qubes containerization on Windows

container-securitydefensive-toolssecurity-virtualization
1285 years ago
HoneyWire preview

HoneyWire

GitHubandreicscs/honeywire

Open-source deception platform that turns any Linux machine into a high-signal canary. Deploy tripwire sensors on files, ports, and network services…
container-securitydevsecopsincident-response+3
1022 months ago
vibebox preview

vibebox

GitHubrobcholz/vibebox

Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
ai-securitycontainer-securitydevsecops+3
1868 months ago
jailer preview

jailer

GitHubgen0sec/jailer

Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
cloud-securitycontainer-securitydefensive-tools+1
5822 days ago
log4j2_vul_local_scanner preview

log4j2_vul_local_scanner

GitHublijiejie/log4j2_vul_local_scanner

Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
code-analysiscontainer-securitydevsecops+3
854 years ago
ingressNightmare-CVE-2025-1974-exps preview

ingressNightmare-CVE-2025-1974-exps

GitHubesonhugh/ingressnightmare-cve-2025-1974-exps

IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…
cloud-securitycontainer-securityexploitation+5
971 year ago
kube-beacon preview

kube-beacon

GitHubchen-keinan/kube-beacon

Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
cloud-securityconfiguration-auditingcontainer-security+2
691 year ago
vpod preview

vpod

GitHubcapsulerun/vpod

Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
ai-securitycontainer-securitydefensive-tools+3
651 month ago
sysflow preview

sysflow

GitHubsysflow-telemetry/sysflow

Cloud-native system telemetry pipeline that collects, processes, and exports system call events into a compact object-relational format for…
cloud-securitycontainer-securitythreat-intelligence
462 years ago
sandboxec preview

sandboxec

GitHubsandboxec/sandboxec

A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
container-securitydefensive-toolsscripting-automation+2
698 months ago
kube-knark preview

kube-knark

GitHubchen-keinan/kube-knark

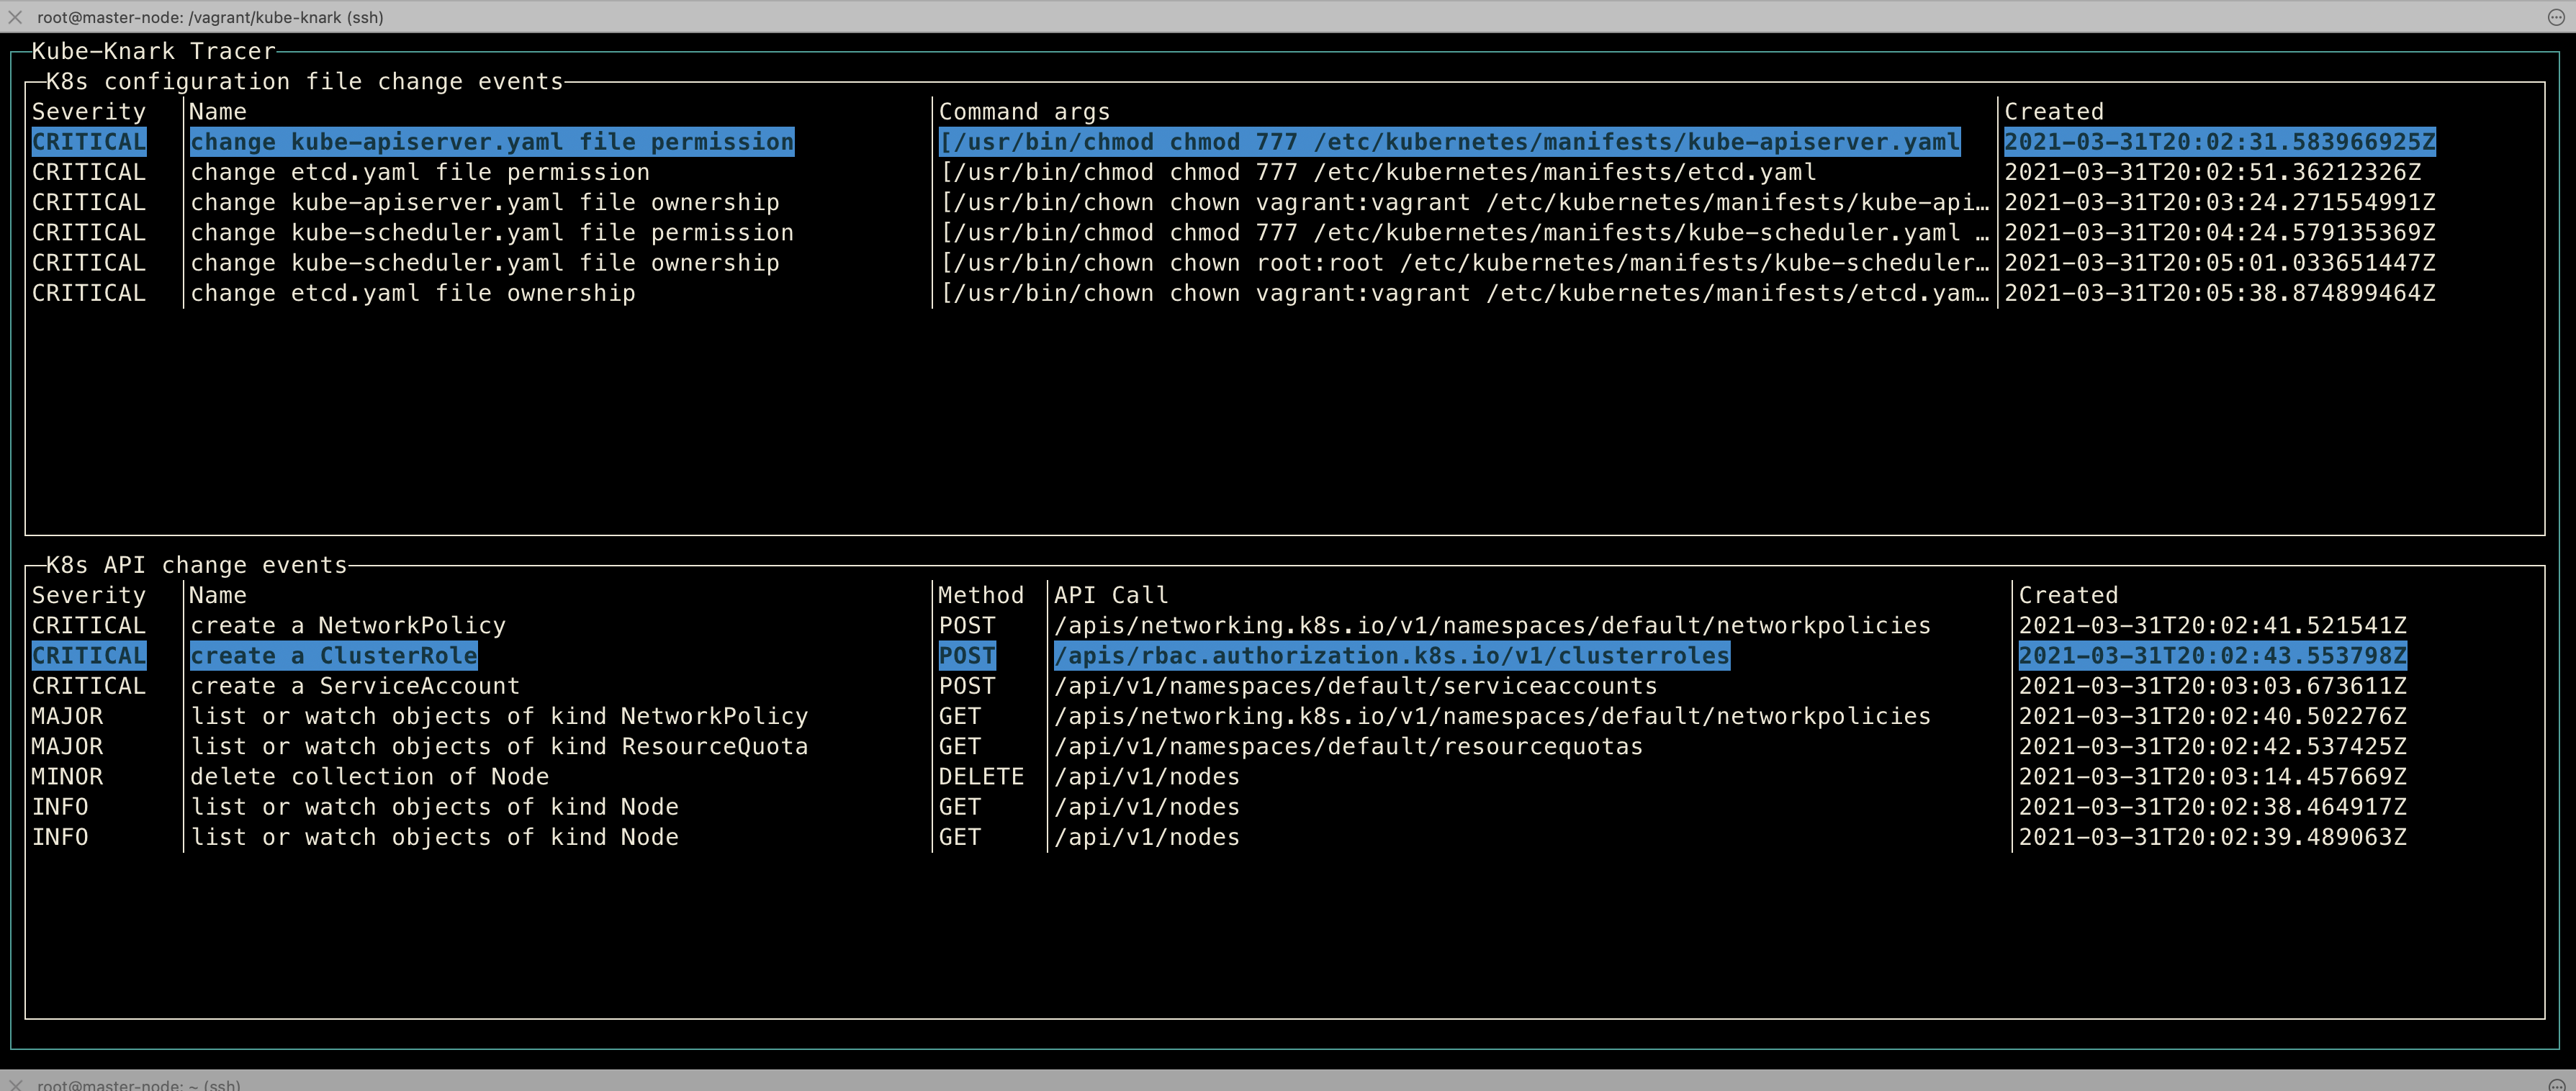
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
cloud-securitycontainer-securityintrusion-detection+1
364 years ago
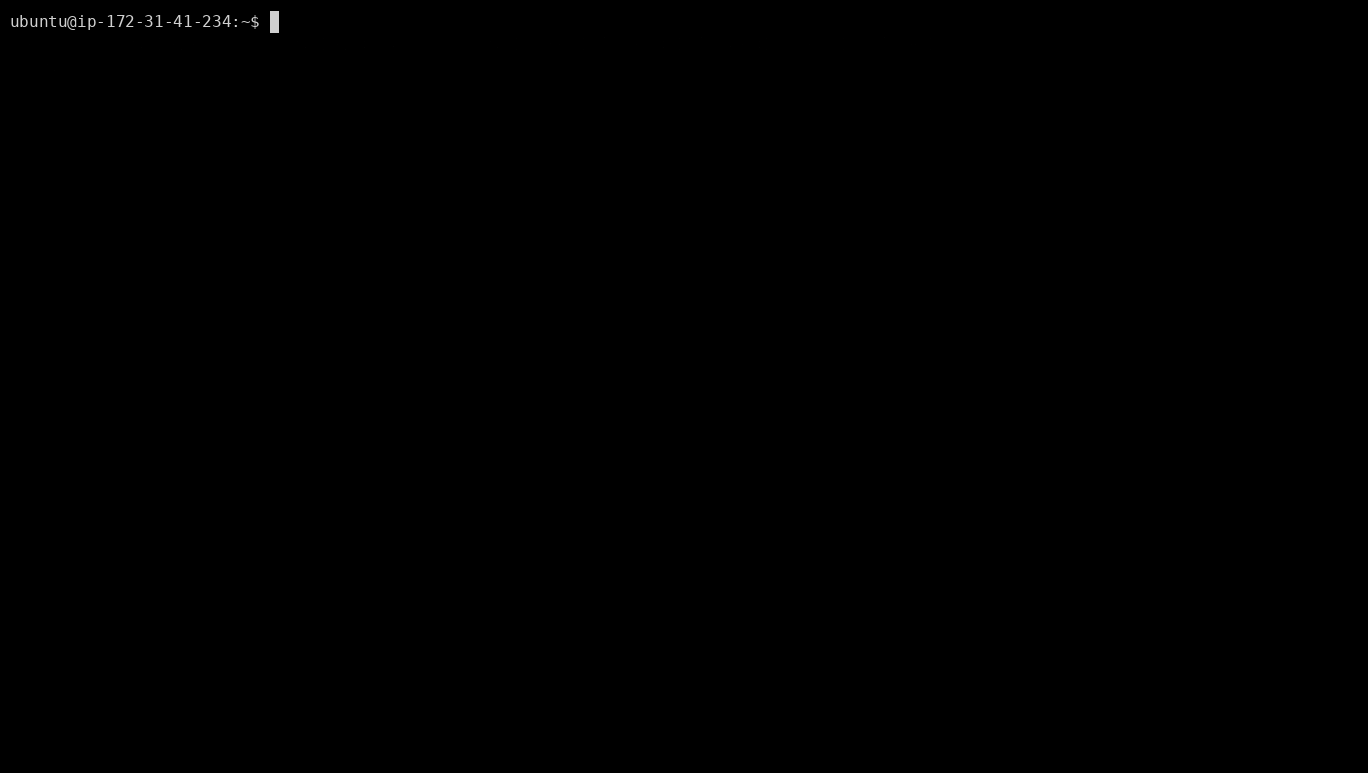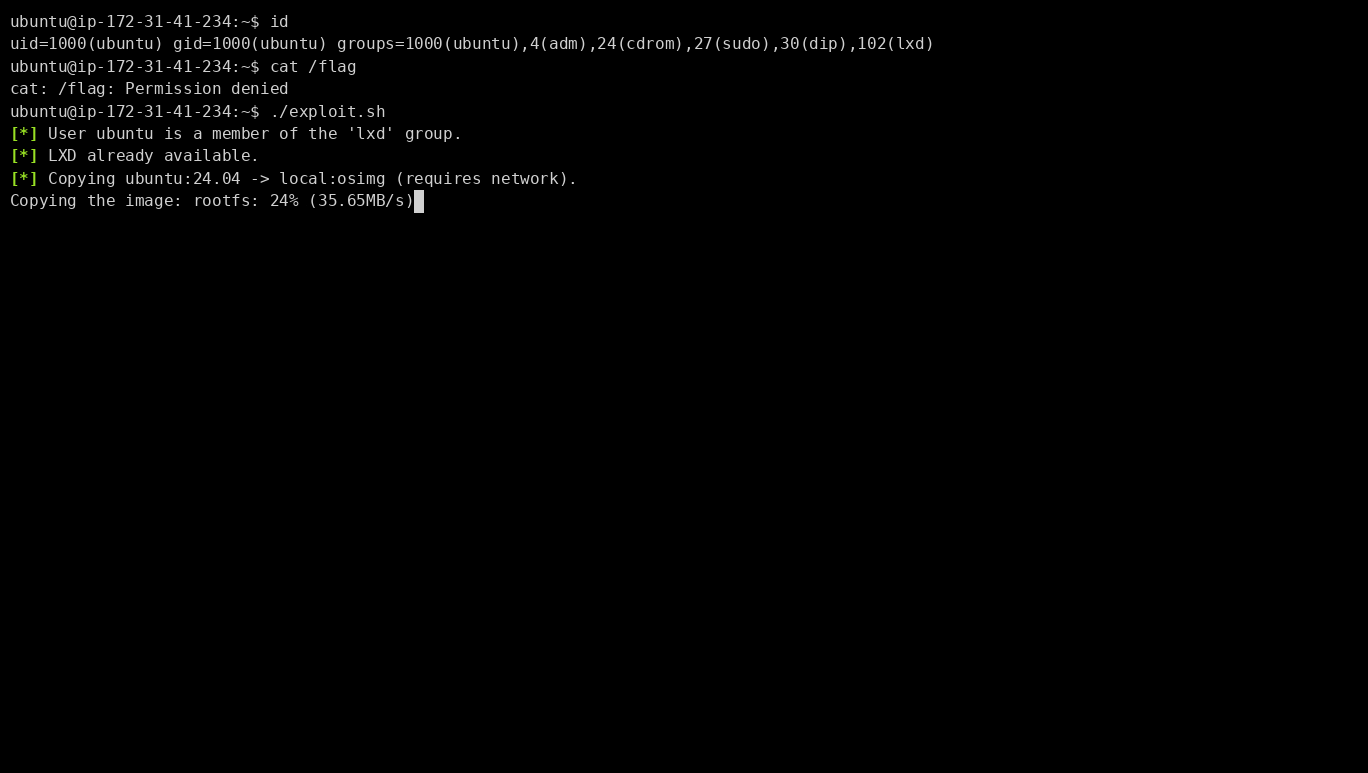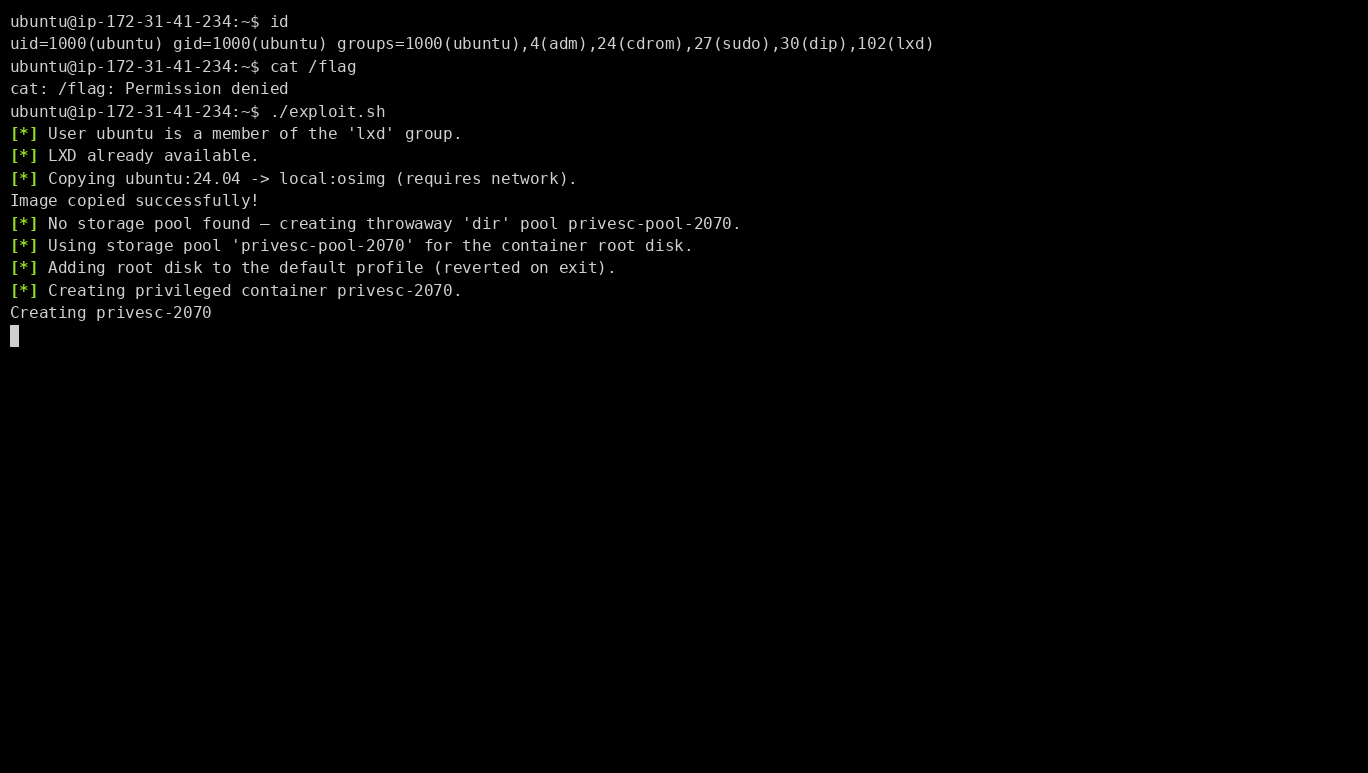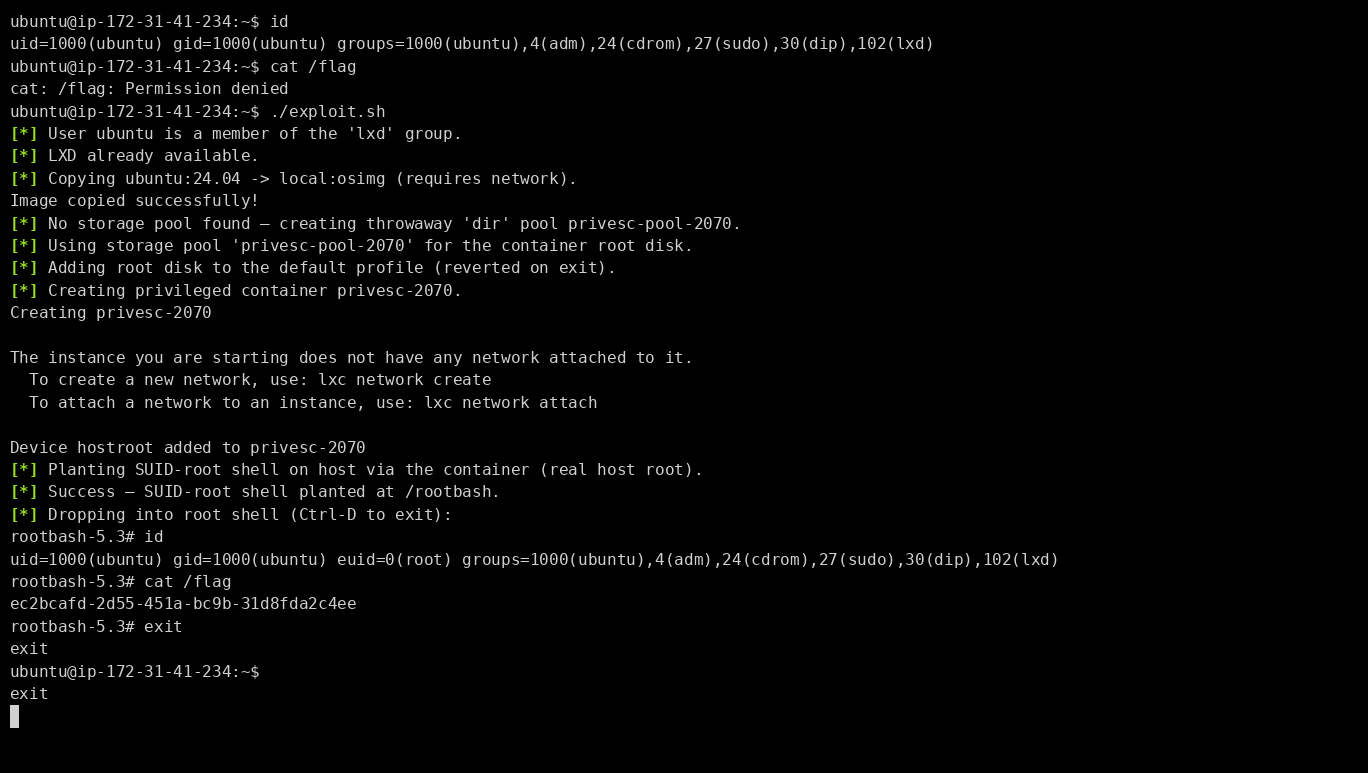
CVE-2026-31431-Copy-Fail---Vulnerability-Detection-Script preview

CVE-2026-31431-Copy-Fail---Vulnerability-Detection-Script

GitHubliamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script

Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
cloud-infrastructure-securityconfiguration-auditingcontainer-security+5
275 months ago
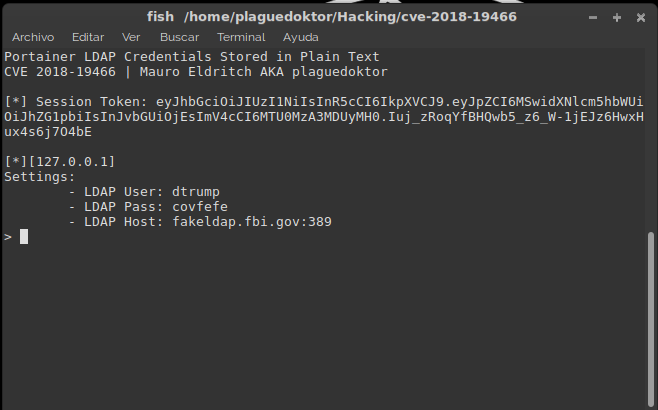
lxd-group-privesc-report preview

lxd-group-privesc-report

GitHubstar-sg/lxd-group-privesc-report

Proof-of-concept and educational report demonstrating local privilege escalation to root via default LXD group membership on Ubuntu Server, with…
container-securityeducationexploitation+3
74 months ago
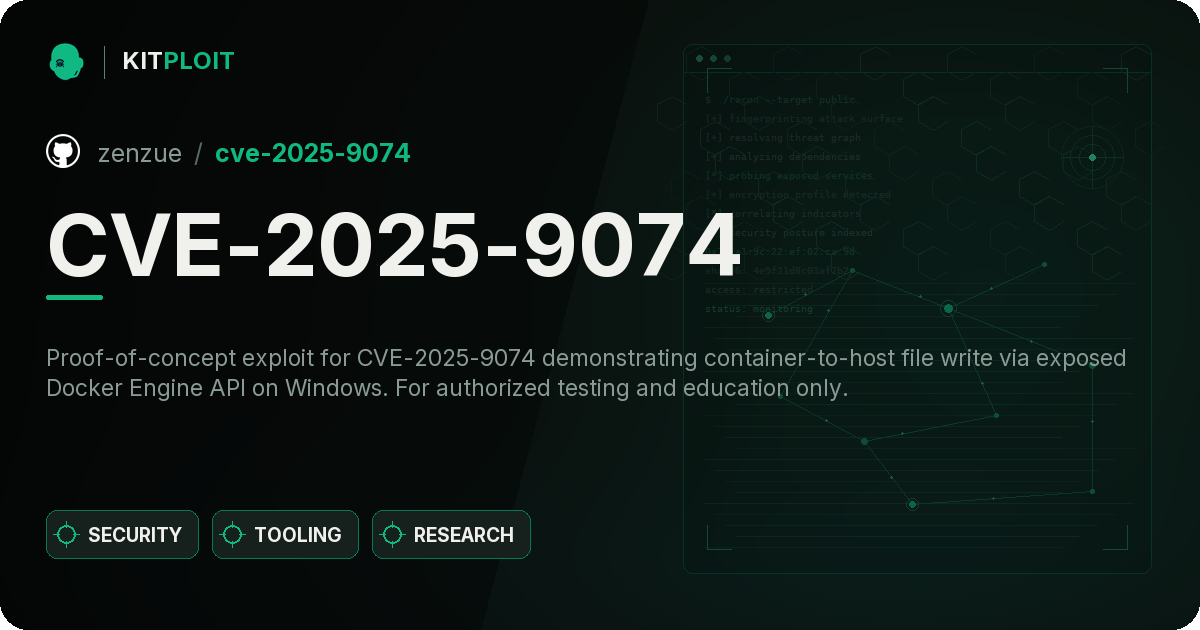
lempo preview

lempo

GitHubmauroeldritch/lempo

LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
authenticationcontainer-securityexploitation+2
116 years ago
CVE-2025-9074 preview

CVE-2025-9074

GitHubzenzue/cve-2025-9074

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
cloud-securitycontainer-escapecontainer-security+6
101 year ago
ai-kubernetes-helm-chart-security preview

ai-kubernetes-helm-chart-security

GitHubsorami-consulting-au/ai-kubernetes-helm-chart-security

Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.

ai-securitycloud-securityconfiguration-auditing+5
21 month ago
CVE-2026-44848-PoC preview

CVE-2026-44848-PoC

GitHubboreas37/cve-2026-44848-poc

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
api-security-testingauthentication-authorizationcontainer-security+3
22 months ago
Dirty-Frag-Research-CVE-2026-43284- preview

Dirty-Frag-Research-CVE-2026-43284-

GitHubnabhan-mohy/dirty-frag-research-cve-2026-43284-

Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…

container-securityincident-responseintrusion-detection+2
3 months ago
Previous123…9Next