
CVE-2024-3400-PoC
 certushack/cve-2024-3400-poc
Sets up a Docker-based Palo Alto firewall test environment and provides an exploit script to test CVE-2024-3400, enabling safe vulnerability…
container-securityexploitationnetwork-security+3
2
certushack/cve-2024-3400-pocSets up a Docker-based Palo Alto firewall test environment and provides an exploit script to test CVE-2024-3400, enabling safe vulnerability…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 johnatag/inf8602-cve-2020-8835
Educational kernel exploit implementation for CVE-2020-8835 with Docker-based testing environment to demonstrate BPF vulnerability exploitation and…
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 paloaltonetworks/can-ctr-escape-cve-2022-0492
Test whether a container environment is vulnerable to container escapes via CVE-2022-0492
 agppp/cve-2019-5736-poc
getshell test
 lhotari/log4shell-mitigation-tester
Test and validate Log4Shell (CVE-2021-44228) mitigation approaches with a sample vulnerable Log4j app, including JNDI exploitation, environment…
 mochizuki875/cve-2024-10220-githooks
CVE-2024-10220 Test repo
 loliverte/log4j-vulnerability
Étude technique et mise en œuvre d'un environnement de test pour la faille Apache Log4j (CVE-2021-44228). Contient un Proof of Concept (PoC)…
 dima2021/cve-2022-42889-text4shell
Docker-based lab environment to demonstrate and test the CVE-2022-42889 (Text4Shell) remote code execution vulnerability in Apache Commons Text.
 yym8538/cve-2026-20896
Proof-of-concept lab and Python/cURL scripts demonstrating CVE-2026-20896, an authentication bypass in official Gitea Docker images via the…
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 nanocoai/nanoclaw
A lightweight alternative to OpenClaw that runs in containers for security. Connects to WhatsApp, Telegram, Slack, Discord, Gmail and other messaging…
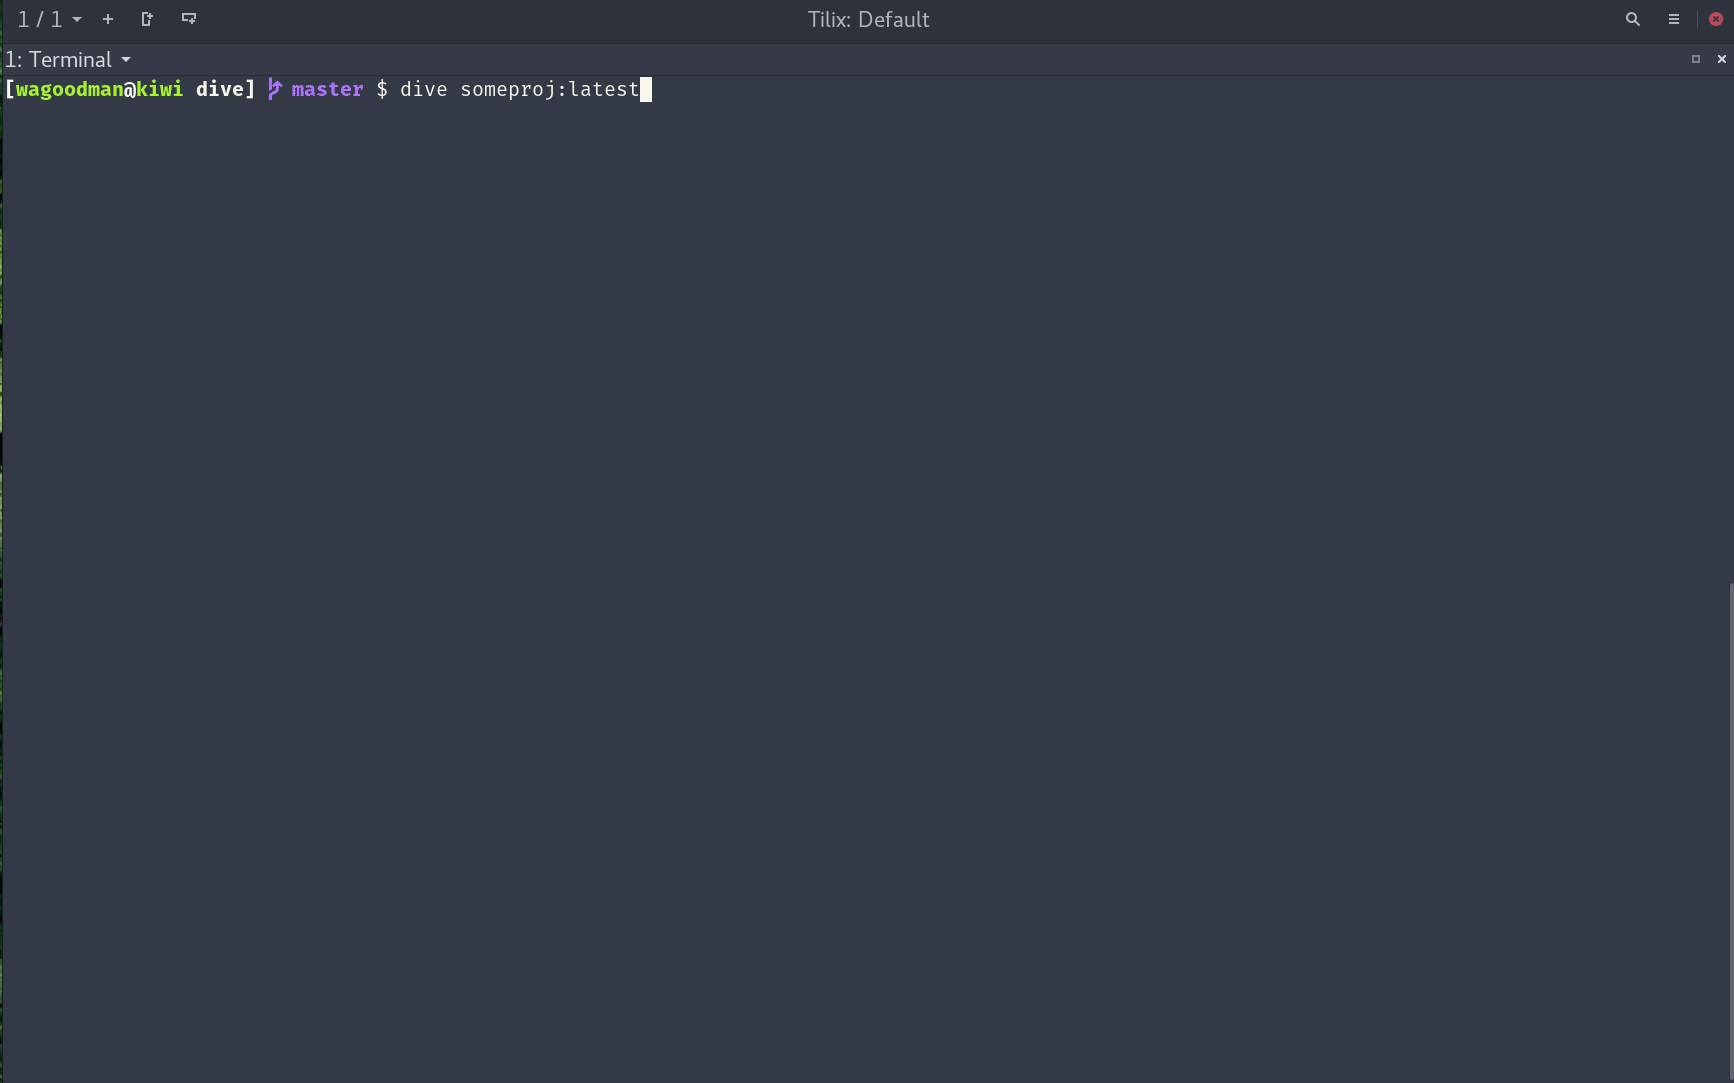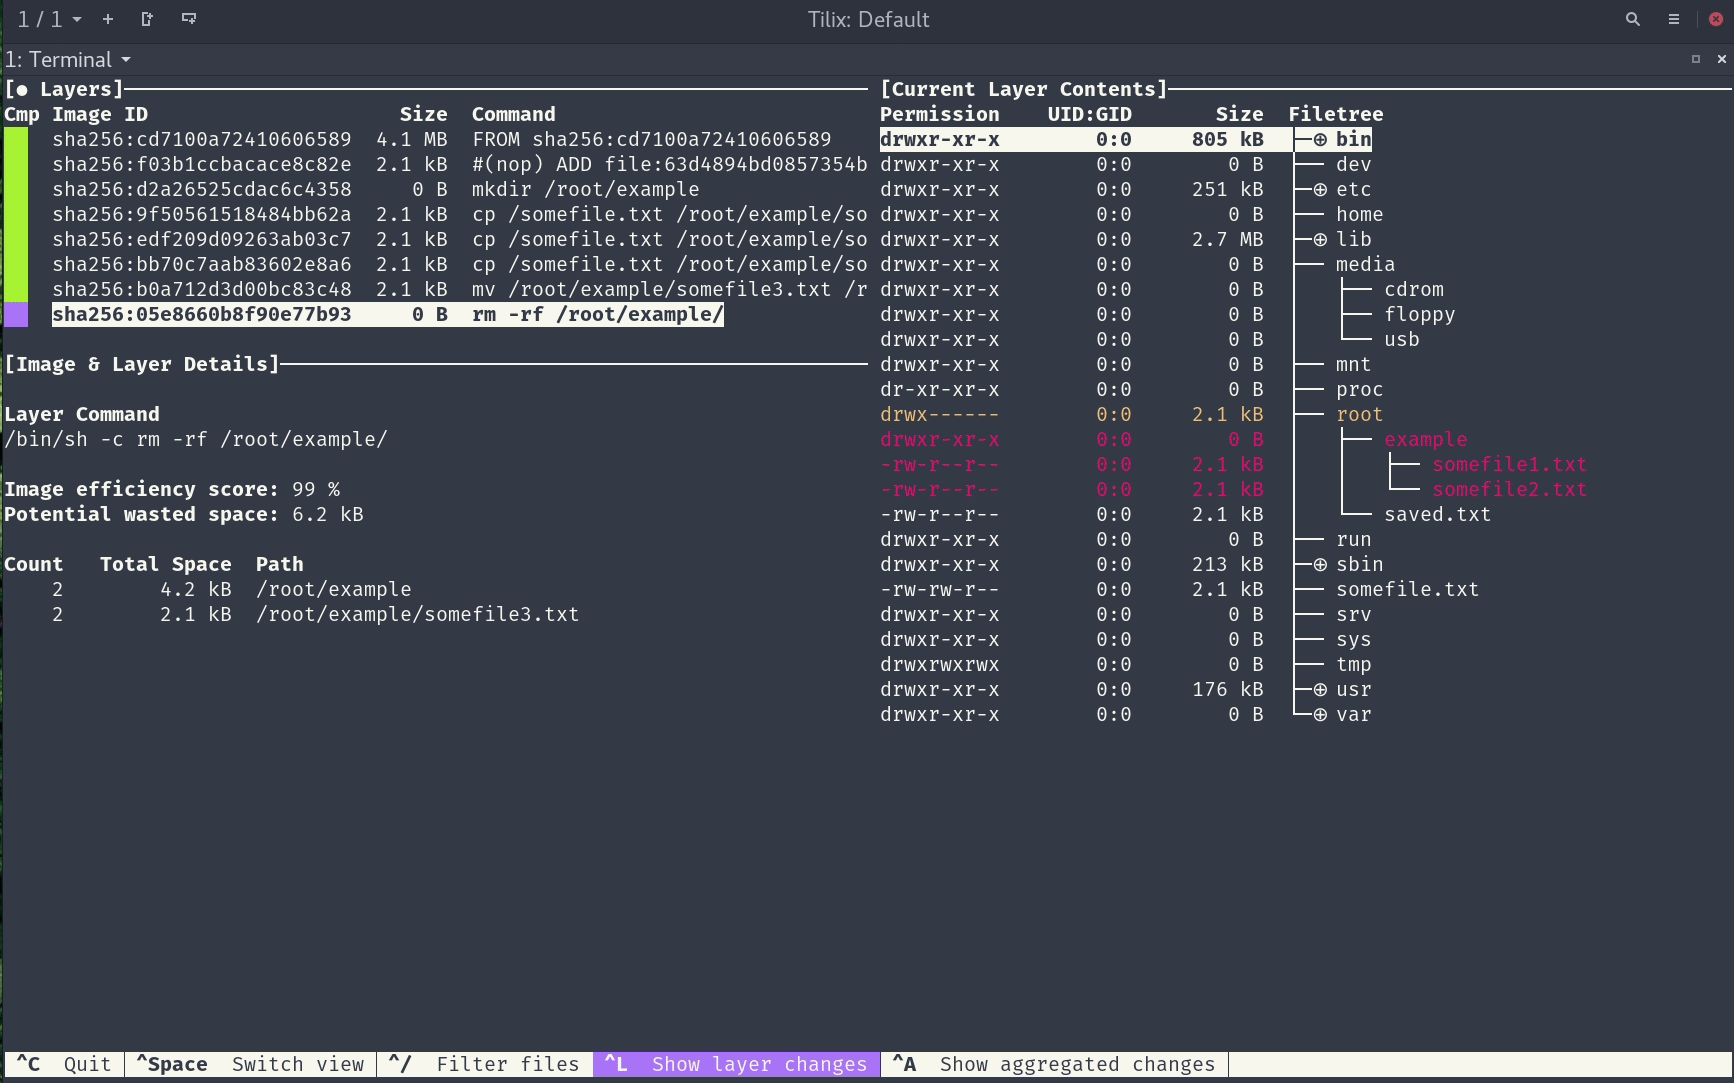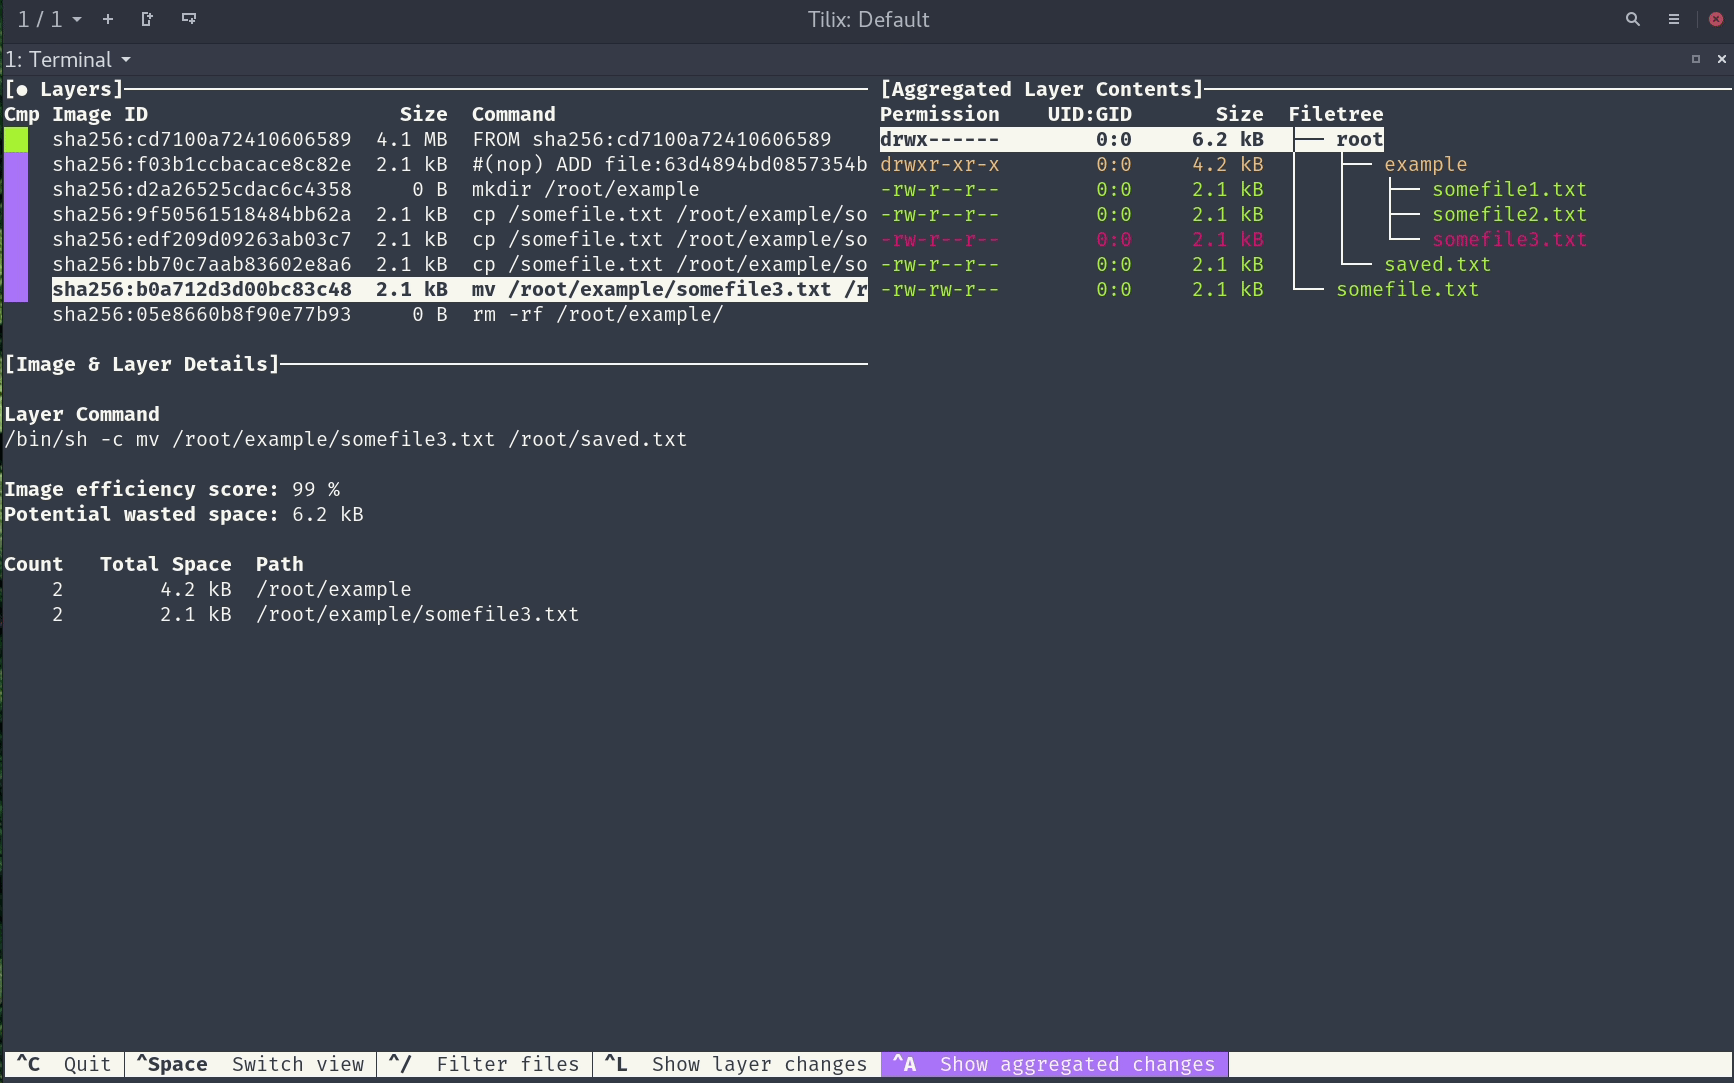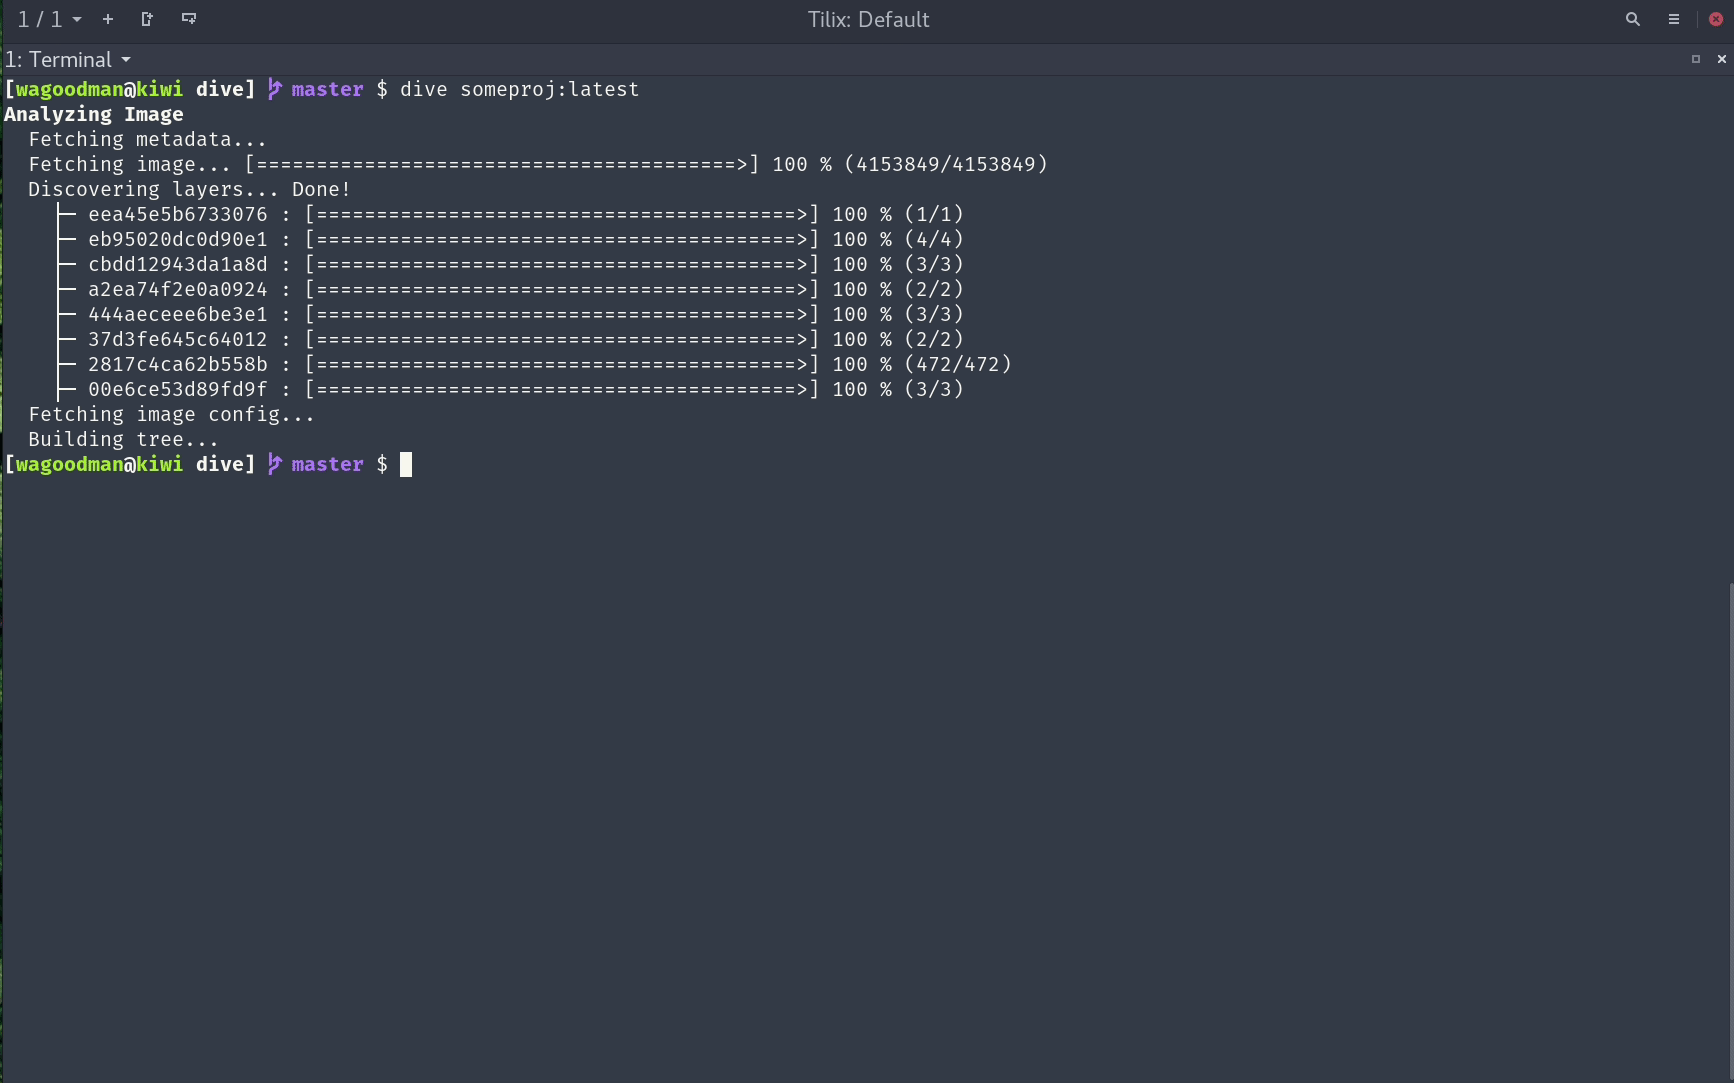 wagoodman/dive
A tool for exploring each layer in a docker image
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…