
vesta
 kvesta/vesta
A static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
cloud-securityconfiguration-auditingcontainer-security+3
206
kvesta/vestaA static analysis of vulnerabilities, Docker and Kubernetes cluster configuration detect toolkit based on the real penetration of cloud computing
 armourbird/csf
ArmourBird CSF - Container Security Framework
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 alixiacf/hpim-training-lab
Trained to Escalate: Forensic Analysis and Local Replication of RLHF-Induced Privilege Escalation in AI Agents (CVE-2026-65616)
 exptechtw/cve-2025-66478
Real-world attack log analysis of CVE-2025-66478 (Next.js Server Actions RCE) with malware samples, attacker IP tracking, and container security…
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
 extracoding-dozen/cve-2024-3094
Research of CVE-2024-3094 vulnerability.
 excellencedev/cve-2018-19629
Hyland Perceptive Content Server - Denial of Service
 shoucheng3/apache__dolphinscheduler_cve-2023-49109_3-2-0
Exploit for CVE-2023-49109 targeting Apache DolphinScheduler, a cloud-native data orchestration platform. Enables security testing of workflow…
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 skorokithakis/stavrobot
An AI personal assistant with a focus on security.

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 mhaggis/package-inferno
A Public Package Scanner for The Community
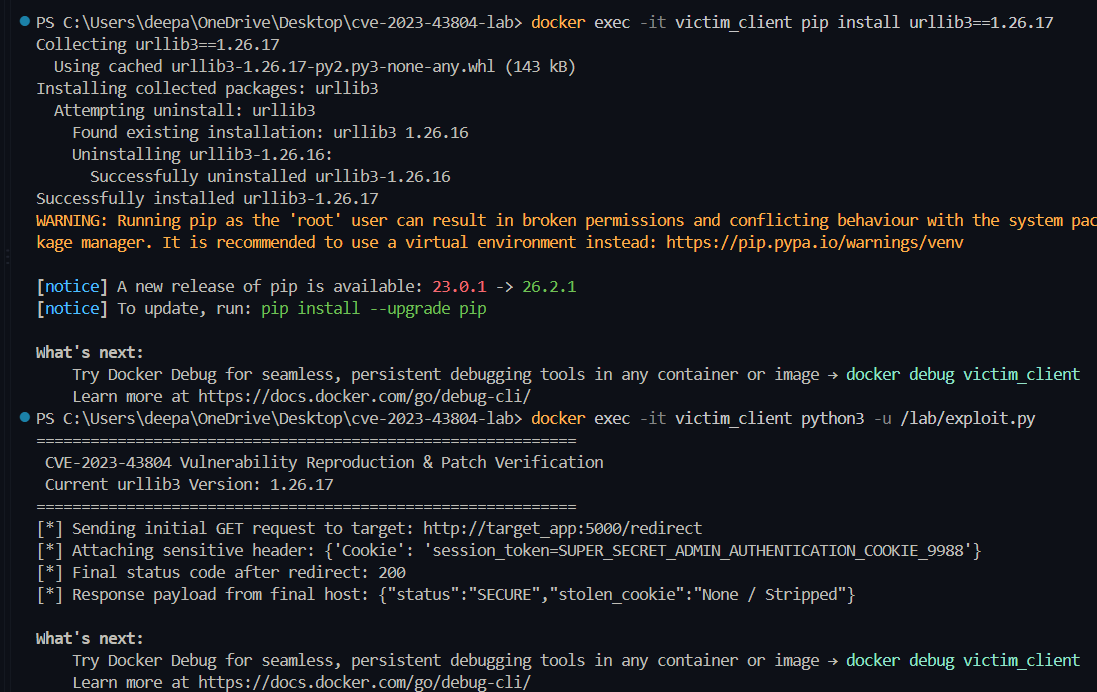 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 vvpoglazov/cve-2024-41110-checker
Parallel SSH-based scanner that detects CVE-2024-41110 in Docker installations, identifies vulnerable versions and AuthZ plugins, and generates a…
 laremontada12/cve-2026-39987-marimo-preauth-rce
CVE-2026-39987 Marimo Pre-auth RCE research, Docker lab reproduction, root cause analysis, and patch validation.