

CVE-2024-21626-POC
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
cloud-securitycontainer-escapecontainer-security+3
zpxlz/cve-2024-21626-pocProof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
 ps-interactive/cve-2025-55182
Vulnerable REACT app in docker container and poc code - for demos
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 flame-11/cve-2018-15133-laravel-framework
Reproducible Docker lab for CVE-2018-15133 (Laravel Framework token unserialize RCE) with a known APP_KEY and a /poc route for testing exploit…
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 nicetop1027/cve-2026-d0cker
Proof-of-concept exploit for critical runC container escape vulnerability (CVE-2026-Pending) with symlink race condition, including Go PoC, analysis,…
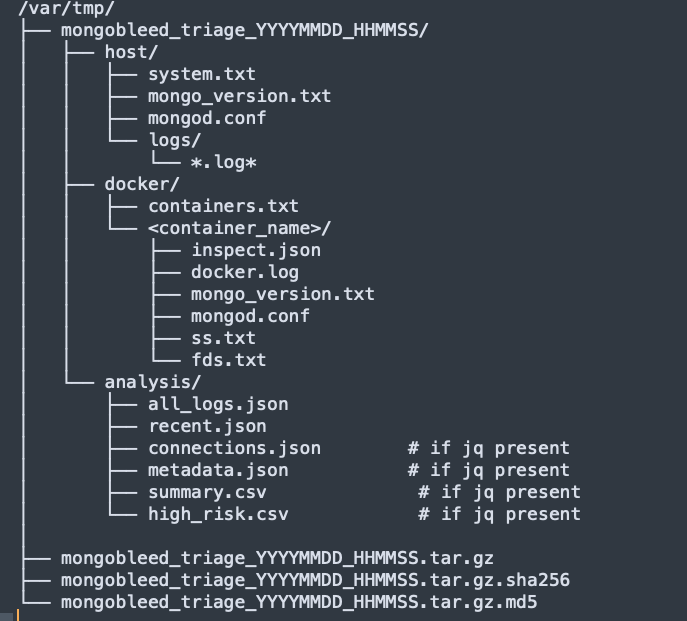 jemhadar/mongobleed-dfir-triage-script-cve-2025-14847
The script focuses on safe artifact acquisition first, followed by optional on-host analysis, and produces a portable, hashed forensic archive…
 septembersend/cve--2026-24061
Dockerized proof-of-concept environment for CVE-2026-24061, targeting InetUtils telnetd vulnerability for security testing and research.
 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 cved-sources/cve-2017-8046
Docker-based vulnerable environment for CVE-2017-8046 Spring framework remote code execution exploit, part of the Cved vulnerable container…
 cved-sources/cve-2018-15473
Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…
 arbaaz29/cve-2022-3294
Privilege Escalation using nodes/proxy (create action allowed) and nodes/status (update/patch actions allowed)
 skysbsb/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in Docker/runc. Demonstrates file descriptor manipulation to break out…
 garethmsheldon/cve-2025-60787-detection-motioneye-rce-via-config-injection
Detection rules and YARA/KQL signatures for CVE-2025-60787, an unauthenticated RCE in motionEye via config injection, with process execution and file…
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 cved-sources/cve-2019-9184
Docker container with a pre-configured vulnerable environment for CVE-2019-9184, designed for security testing and educational exploitation practice.
 lalaterry/cve-2025-55182-react2shell-lab
Docker-based research lab for CVE-2025-55182 (React2Shell) exploitation, providing a controlled environment to study and practice the vulnerability.