
shellshock-poc-cve-2014-7169
 kushiro45/shellshock-poc-cve-2014-7169
This contains the Dockerfile for building and reproduing shellshock
binary-exploitationcontainer-securityeducation+2
kushiro45/shellshock-poc-cve-2014-7169This contains the Dockerfile for building and reproduing shellshock
 gunwoo105/node_cve-2023-29017
Node.js vm2 CVE-2023-29017 reproduction with Docker Compose and PoC
 george0papasotiriou/cve-2026-21019-kubernetes-cronjob-suspended-execution-via-time-manipulation
Reproduces CVE-2026-21019 by manipulating node clock to force early Kubernetes CronJob execution; includes vulnerable YAML manifest and Python…
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 niclas-zone/ctr/gitleaks
Containerized secret scanning tool that detects exposed credentials, API keys, and tokens in Git repositories using regex and entropy-based…
 gyubin02/cve-2026-59891-control-lab
Isolated regression and security-control lab for CVE-2026-59891 in @sigstore/oci
 sk3pper/cve-2024-21626
Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…
 ahndrewalters/projectsecurity-homelab
Hands-on homelab simulating the Log4Shell (CVE-2021-44228) vulnerability. Deploy Docker containers to build a vulnerable target and attacker machine,…
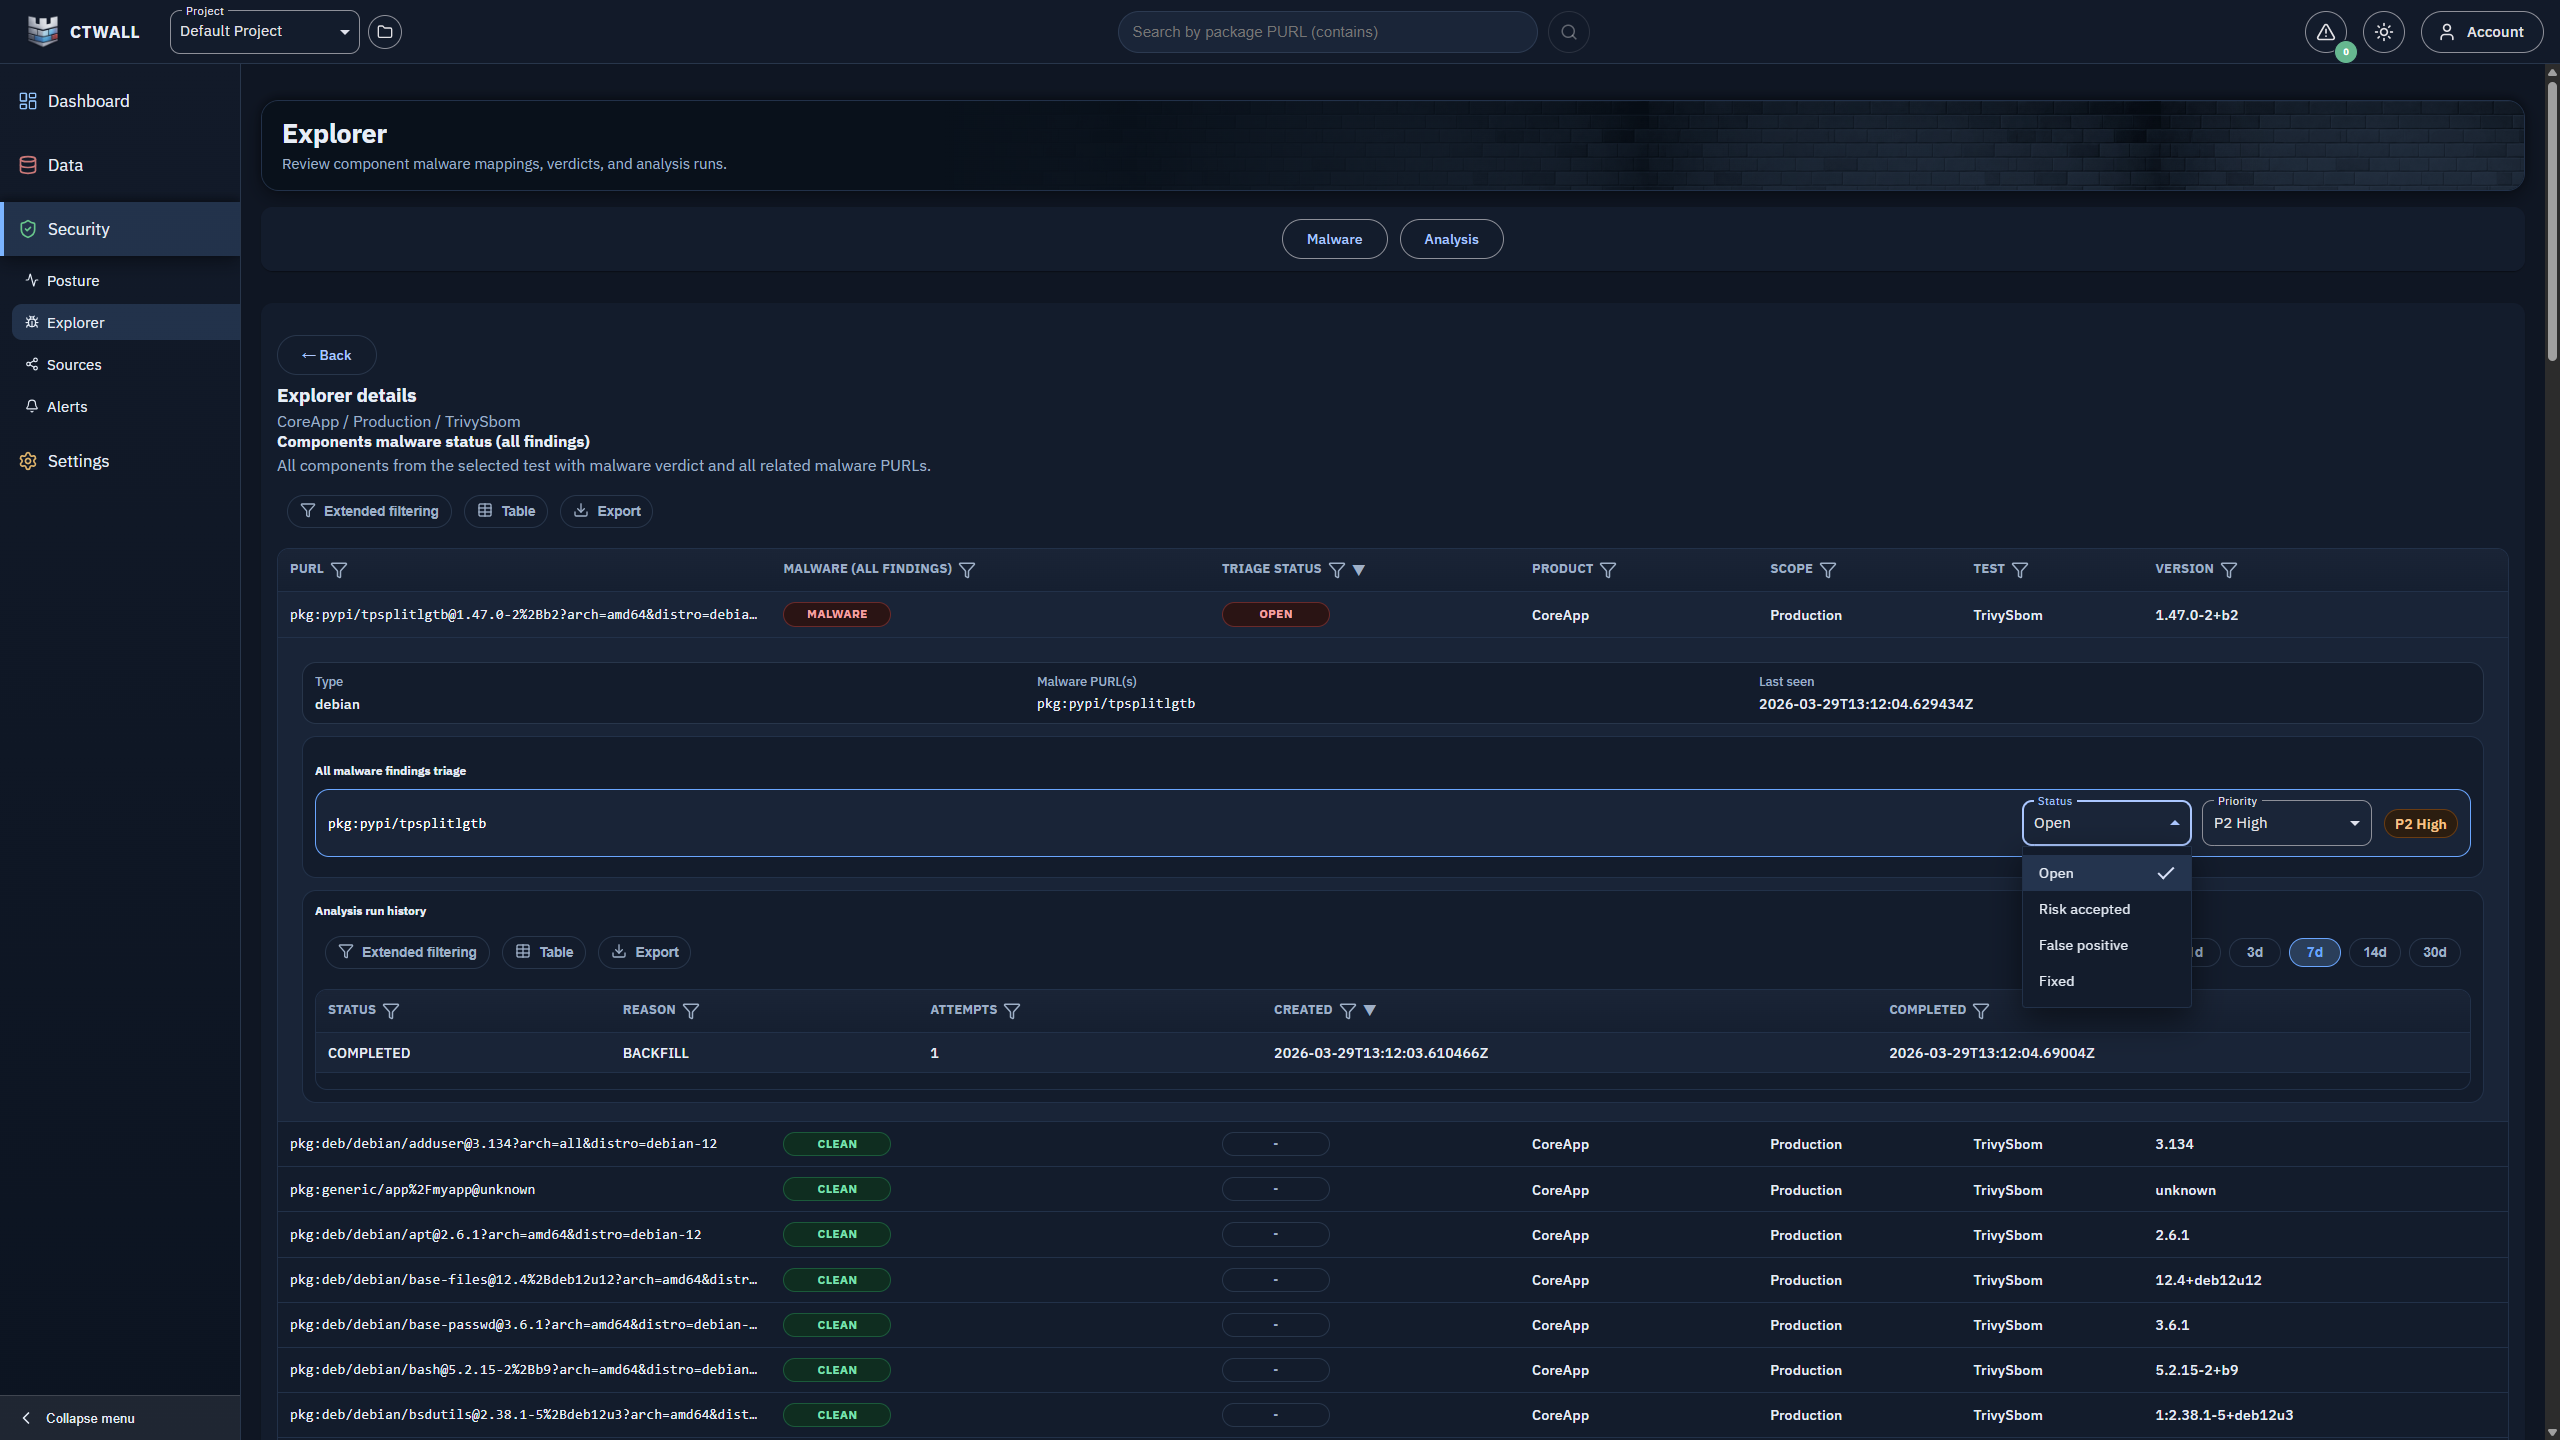 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 snyk/snyk-scan
Automated Snyk vulnerability scanning for dependencies and Docker images in Bitbucket Pipelines, with severity thresholds and monitoring options.
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 yifanzhg/cve-2020-15778
Reproduces CVE-2020-15778 SCP command injection exploit with Docker-based client-server setup for testing remote code execution and reverse shell…
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
 tuxotron/cve-2018-11776-docker
Dockerized proof-of-concept exploit for CVE-2018-11776 (Apache Struts2) with a Go-based command execution payload for penetration testing and…