
agent-bom
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
ai-securitycloud-securitycontainer-security+6
msaad00/agent-bomOpen security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 gensecaihq/react2shell-scanner
Detects CVE-2025-55182 RCE in React Server Components by scanning npm/pnpm/yarn lockfiles, Docker images, SBOMs, and live URLs. Includes auto-fix,…
 nccgroup/kubetcd
Post-exploit a compromised etcd, gain persistence and remote shell to nodes.
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 t0kx/exploit-cve-2016-9920
Roundcube 1.0.0 <= 1.2.2 Remote Code Execution exploit and vulnerable container
 owasp/vulnerable-container-hub
VULCONHUB provides access to files to build your own hands-on vulnerable container image to learn and practice security
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 opsxcq/exploit-cve-2016-7434
NTPD remote DOS exploit and vulnerable container
 akamajoris/cve-2019-11043-docker
Dockerized vulnerable PHP-FPM environment for CVE-2019-11043, with instructions to build and run the phuip-fpizdam exploit to achieve remote code…
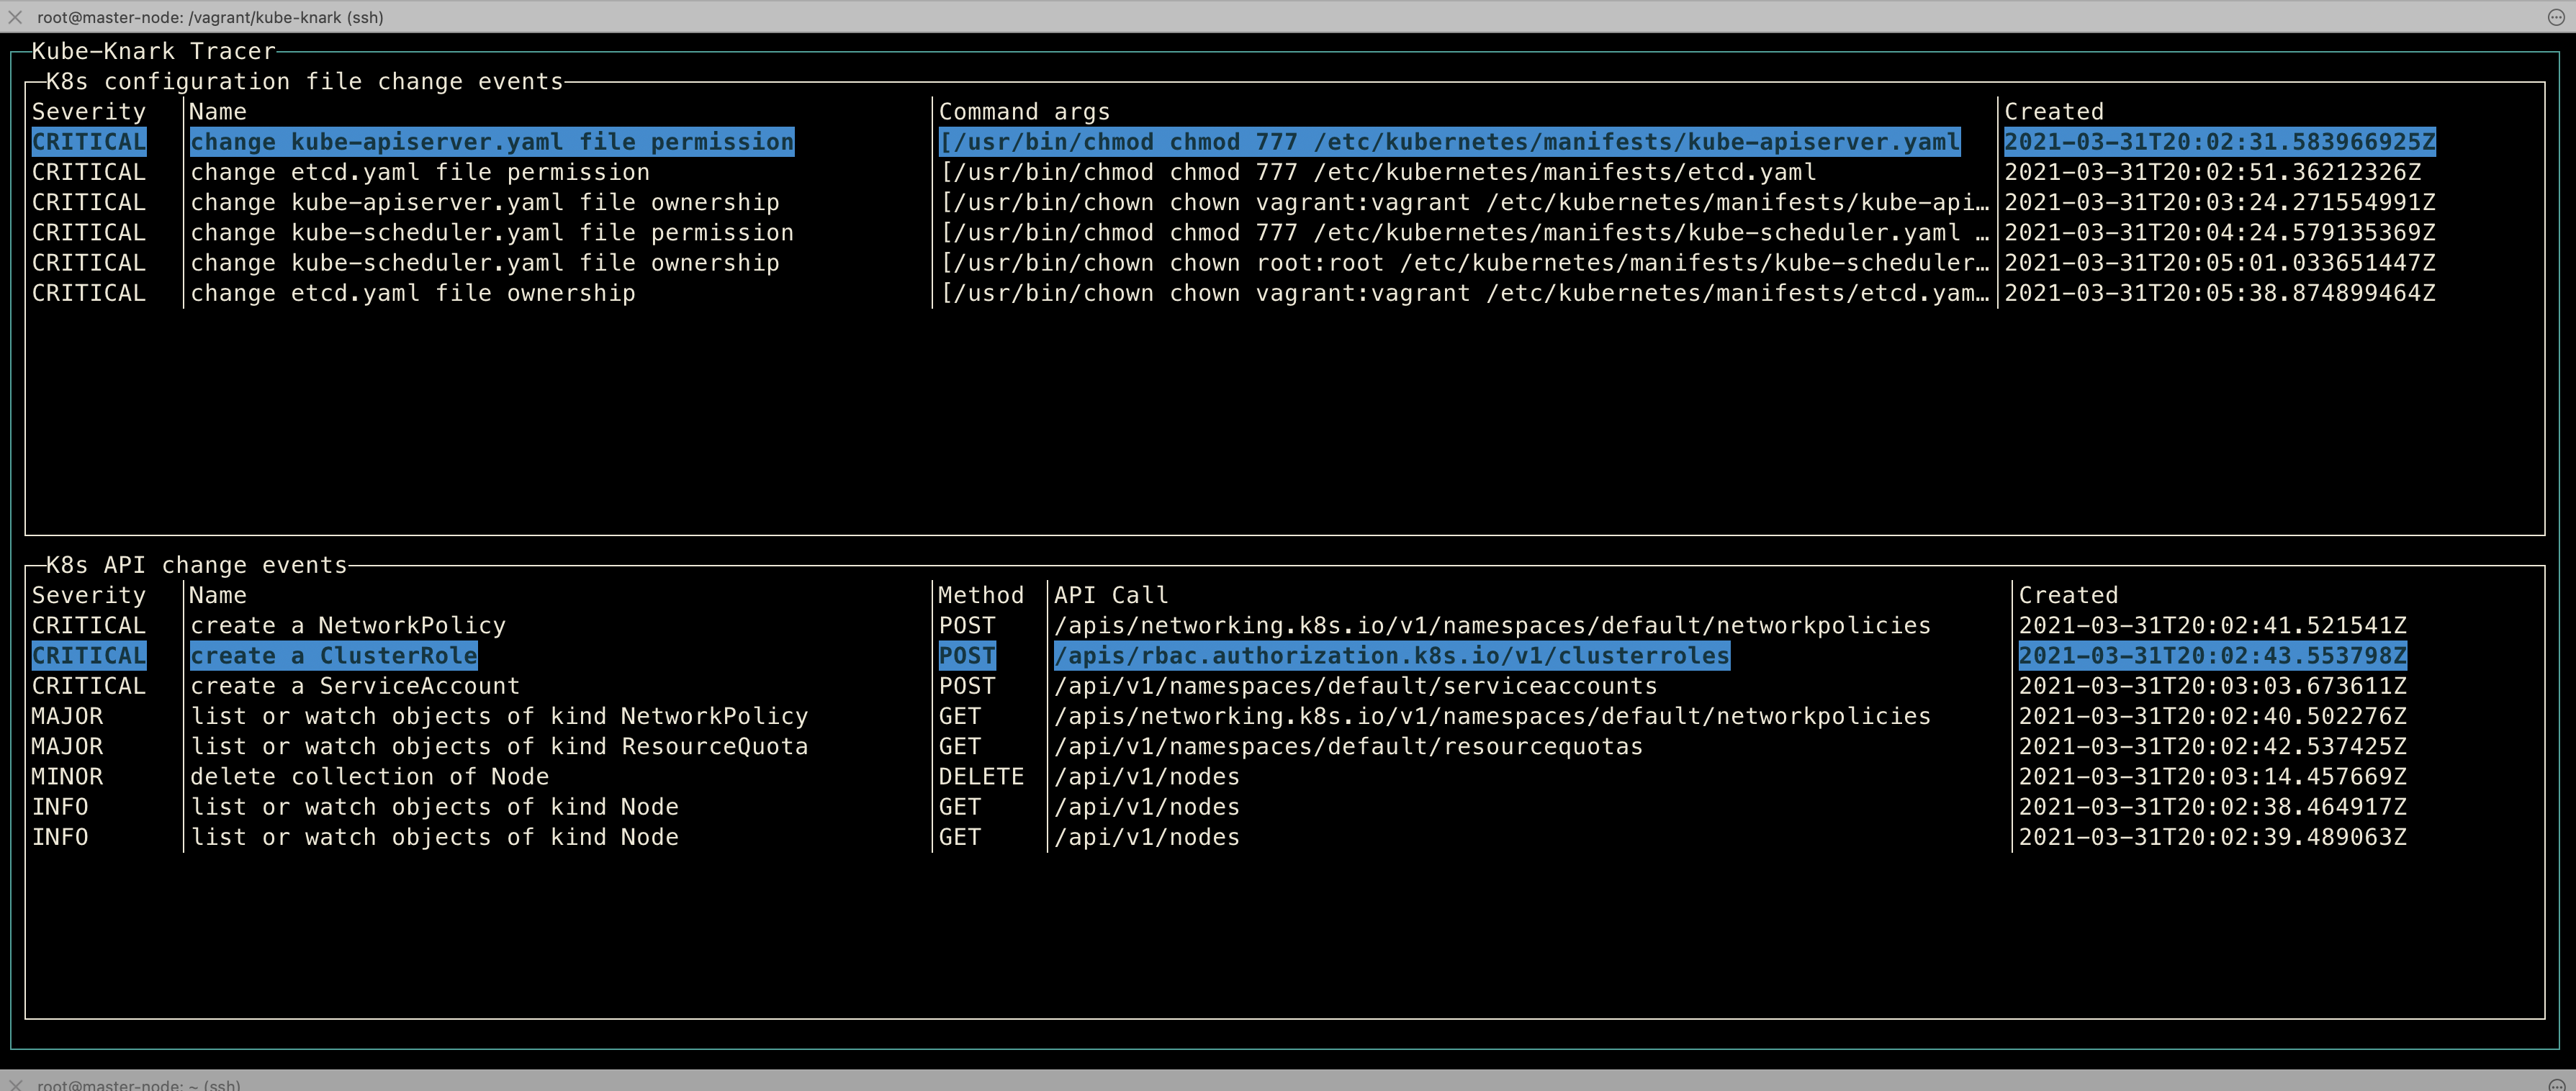 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
 chen-keinan/mesh-kridik
Automated security checker for Kubernetes clusters with Istio service mesh, enforcing best practices via OPA policies and generating remediation…
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…
 xtuc/airgap
Security for the modern age of AI: defend against bad AI agents and malicious npm packages