

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k1 day ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
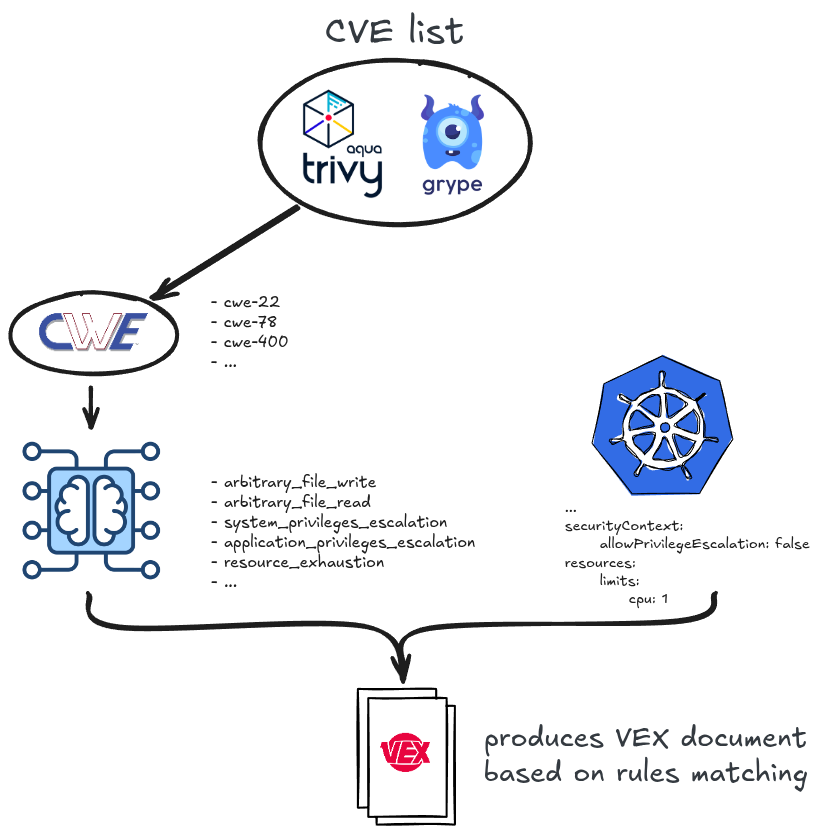 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
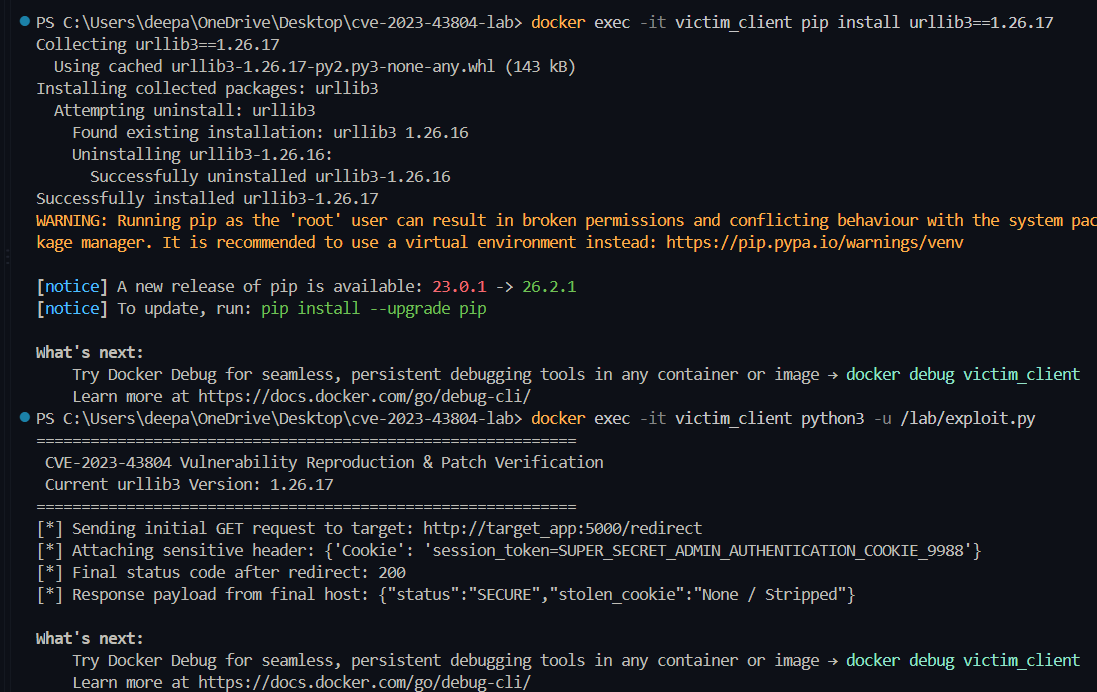 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 yen5004/cve-2024-40635_poc
Proof of Concept code for proving CVE-2024-40635 vulnerability
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 adarkst/honeypot_smart_infrastructure
This Repository Includes Kubernetes manifest files for configuration of Honeypot system and Falco IDS in K8s environment. There are also Demo…
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 rezilion/mi-x
Determine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…