
cynative
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
ai-securitycloud-securitycontainer-security+7
cynative/cynativeRead-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 domcyrus/rustnet
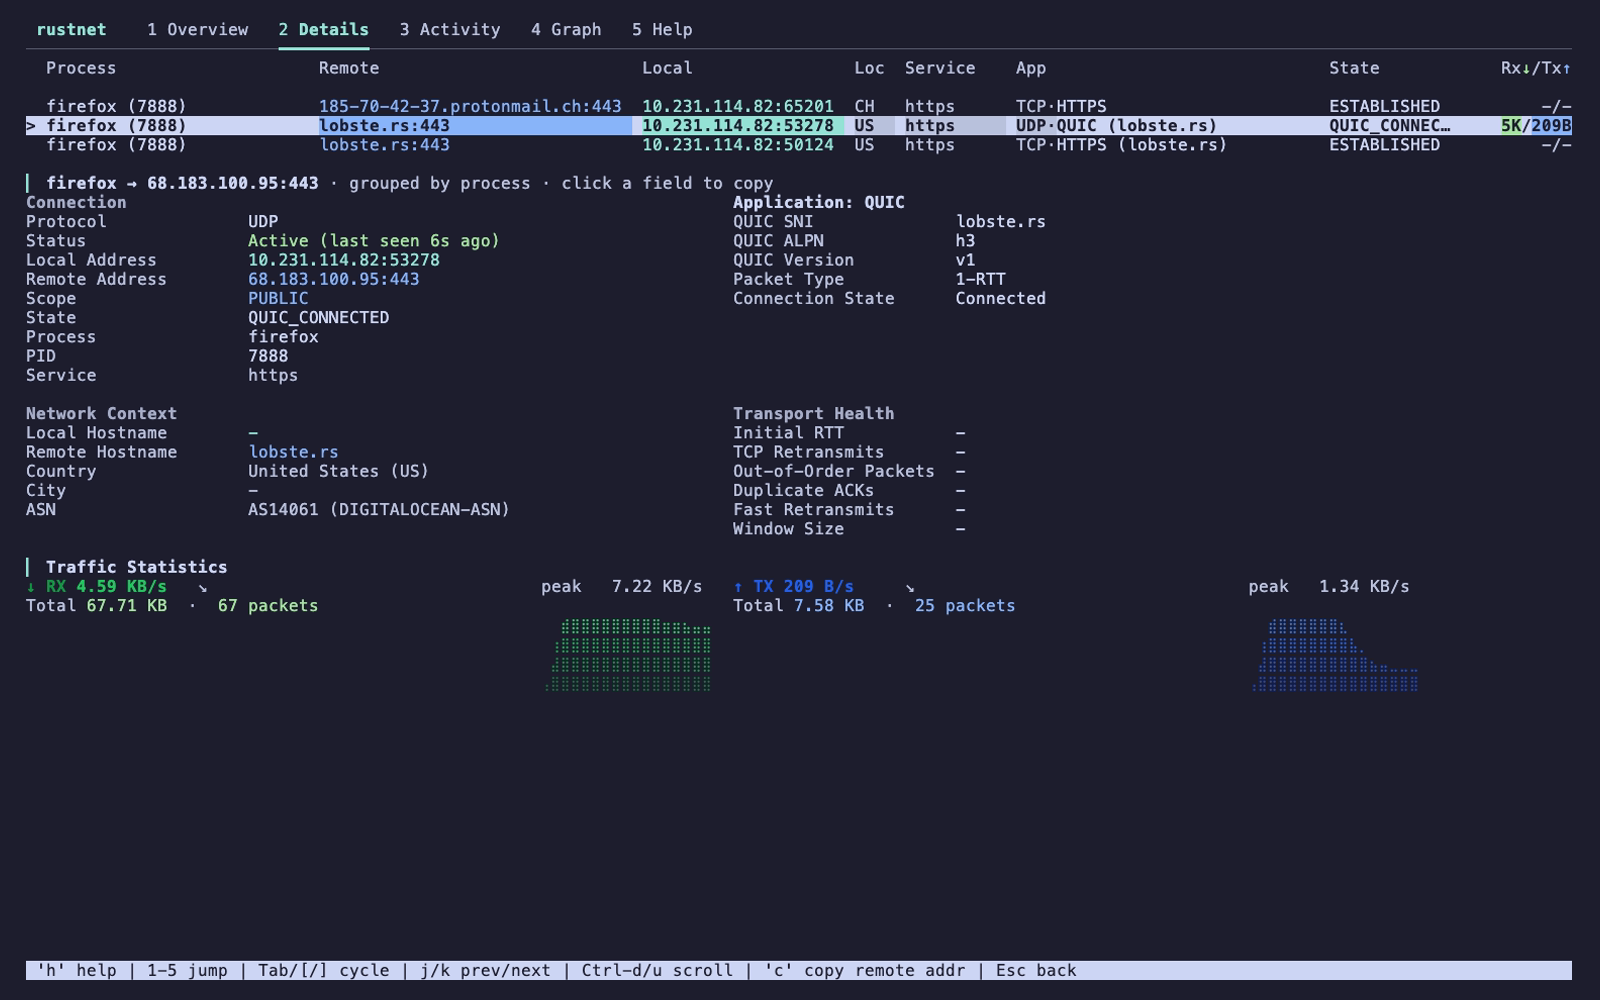
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 blessedrebus/krawl
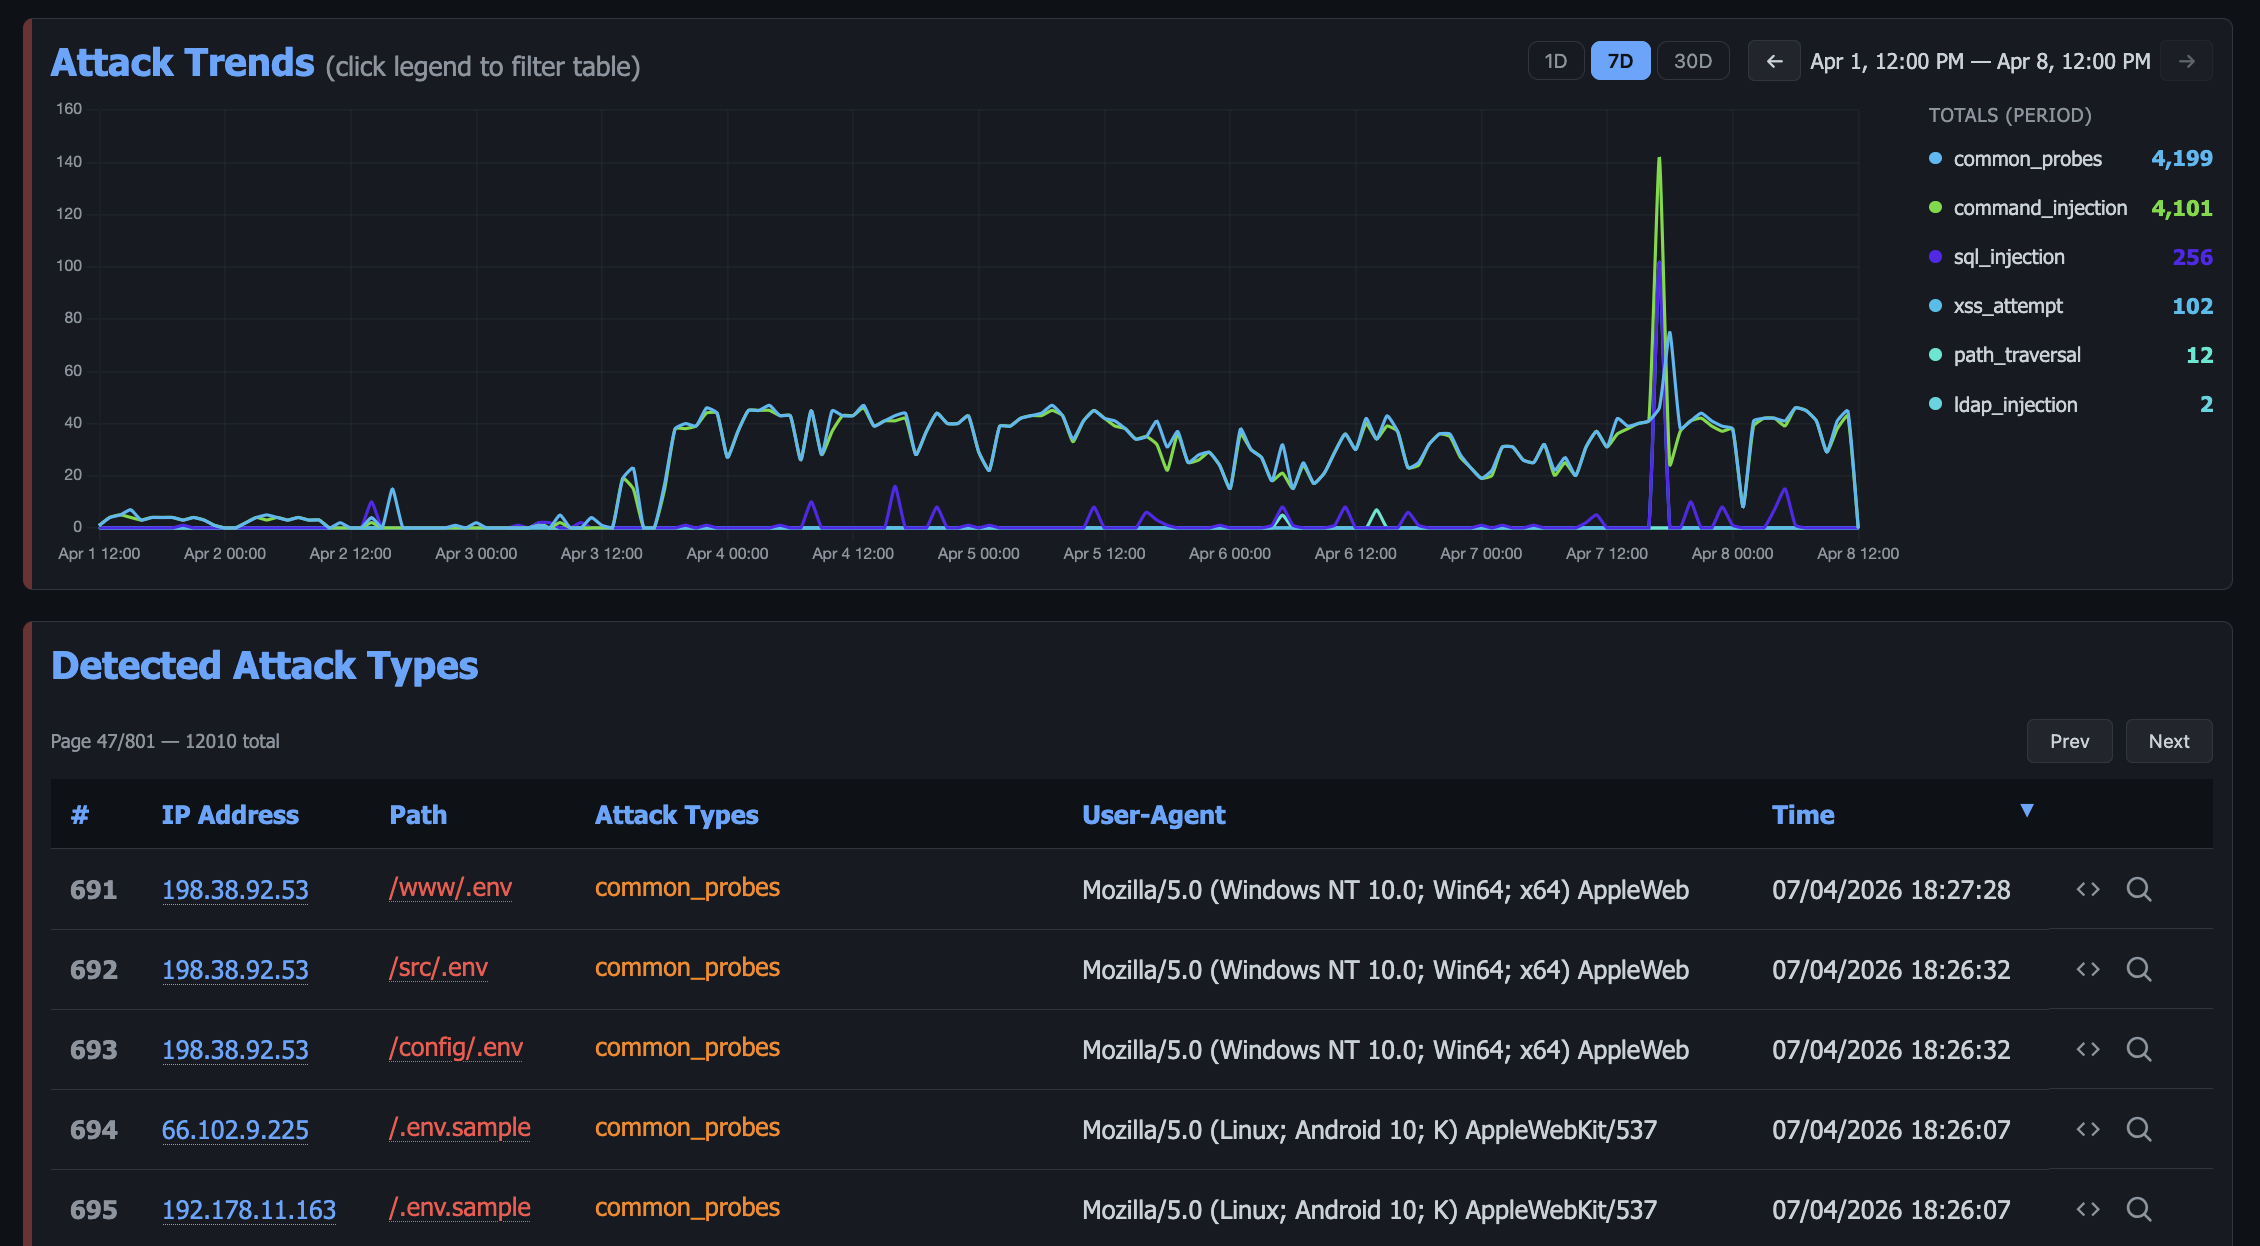
Krawl is a customizable, lightweight, cloud-native web deception server and anti-crawler that creates fake web applications with low-hanging…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 projectdiscovery/pd-agent
ProjectDiscovery Cloud - Agent
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…