
cve-2019-15107-lab
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
container-securitydefensive-toolseducation+5
shambhavim18/cve-2019-15107-labDocker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 saku0512/cve-2026-54761-poc
Proof-of-concept demonstrating an authorization bypass in Traefik's Kubernetes Gateway provider (CVE-2026-54761) via a crossProviderNamespaces…
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…
 learner202649/cve-2026-40217-poc
The code for personally reproducing the corresponding vulnerability
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
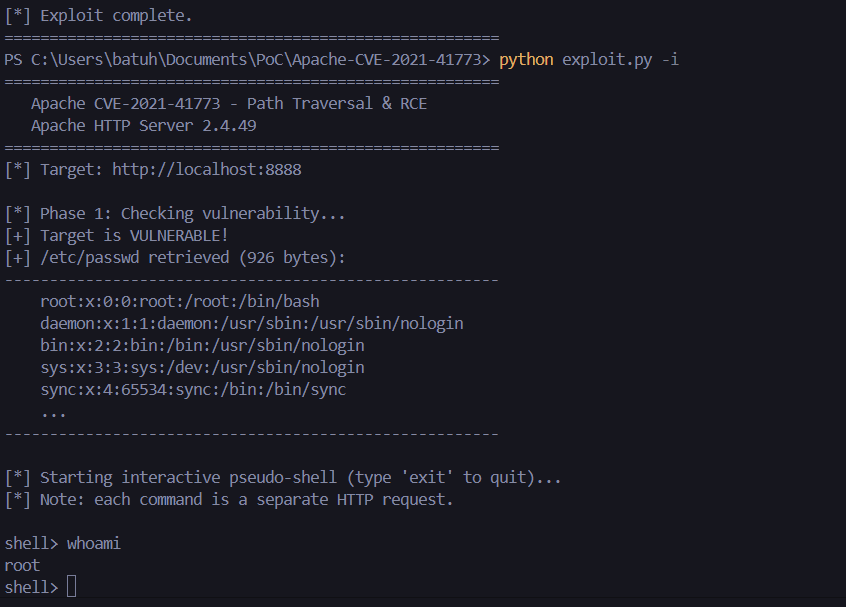 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…
 ps-interactive/cve-2025-55182
Vulnerable REACT app in docker container and poc code - for demos
 abcfabian/react2shell-cve-2025-55182-testing-environment
A containerized testing environment for CVE-2025-55182, a critical (10.0 CVSS) Remote Code Execution vulnerability in React Server Components.
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 bbo513/cve-2023-7231
PoC and Disclosure for CVE-2023-7231 – Memcached Gopher RCE chain