
agent-bom
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
ai-securitycloud-securitycontainer-security+6
31
msaad00/agent-bomOpen security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
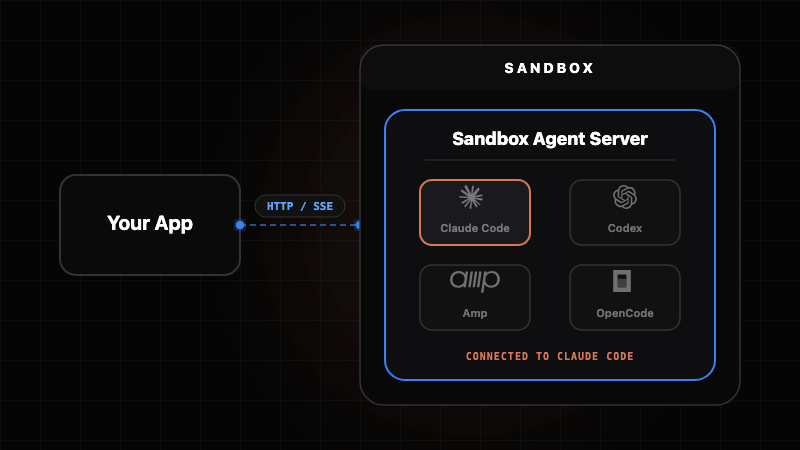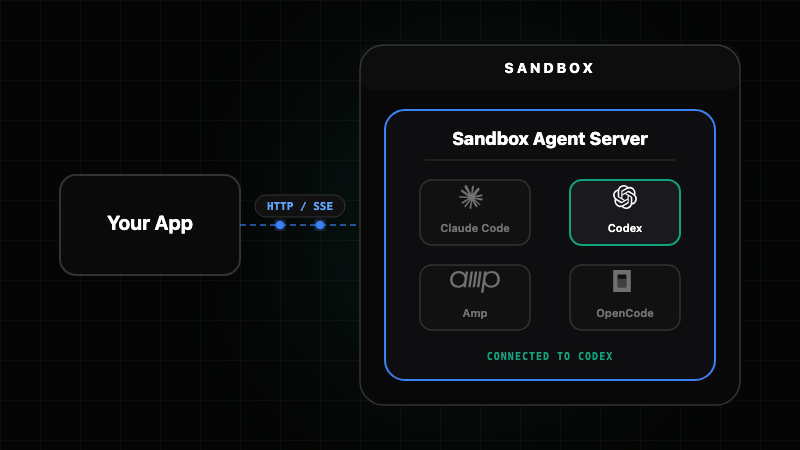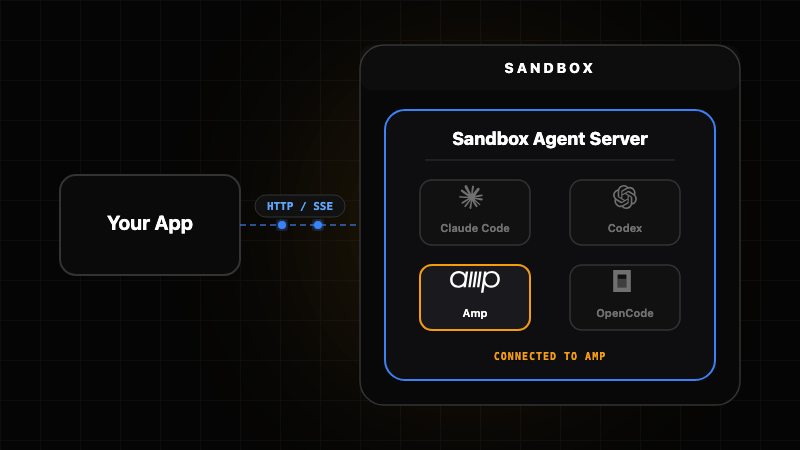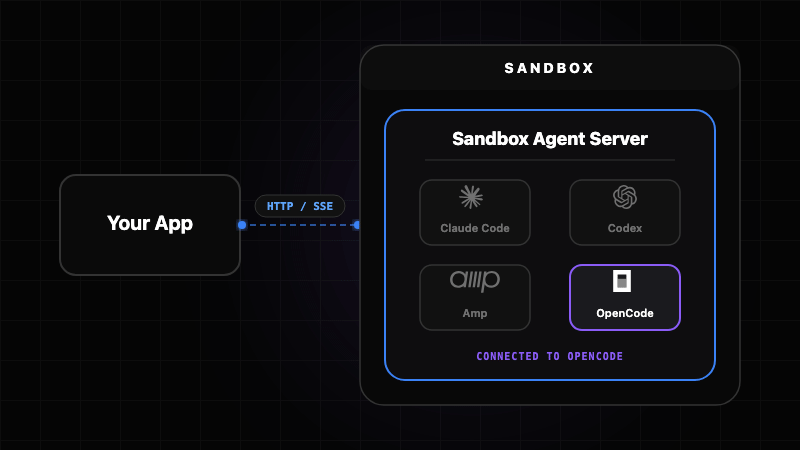 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
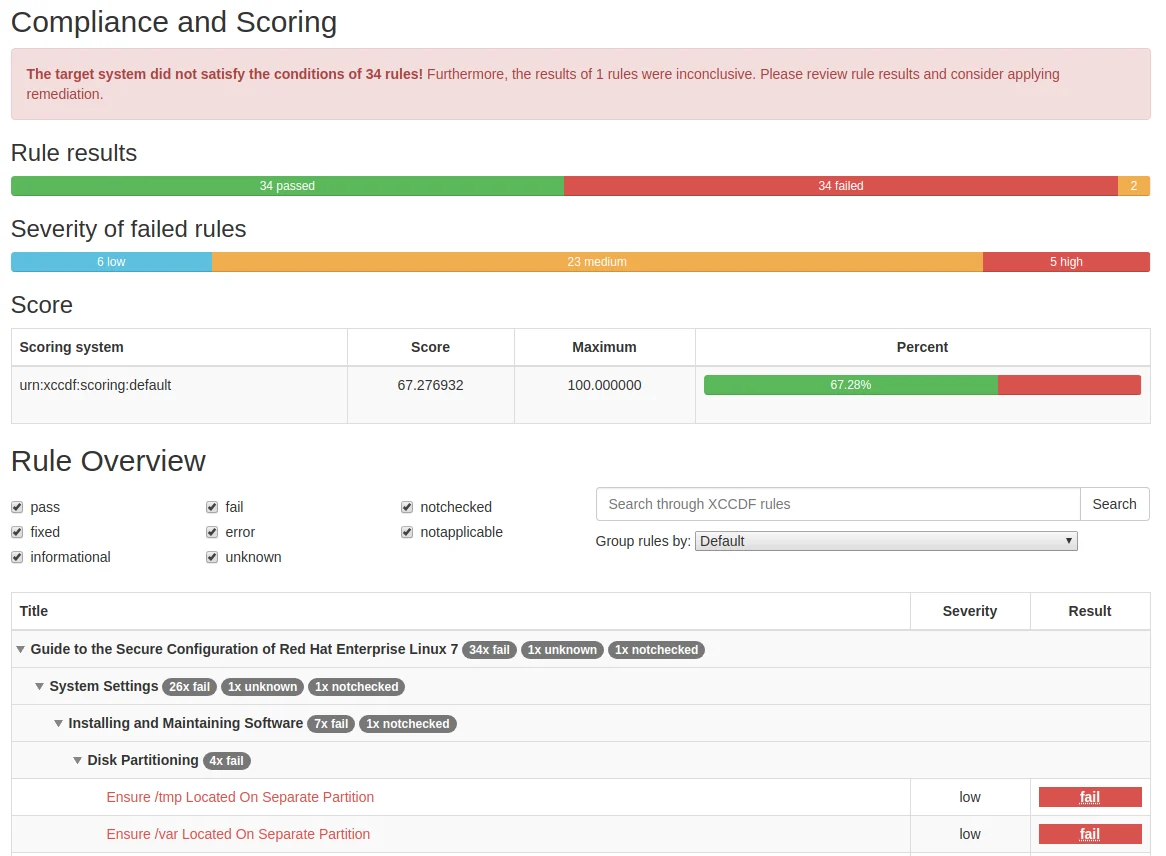 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
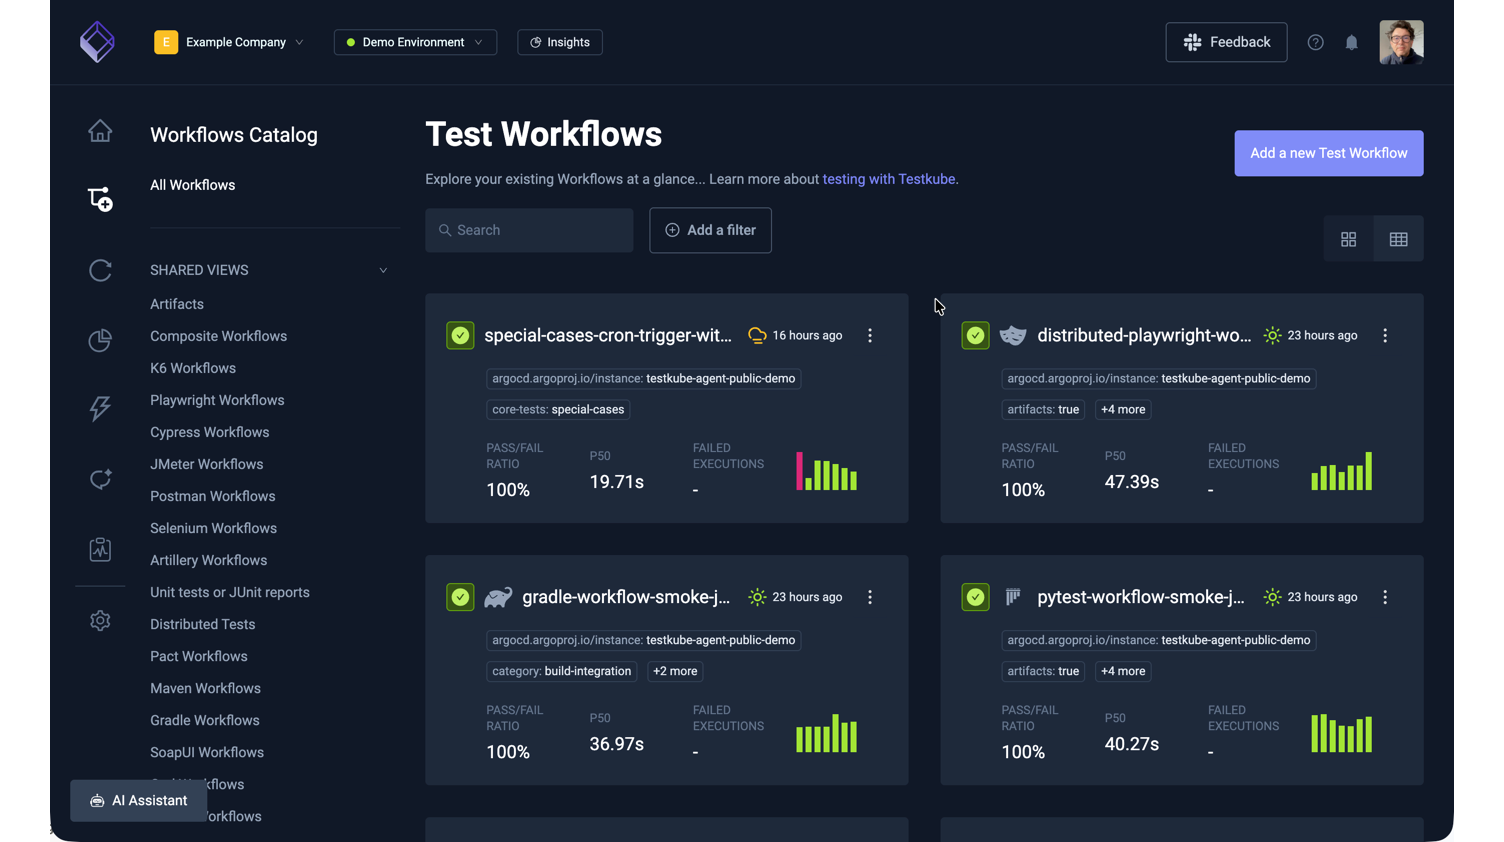 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
 rtvkiz/minimal
Minimal CVE Hardened container image collection
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
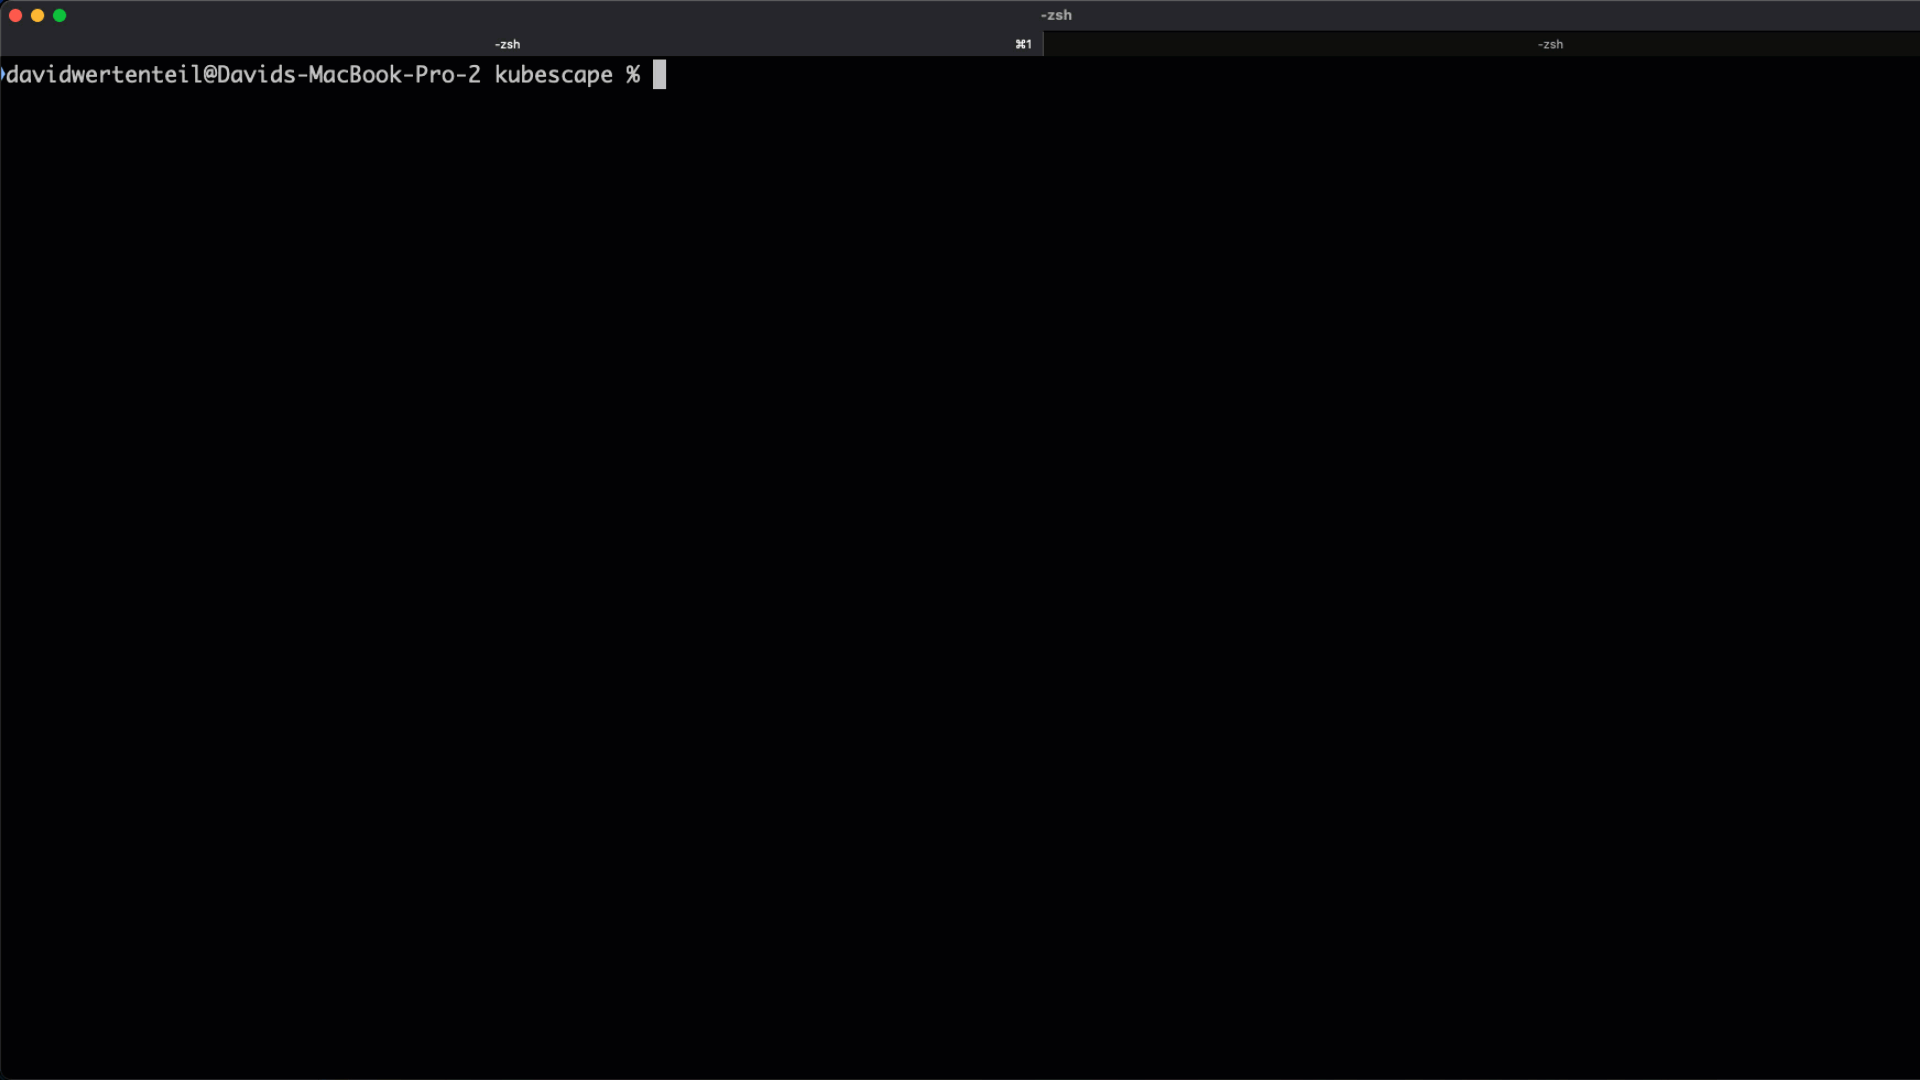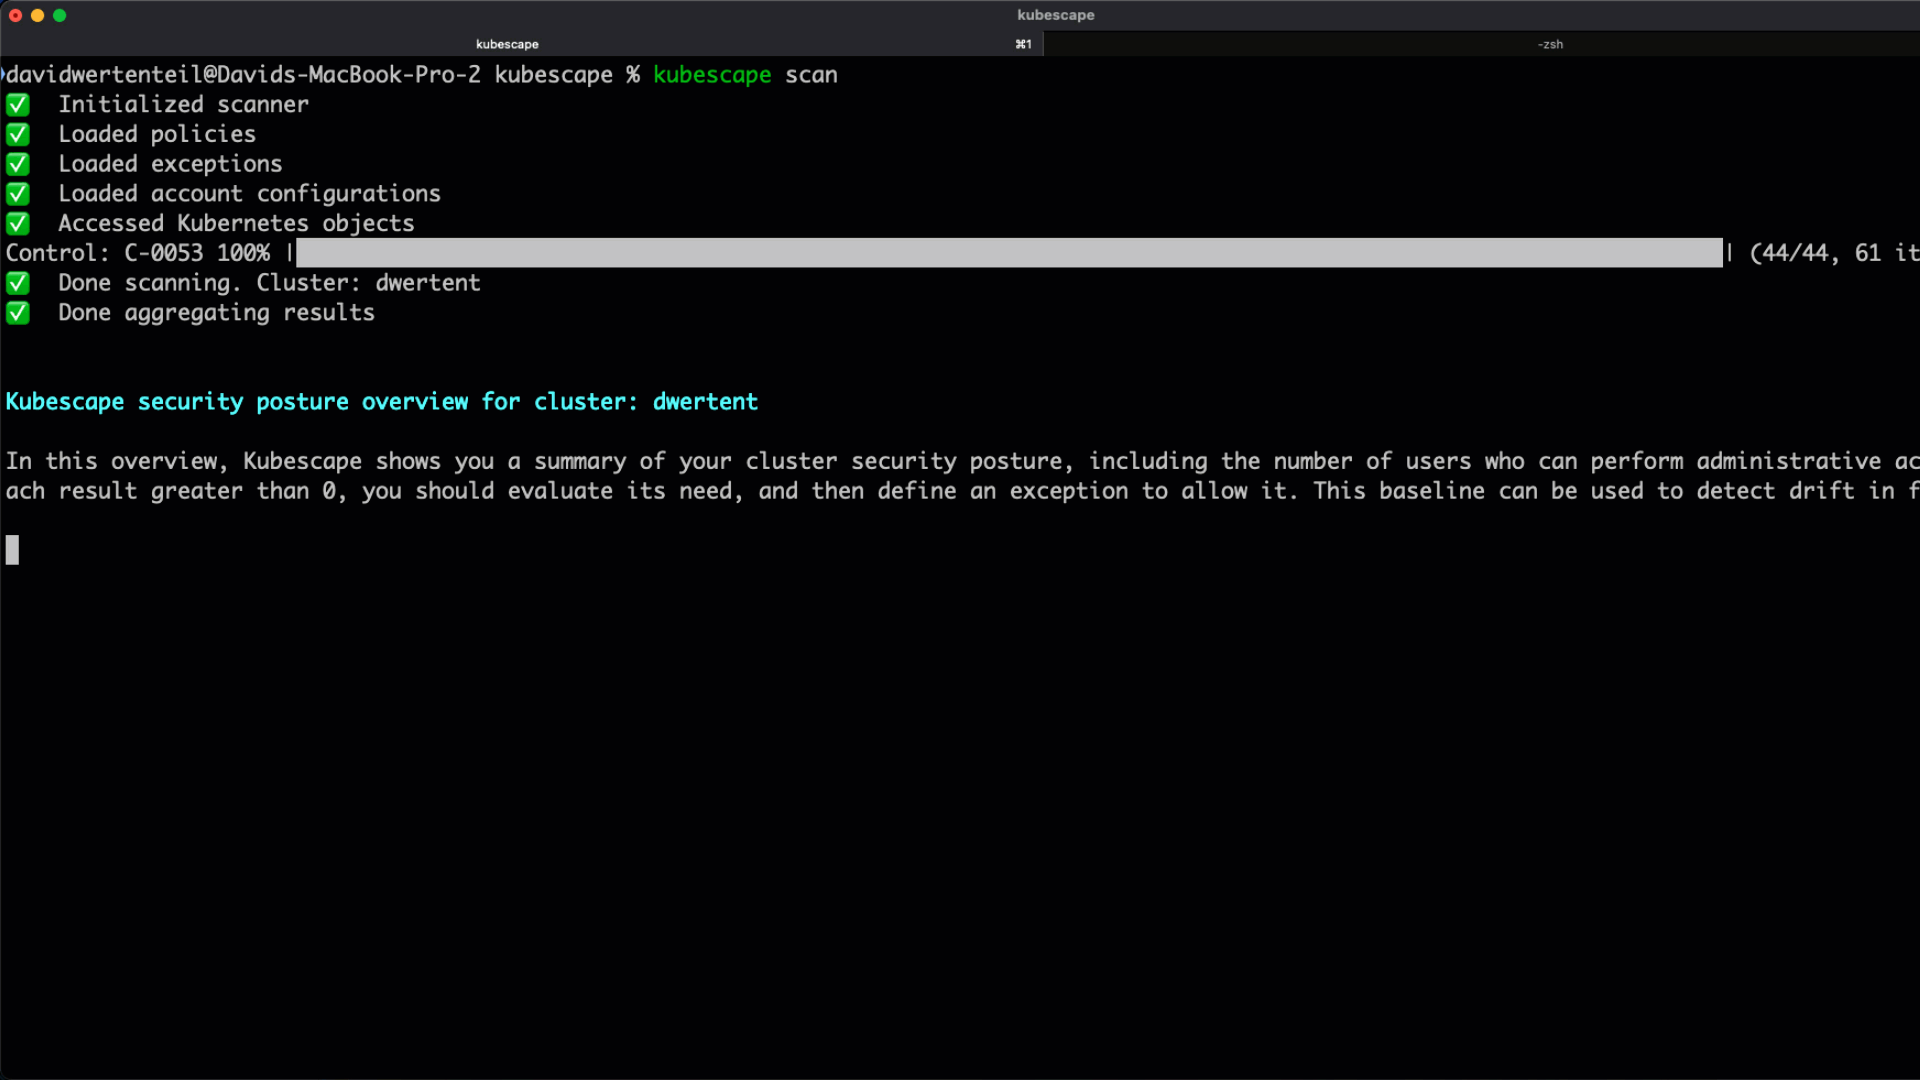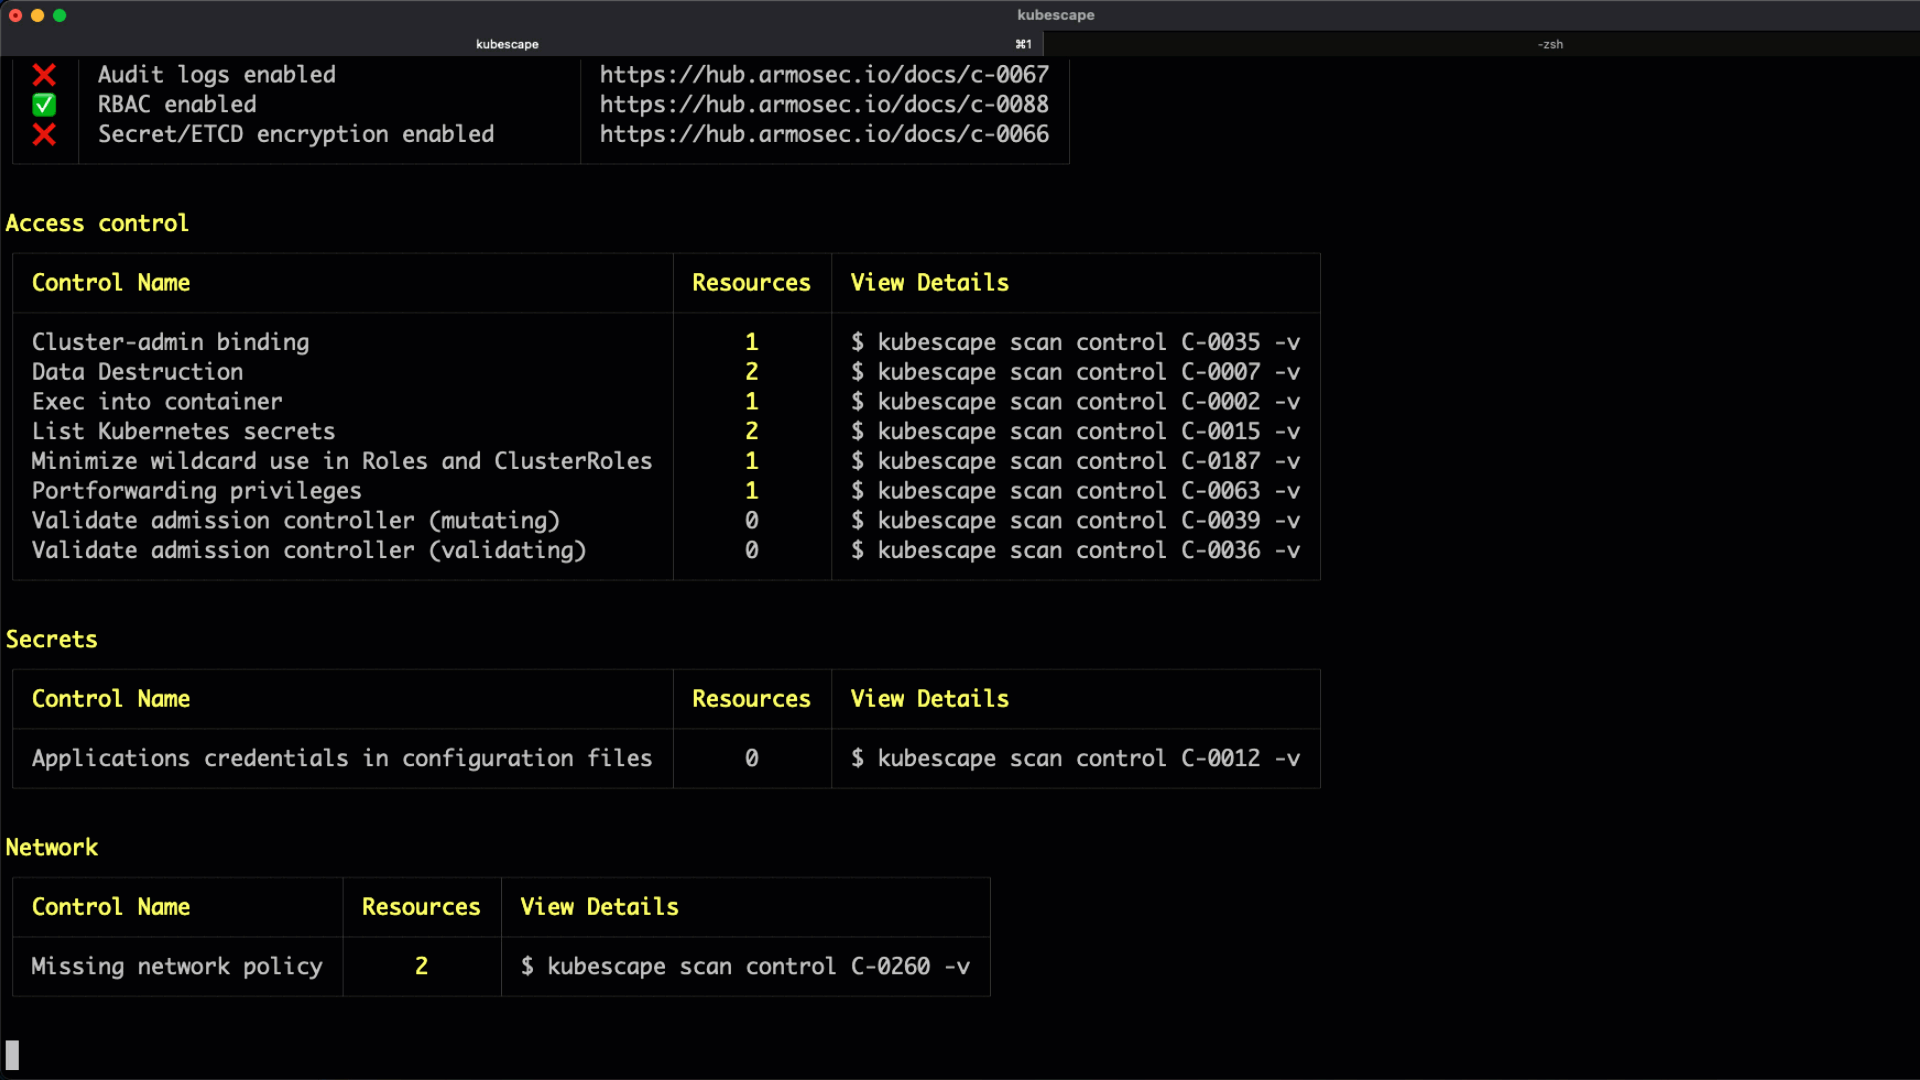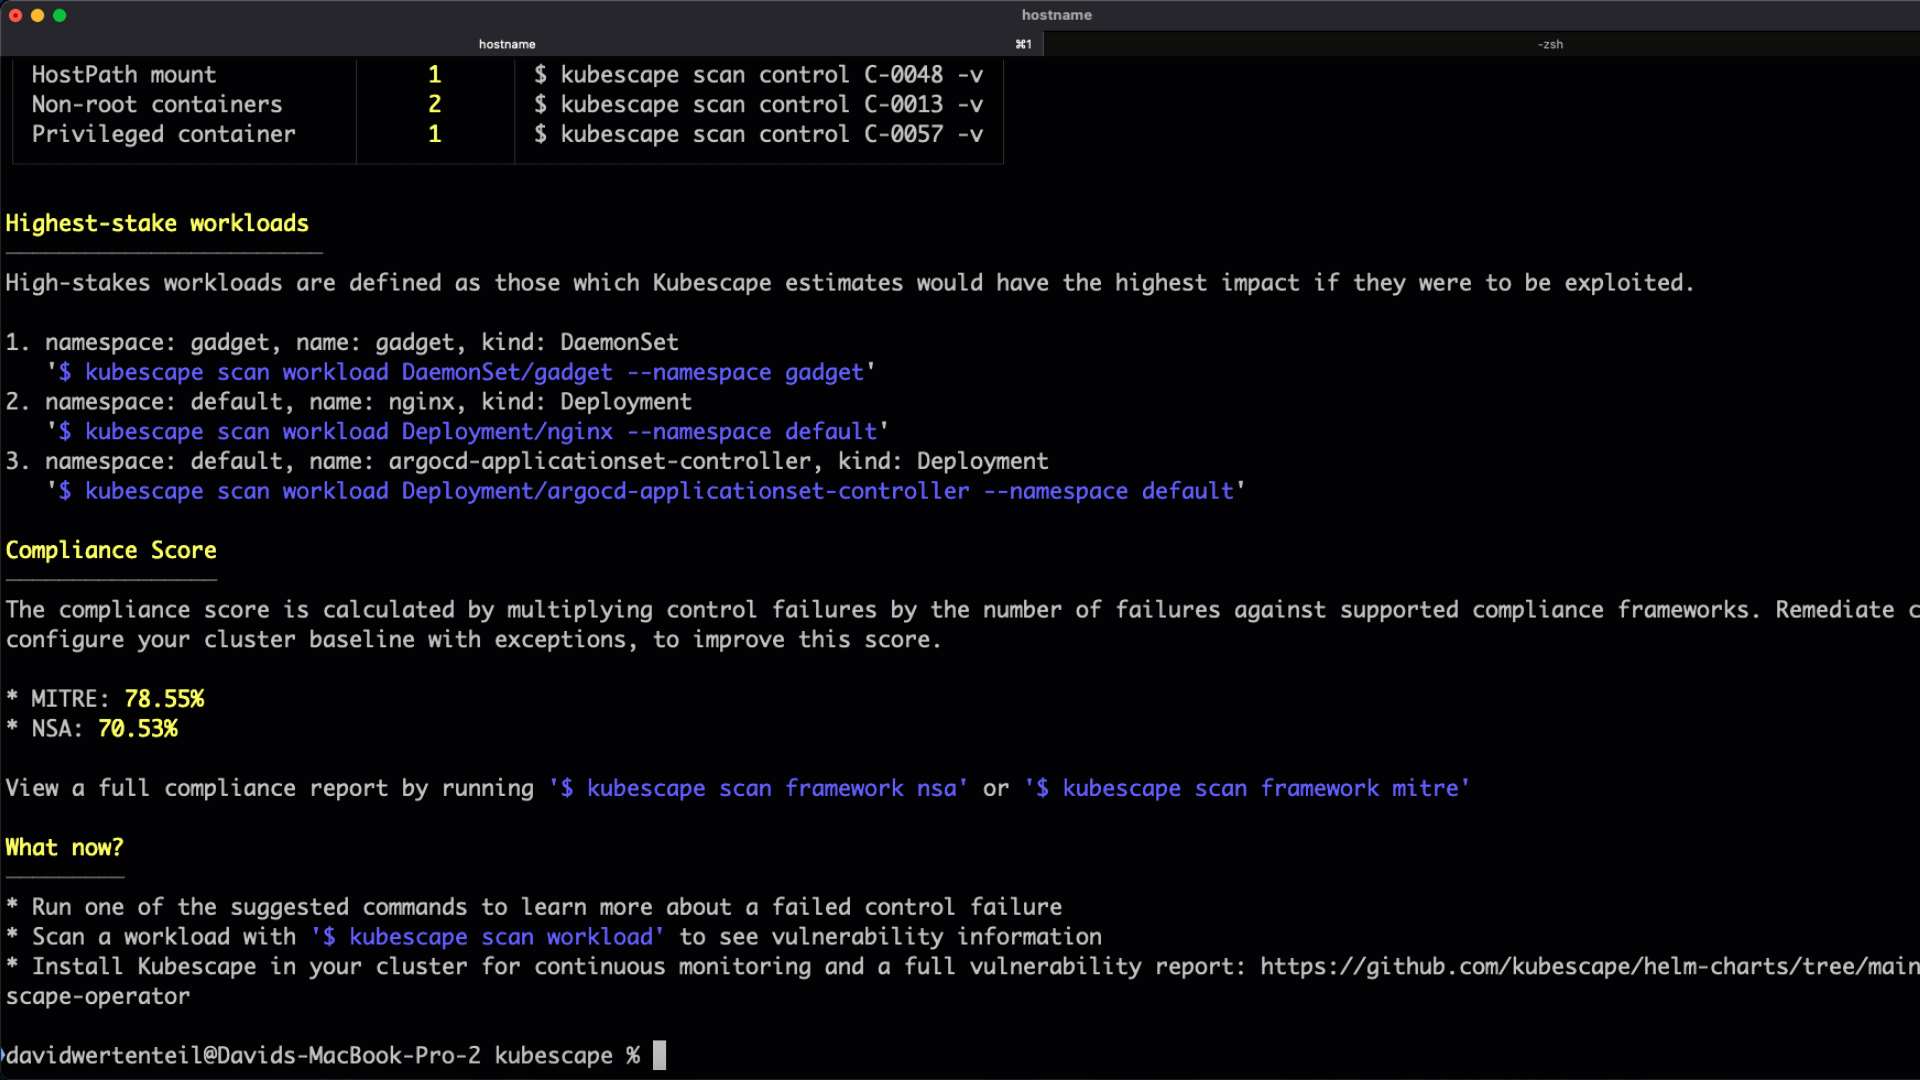 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 rderaison/bromure
Proper sandboxing for agentic coding and web browsing
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.