
mi-x
 rezilion/mi-x
Determine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
configuration-auditingcontainer-securityvulnerability-analysis+1
141
rezilion/mi-xDetermine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 liske/needrestart
System utility that identifies and restarts daemons using outdated libraries after package upgrades to maintain security. Supports containers and…
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 opsxcq/exploit-cve-2016-6515
OpenSSH remote DOS exploit and vulnerable container
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 opsxcq/exploit-cve-2016-7434
NTPD remote DOS exploit and vulnerable container
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 vin01/poc-cve-2024-38396
PoC for iTerm2 CVEs CVE-2024-38396 and CVE-2024-38395 which allow code execution
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 rhysemmas/martian-packets
Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC
 yen5004/cve-2024-40635_poc
Proof of Concept code for proving CVE-2024-40635 vulnerability
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
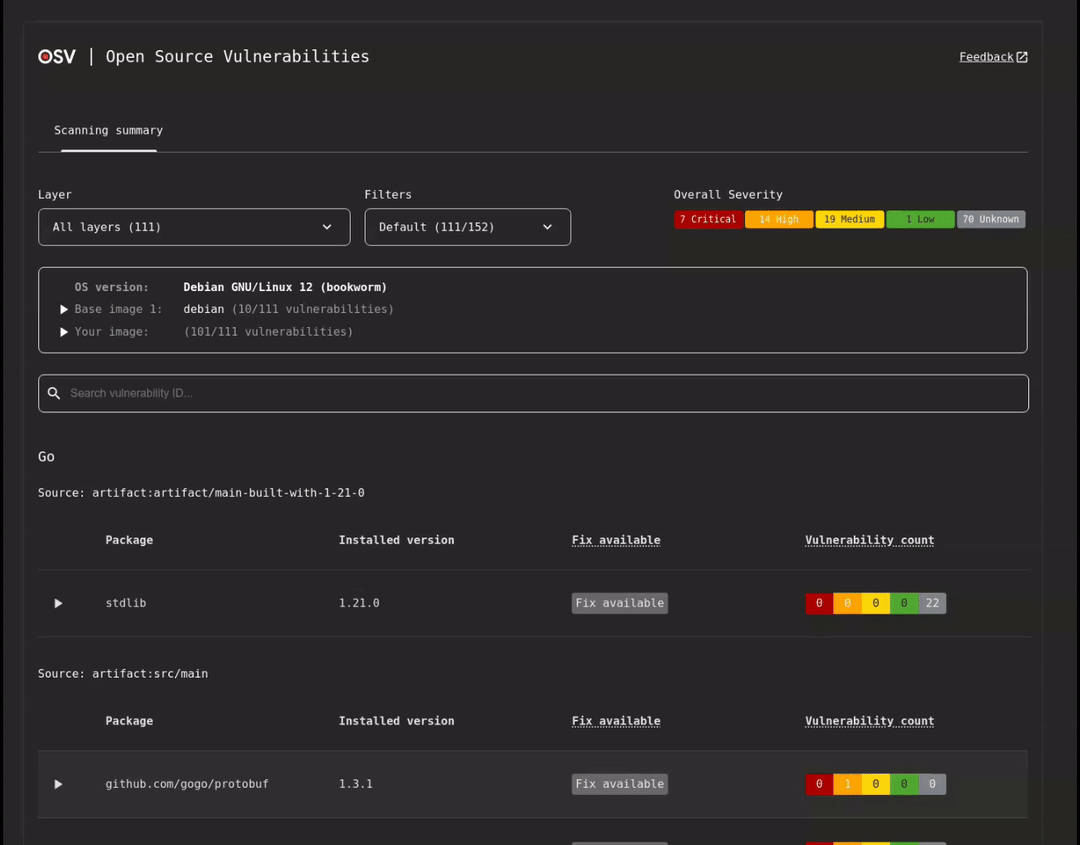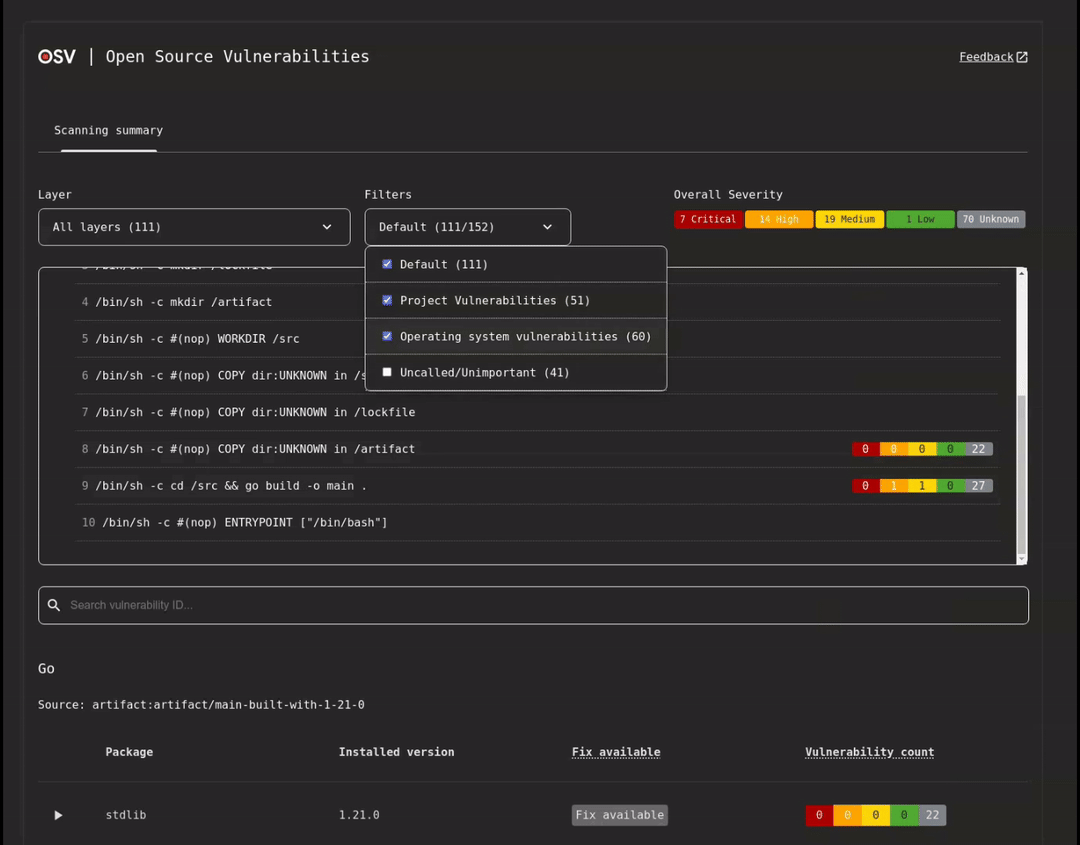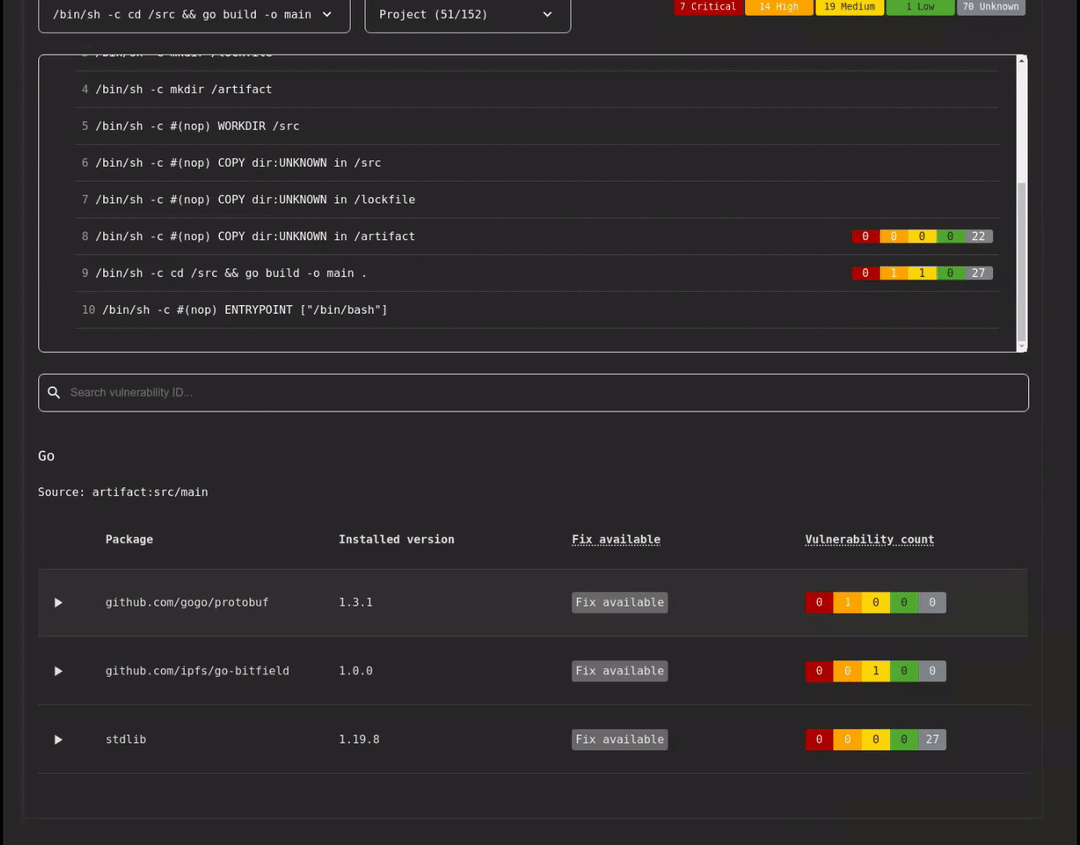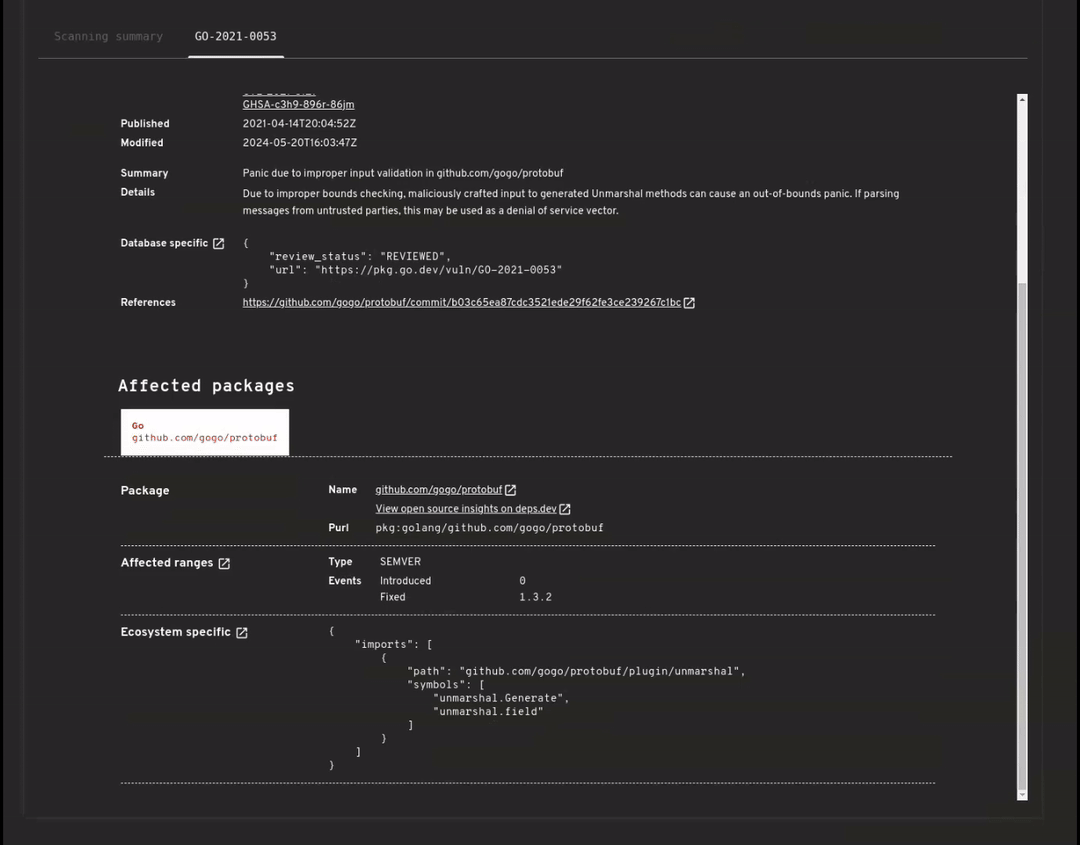 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.