
CubeSandbox
 tencentcloud/cubesandbox
Instant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
ai-securitycloud-infrastructure-securitycloud-security+4
13.1k
tencentcloud/cubesandboxInstant, Concurrent, Secure & Lightweight Sandbox for AI Agents.
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 nccgroup/wubes
Qubes containerization on Windows
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
 provos/ironcurtain
A secure* runtime for autonomous AI agents. Policy from plain-English constitutions. (*https://ironcurtain.dev)
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 grepular/foxcage
Run Firefox in a rootless Podman container with dropped capabilities, isolated networking, and ephemeral storage to contain sandbox escapes and…
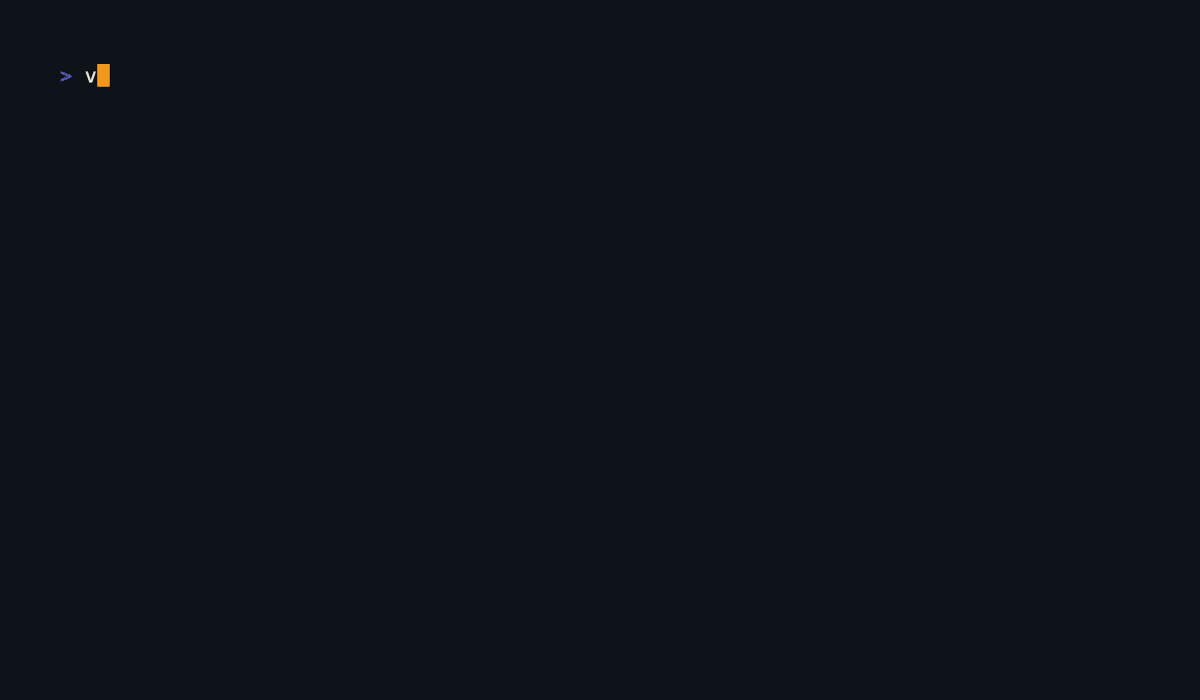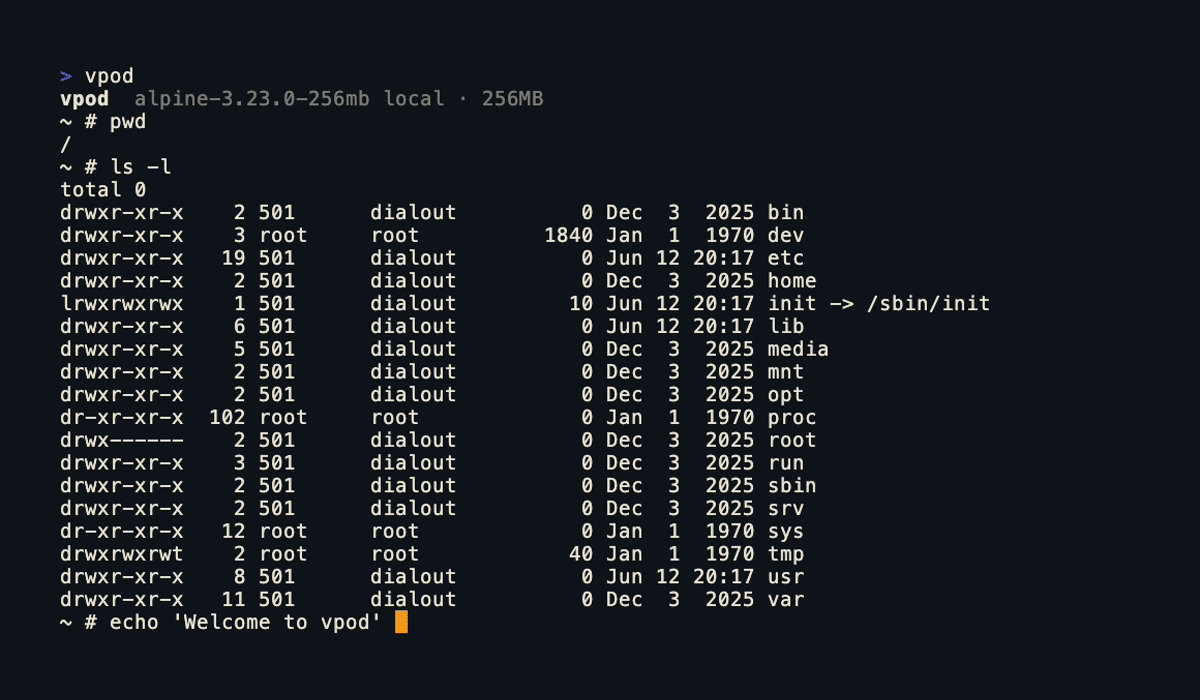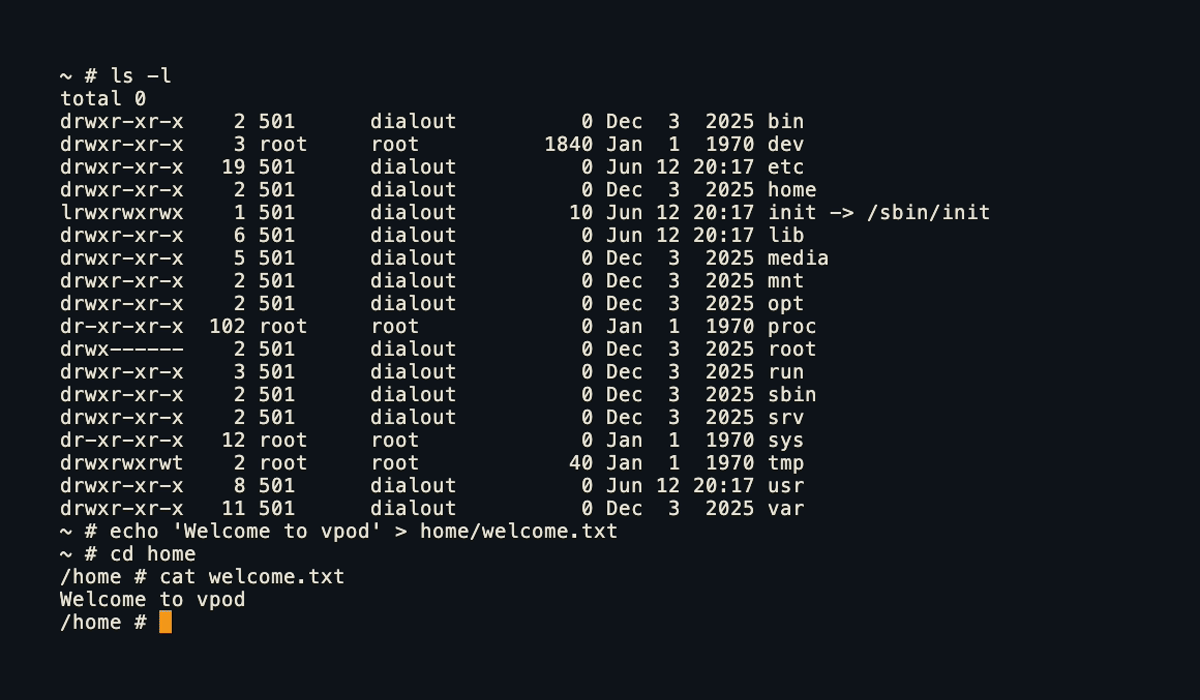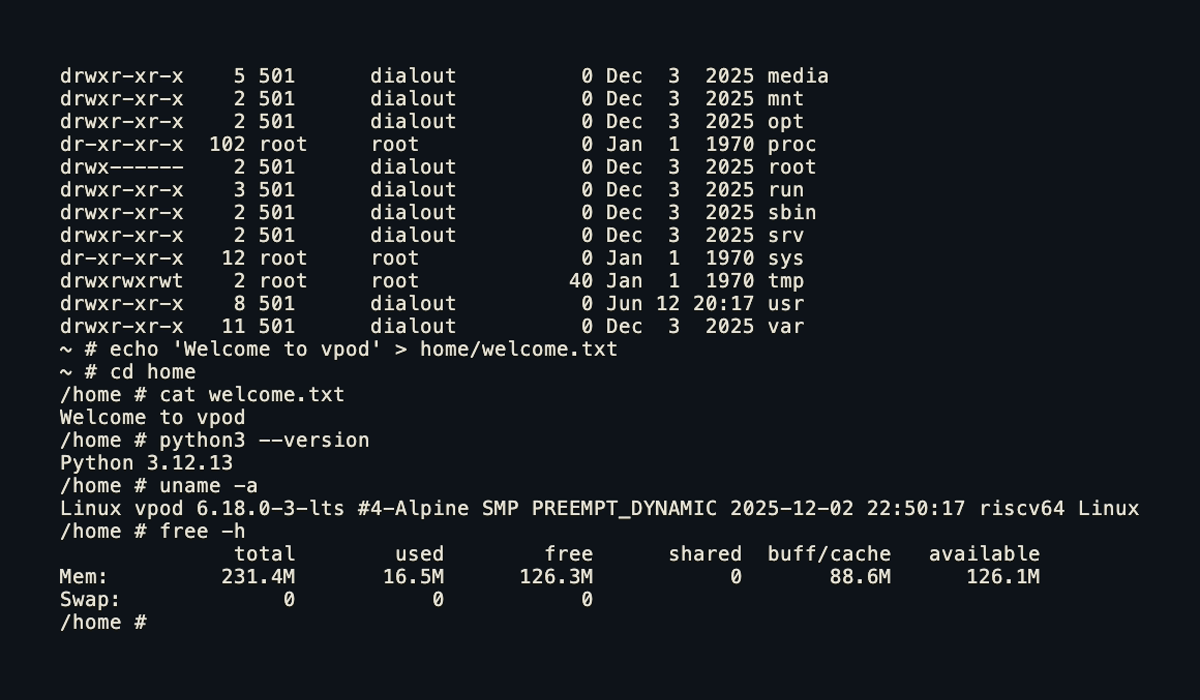 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 pwnfunction/sandbox
Run untrusted AI code safely, fast
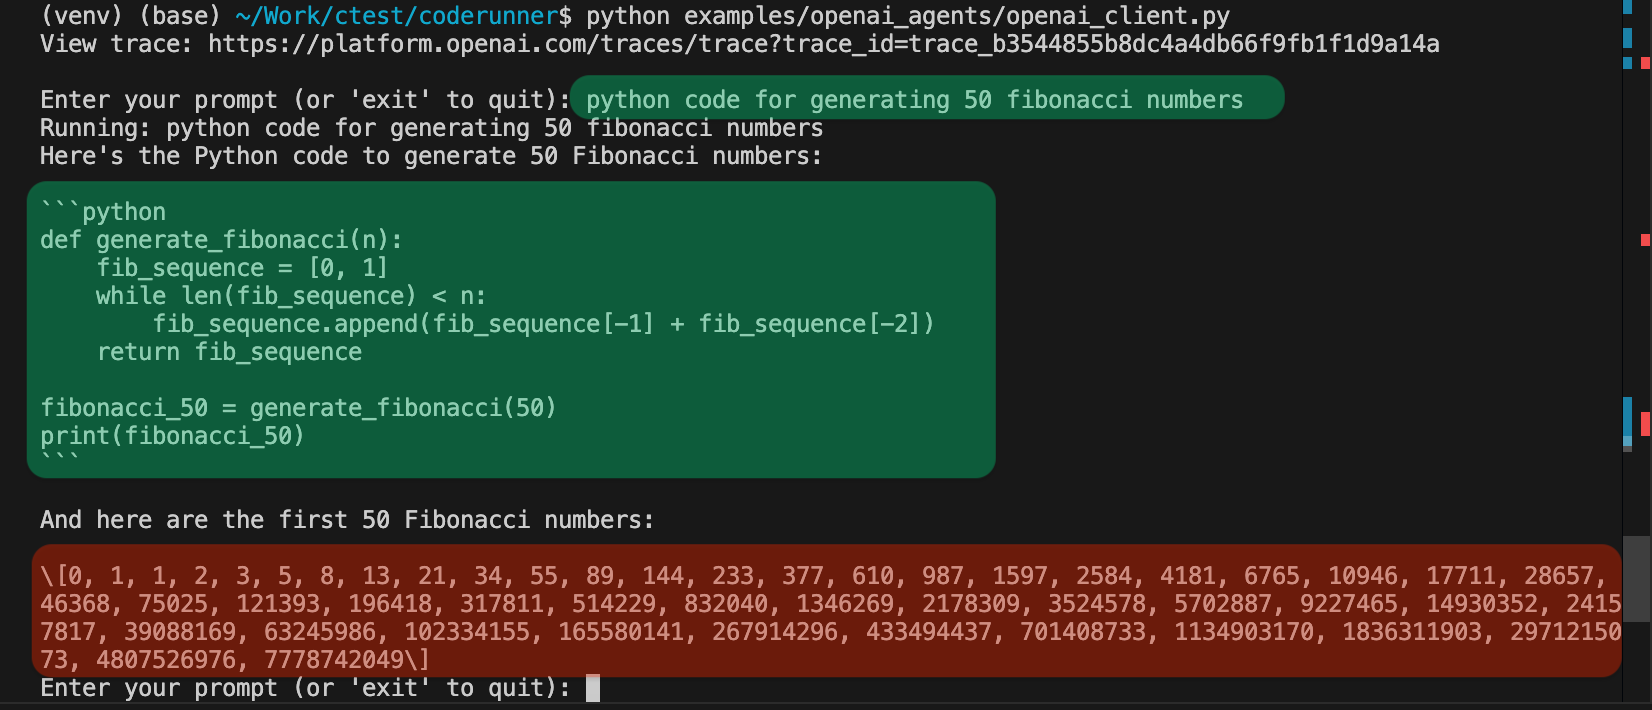 instavm/coderunner
A local sandbox for your AI agents