
limeyard
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
container-securitydevsecopsdns-subdomain-enumeration+8
1
clickswave/limeyardDeliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
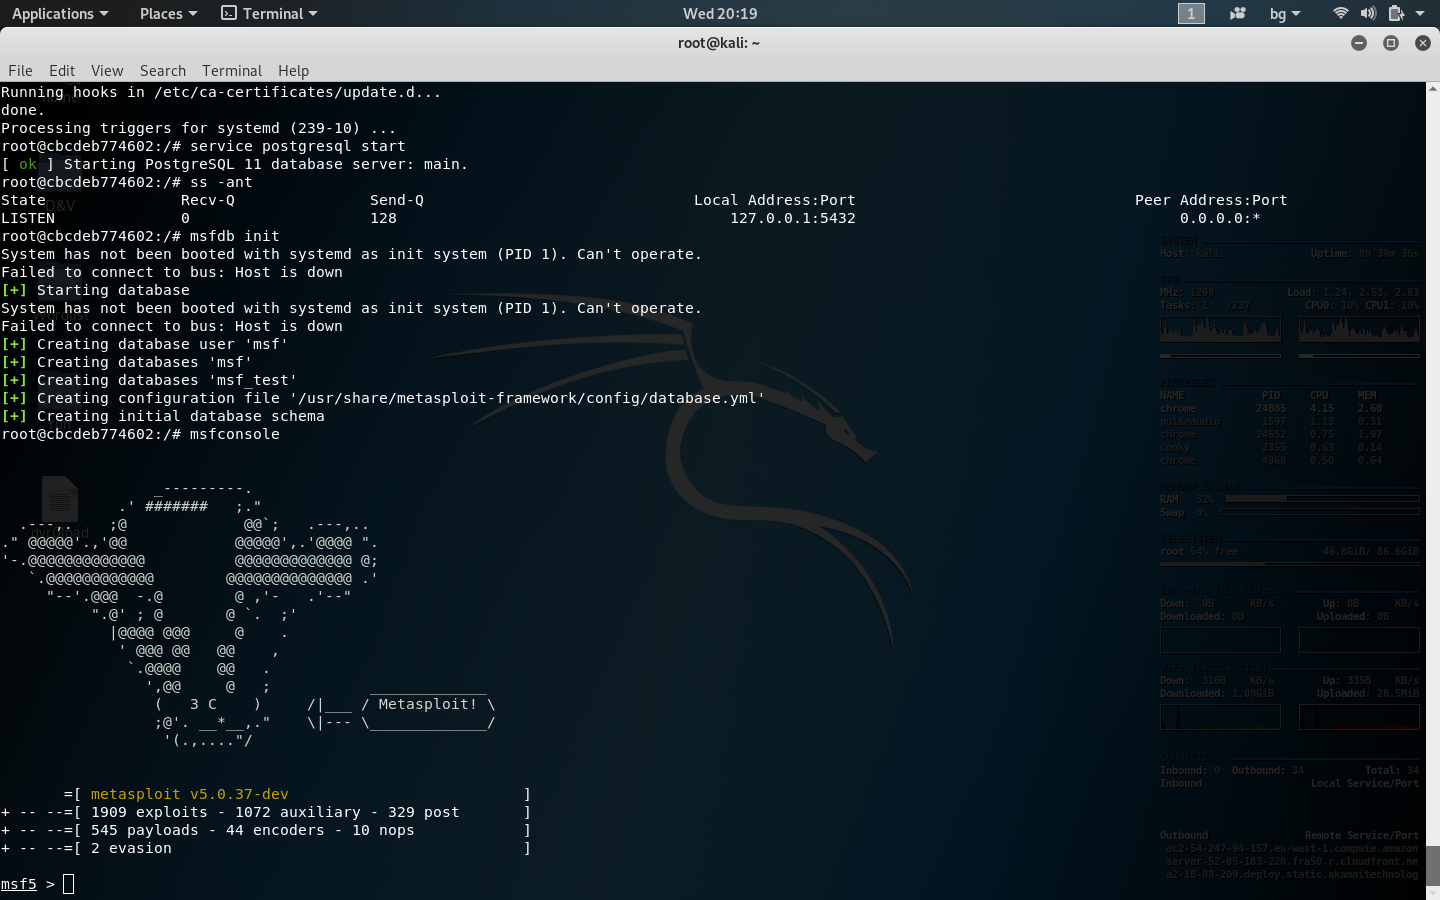 nu11secur1ty/kali-linux-docker
kali-linux-docker
 projectdiscovery/pd-agent
ProjectDiscovery Cloud - Agent
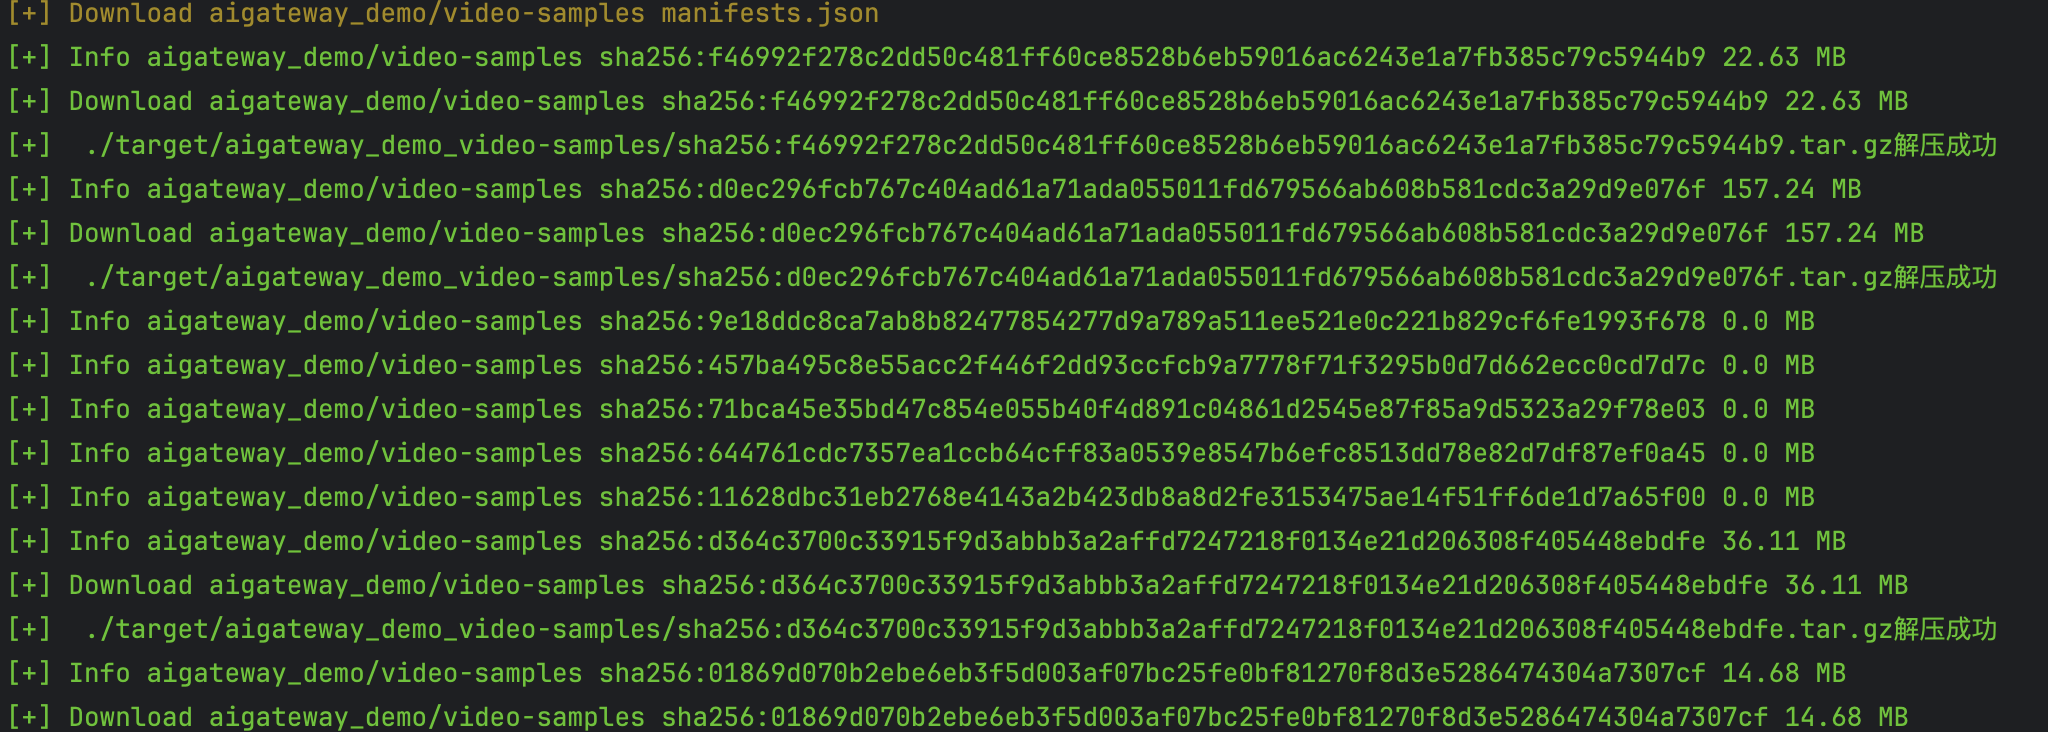 codesecurityteam/harbor
CVE-2022-46463 harbor公开镜像全自动下载脚本
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 lijiejie/log4j2_vul_local_scanner
Log4j 漏洞本地检测脚本。 Scan all java processes on your host to check whether it's affected by log4j2 remote code execution vulnerability (CVE-2021-45046)
 raj3shp/persisthunt
Linux Persistence Detection, Hunting and Artifact Collection script
 maherazzouzi/cve-2022-47952
LXC Information Disclosure vulnerability.
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 shodanwashere/boatcrash
Exploit for CVE-2019-19030 that affects Harbor versions <1.10.3 and <2.0.1. Can also be used to enumerate and pull public projects from higher…