melange
 chainguard-dev/melange
Compiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
container-securitydevsecopssupply-chain-security+1
629
chainguard-dev/melangeCompiles source code into auditable, signed APK packages using declarative pipelines for Wolfi/Alpine, with multi-architecture QEMU emulation and…
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 rhysemmas/martian-packets
Crafting raw TCP/IP packets to send to poorly configured Kubernetes servers - CVE-2020-8558 PoC
 shodanwashere/boatcrash
Exploit for CVE-2019-19030 that affects Harbor versions <1.10.3 and <2.0.1. Can also be used to enumerate and pull public projects from higher…
 greenhandatsjtu/cve-2022-0847-container-escape
CVE-2022-0847 used to achieve container escape 利用CVE-2022-0847 (Dirty Pipe) 实现容器逃逸
 cved-sources/cve-2017-10271
Docker container for CVE-2017-10271 (Oracle WebLogic RCE) used with Cved framework to manage and deploy vulnerable environments for security testing…
 cved-sources/cve-2016-8869
Dockerized vulnerable environment for CVE-2016-8869 (Joomla privilege escalation) used for security training and exploitation practice.
 axelcurmi/log4shell-docker-lab
Log4Shell (CVE-2021-44228) docker lab
 0xnemian/cve-2021-23394
Docker container to setup a vulnerable elfinder version on both nginx and apache servers. Can be used to test vulnerability POC
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
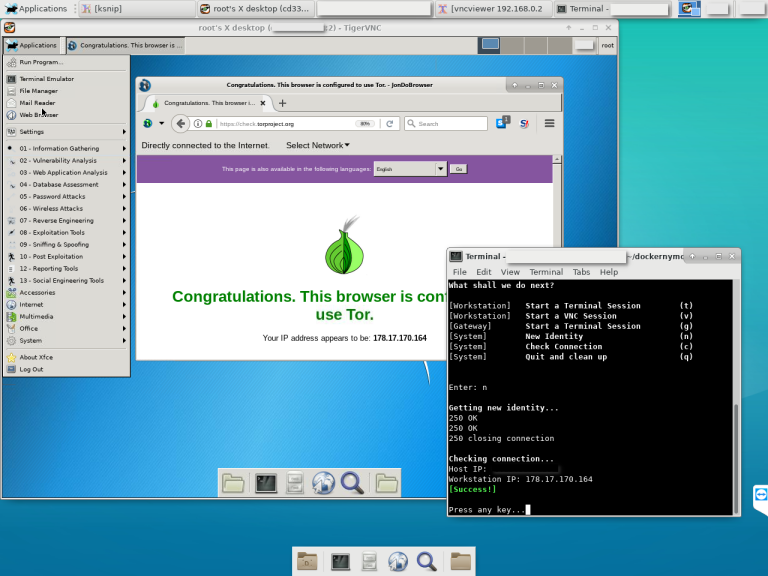 bcapptain/dockernymous
A script used to create a whonix like gateway/workstation environment with docker containers.
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 cyberhades/hardening-k8s-containers
Hands-on lab demonstrating Kubernetes container hardening by comparing default vs. security-enhanced deployments of a vulnerable note-taking…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…