
kyverno
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
8.2k
kyverno/kyvernoEnforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 sysflow-telemetry/sysflow
Cloud-native system telemetry pipeline that collects, processes, and exports system call events into a compact object-relational format for…
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 bombinisecurity/bombini
eBPF Security Monitoring and Sandboxing Agent Based on Aya
 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
 fabriziosalmi/tanstack-compromise-checker
Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)
 cr0nx/awesome-linux-attack-forensics-purplelabs
This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 nanocoai/nanoclaw
A lightweight alternative to OpenClaw that runs in containers for security. Connects to WhatsApp, Telegram, Slack, Discord, Gmail and other messaging…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 eeriedusk/nysm
eBPF-based stealth container that hides processes, sockets, eBPF objects, and audit logs from system monitoring tools, enabling covert…
 owasp/owasp-ctf
Self-hosted CTF control plane for security-learning events: team registration, live leaderboard, and patch-to-score, quiz, jeopardy, and AI challenge…
 lightspin-tech/red-kube
Red Team K8S Adversary Emulation Based on kubectl
 khast3x/redcloud
Automated Red Team Infrastructure deployement using Docker
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 flatpak/flatpak
Linux application sandboxing and distribution framework
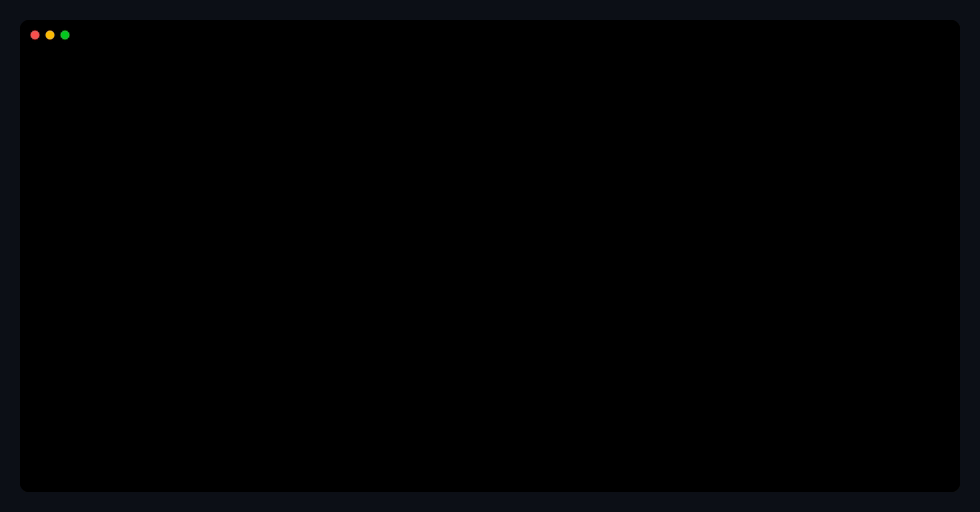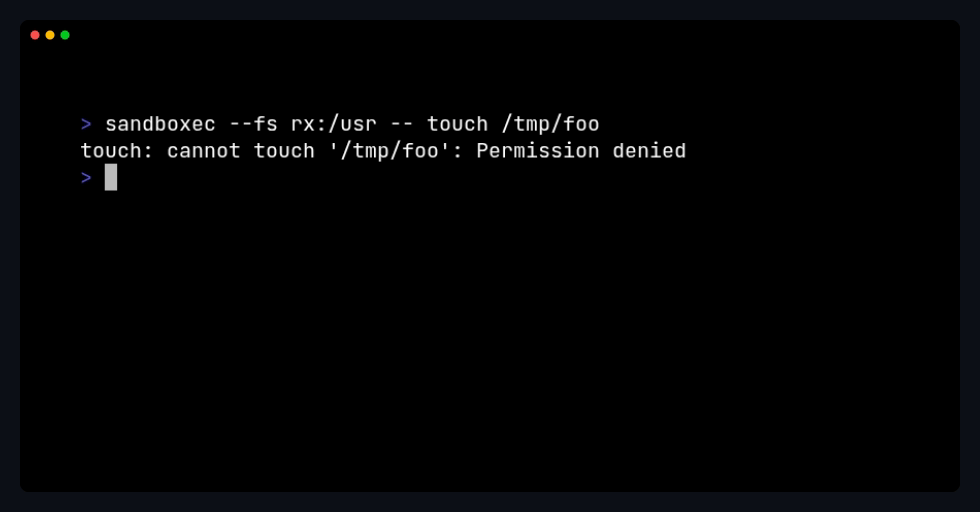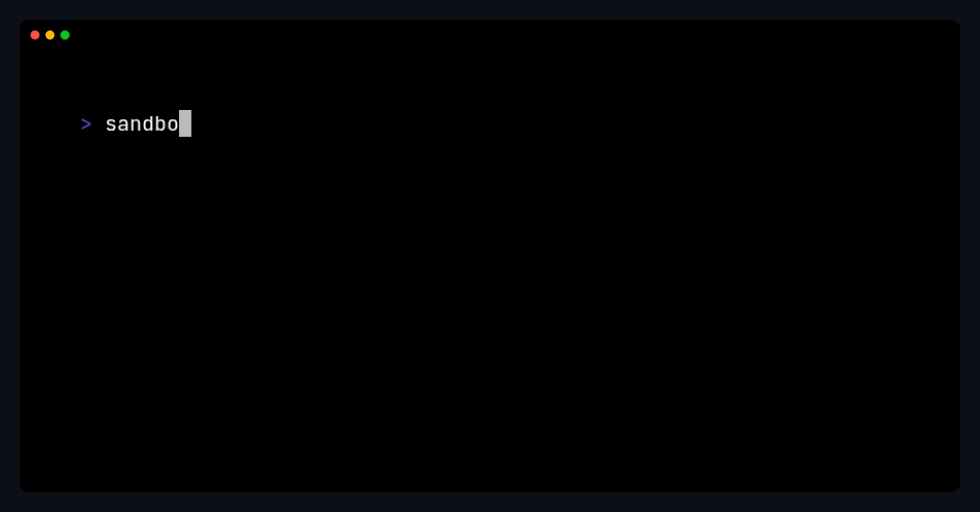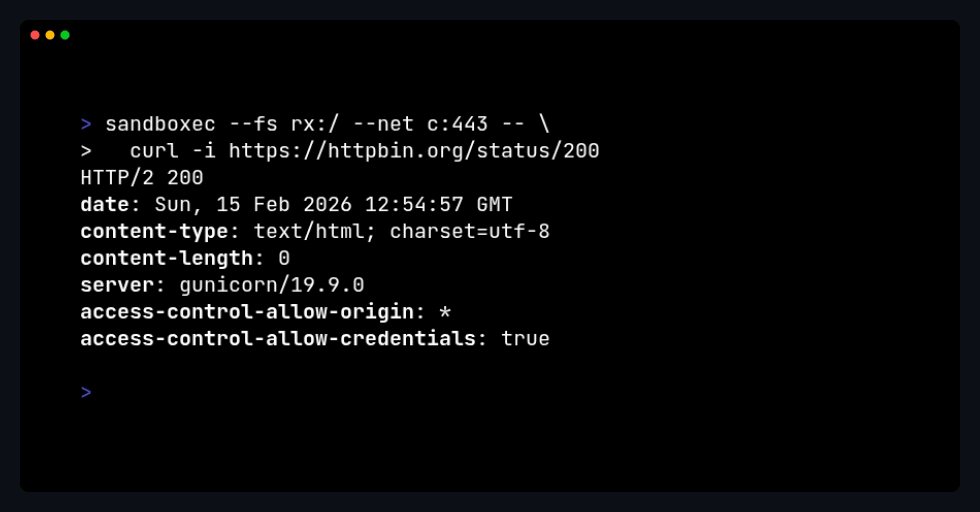 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.