

osv-scanner
 google/osv-scanner
Vulnerability scanner written in Go which uses the data provided by https://osv.dev
code-analysiscontainer-securitydevsecops+4
10.8k11h 47m ago
google/osv-scannerVulnerability scanner written in Go which uses the data provided by https://osv.dev
 metarget/k0otkit
k0otkit is a universal post-penetration technique which could be used in penetrations against Kubernetes clusters.
 videns/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
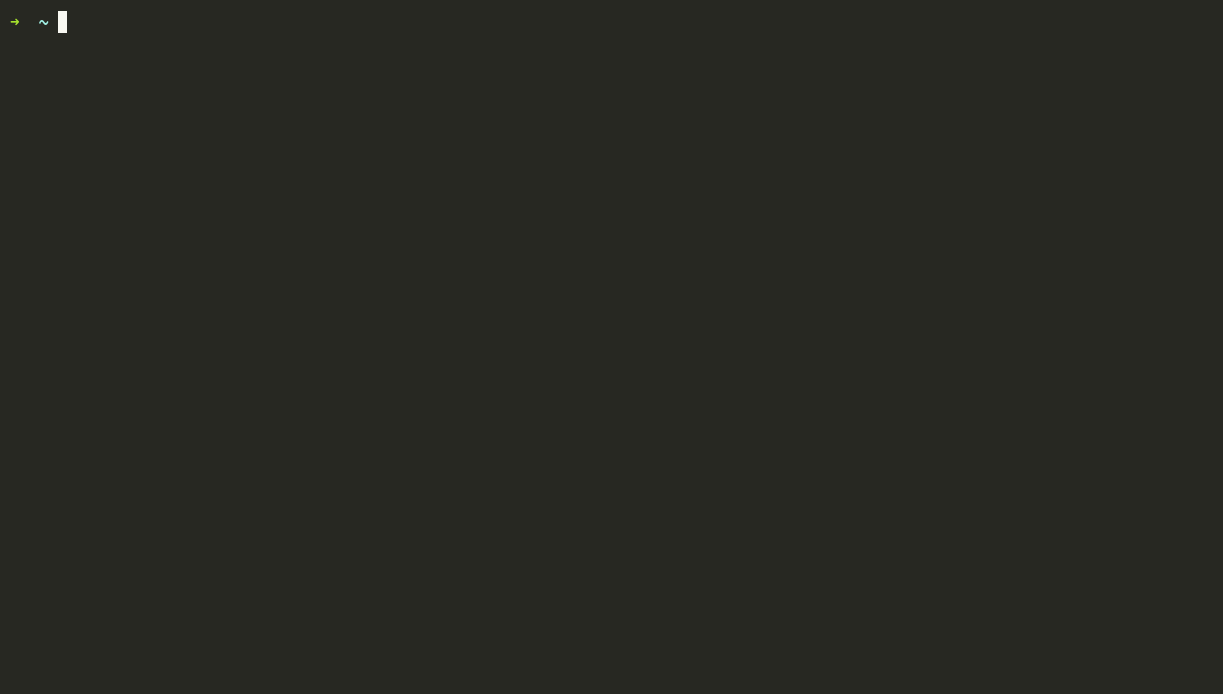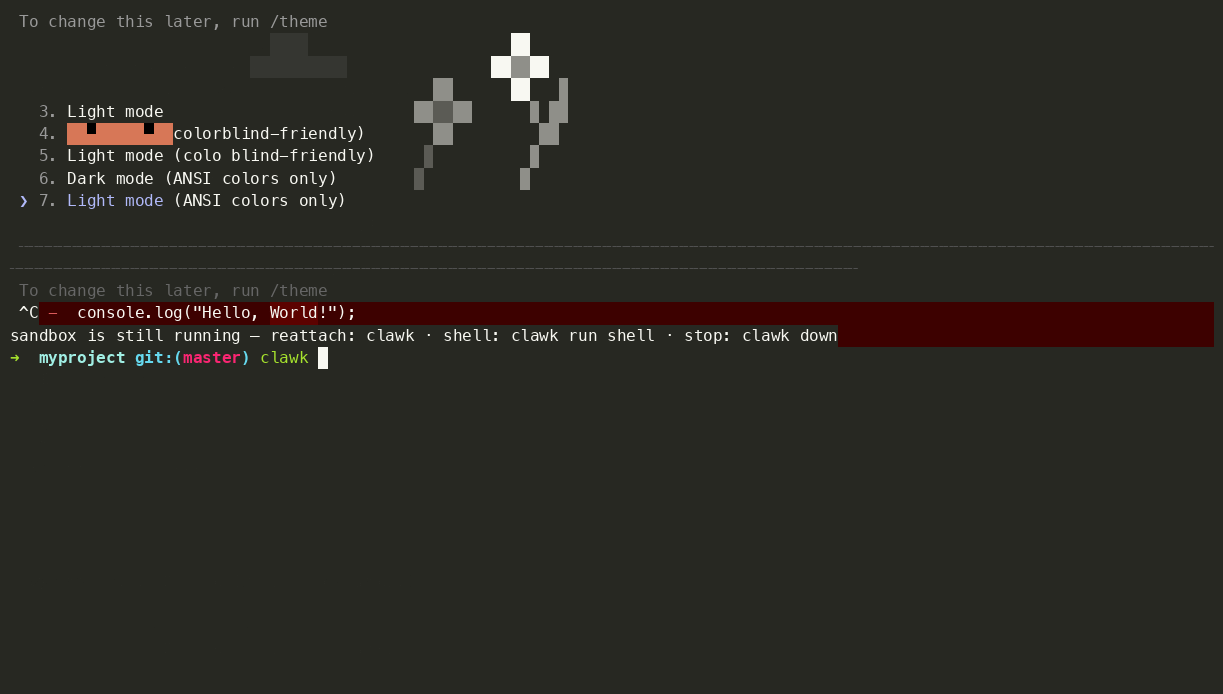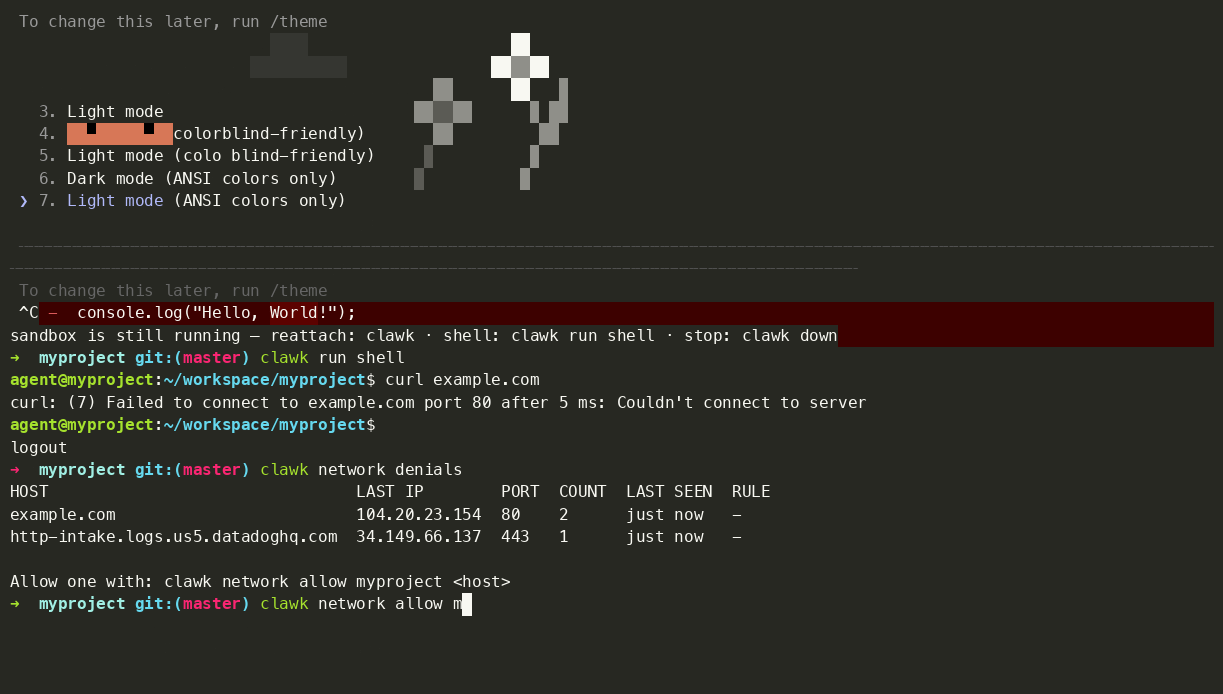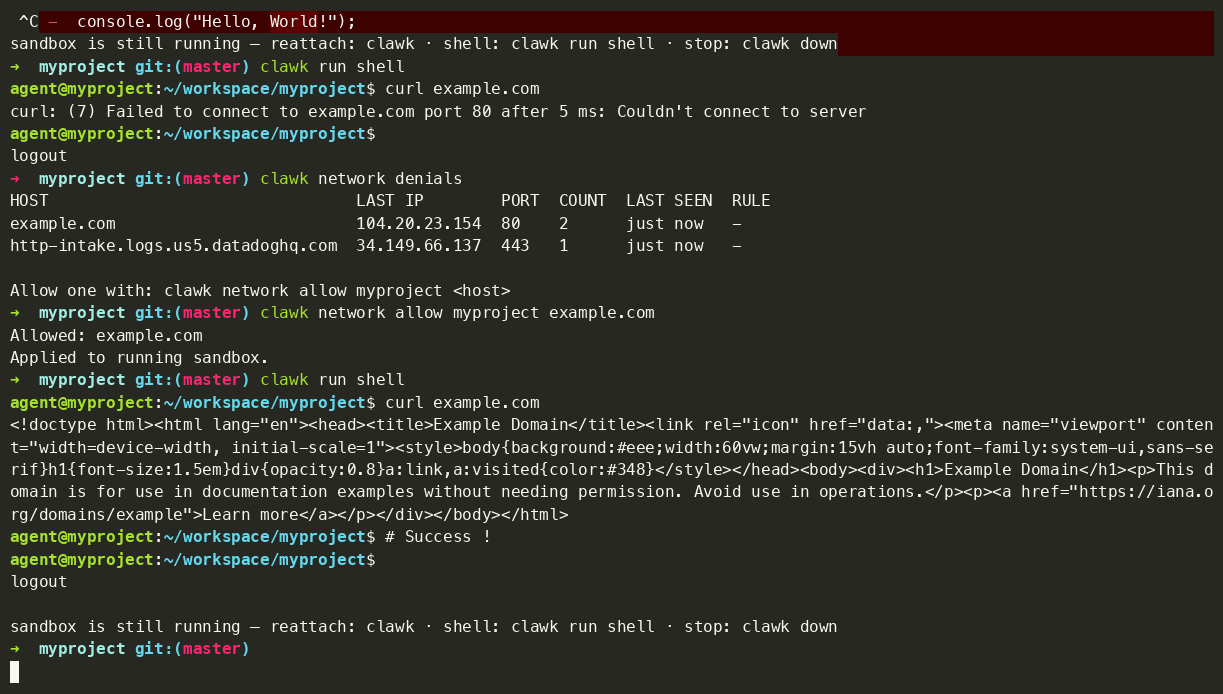 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
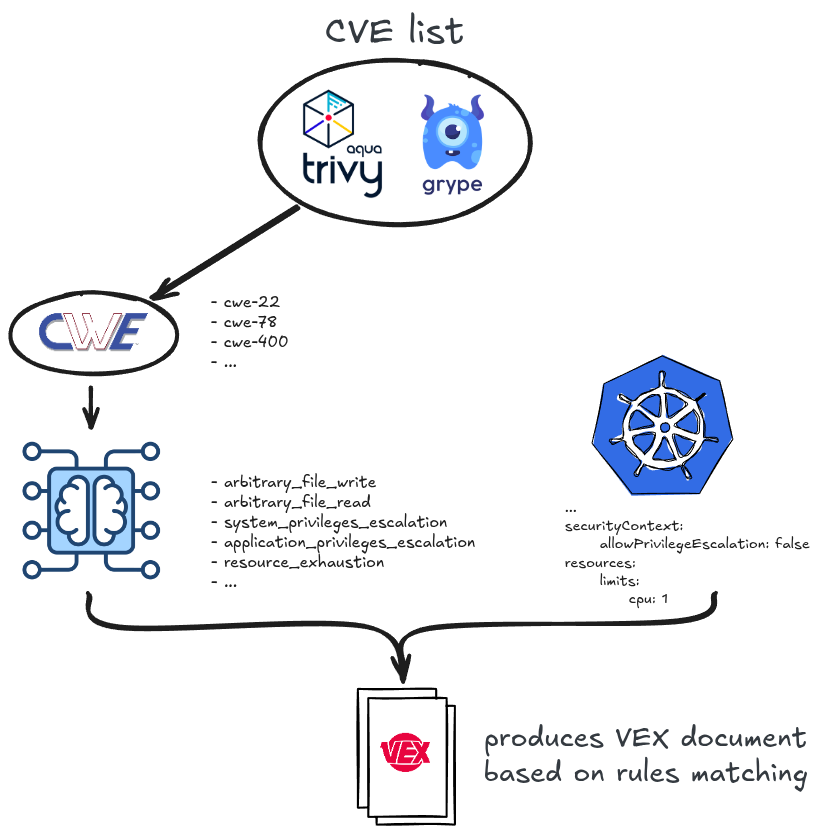 alegrey91/vex8s
Suppress vulnerabilities applying Kubernetes context to scans
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 linnix-os/linnix
eBPF-powered Linux observability with AI incident detection. AGPL-3.0 licensed.
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
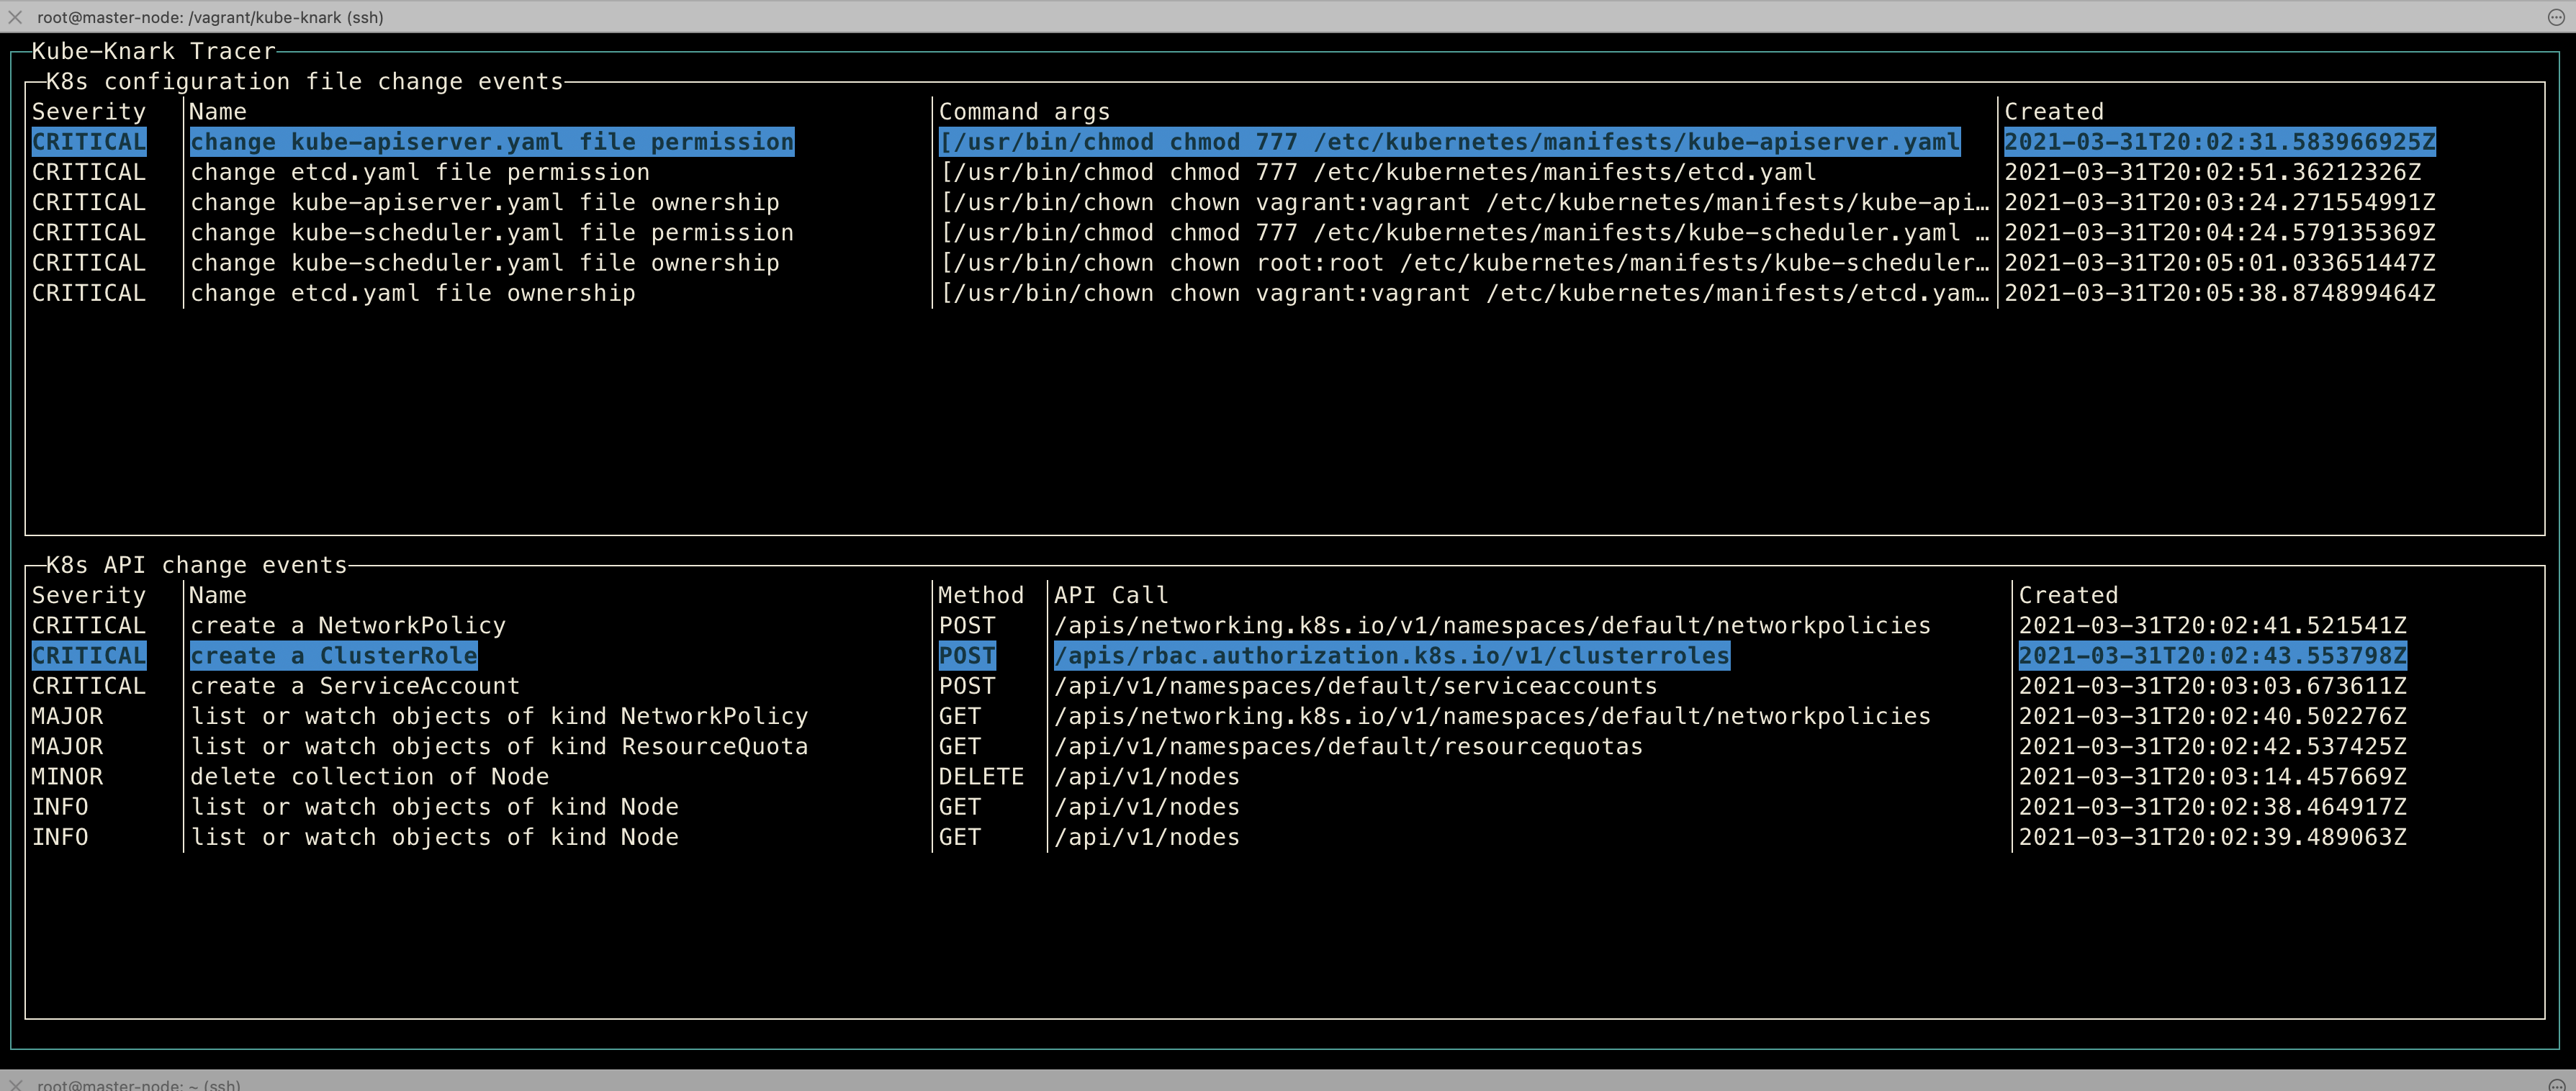 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 george0papasotiriou/cve-2026-21005-docker-registry-v2-schema-1-image-poisoning
Exploits CVE-2026-21005 by poisoning Docker Registry V2 Schema 1 manifests via unauthenticated pushes, enabling tag overwrite and supply-chain…
 opsxcq/exploit-cve-2014-6271
Shellshock exploit + vulnerable environment
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.