Linux-Kernel-Vulnerabilities-CVE-2026-23111

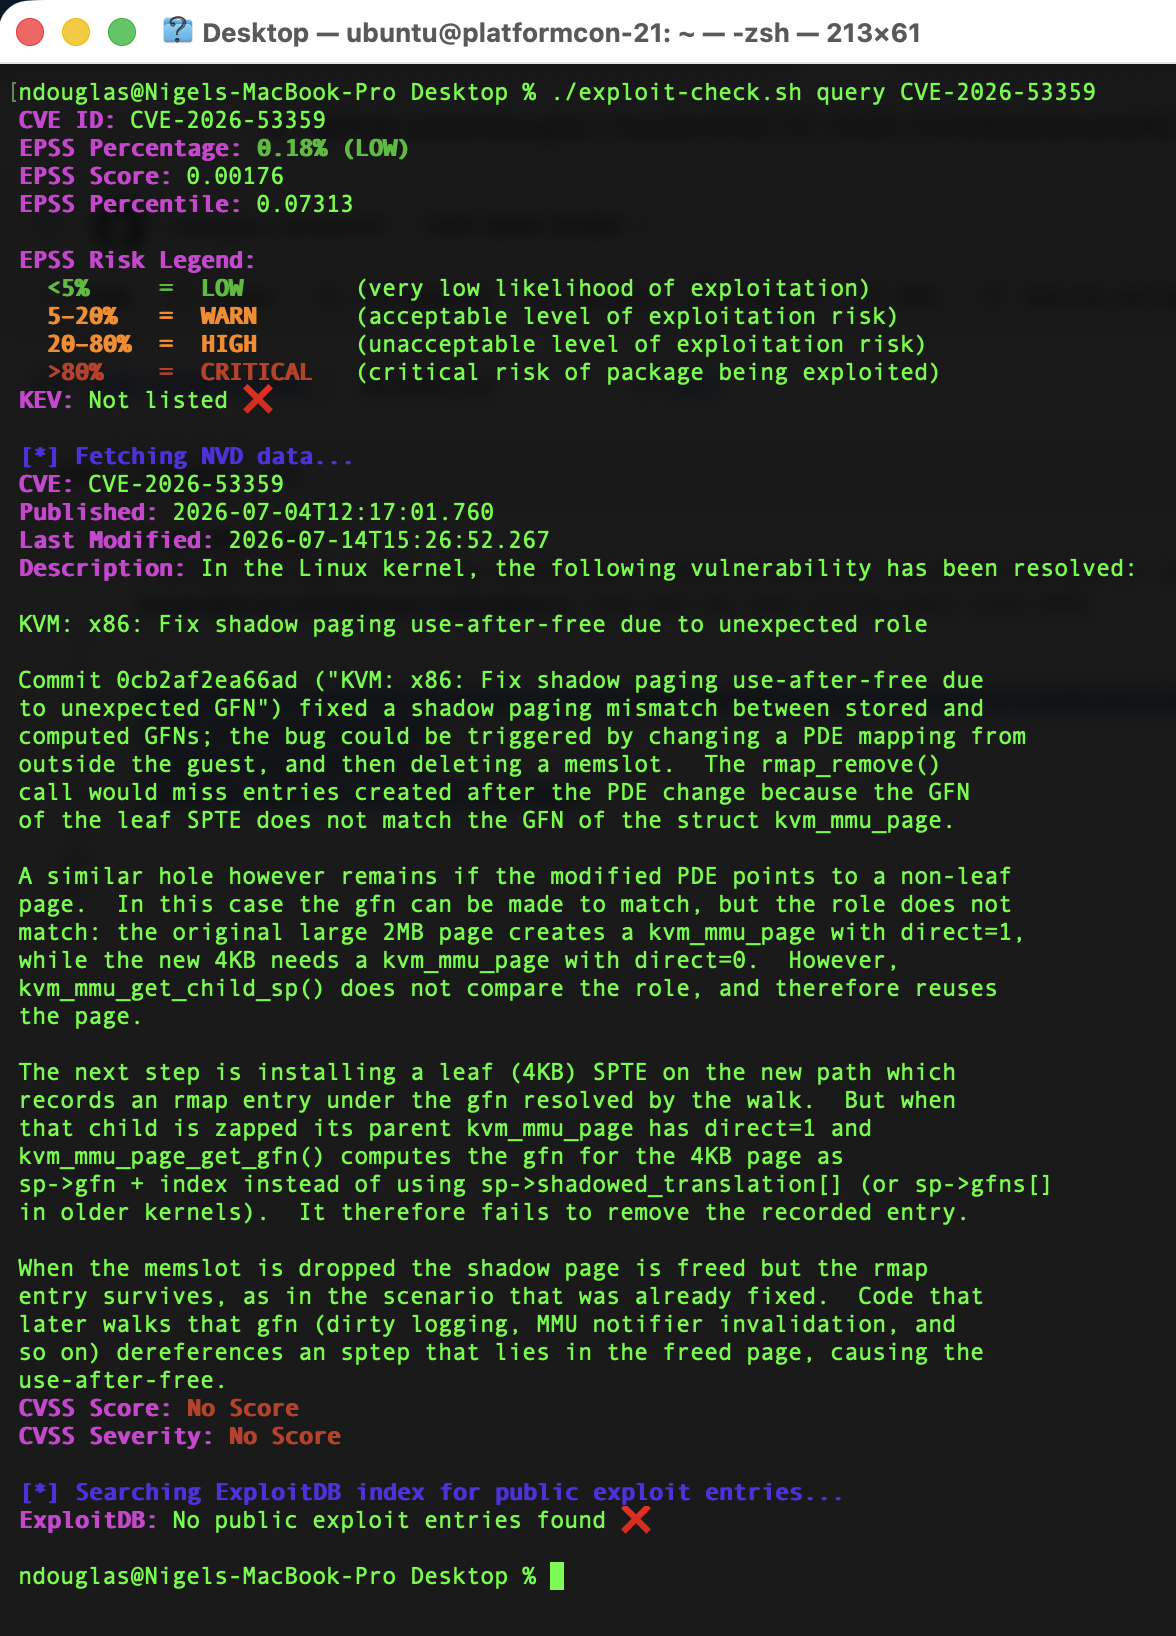
High Severity LPE vulnerability in Linux Kernel, with a CVS score of 7.8. An inverted check from user enables a process inside the container to break…

High Severity LPE vulnerability in Linux Kernel, with a CVS score of 7.8. An inverted check from user enables a process inside the container to break…

Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…

Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.

A collection of manifests that will create pods with elevated privileges.

A tool that shows detailed information about named pipes in Windows

Exploit for CVE-2019-5736: runc container escape that overwrites host docker-runc binary with a payload, triggered via docker exec.

Dockerized proof-of-concept for CVE-2024-1086, a Linux kernel privilege escalation exploit that grants root access via a crafted binary.

A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…

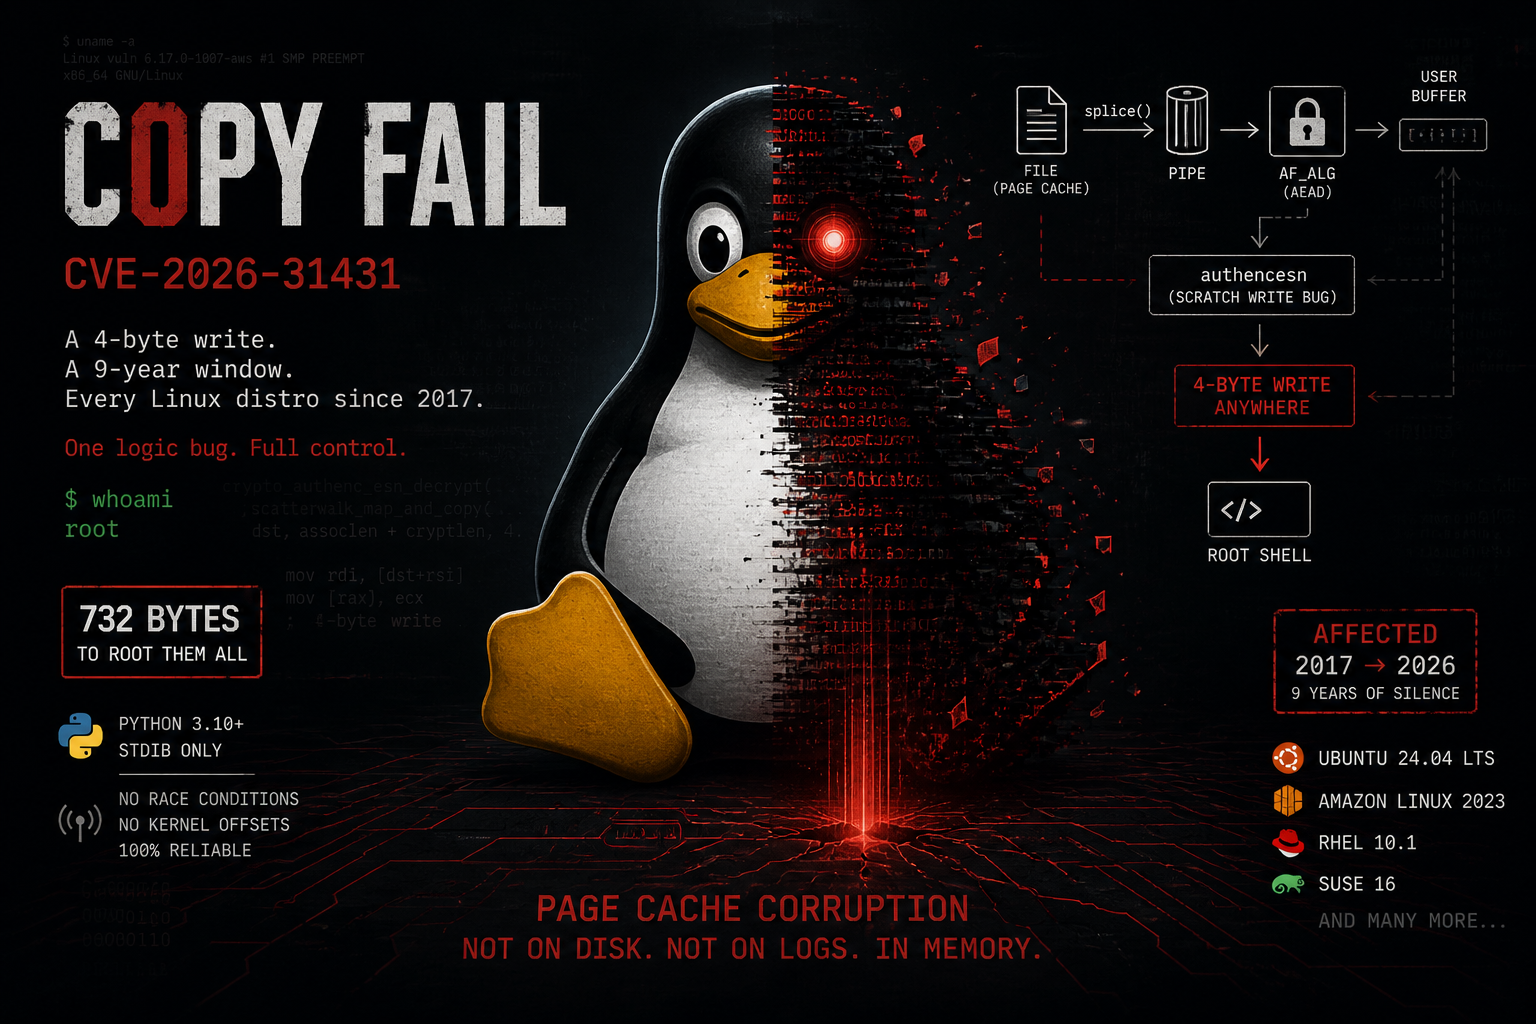
A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…

A simple exploit that uses dirtypipe to inject shellcode into runC entrypoint to implement container escapes.

Bash-based exploit script for CVE-2025-9074 that abuses the internal Docker API to mount the host C drive, execute commands inside a container, and…

C implementation of a proof-of-concept for CVE-2026-31431, a Linux kernel AF_ALG page cache poisoning vulnerability that enables local privilege…