CVE-2026-31431-RCE-Exploit

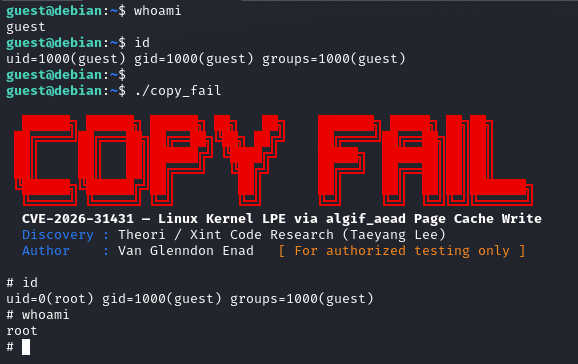
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…

Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…


Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…

📦 Make security testing of K8s, Docker, and Containerd easier.

Peirates - Kubernetes Penetration Testing tool

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…

SCTPhantom (CVE-2026-64564) SCTP ASCONF DEL-IP UAF LPE PoC (Debian 13 6.12.95) — community PoC mirror, MIT; for authorized security testing

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, demonstrating the attack and enabling security testing.

Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…

Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…

Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…

Kestra Unauthenticated RCE Exploit (CVE-2026-53576)

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

A vulnerability scanner for container images and filesystems