
CDK
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
cloud-securitycontainer-escapecontainer-security+7
cdk-team/cdk📦 Make security testing of K8s, Docker, and Containerd easier.
 b3d3c/poc-cve-2019-5736
Proof-of-concept exploit for CVE-2019-5736, a container escape vulnerability in runc, demonstrating the attack and enabling security testing.
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
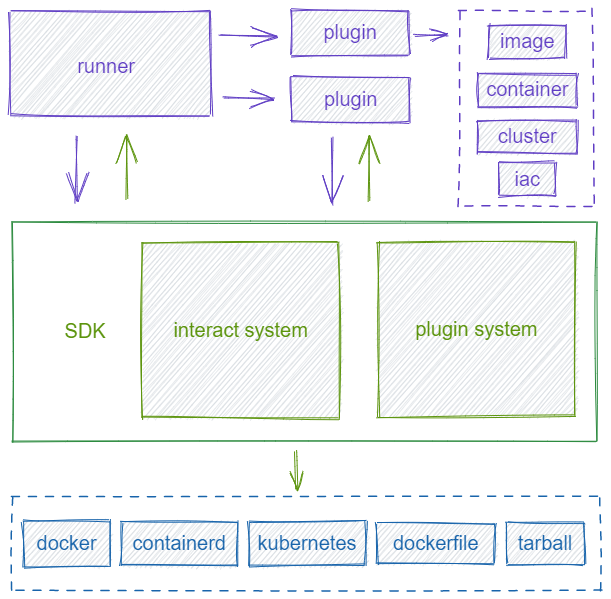 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
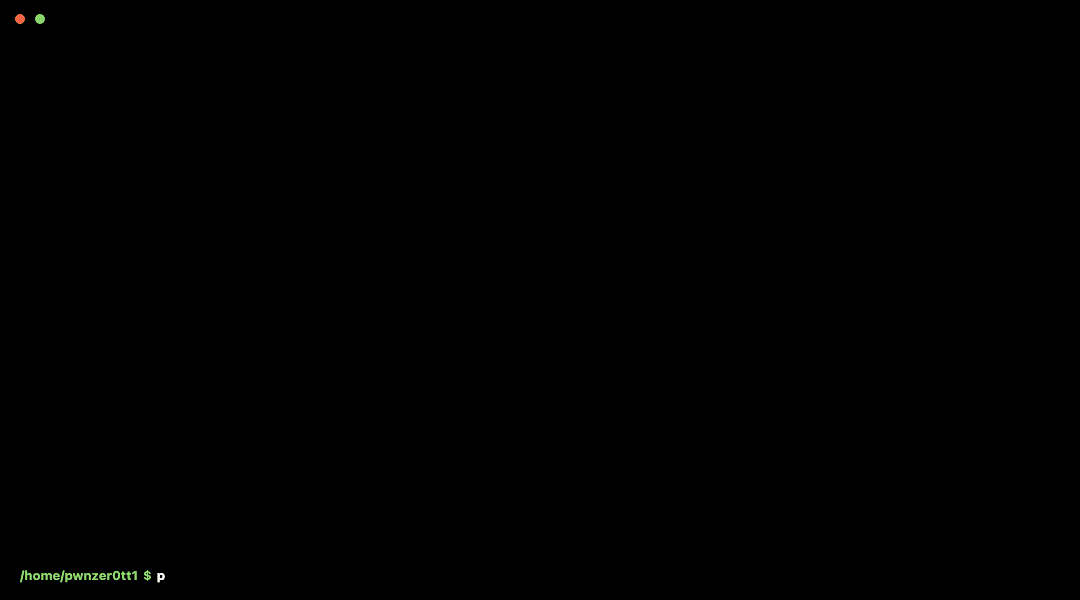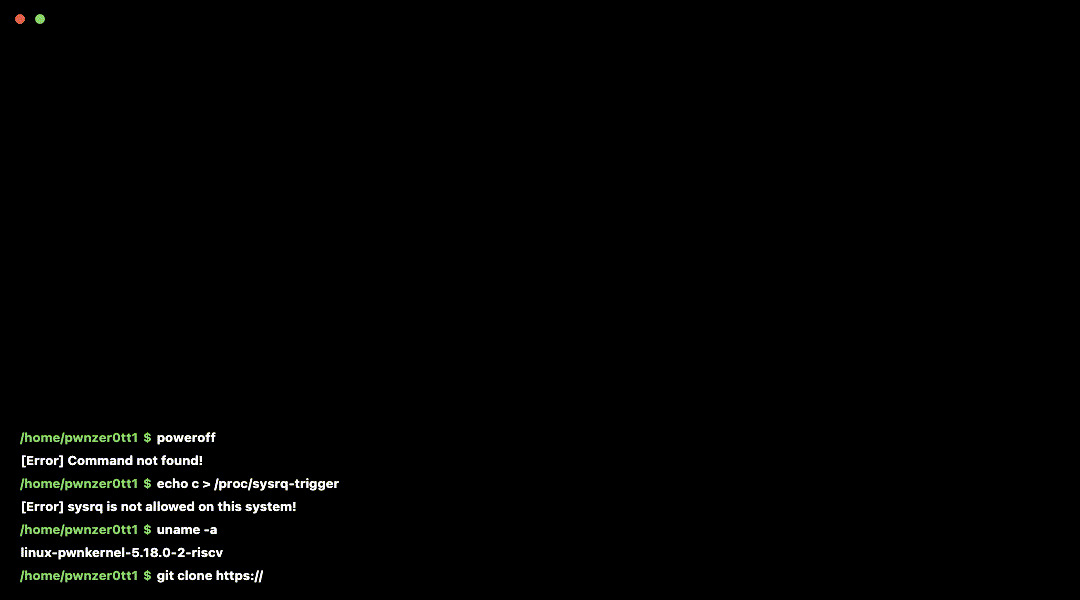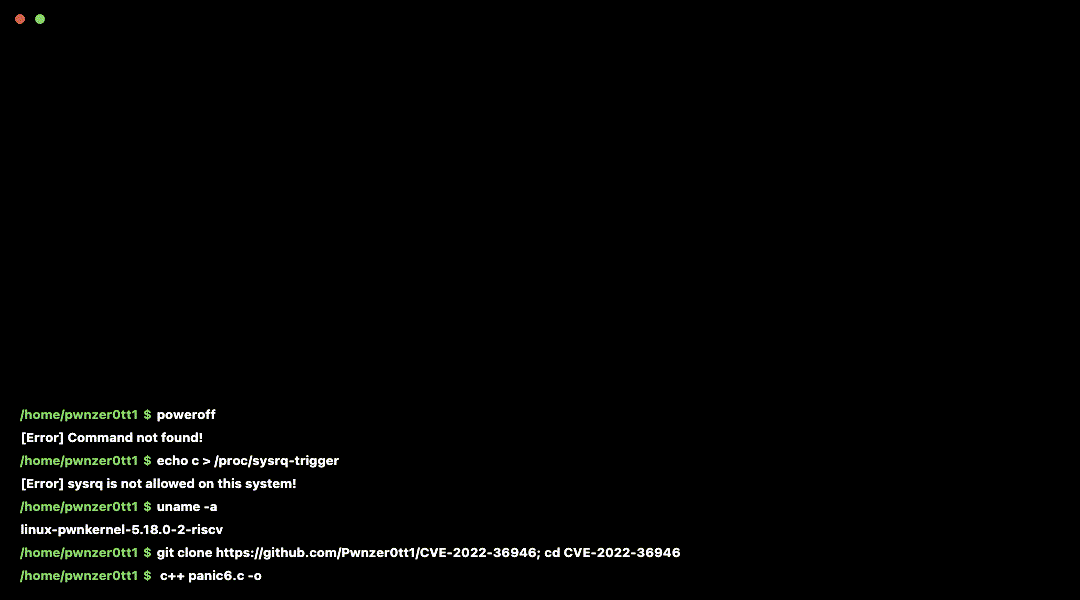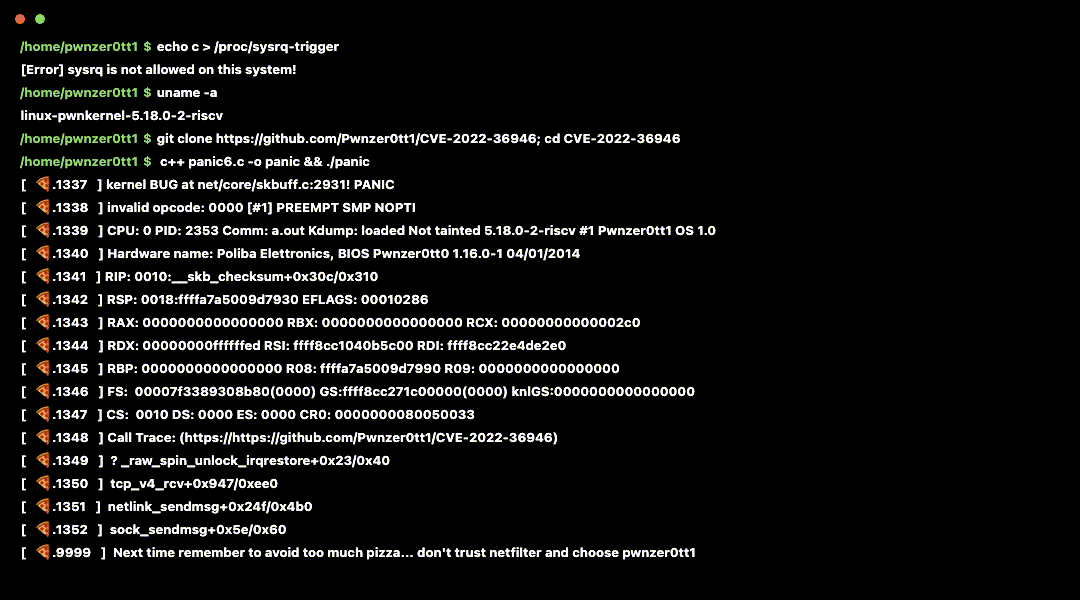 pwnzer0tt1/cve-2022-36946
CVE-2022-36946 linux kernel panic in netfilter_queue
 suominen/ipv6_frag_escape
Tracking IPV6_FRAG_ESCAPE (CVE-2026-53362, CVE-2026-53366), the IPv6 fragmentation container escape
 686f6c61/poc-copyescape-cve-2026-17106
PoC funcional de CVE-2026-17106 (CopyEscape): carrera TOCTOU en docker cp que permite escritura arbitraria en el host Docker. Laboratorio Docker +…
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
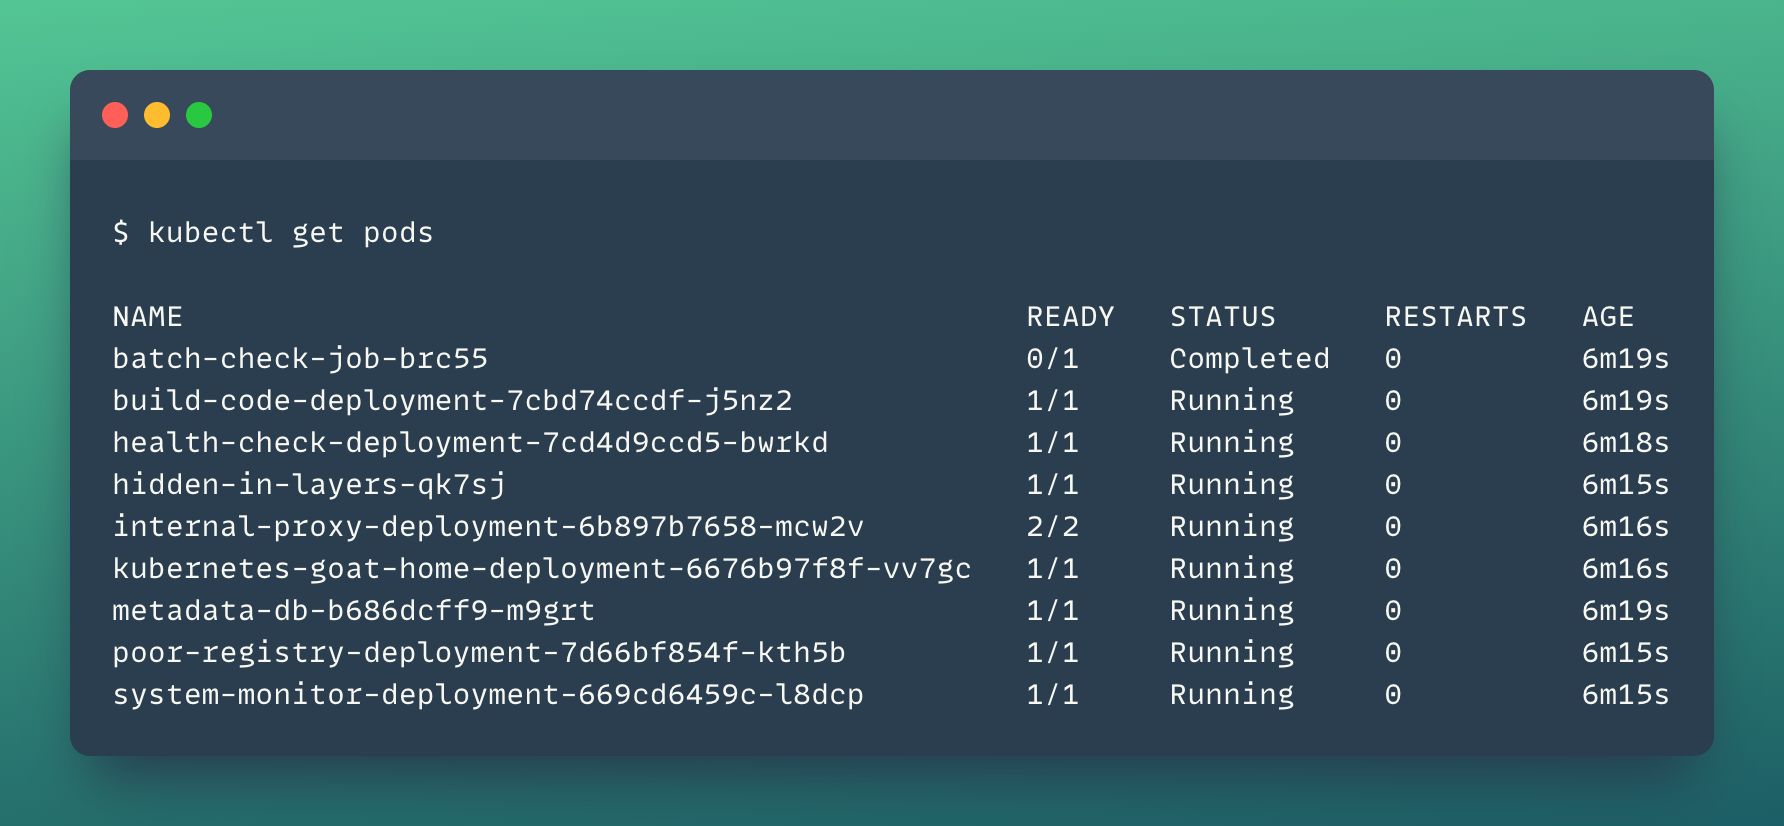 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.