

CVE-2024-21262
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
container-escapeeducationexploitation+3
noah4puppy/cve-2024-21262THREE different reproduction, WORKDIR, EXEC & RUNC.
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
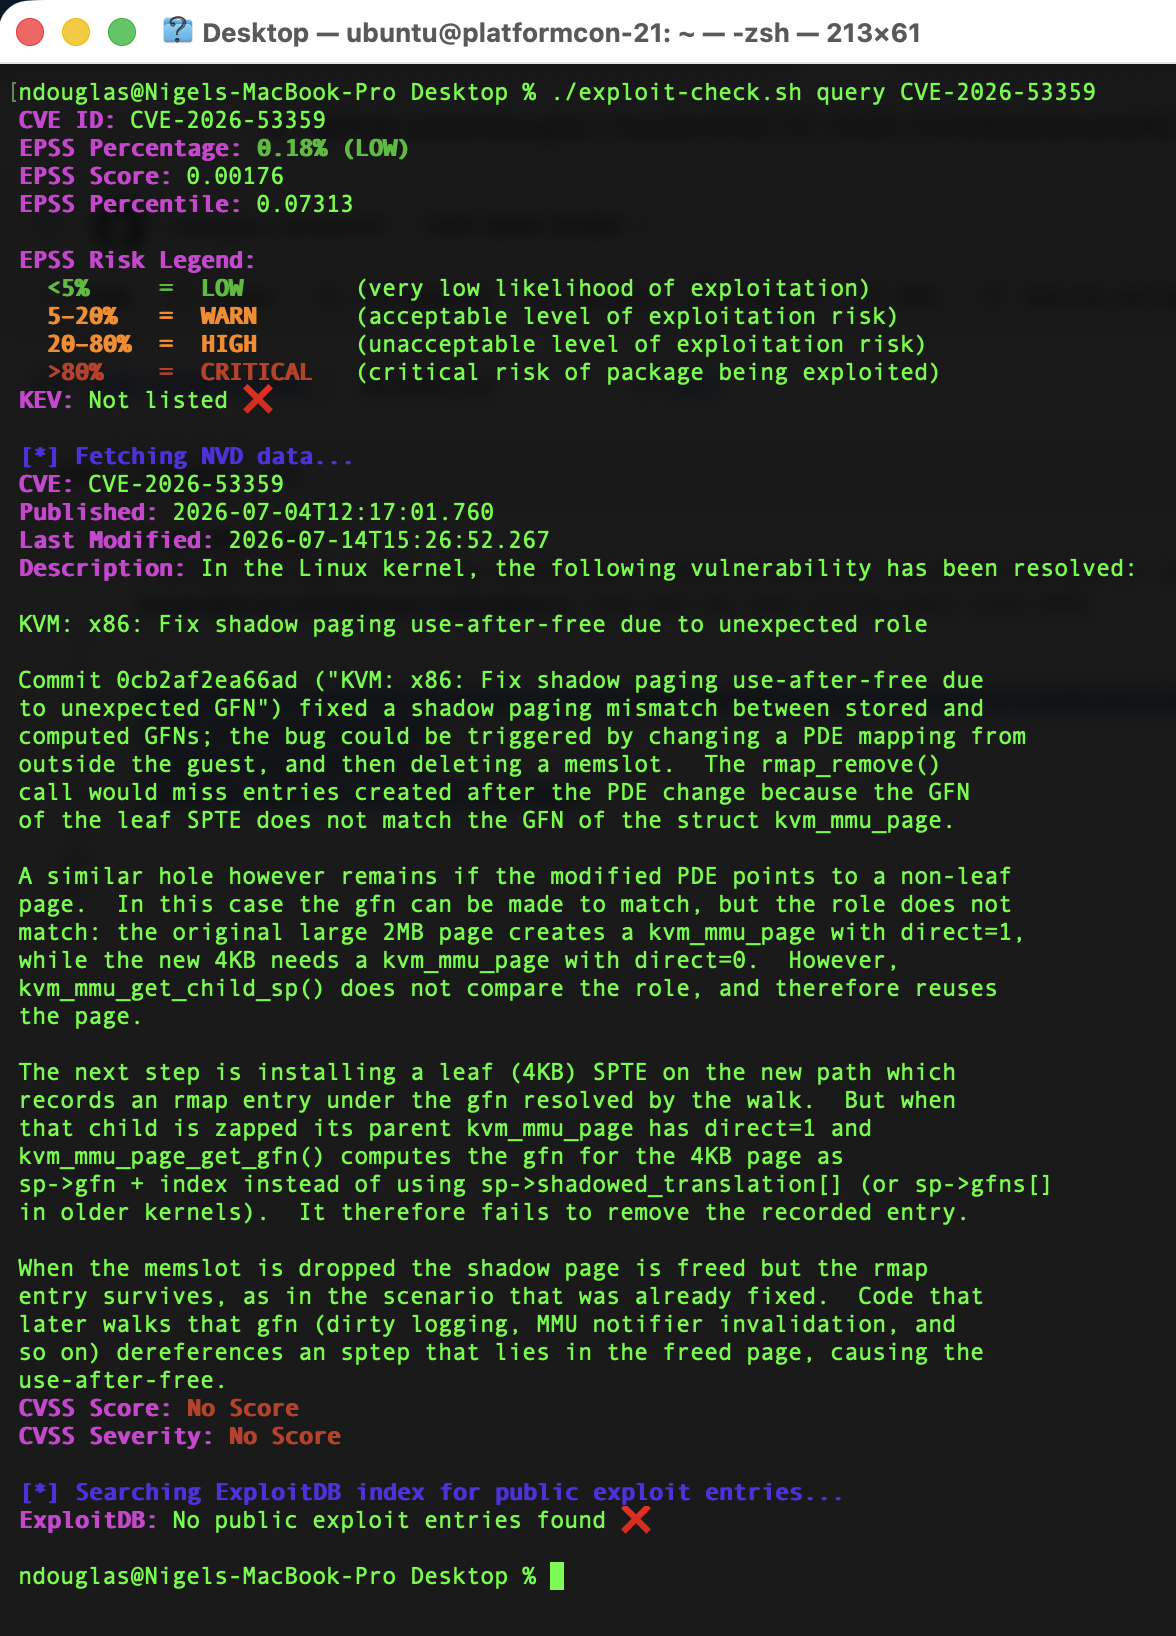 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 berdav/cve-2026-41567
Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 sonyavalo/cve-2019-5736-dockerattack-and-security-mechanism
In this project, we found a recent attack through the malicious container and implemented a security mechanism to stop it.
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 q3k/cve-2019-5736-poc
Unweaponized Proof of Concept for CVE-2019-5736 (Docker escape)
 twistlock/runc-cve-2019-5736
CVE-2019-5736 POCs