
CVE-2025-61765_PoC
 locus-x64/cve-2025-61765_poc
Proof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
container-escapeeducationexploitation+3
1
locus-x64/cve-2025-61765_pocProof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
 scumfrog/cve-2025-55130
POC for CVE-2025-55130
 0xrakan/coolify-cve-2025-66209-66213
Public security advisory for CVE-2025-66209, CVE-2025-66210, CVE-2025-66211, CVE-2025-66212, and CVE-2025-66213
 ihsansencan/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 prabeershakya/cve-2022-0185-poc
Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…
 vpr-labs/cve-2025-32463
C reimplementation of chwoot PoC
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 wenura17125/cve-2025-49131-poc
Proof-of-concept exploit for CVE-2025-49131, a sandbox escape in FastGPT allowing arbitrary file read/write, import bypass, and remote code execution…
 r4mbb/cve-2024-21626-poc
Root cuase & Proof Of Code
 zakariamaaraki/dirty-cow-cve-2016-5195-
Exploit the dirtycow vulnerability to login as root
 bbrathnayaka/poc-cve-2019-5736
Proof-of-concept exploits for CVE-2019-5736, a runC container escape vulnerability, demonstrating container breakout via malicious images and exec…
 twappz/htb-silentium-writeup
Hack The Box - Silentium machine writeup | CVE-2025-58434, CVE-2025-59528, CVE-2025-8110
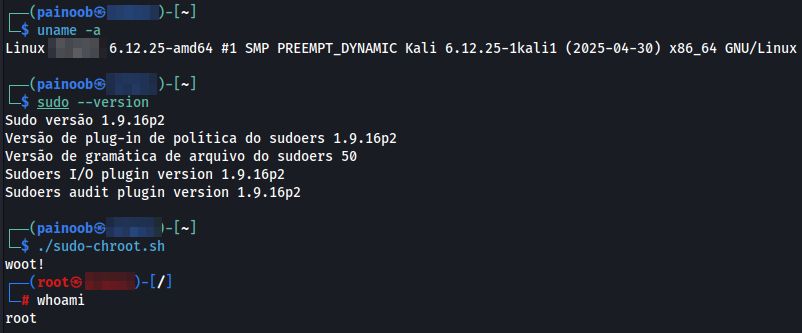 painoob/cve-2025-32463
Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…
 h3x0v3rl0rd/cve-2019-5736
Go-based exploit for CVE-2019-5736 (Runc container escape) with a customizable reverse shell payload, designed for penetration testing and red team…
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 fahmifj/docker-breakout-runc
Modified version of CVE-2019-5736-PoC by Frichetten