CVE-2026-23111-nftables-lab

Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…

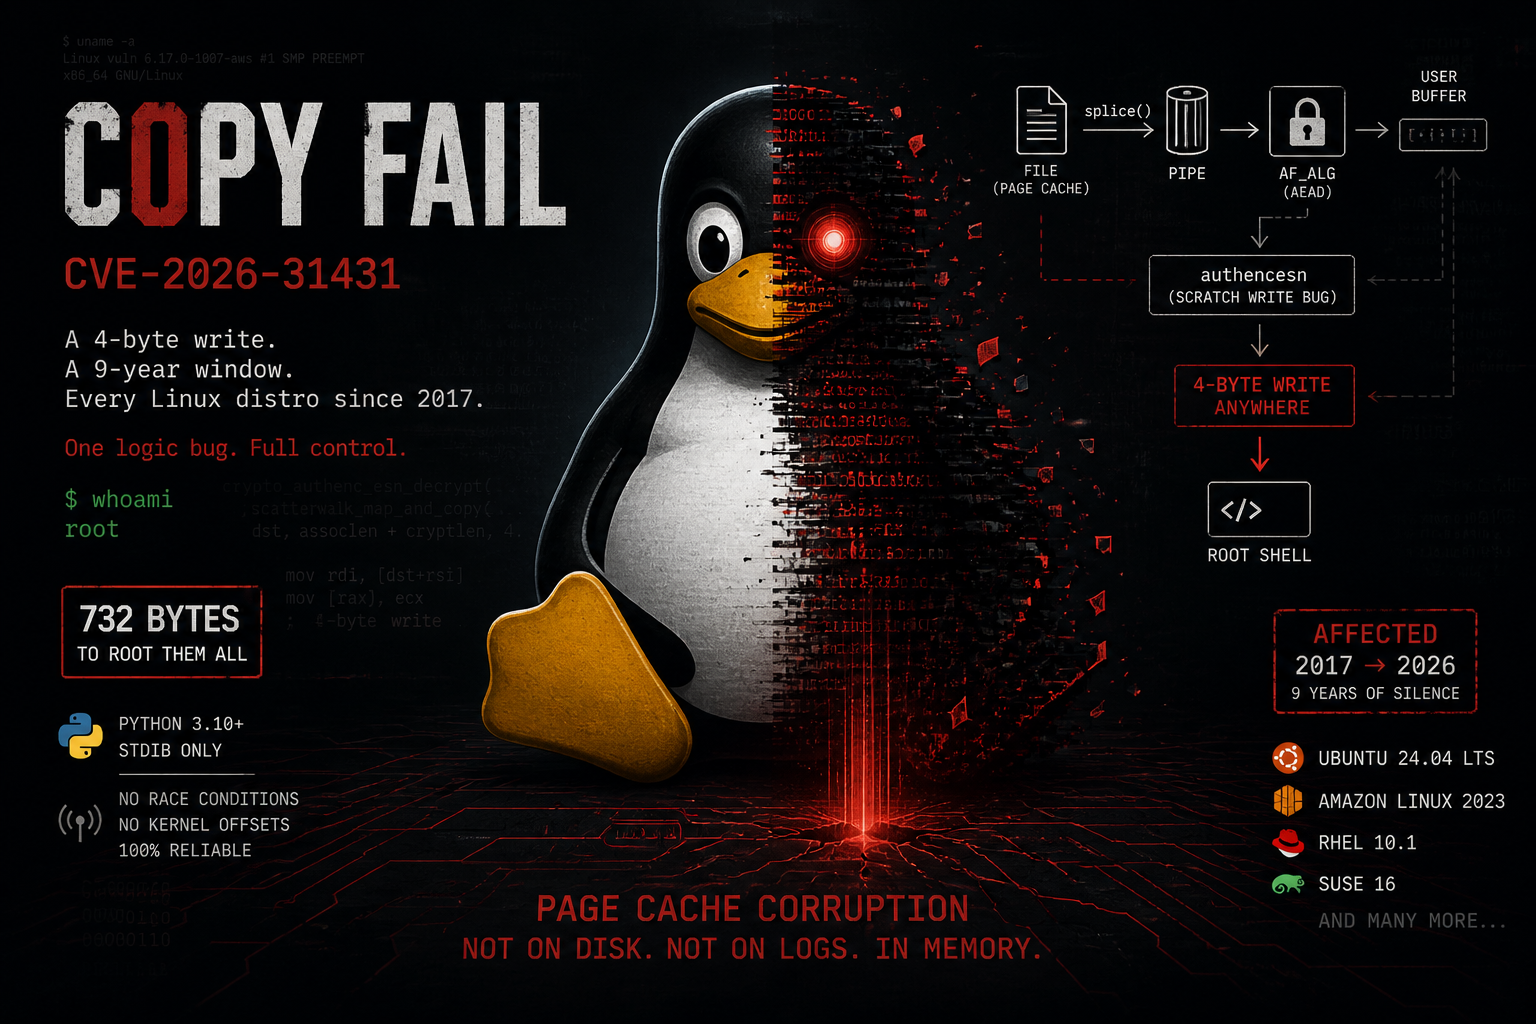
Exploit for CVE-2026-31431, a Linux kernel page-cache write primitive enabling local privilege escalation and container escape via AF_ALG and…

Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.

Destructive Docker container escape exploit for CVE-2019-5736, overwriting host /usr/bin/docker-runc with a payload triggered via docker exec.

Proof-of-concept exploit for CVE-2022-0185, a Linux kernel heap buffer overflow enabling local privilege escalation and container escape via FUSE and…

Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…

Proof-of-concept exploit for CVE-2025-32463, a local privilege escalation vulnerability in sudo allowing chroot jail escape via specific sudoers…

A container analysis and exploitation tool for pentesters and engineers.

Basic POC to test CVE-2024-3094 vulnerability inside K8s cluster

A structured explanation of CVE-2026-31431 (Copy Fail), connecting the three kernel changes that introduced the vulnerability and enabled its…

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

An exploit primitive in linux kernel inspired by DirtyPipe

Detailed technical analysis and working exploit for CVE-2022-0492 Linux kernel container escape via cgroup release_agent, with step-by-step lab setup…

Proof-of-concept exploit for CVE-2026-41900, an unauthenticated remote code execution in OpenLearnX via container volume mount, enabling /tmp…

CVE-2025-23266 targets FastAPI’s parse_request() function, where oversized HTTP headers cause a buffer overflow and remote code execution. The…

A convenient and time-saving auto script of building environment and exploit it.