
CDK
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
cloud-securitycontainer-escapecontainer-security+7
4.8k4 months ago
cdk-team/cdk📦 Make security testing of K8s, Docker, and Containerd easier.
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 aegrah/panix
Customizable Linux Persistence Tool for Security Research and Detection Engineering.
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
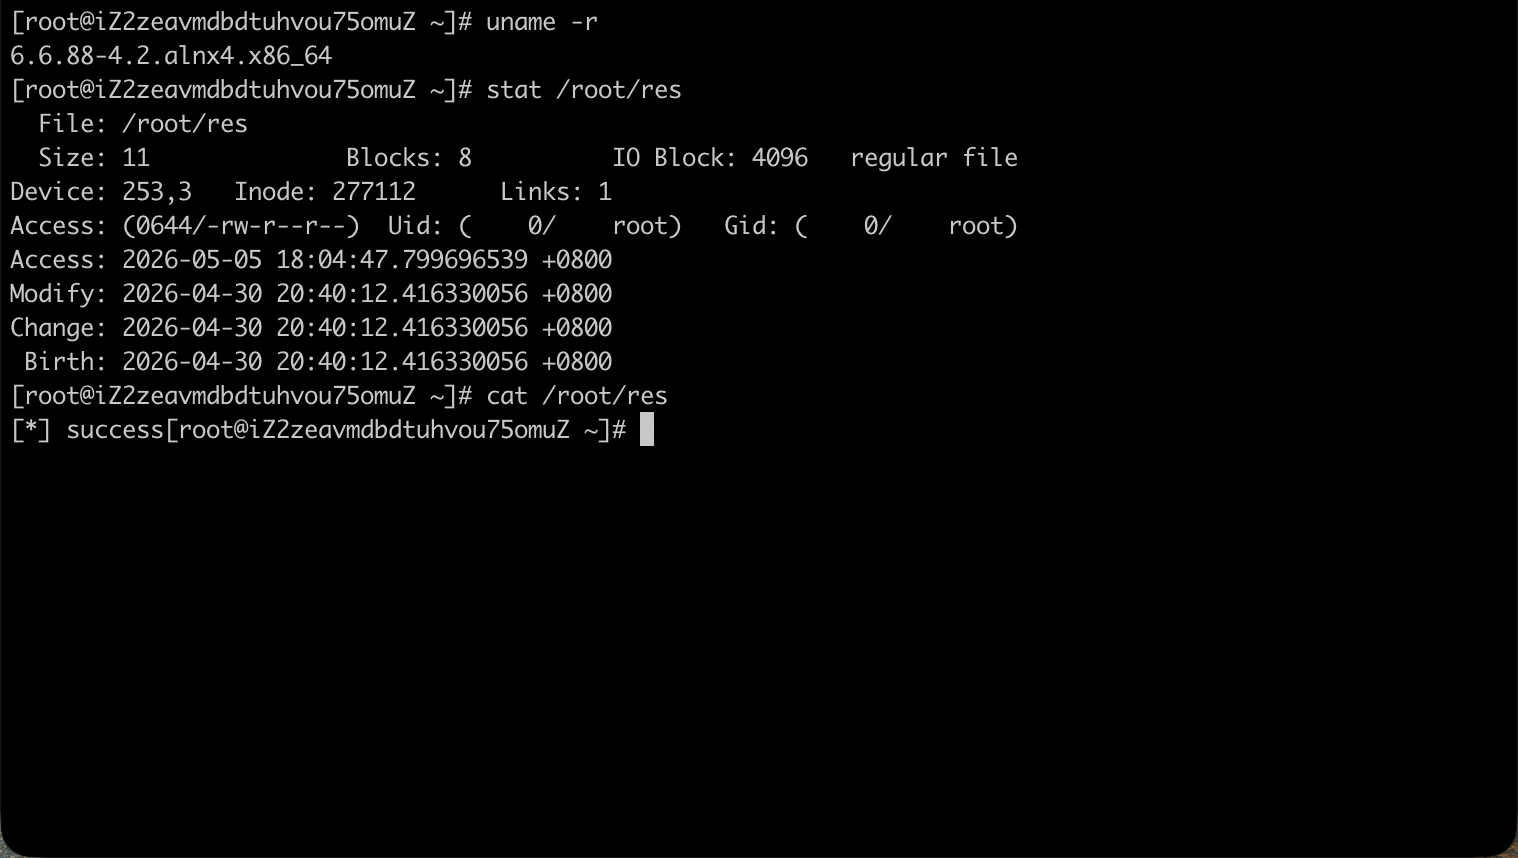 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 wavestone-cdt/defcon-cicd-pipelines-workshop
Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 nitrocao/cve-2024-21626
PoC and Detection for CVE-2024-21626
 yoshino-s/cve-2025-1974
Exploit for CVE-2025-1974 targeting ingress-nginx controllers in Kubernetes, enabling container escape via crafted shared object injection and shell…
 karazajac/dirtyfail
Detector + PoC for Linux page-cache write vulnerabilities: Copy Fail (CVE-2026-31431) and Dirty Frag (CVE-2026-43284/43500). Authorized security…
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up
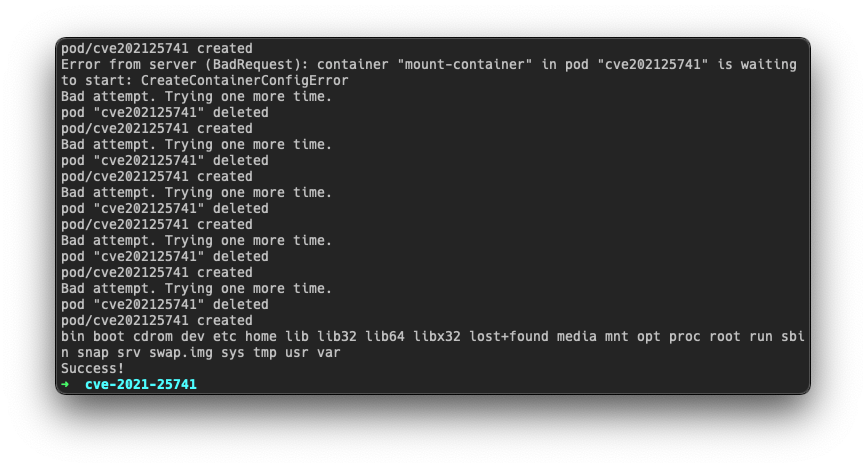 betep0k/cve-2021-25741
Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
 chenaotian/cve-2022-0492
Detailed technical analysis and working exploit for CVE-2022-0492 Linux kernel container escape via cgroup release_agent, with step-by-step lab setup…
 qi4l/cve-2026-31431-container-escape
Proof-of-concept container escape exploit targeting CVE-2026-31431 in runC, demonstrating privilege escalation and namespace breakout for security…
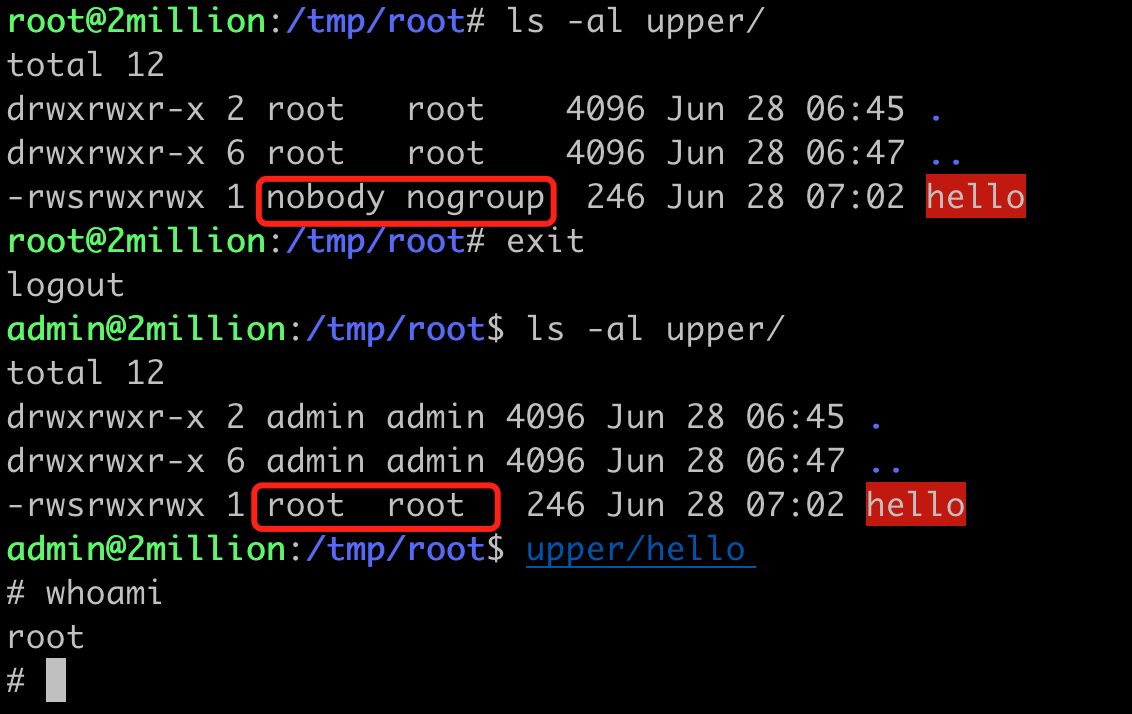 fanxiaoyao66/cve-2023-0386
非常简单的CVE-2023-0386's exp and analysis.Use c and sh.
 percivalll/dirty-frag-kubernetes-poc
Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…