
CVE-2026-41567
 berdav/cve-2026-41567
Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
container-escapeexploitationvulnerability-analysis
berdav/cve-2026-41567Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
 davidrxchester/cve-2026-5817
Docker Container-to-Host Remote Code Execution POC via vllm-metal trust_remote_code=True
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 louisliunova/cve-2022-1227_exploit
A script for exploiting CVE-2022-1227
 giverofgifts/cve-2019-5736-custom-runtime
CVE-2019-5736 implemented in a self-written container runtime to understand the exploit.
 locus-x64/cve-2025-61765_poc
Proof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
 mindasy/cve-2025-23266-migration-bypass
cve-2025-23266-migration-bypass
 rubby2001/cve-2025-1974-go
Exploit CVE-2025-1974 with a single file.
 ihsansencan/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 followboy1999/cve-2022-25365
Proof-of-concept exploit for CVE-2022-25365, a privilege escalation vulnerability in Docker Desktop for Windows via named pipe impersonation.
 megadimenex/megahidocker
This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 spiralbl0ck/cve-2024-32462
CVE-2024-32462 code exec sbx escape
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
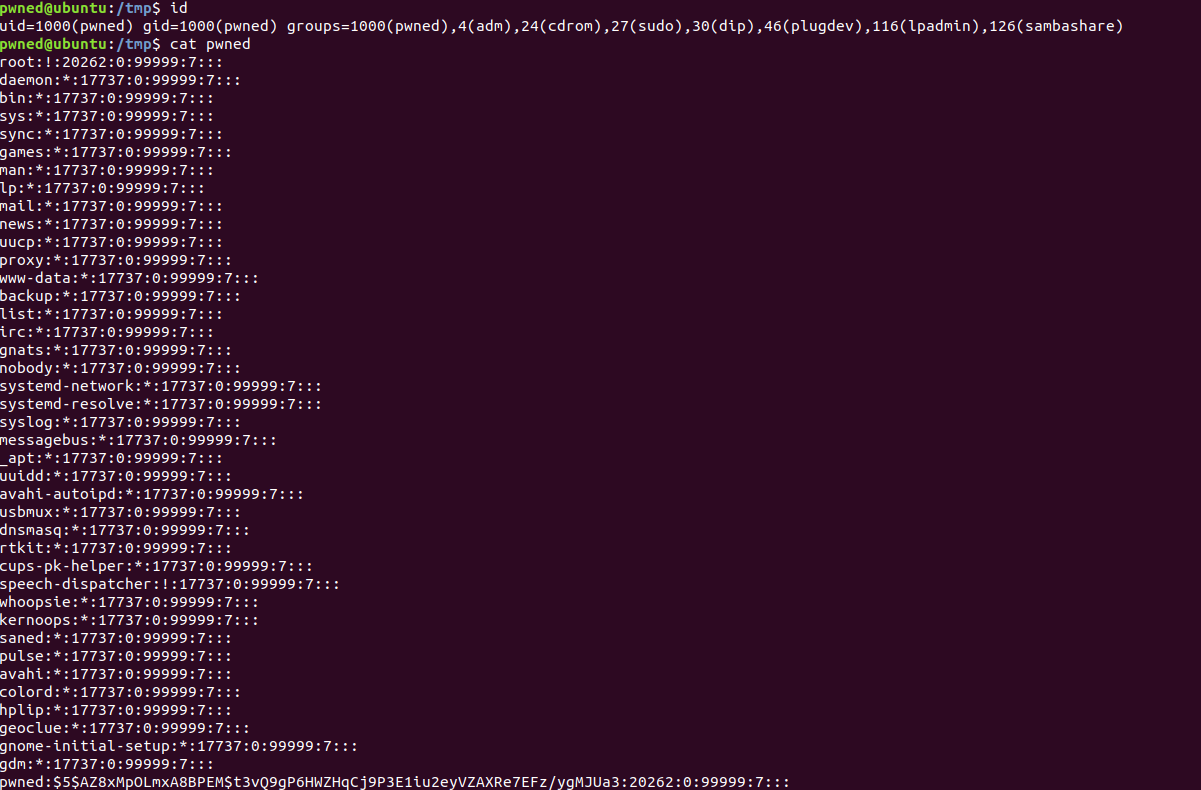 perimora/cve_2019-5736-poc
C-based PoC for CVE-2019-5736
 matesz44/cve-2025-9074
CVE-2025-9074: Docker Desktop LPE via Docker Engine API wo/ AuthN in posix sh
 r4mbb/cve-2024-21626-poc
Root cuase & Proof Of Code
 x0da6h/poc-for-cve-2025-9074
一个容器逃逸漏洞POC