kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

A vulnerability scanner for container images and filesystems

Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…

CLI tool and library for generating a Software Bill of Materials from container images and filesystems

Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…

Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more

CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

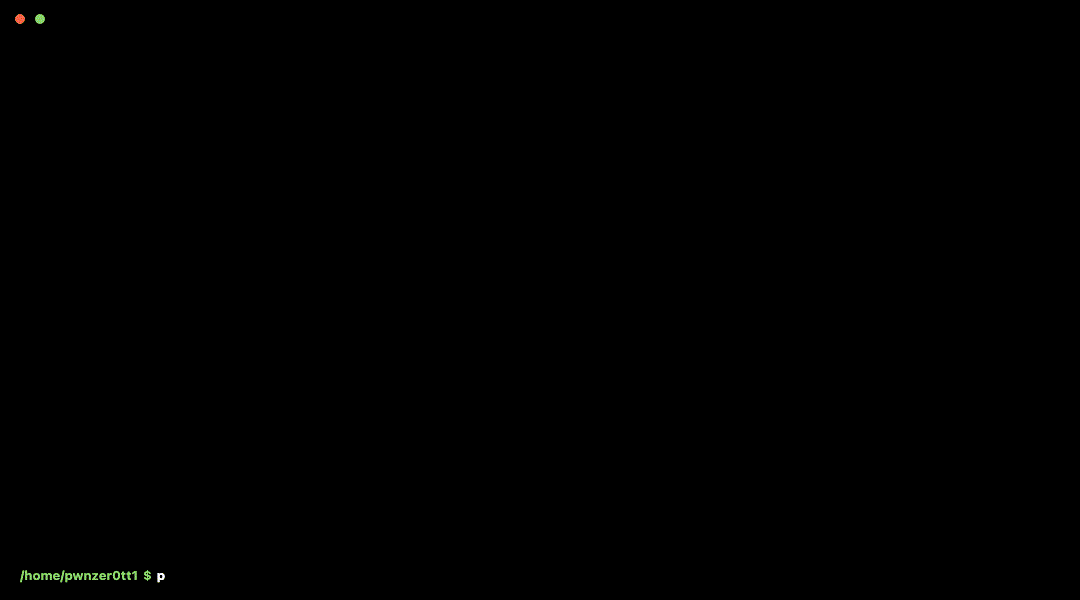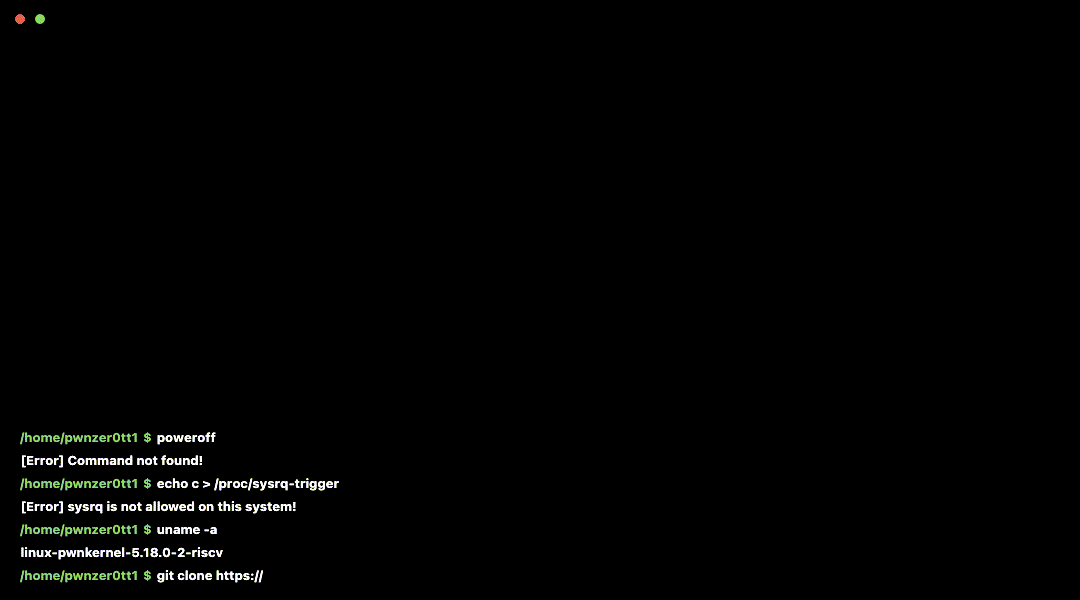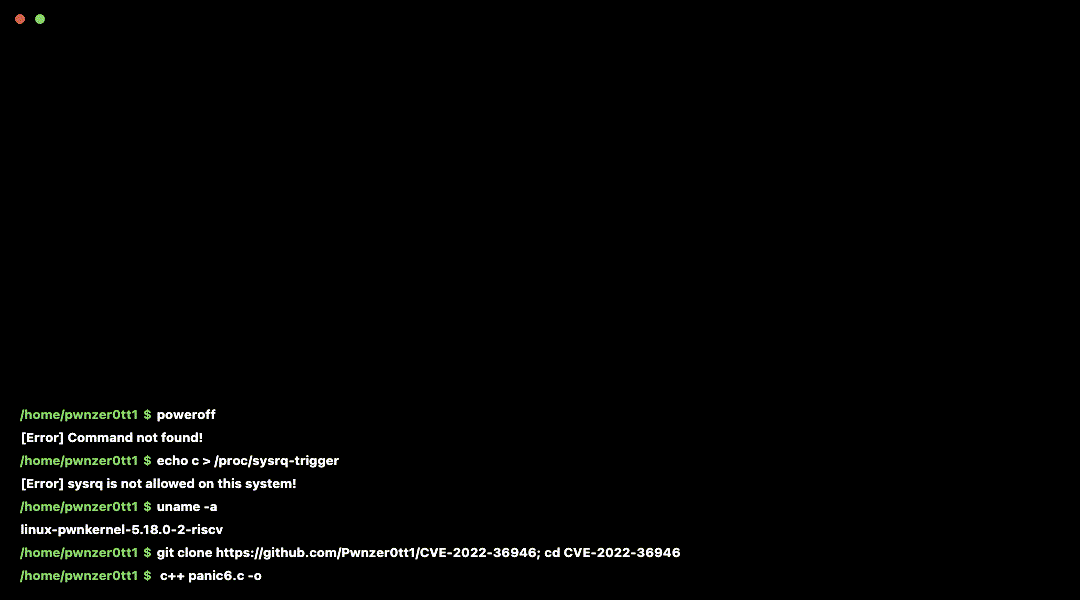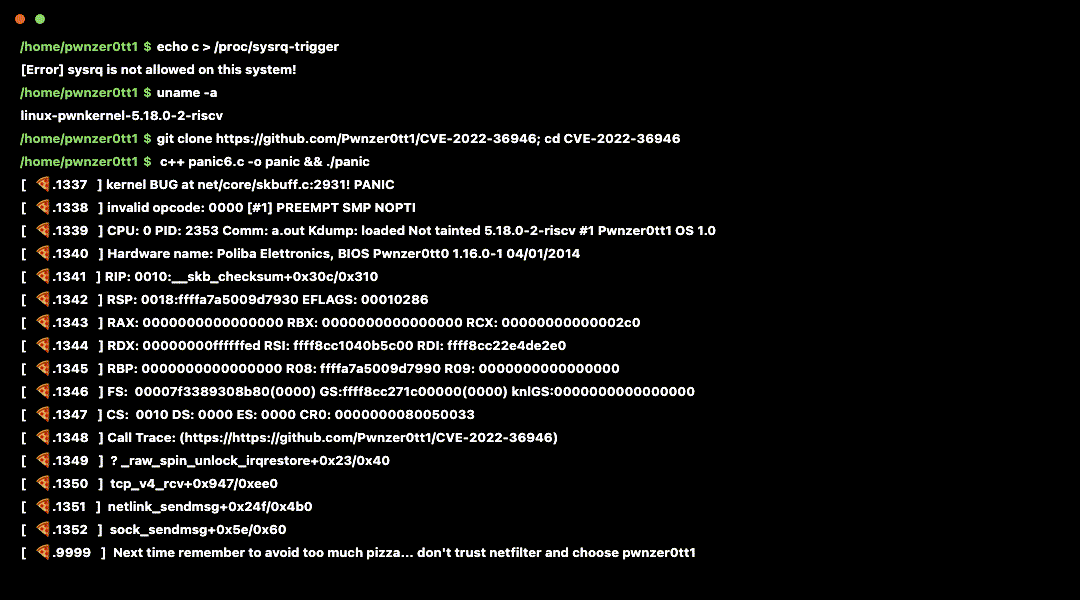
CVE-2022-36946 linux kernel panic in netfilter_queue

An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.

Security risk analysis for Kubernetes resources

Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.

Proof of concept code for Datadog Security Labs referenced exploits.

Isolate your big brother apps https://secure-system.gitlab.io/Insular/

110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.