

opa
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
api-securityauthenticationauthentication-authorization+10
12.3k
open-policy-agent/opaDeclarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 berdav/cve-2026-41567
Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 hackspeak/cve-2026-17106
PoC for Docker `docker cp` arbitrary file write, exploiting symlink and tar extraction flaws to overwrite host binaries or launch agents for…
 masasron/copyescape-cve-2026-17106
PoC repository for the blog post CopyEscape: Taking Over Docker Hosts with docker cp
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…
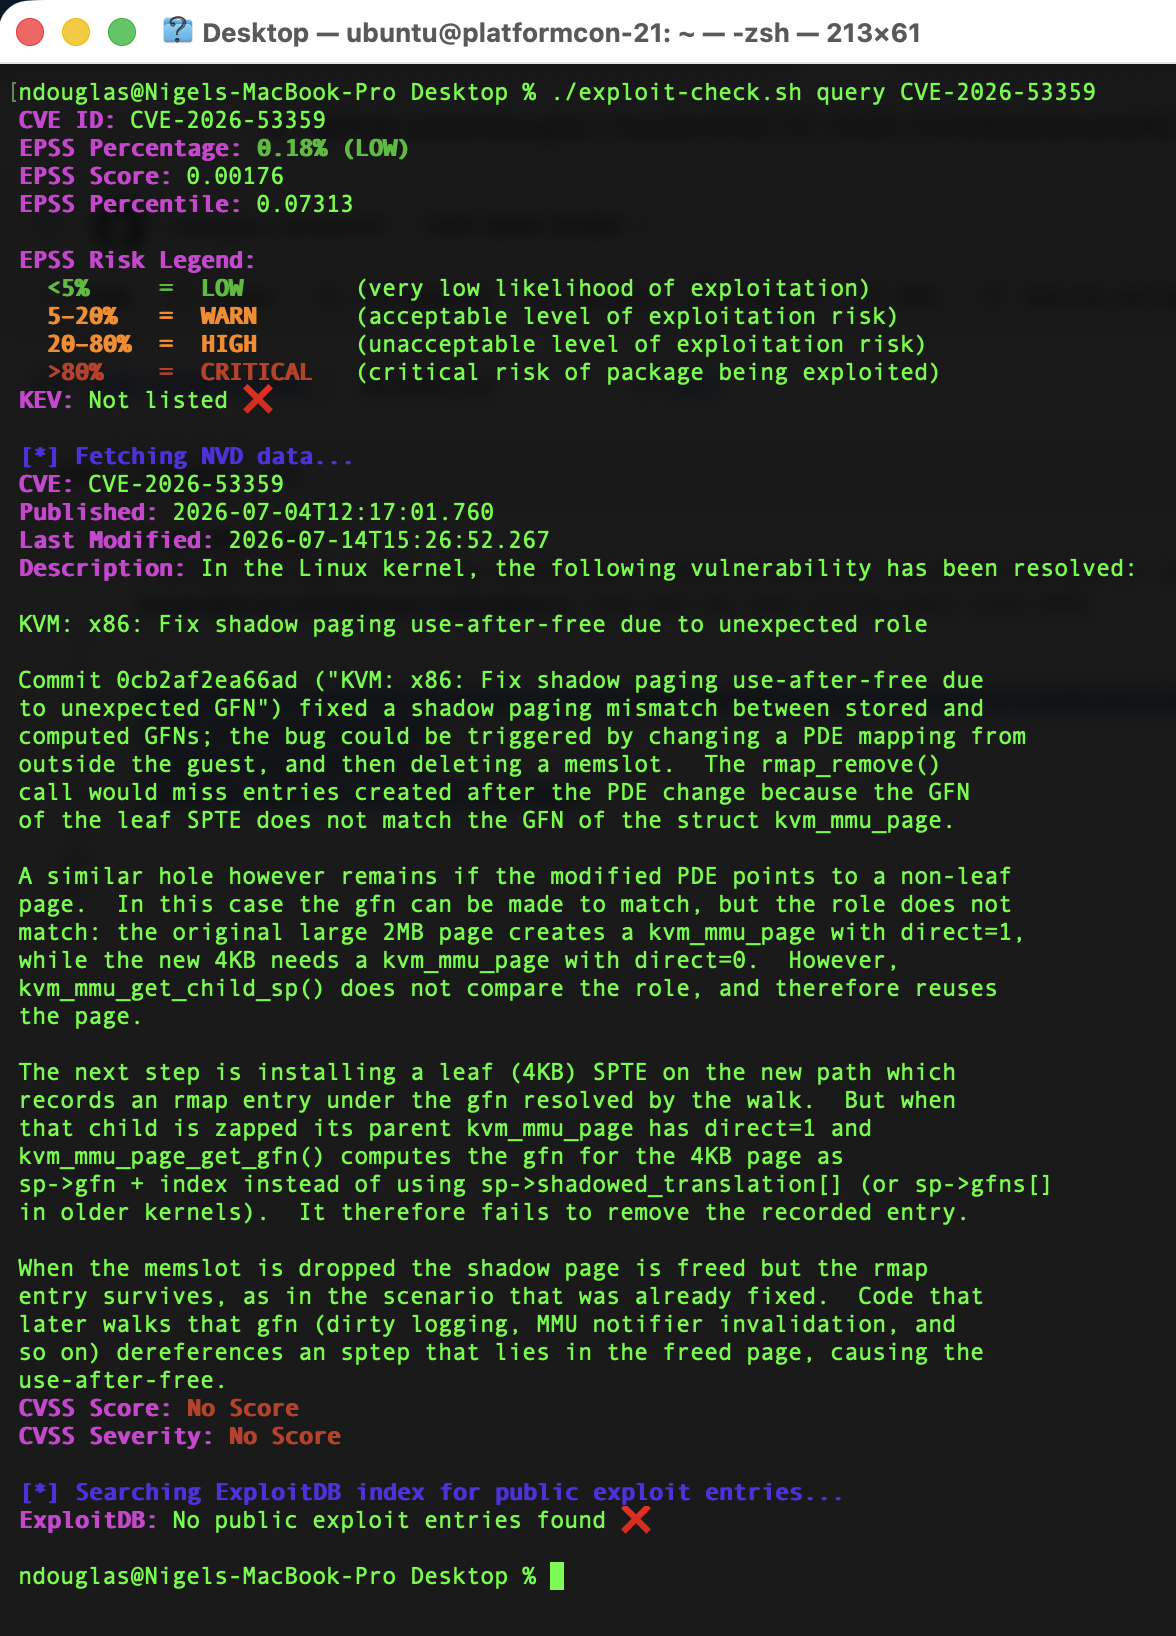 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 yanxinwu946/cve-2026-46331
CVE-2026-46331 act_pedit page-cache corruption exploit, with Alpine PIE fix
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 1neptune/copyfail
go CVE-2026-31431 (CopyFail) local privilege escalation exploit
 c0gnit00/cve-2025-9074
PHP poc, exploit for CVE-2025-9074
 davidrxchester/cve-2026-5817
Docker Container-to-Host Remote Code Execution POC via vllm-metal trust_remote_code=True
 sgkdev/ptrace_may_dream
CVE-2026-31431-killed page-cache exploit — code exec into containers sharing the same image layer
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…