

gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
cloud-infrastructure-securitycloud-securitycontainer-escape+4
19.4k
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 anchore/grype
A vulnerability scanner for container images and filesystems
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.
 livecontainer/livecontainer
Run iOS apps without actually installing them!
 nestybox/sysbox
An open-source, next-generation "runc" that empowers rootless containers to run workloads such as Systemd, Docker, Kubernetes, just like VMs.
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 qianlijaingshan/fastgpt-sandbox-audit
FastGPT Python sandbox escape chain audit tool (CVE-2026-32128 related, v4.14.8 inspect chain)
 go-lanz/persistnux
Bash-based Linux persistence detection tool for DFIR investigations. Scans 15+ persistence mechanisms (systemd, cron, kernel modules, SSH,…

 kinryulabs/rootpacket-cve-2026-31431
Live cryptojacking toolkit with CVE-2026-31431 LPE exploit, container escape, kernel rootkit, and XMRig Monero miner, captured from real attacks for…
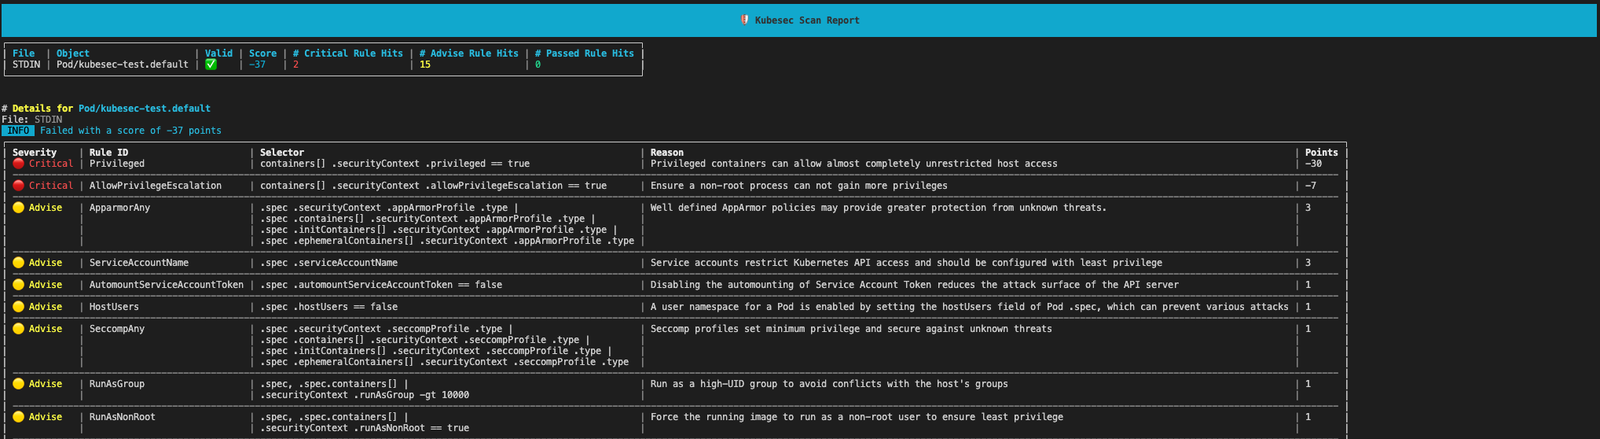 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 krish-foren6/cve-2026-31431-report-copy-fail-vulnerability-
Detailed analysis of the Copy Fail vulnerability (CVE-2026-31431) in the Linux kernel, including memory corruption mechanism, privilege escalation…