

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.7k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 falcosecurity/falco
Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…
 aquasecurity/kube-hunter
Hunt for security weaknesses in Kubernetes clusters
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
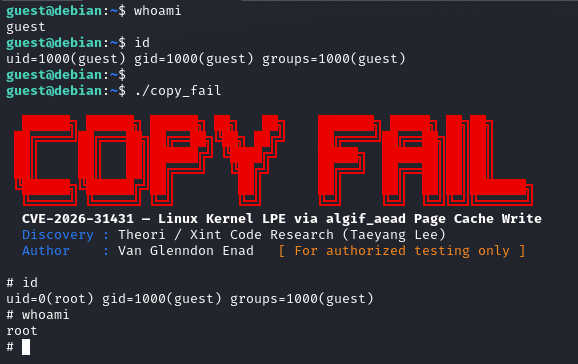 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 inguardians/peirates
Peirates - Kubernetes Penetration Testing tool
 4nuxd/react2shell
R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 galoryber/fawkes
Fawkes is a golang Mythic C2 Agent exclusively written by AI.
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
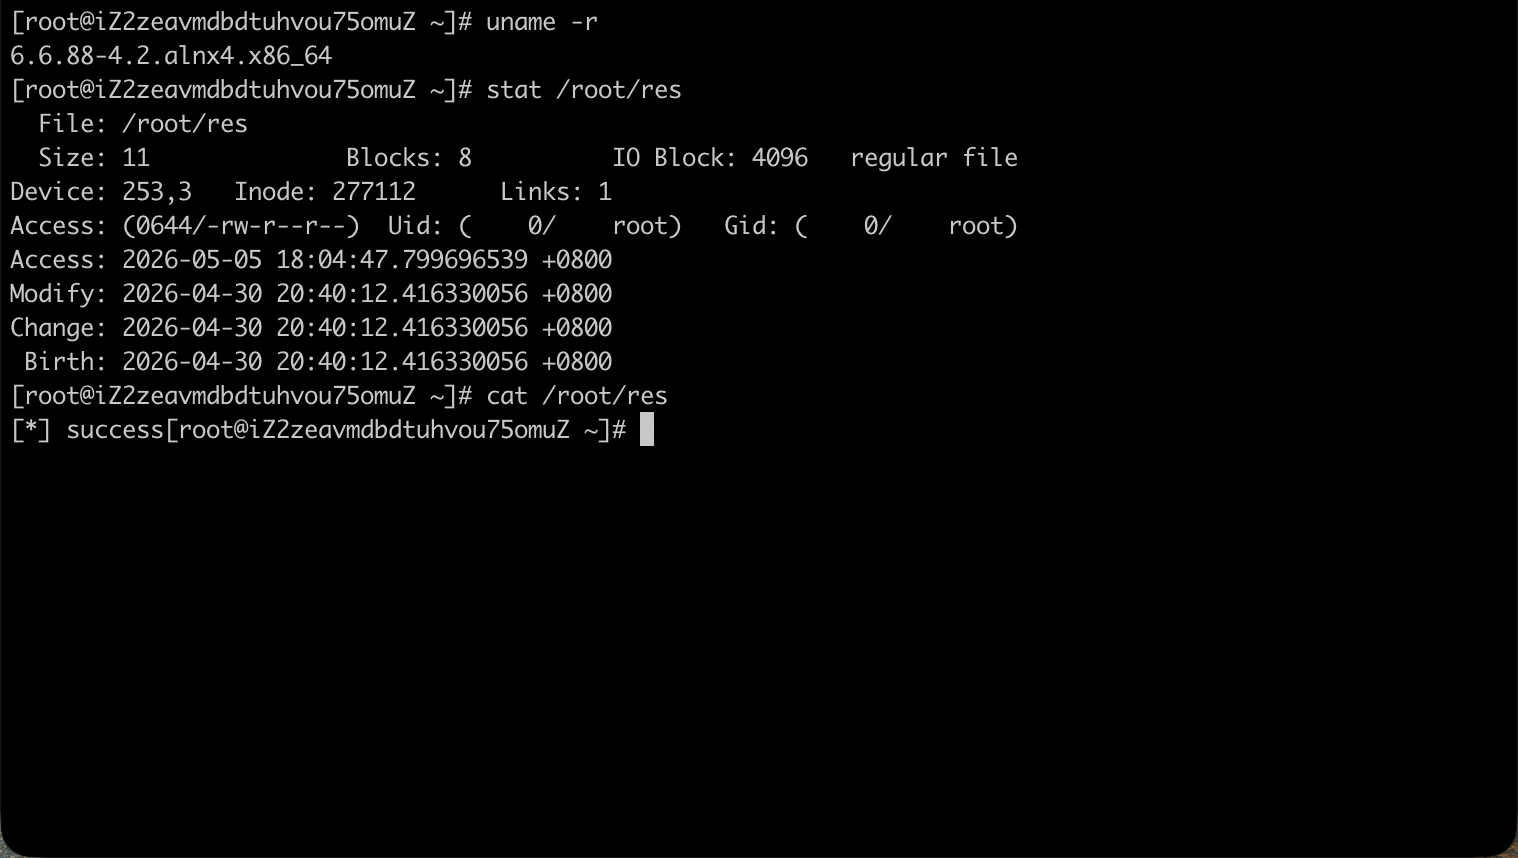 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 sgkdev/ipv6_frag_escape
Linux LPE - Reliable Jail/Container Escape