

IDWolf
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
cloud-securityconfiguration-auditingdefensive-tools+6
22
g4bri-3l3/idwolfRead-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 0warn/defender
This is a bash script focus on hardening linux. This is a custom think of windows defender but unlike of their privacy issue. User can feel freedom…
 d4gh0s7/cve-2018-19788
Ansible role to audit and test systems for CVE-2018-19788 (PolicyKit privilege escalation) with automated user provisioning and exploit verification.
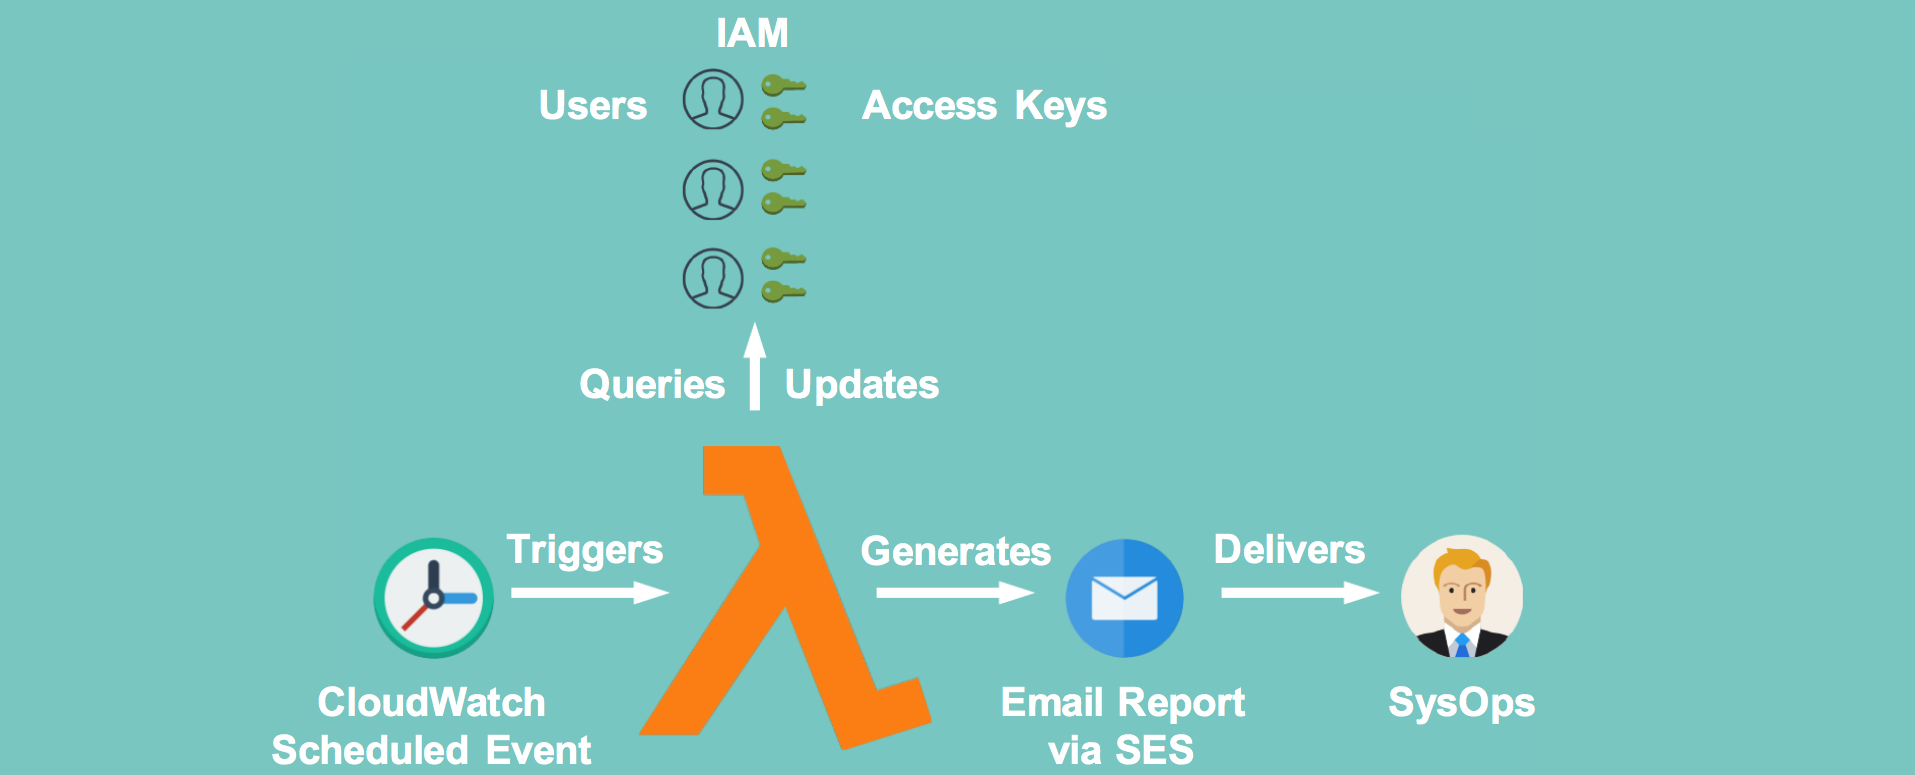 te-papa/aws-key-disabler
A small lambda script that will disable access keys older than a given amount of days.
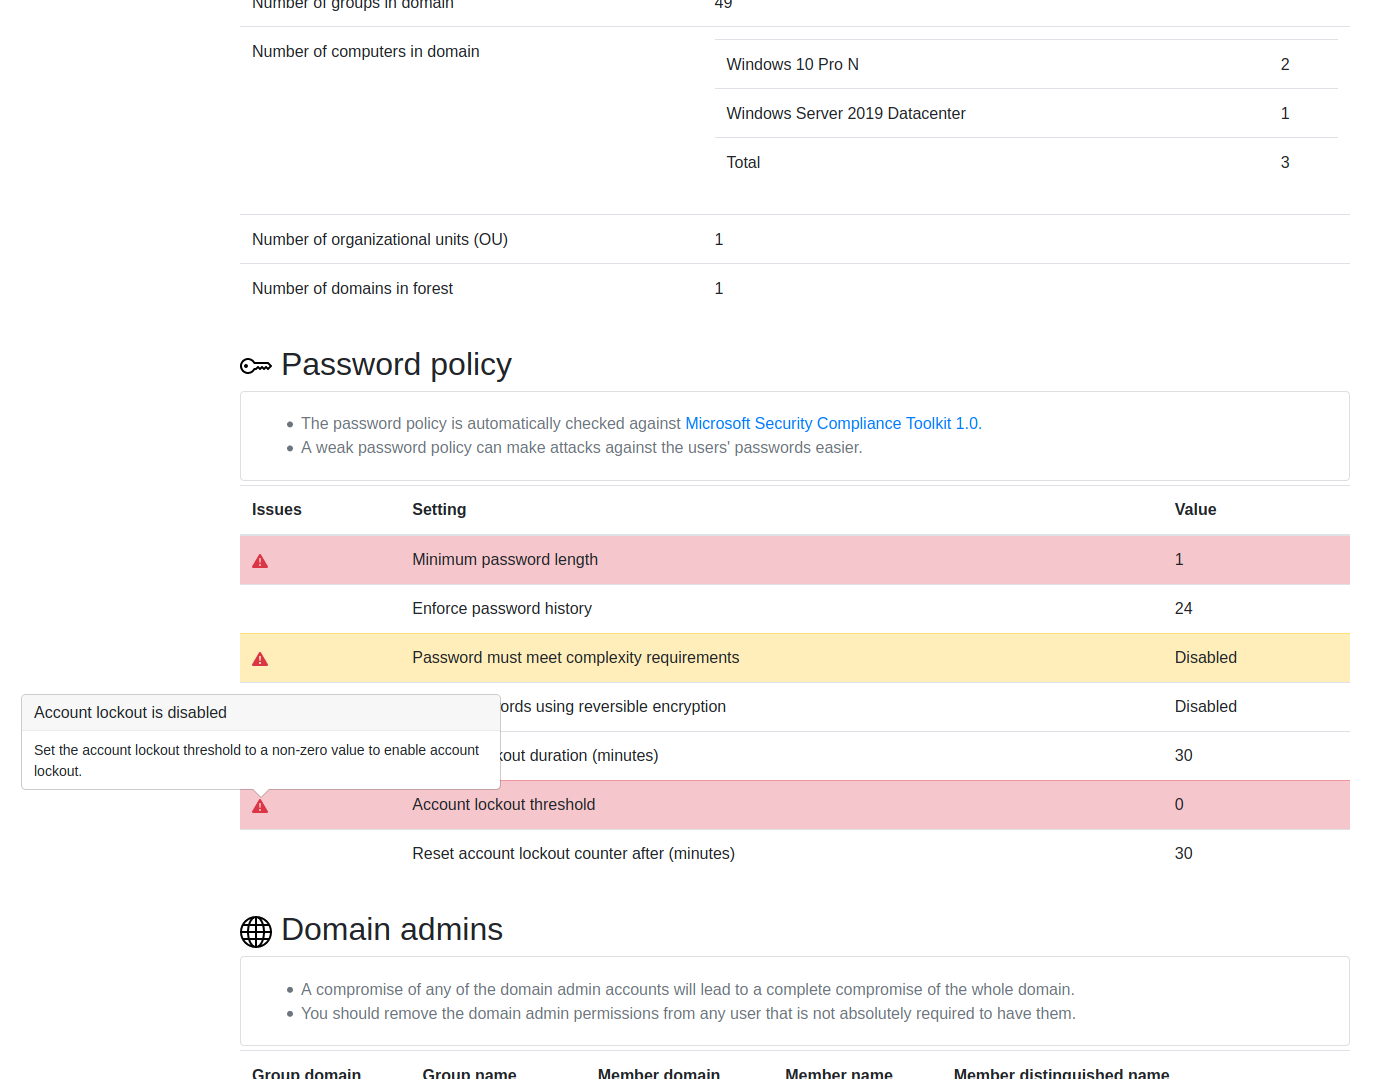 ncsc-fi/tiuku
Tiuku is a tool for scanning various kinds of systems and environments for security related information and displaying the results in a browser-based…
 password123456/setup-wordpress-with-security-best-practice
Comprehensive guide for hardening WordPress installations: covers admin user changes, HTTPS enforcement, plugin security, file permissions, and…
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 hwdsl2/setup-ipsec-vpn
Automated IPsec VPN server setup with IPsec/L2TP, Cisco IPsec, and IKEv2 support. Includes helper scripts for user and certificate management, and…
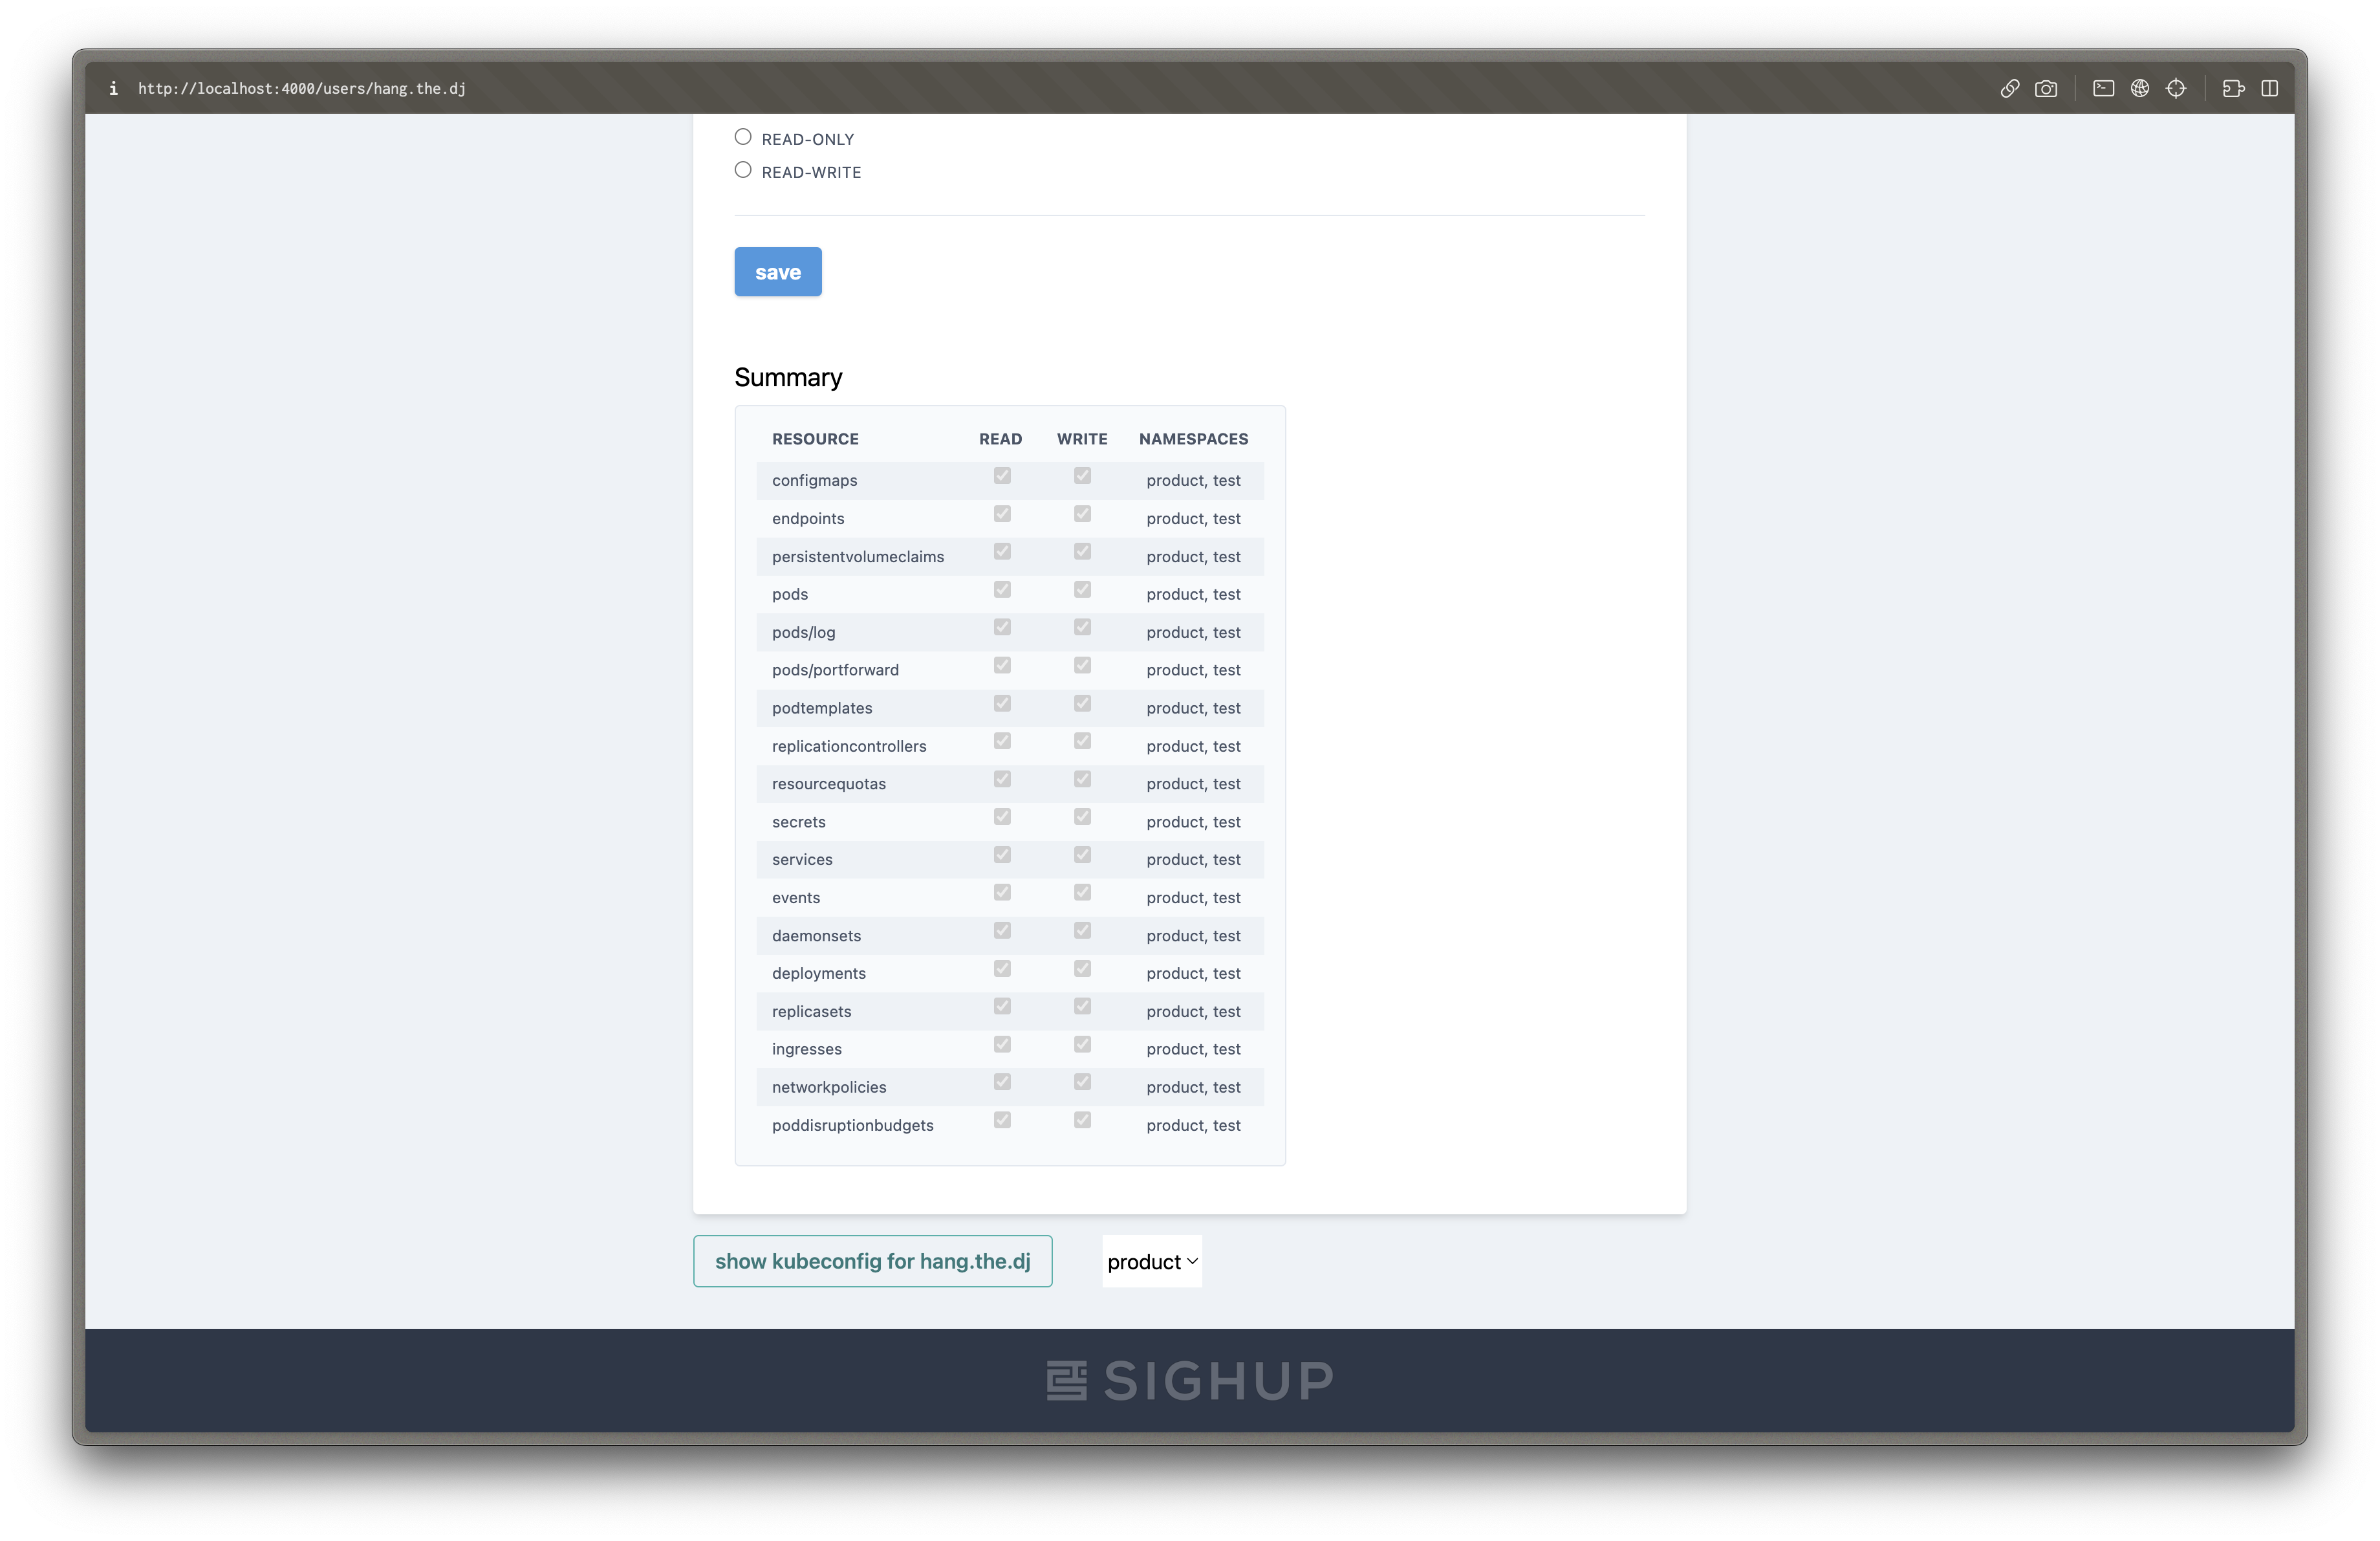 sighupio/permission-manager
Permission Manager is a project that brings sanity to Kubernetes RBAC and Users management, Web UI FTW
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 deadjakk/reg1c1de
Registry permission scanner written in C# for finding potential privesc avenues within registry
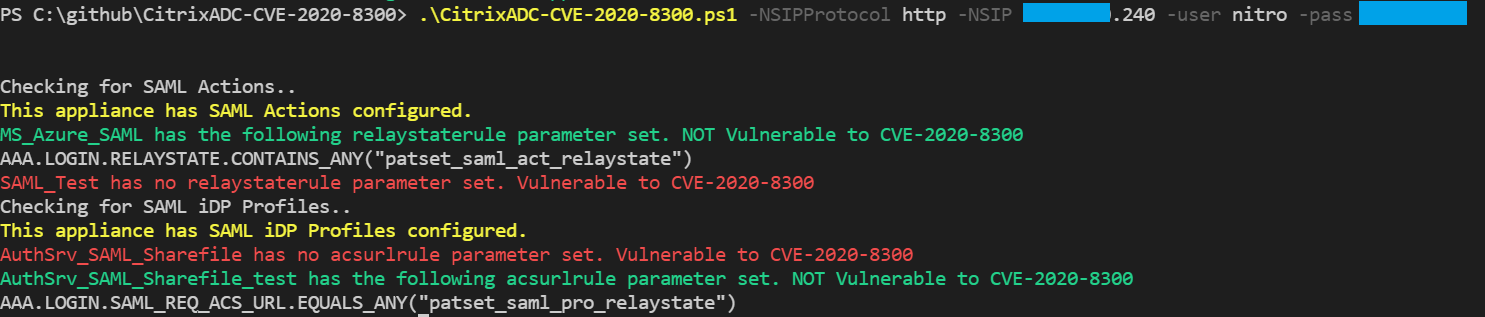 stuartcarroll/citrixadc-cve-2020-8300
Detect Citrix ADC SAML action or SAML iDP Profile config vulnerable to CVE-2020-8300 using Citrix ADC NITRO API
 tailwindrg/cve-2026-0300-audit
Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)
 criann/check-cve-2026-23111
Script to check if system are vulnable to cve-2026-23111
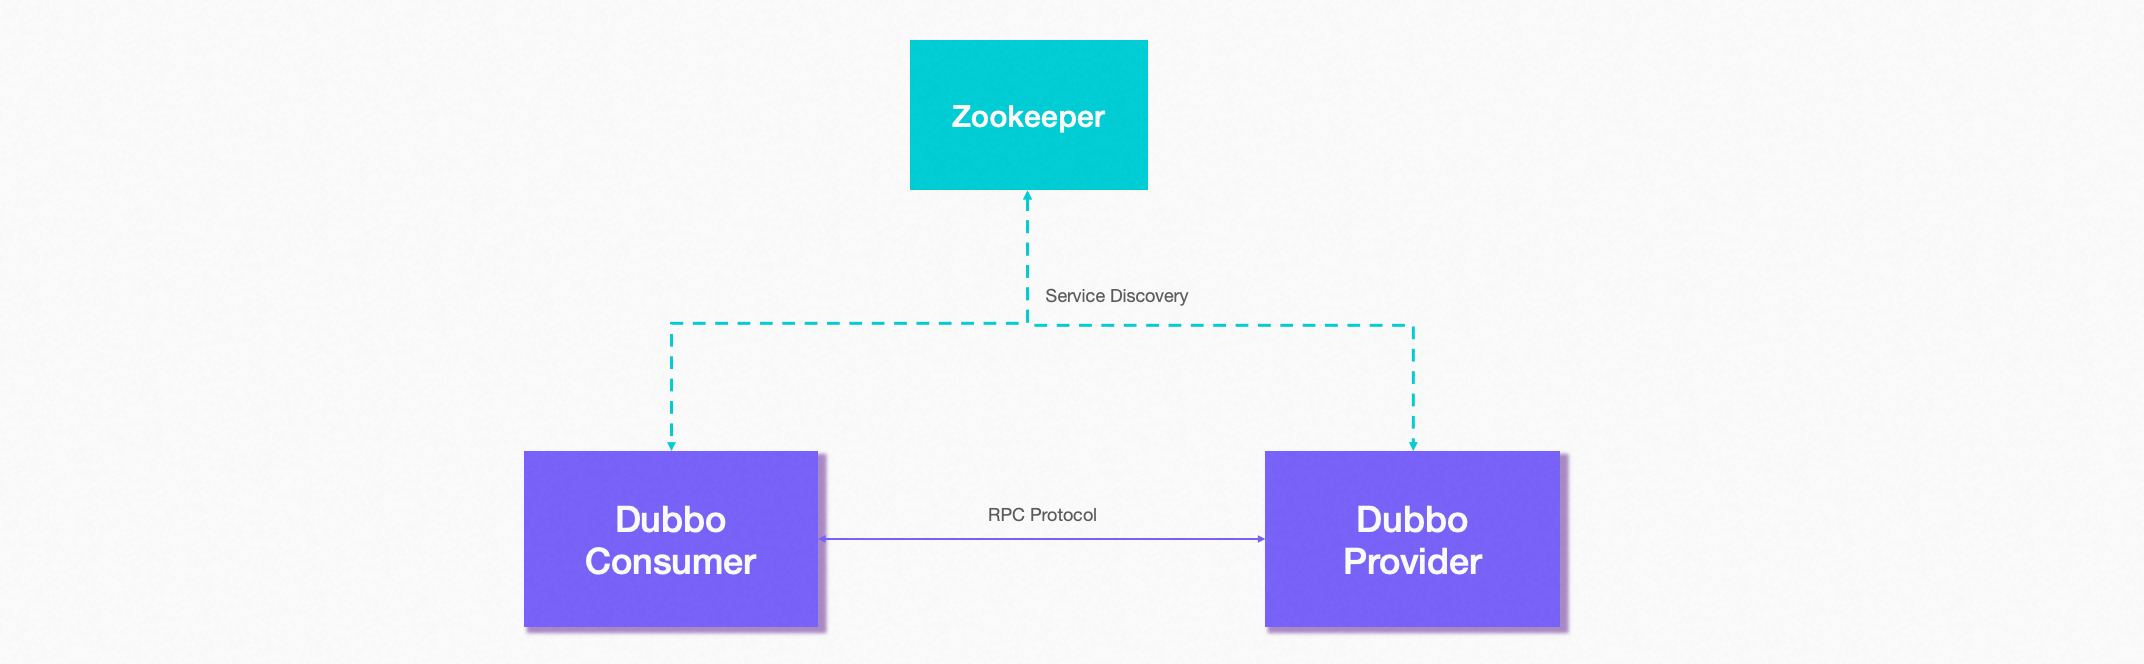 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…