
Archived
metabadger
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
salesforce/metabadgerPrevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…

 eveo7/aa-discord-audit
Reconciliation audit for Alliance Auth's Discord integration: finds guild members holding AA-managed roles that Auth never granted and strips or…
 teedeedubya/bash-fix-exploit
Ansible role to check the CVE-2014-6271 vulnerability
 d4gh0s7/cve-2018-19788
Ansible role to audit and test systems for CVE-2018-19788 (PolicyKit privilege escalation) with automated user provisioning and exploit verification.
 chef-boneyard/bash-shellshock
DEPRECATED: Chef cookbook to audit & remediate "Shellshock" (BASH-CVE-2014-7169)
 joltcan/ansible-role-cve-2026-31431
Ansible role that applies and verifies the modprobe.d mitigation for CVE-2026-31431 by disabling the algif_aead kernel module, with safety checks for…
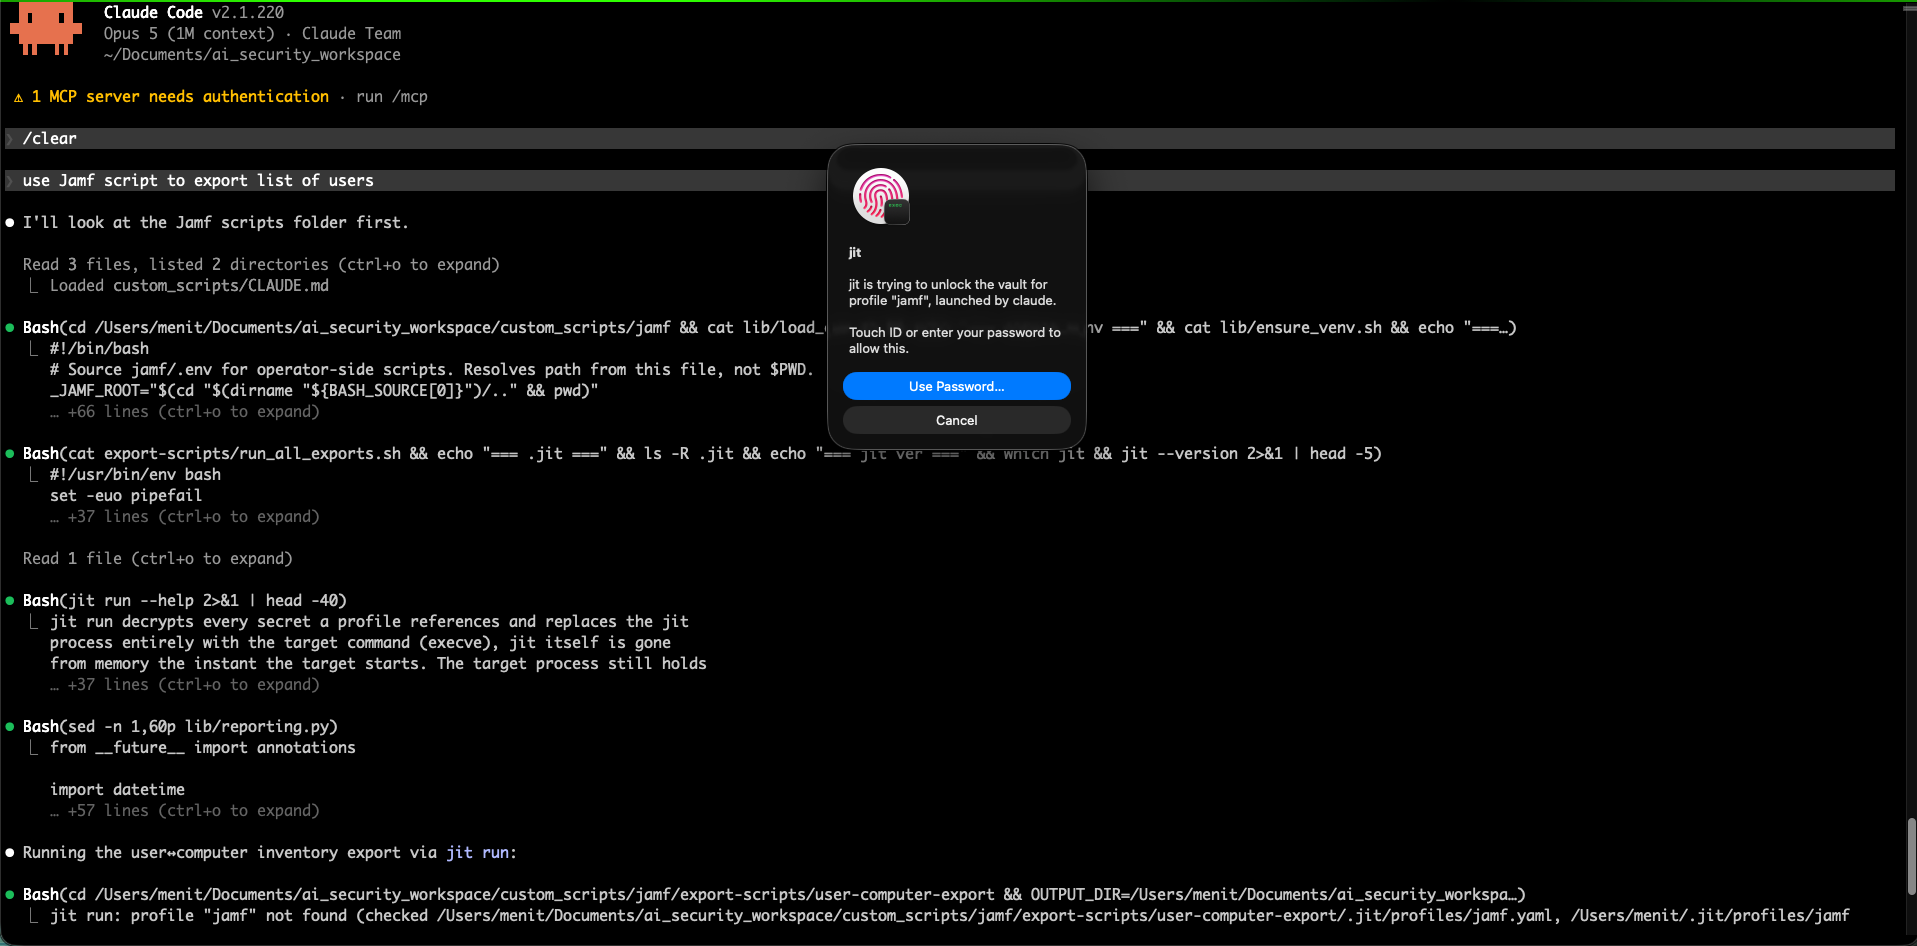 jitpass/jit
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 lucab85/ansible-role-log4shell
Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 shoucheng3/apache__jspwiki_cve-2019-10078_2_11_0_m4_fixed
Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 shoucheng3/apache__jspwiki_cve-2019-10076_2-11-0-m3
Java-based wiki platform with JAAS security integration, access control, and detailed configuration auditing. Includes documentation for…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
 axisops/cve-2021-44228
log4j mitigation work
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…