
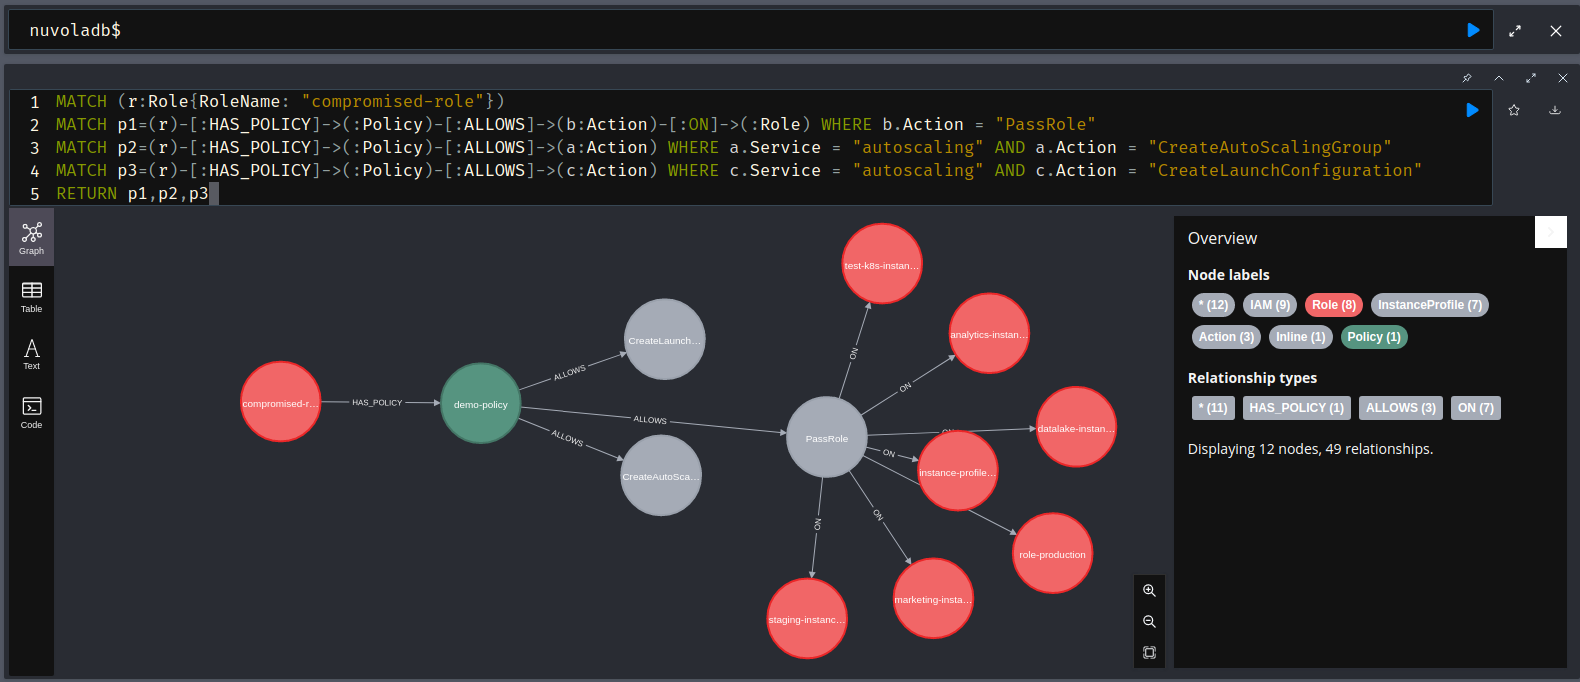
nuvola
 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+5
144
primait/nuvolaGraph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 tanmayshahane/kyubisweep
A lightweight, cross-platform CLI tool that scans your filesystem to detect exposed secrets, API keys, and tokens. Built with Go for maximum…
 p0dalirius/sharehound
A python tool to map the access rights of network shares into a BloodHound OpenGraphs easily
 ustayready/outpost
AWS Testing and Reporting Management Tool
 optiopay/klar
Integration of Clair and Docker Registry
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
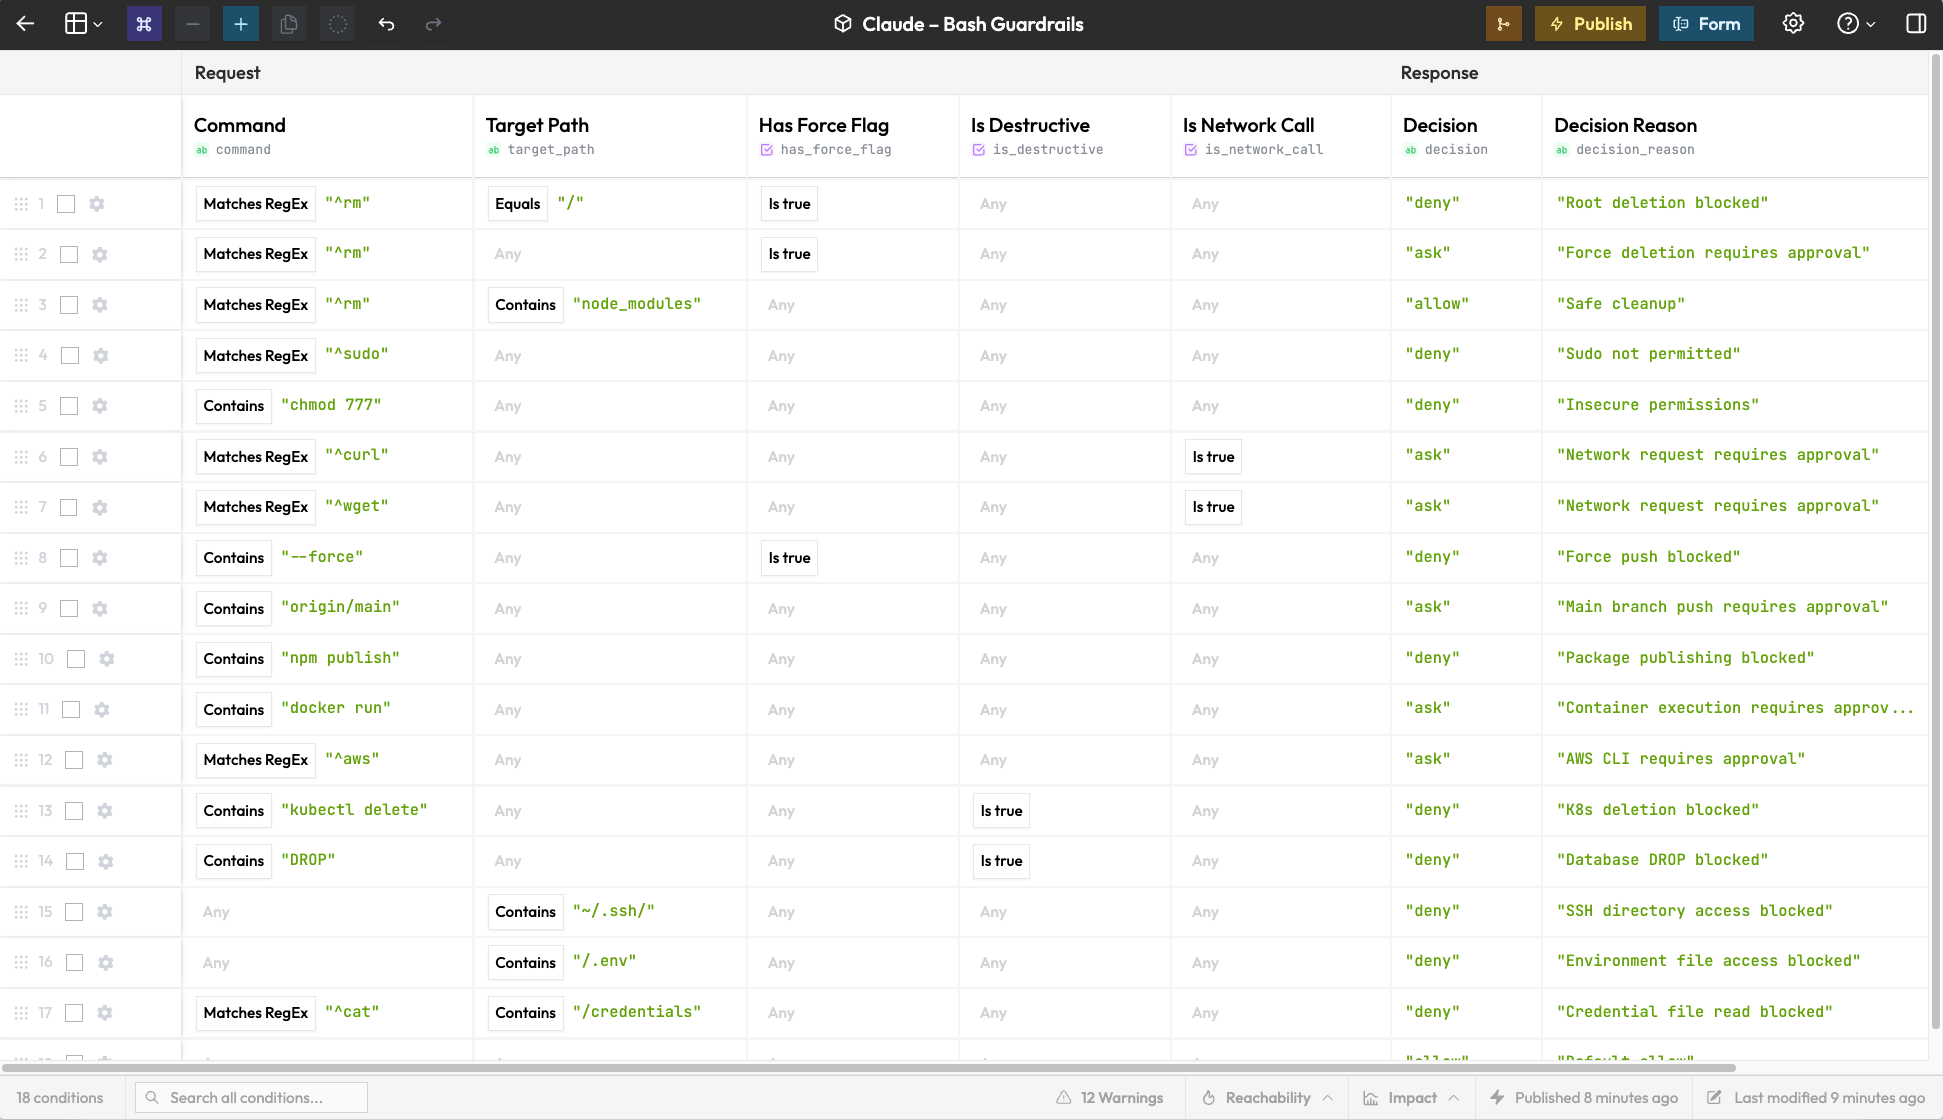 rulebricks/claude-code-guardrails
Real-time guardrails for Claude Code tool calls.
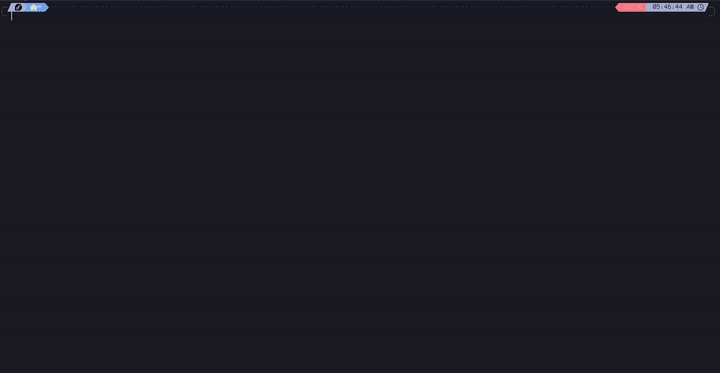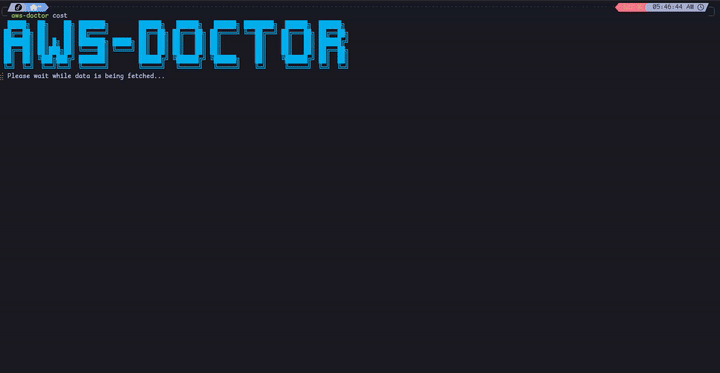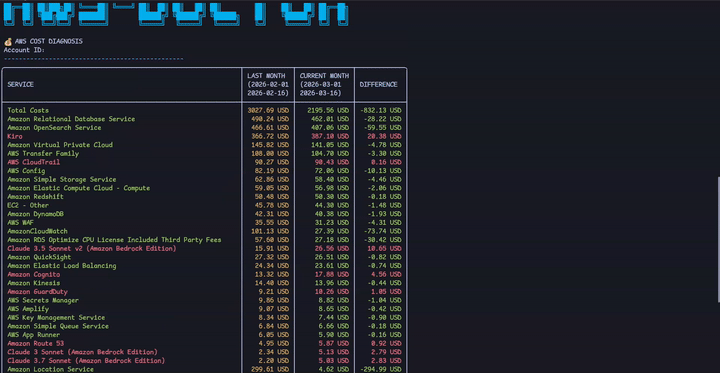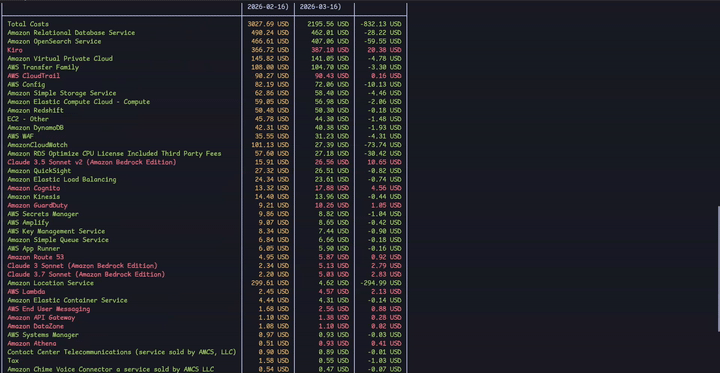 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 michelin/chopchop
YAML-driven CLI scanner that detects exposed services, files, and folders on web endpoints. Designed for developers to integrate security checks into…
 skyscanner/whispers
Identify hardcoded secrets in static structured text
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 ramonzx6/rapid-reset-check
Go CLI that inventories HTTPS endpoints negotiating HTTP/2 via ALPN to identify systems requiring CVE-2023-44487 mitigation review. Non-exploitative,…
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 goodwithtech/dockle
Container Image Linter for Security, Helping build the Best-Practice Docker Image, Easy to start
 appliscale/cloud-security-audit
A command line security audit tool for Amazon Web Services
