
PS-CVE-2021-44228
 arnaudluti/ps-cve-2021-44228
Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
cloud-infrastructure-securityconfiguration-auditingdevsecops+2
arnaudluti/ps-cve-2021-44228Static detection of vulnerable log4j librairies on Windows servers, members of an AD domain.
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 cyberdefenders/detectionlabelk
DetectionLabELK is a fork from DetectionLab with ELK stack instead of Splunk.
 phillips321/adaudit
Powershell script to do domain auditing automation
 bishopfox/spoofcheckselftest
Web application that lets you test if your domain is vulnerable to email spoofing
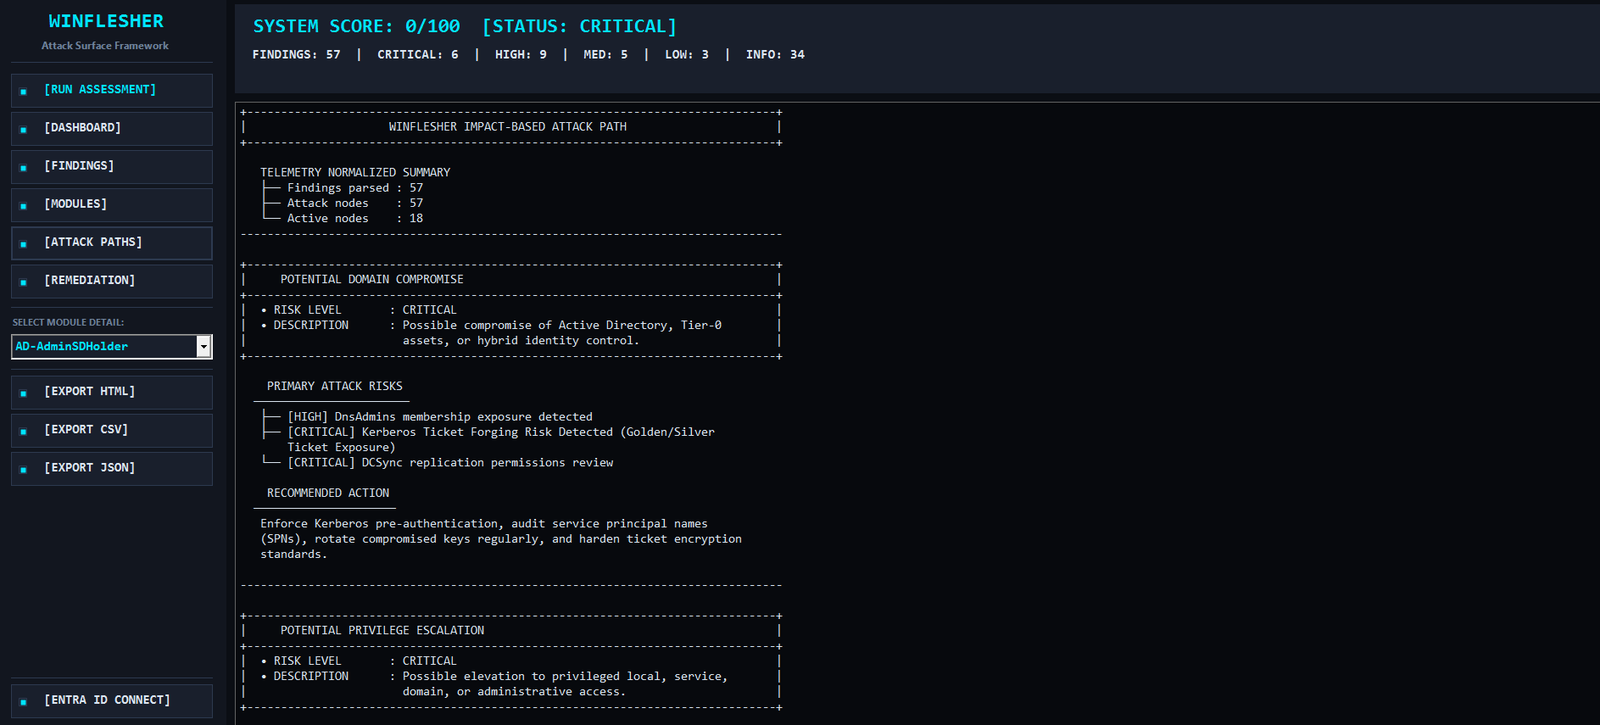 mindsflee/winflesher
Automated attack surface assessment framework for Active Directory and local infrastructures, correlating vulnerabilities with attack paths to domain…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 password123456/ssl-certificate-expiry-date-checker
Scans SSL/TLS certificates for expiry dates, issuer details, and OCSP status. Sends notifications via webhook, Telegram, or Slack. Supports proxy per…
 keysau/get-log4j-windows.ps1
Identifying all log4j components across all windows servers, entire domain, can be multi domain. CVE-2021-44228
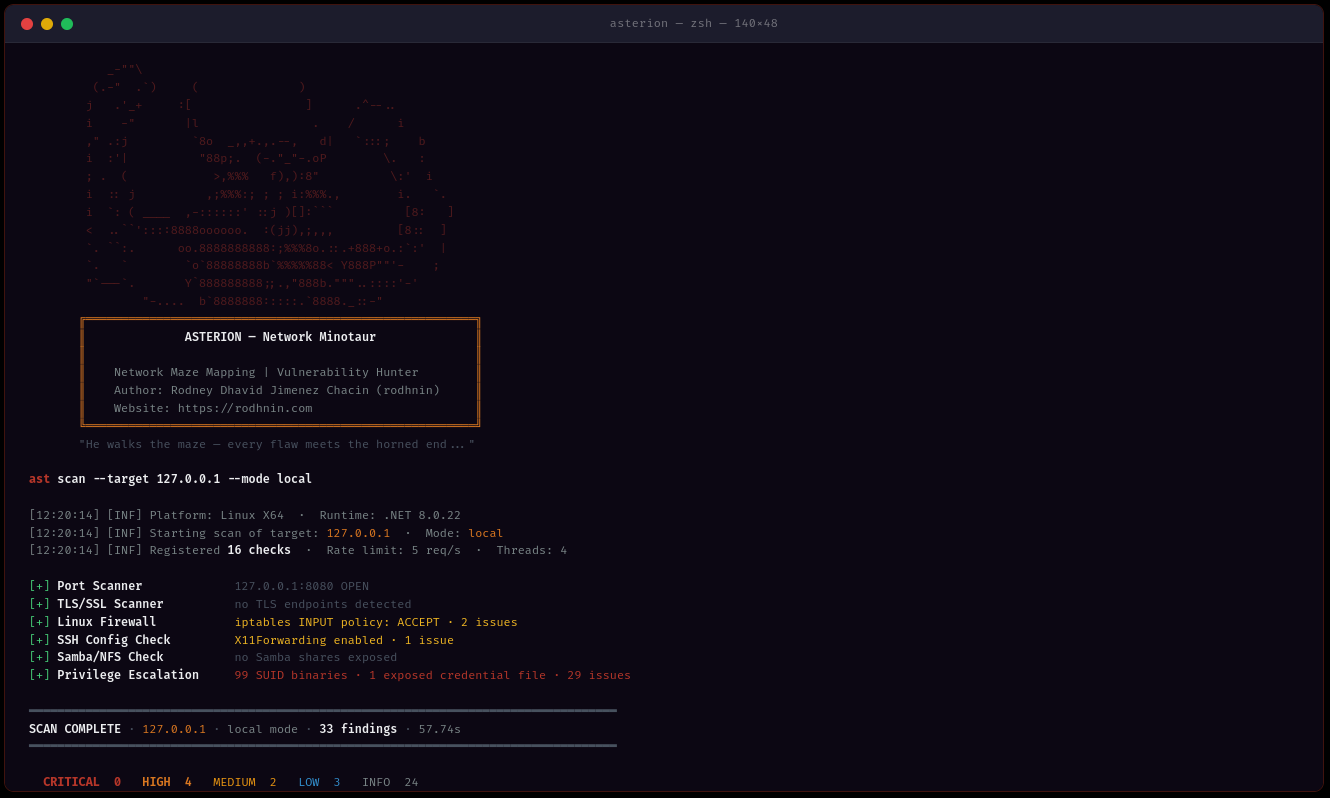 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 danaug23/detect_cve-2026-25177
Production-safe scanner that detects CVE-2026-25177 (AD SPN Unicode Collision) exploitation on Active Directory Domain Controllers. Read-only.
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 aleongx/cve-2025-29810-check
Para verificar si tu entorno podría ser vulnerable al CVE-2025-29810, necesitamos hacer algunas comprobaciones básicas, como: Versión del sistema…
 clong/detectionlab
Automate the creation of a lab environment complete with security tooling and logging best practices
 dnsviz/dnsviz
Analyzes DNS delegation and DNSSEC security by probing resolvers and authoritative servers, then validating, diagnosing, and visualizing zone…
 zyn3rgy/ldaprelayscan
Check for LDAP protections regarding the relay of NTLM authentication