

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.1k9h 19m ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
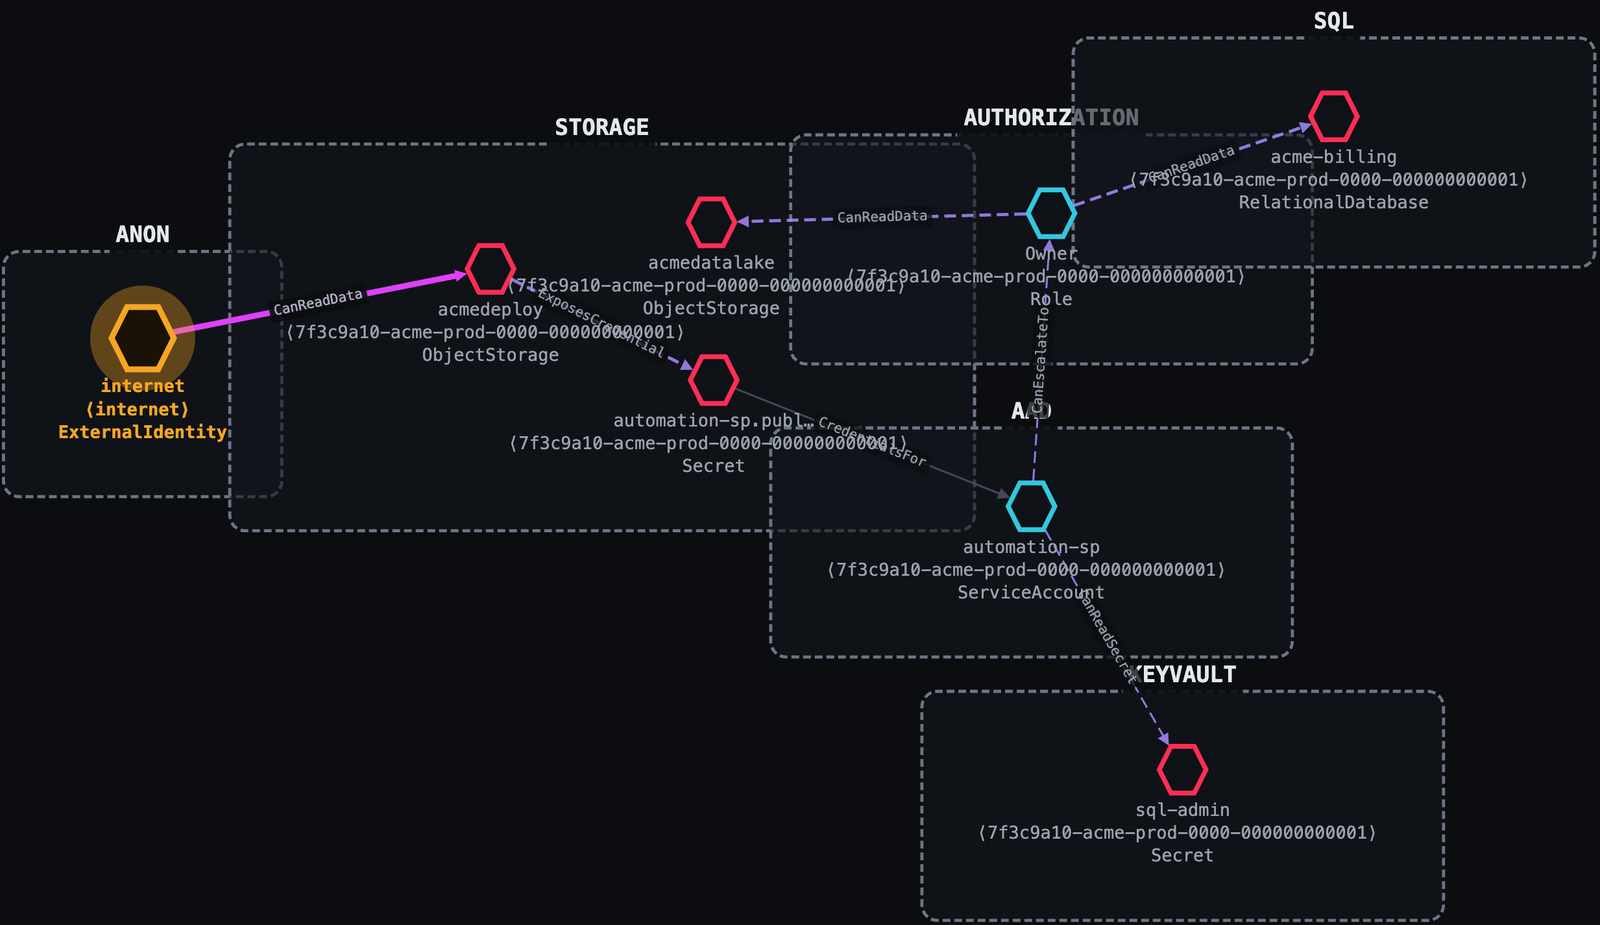 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 password123456/setup-wordpress-with-security-best-practice
Comprehensive guide for hardening WordPress installations: covers admin user changes, HTTPS enforcement, plugin security, file permissions, and…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 o0matte0o/cve-2022-41099-fix
Update WINRE.WIM file to fix CVE-2022-41099
 paveg/rails-activestorage-vips-audit
Agent skill that audits a Rails codebase for CVE-2026-66066 (KindaRails2Shell) — Active Storage + libvips arbitrary file read / RCE, checking Rails…
 kriskimmerle/wheelaudit
Python Wheel File Security Scanner — scan .whl files for security issues before installation. Detects path traversal (CVE-2026-24049), RECORD…
 gdraperi/remote-bitlocker-encryption-report
PowerShell script to mitigate CVE-2018-12038. The script takes a list of PC as input, gets their BitLocker encryption type remotely, and outputs a…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
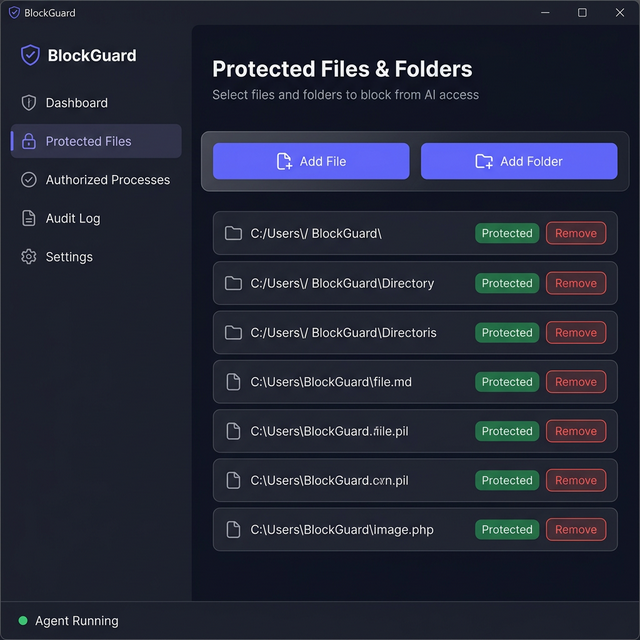 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 antisecc/cve-2022-24716
Exploit for CVE-2022-24716 in Icinga Web 2, allowing unauthenticated file disclosure of configuration files containing database credentials.
 ilismal/nessus_cve-2014-6271_check
Quick and dirty nessus .audit file to check is bash is vulnerable to CVE-2014-6271
 konstantin-kelemen/mysqld_safe-cve-2016-6662-patch
Ansible playbook that applies the Percona patch for CVE-2016-6662 to the mysqld_safe file on CentOS and FreeBSD systems.
 ekamsinghwalia/mitigation-apache-cve-2021-41773-
Mitigation/fix of CVE-2021-41773 A Path Traversal And File Disclosure Vulnerability In Apache
 thetorjancaptain/cve-2024-3094-checker
The repository consists of a checker file that confirms if your xz version and xz-utils package is vulnerable to CVE-2024-3094.
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…