cpanel-cve-2026-41940-fix

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…

One-shot detection and remediation for cPanel/WHM servers compromised via CVE-2026-41940, including IOC checks, malware cleanup, C2 blocking, and…

Secure, ephemeral secret sharing for developers.

Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…

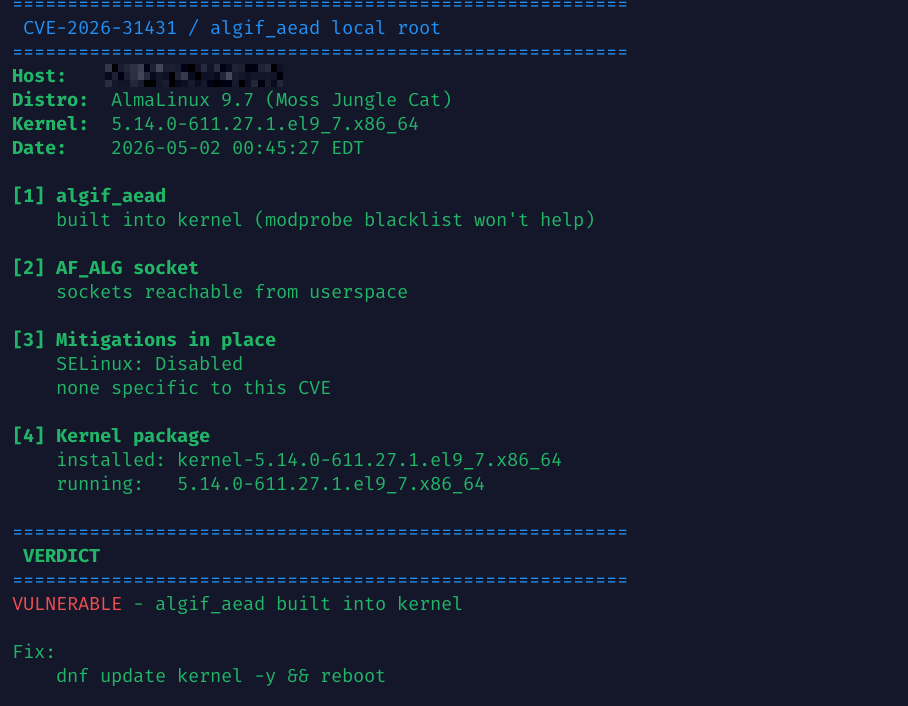
Read-only checker for CVE-2026-31431 (algif_aead local root). Reports kernel/module state and suggests mitigations.

CVE-2026-42533 Nginx

Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy

Reconciliation audit for Alliance Auth's Discord integration: finds guild members holding AA-managed roles that Auth never granted and strips or…

Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…

Mitigation scripts for CVE-2026-50751

Apache Struts version analyzer (Ansible) based on CVE-2017-5638

Security advisory detailing broken access control in UZ801/ES-U3TS MifiService web API, allowing unauthenticated data extraction, config…

A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…

Read-only audit tooling for CVE-2026-0300 (PAN-OS User-ID Authentication Portal exposure)

Source-built nginx 1.25.5 container with backported CVE-2026-42945 fix, OpenSSL bump, full provenance chain, and VEX attestation.

Check local Linux mitigation/exposure status for CVE-2026-31431 "Copy Fail"

Safe read-only version checker + Sigma rule for Redis CVE-2026-23479 (authenticated use-after-free → RCE). Find exposed instances, patch…

Centralized Wazuh SCA Assessment for CVE-2026-42945 on NGINX Servers

Scenario-based training exercise for IT administrators: identify, approve, and deploy critical patches for financial systems under a 48-hour SLA…