

sops
 getsops/sops
Simple and flexible tool for managing secrets
cloud-securityconfiguration-auditingcryptography+6
getsops/sopsSimple and flexible tool for managing secrets
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 cisagov/cset
Cybersecurity Evaluation Tool
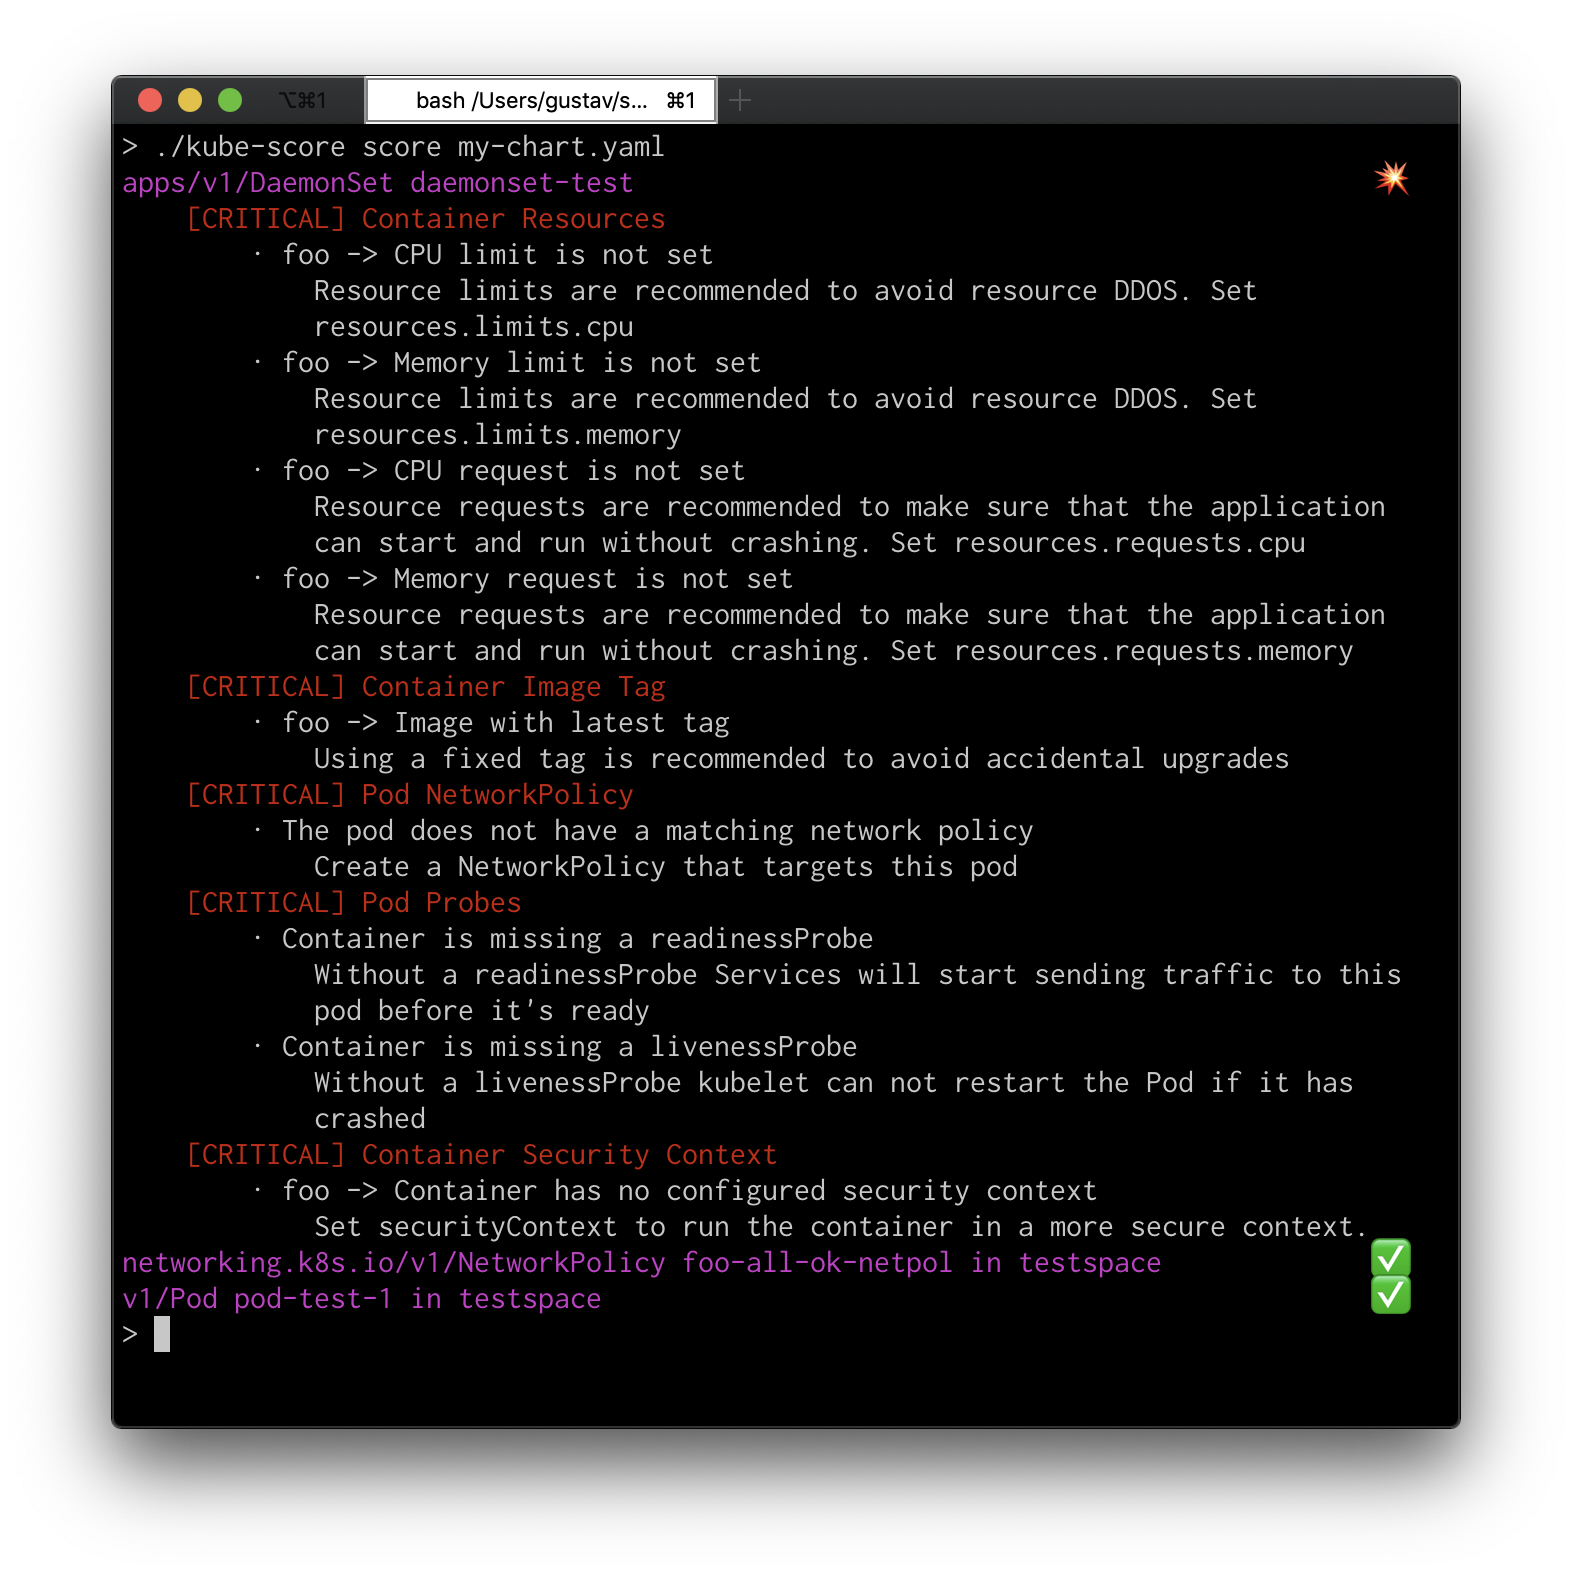 zegl/kube-score
Kubernetes object analysis with recommendations for improved reliability and security. kube-score actively prevents downtime and bugs in your…
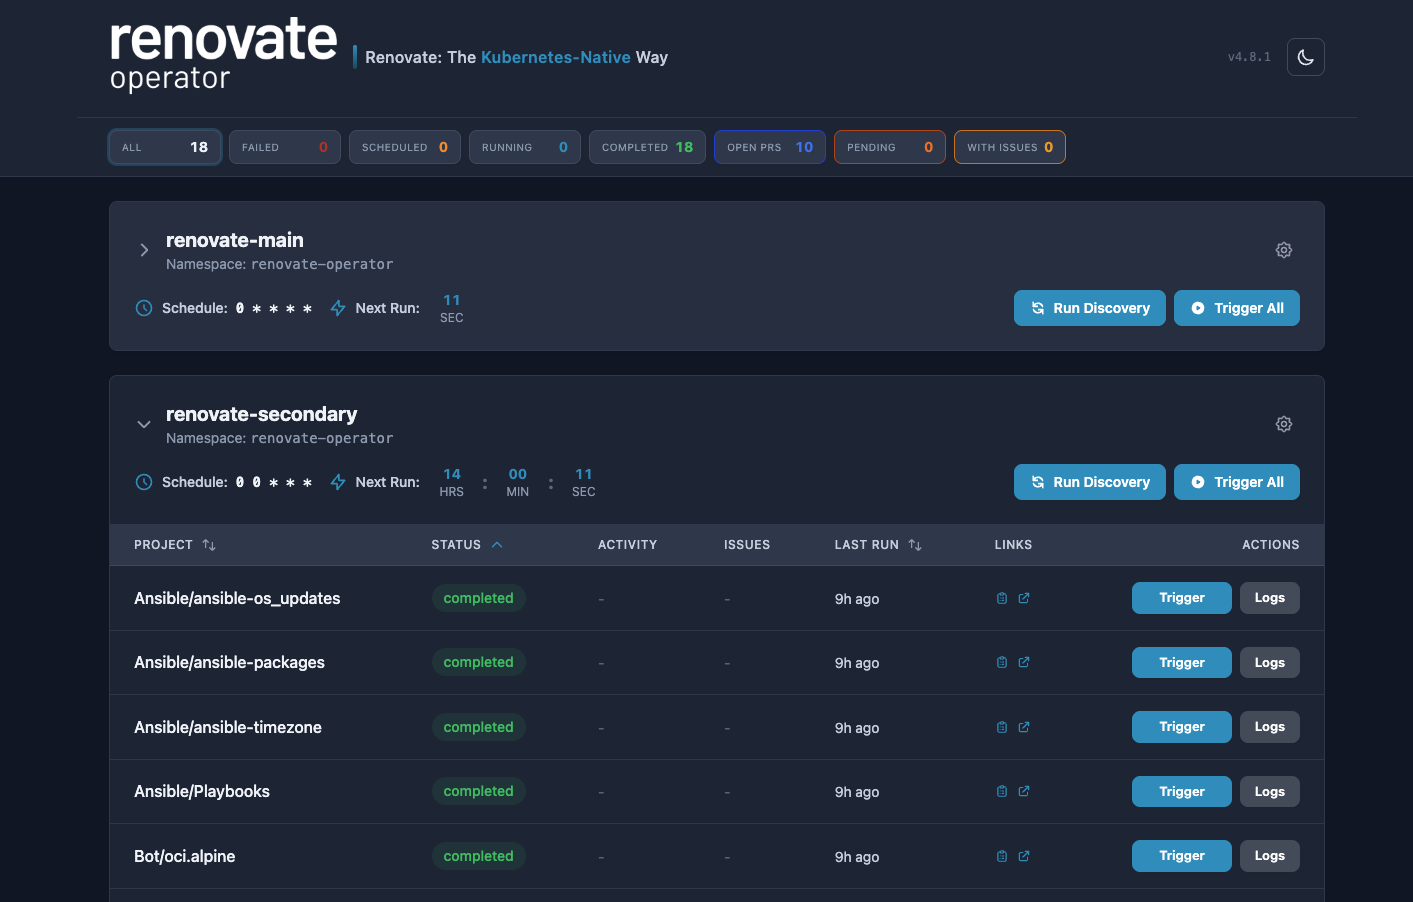 mogenius/renovate-operator
Operator to streamline renovate executions in Kubernetes
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
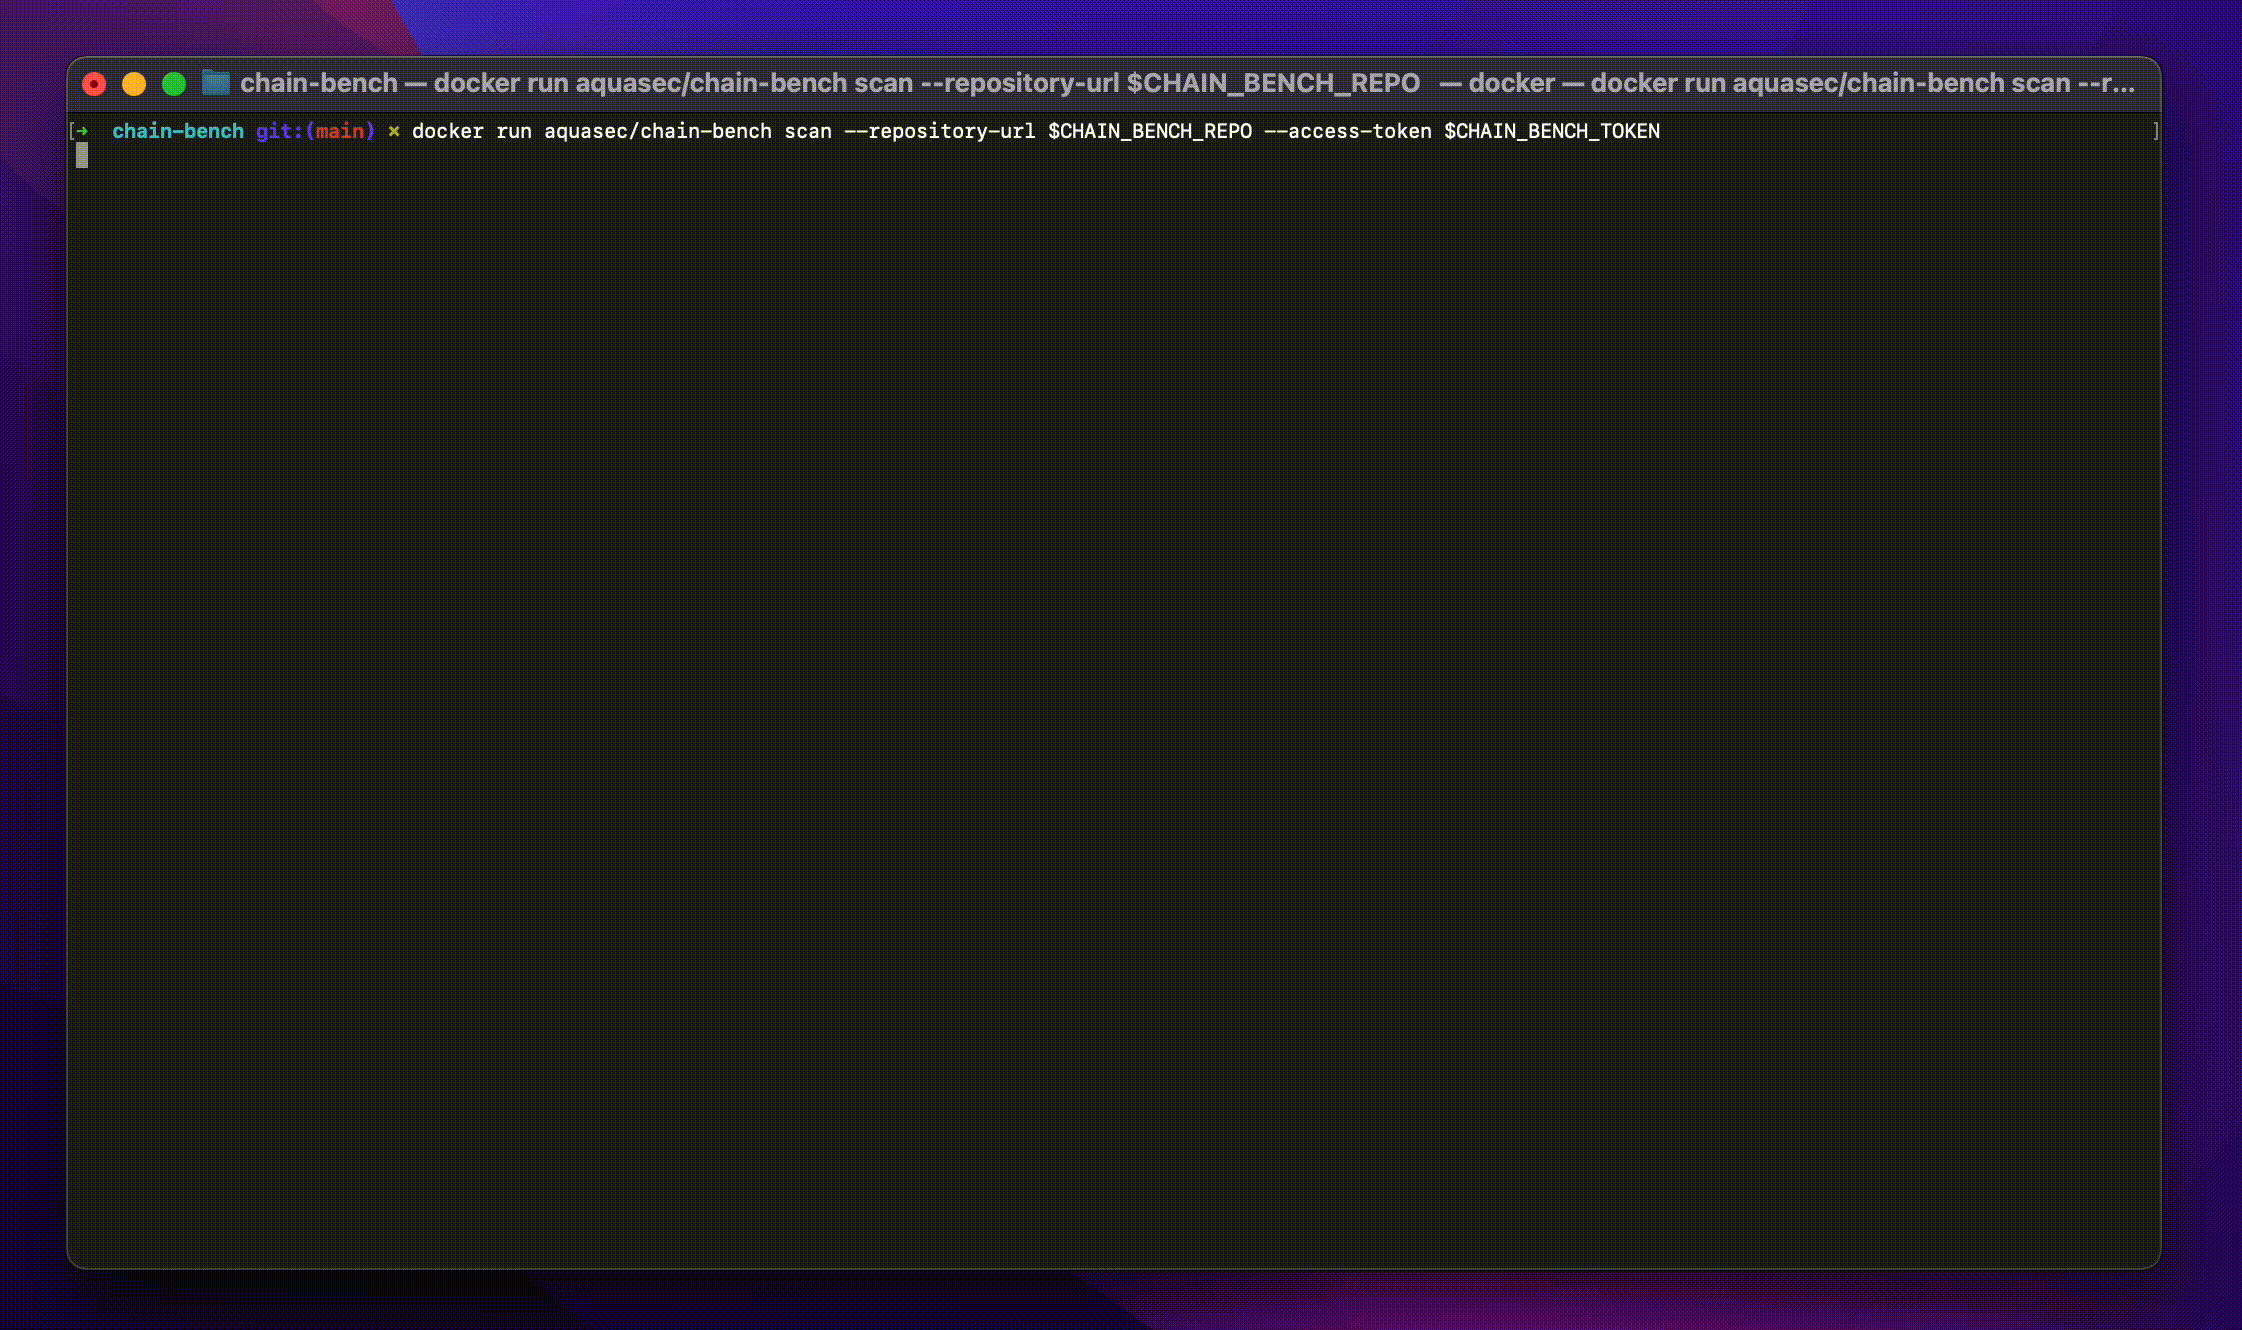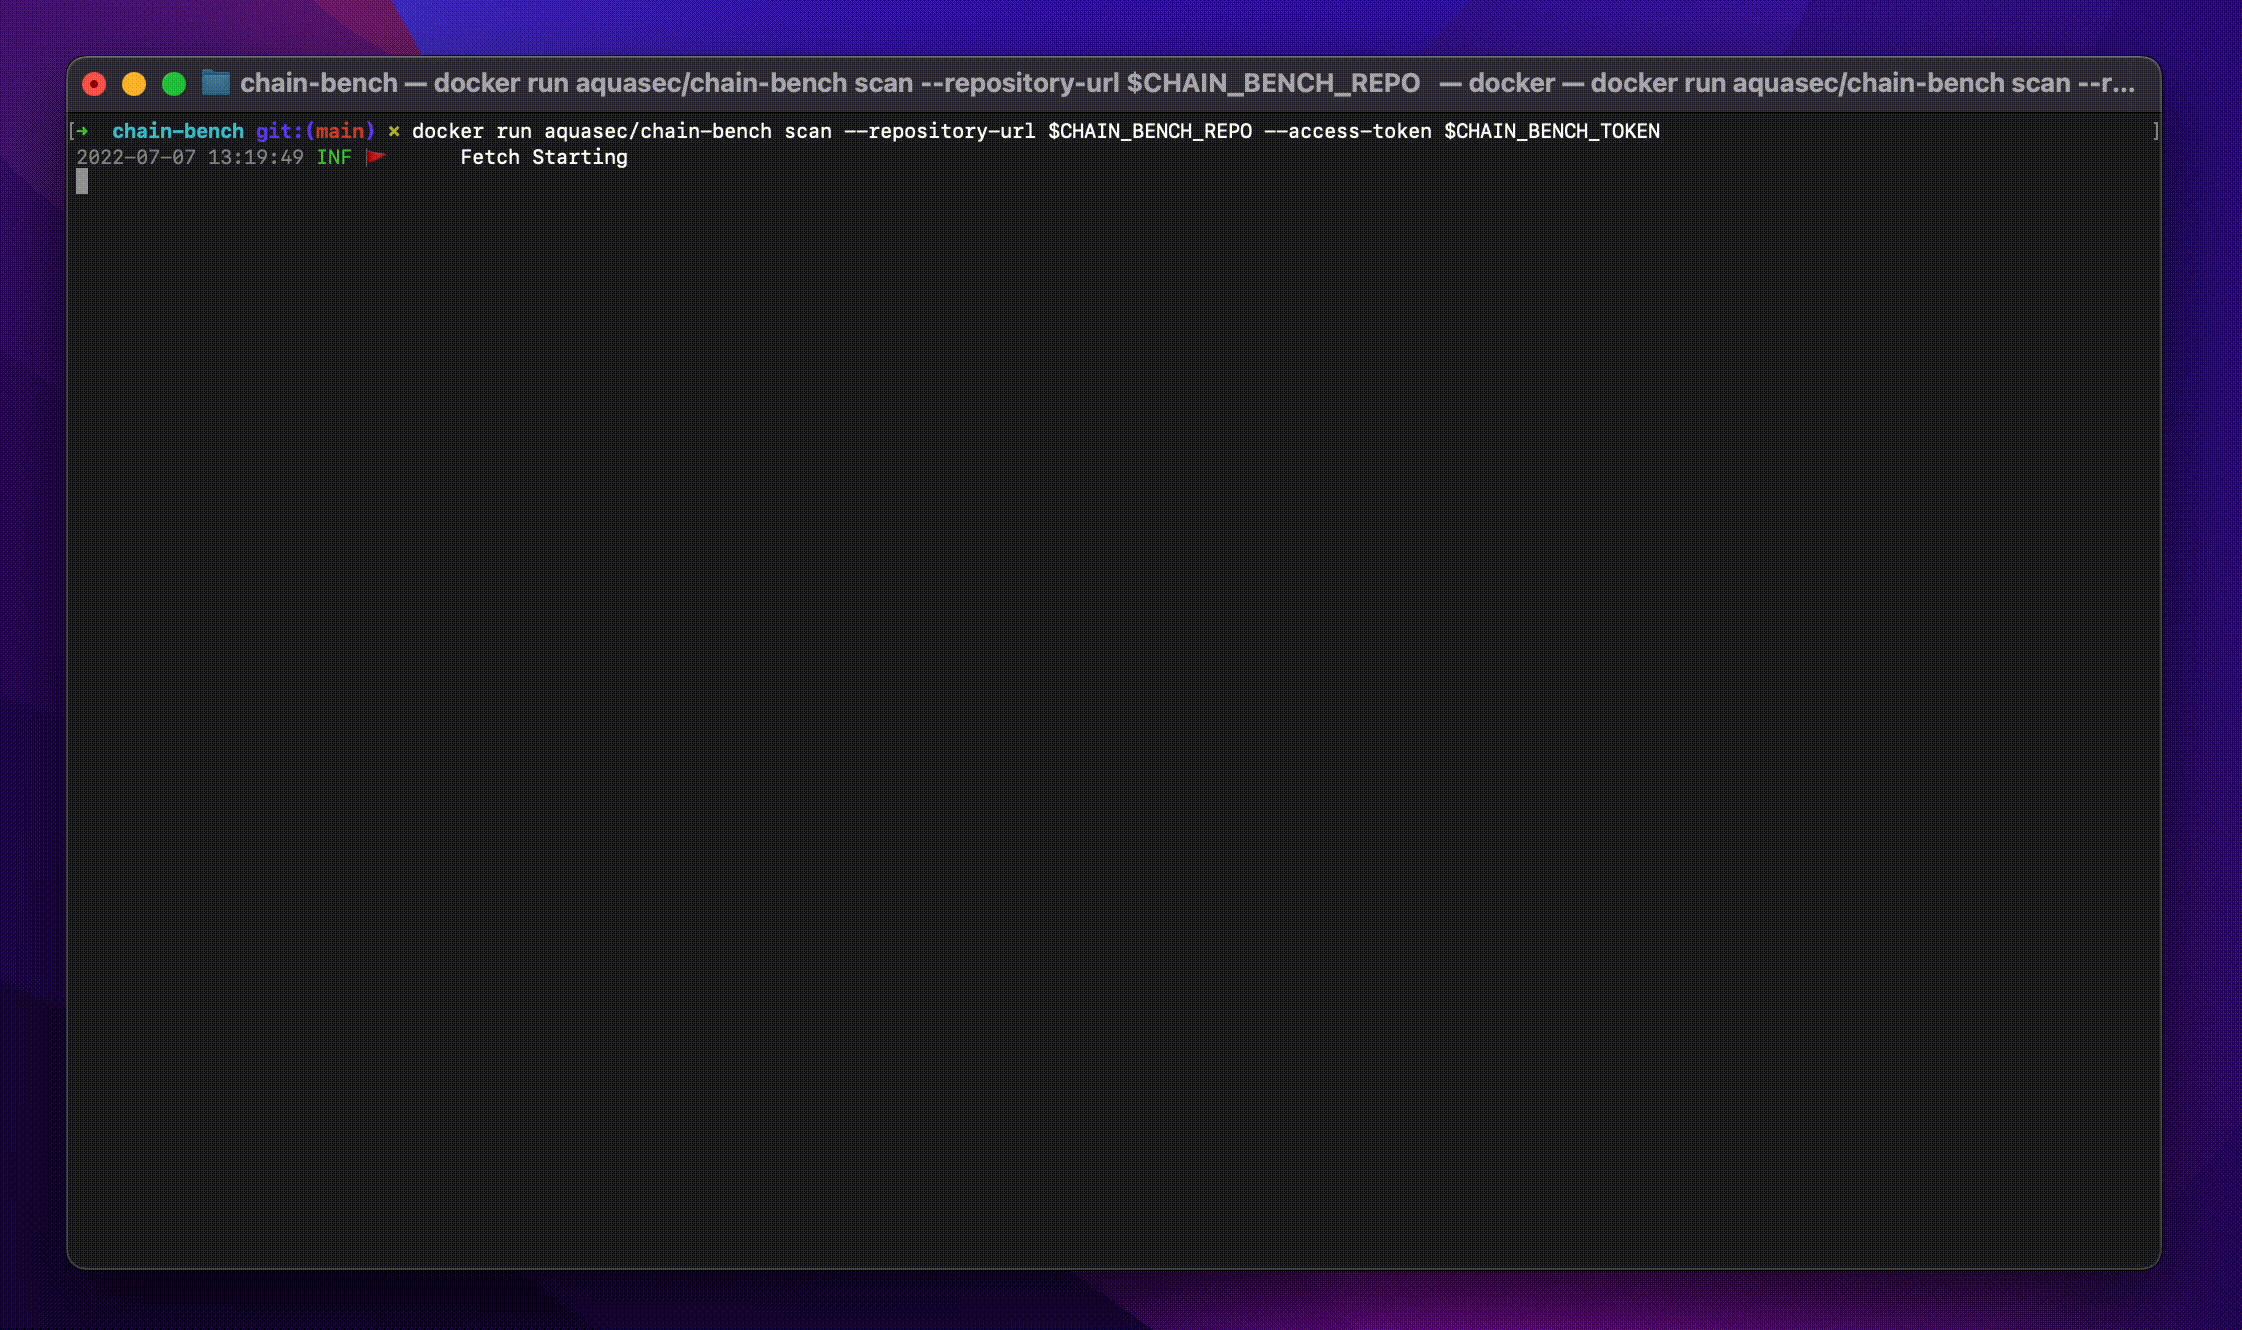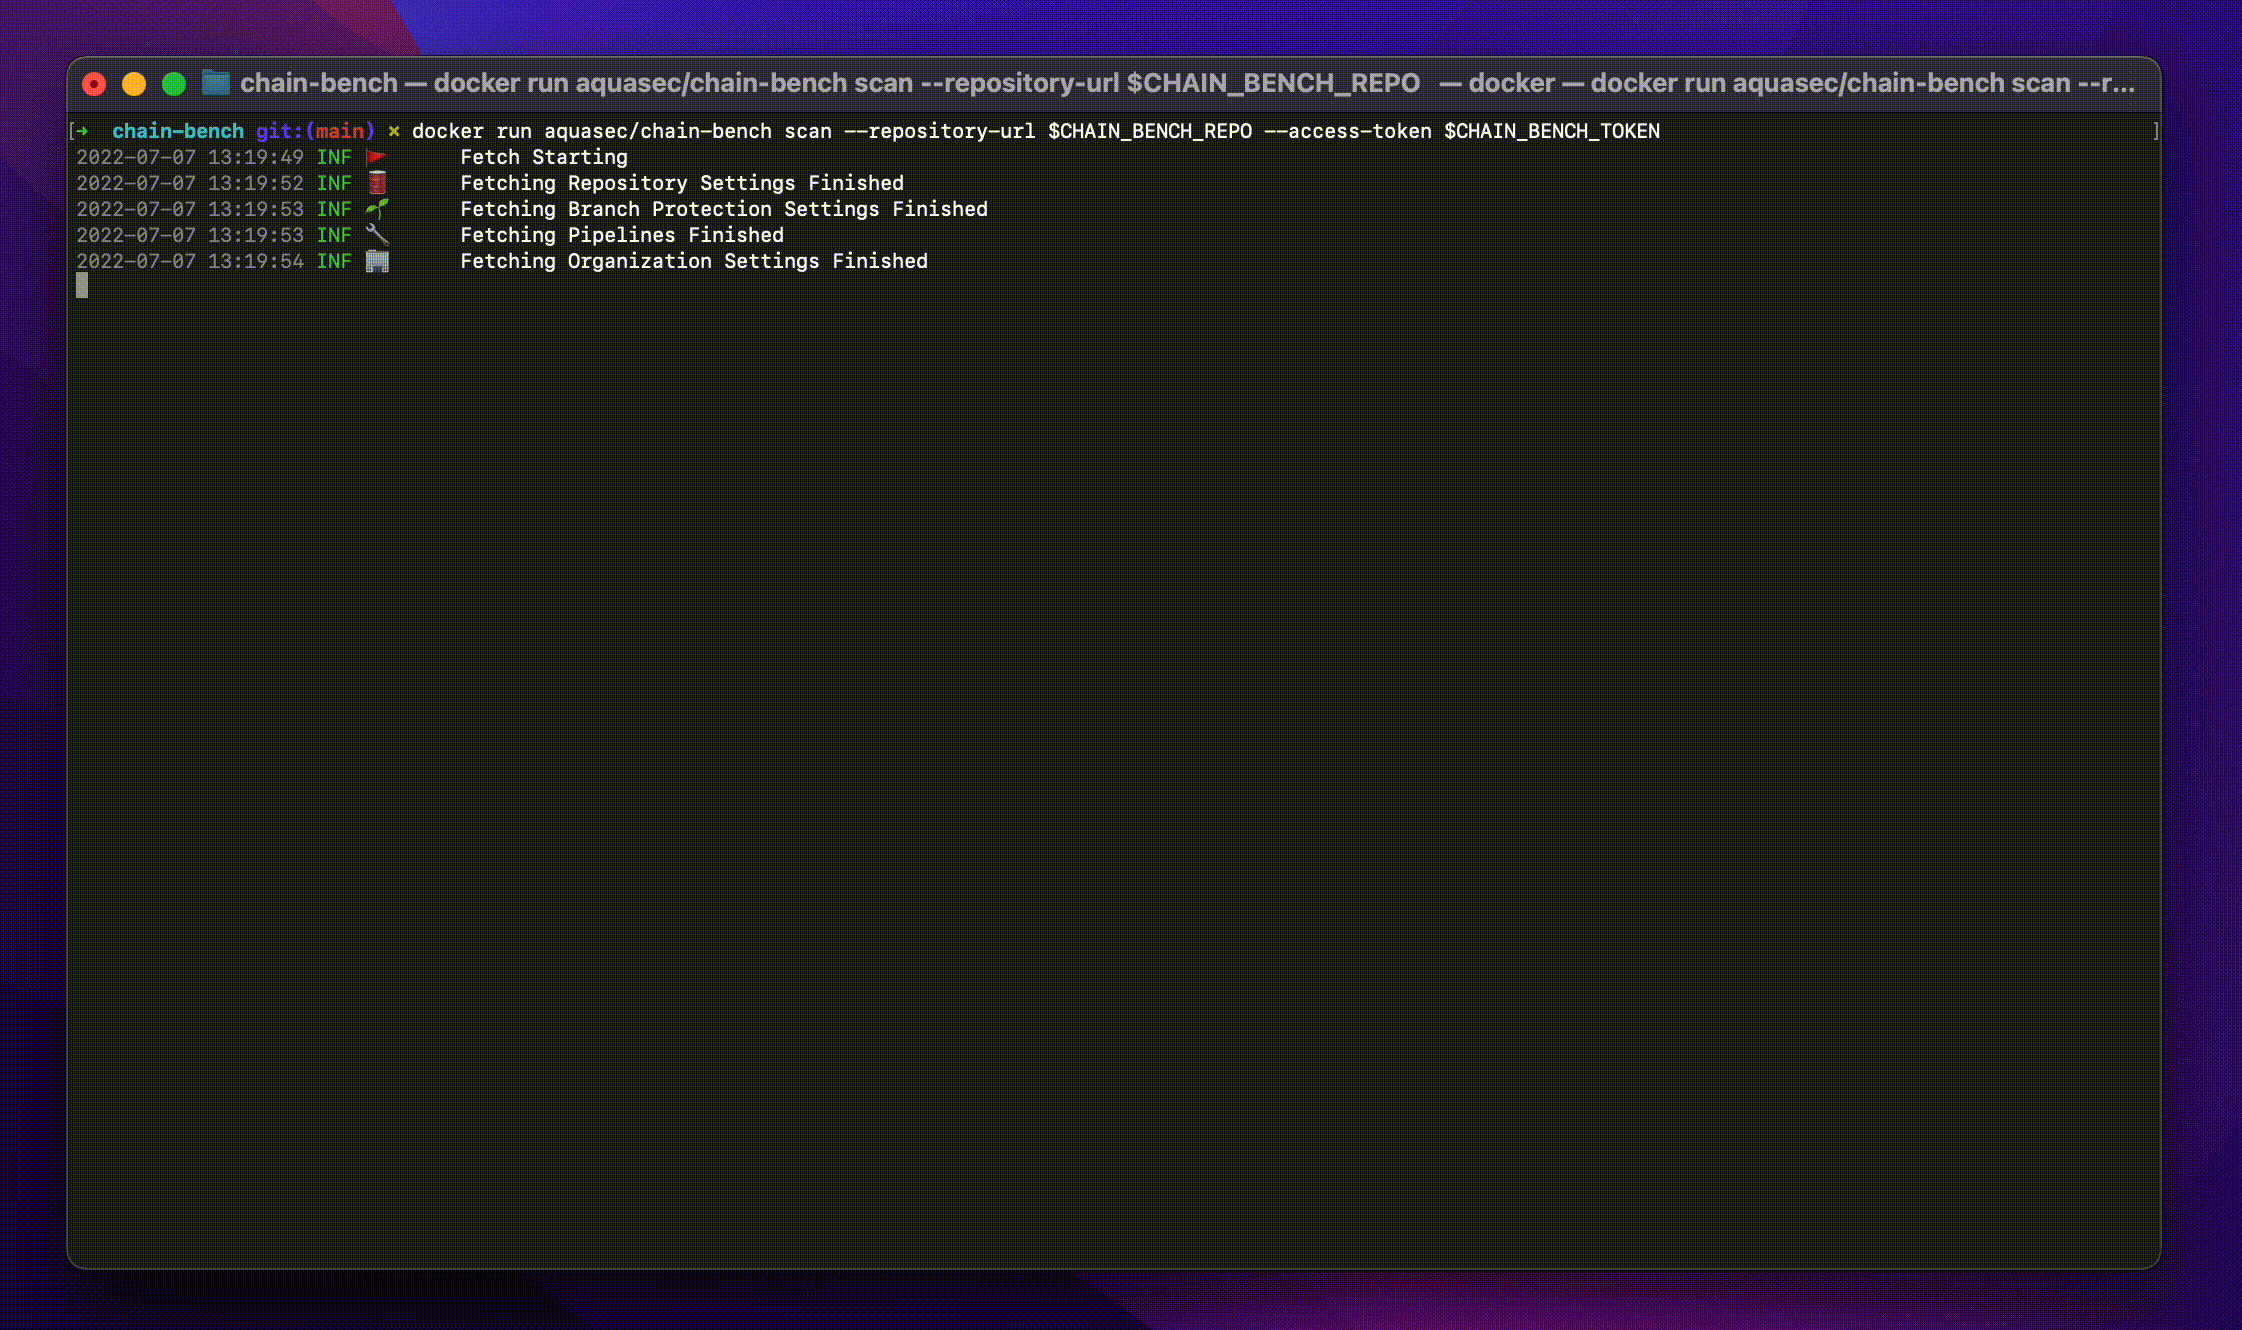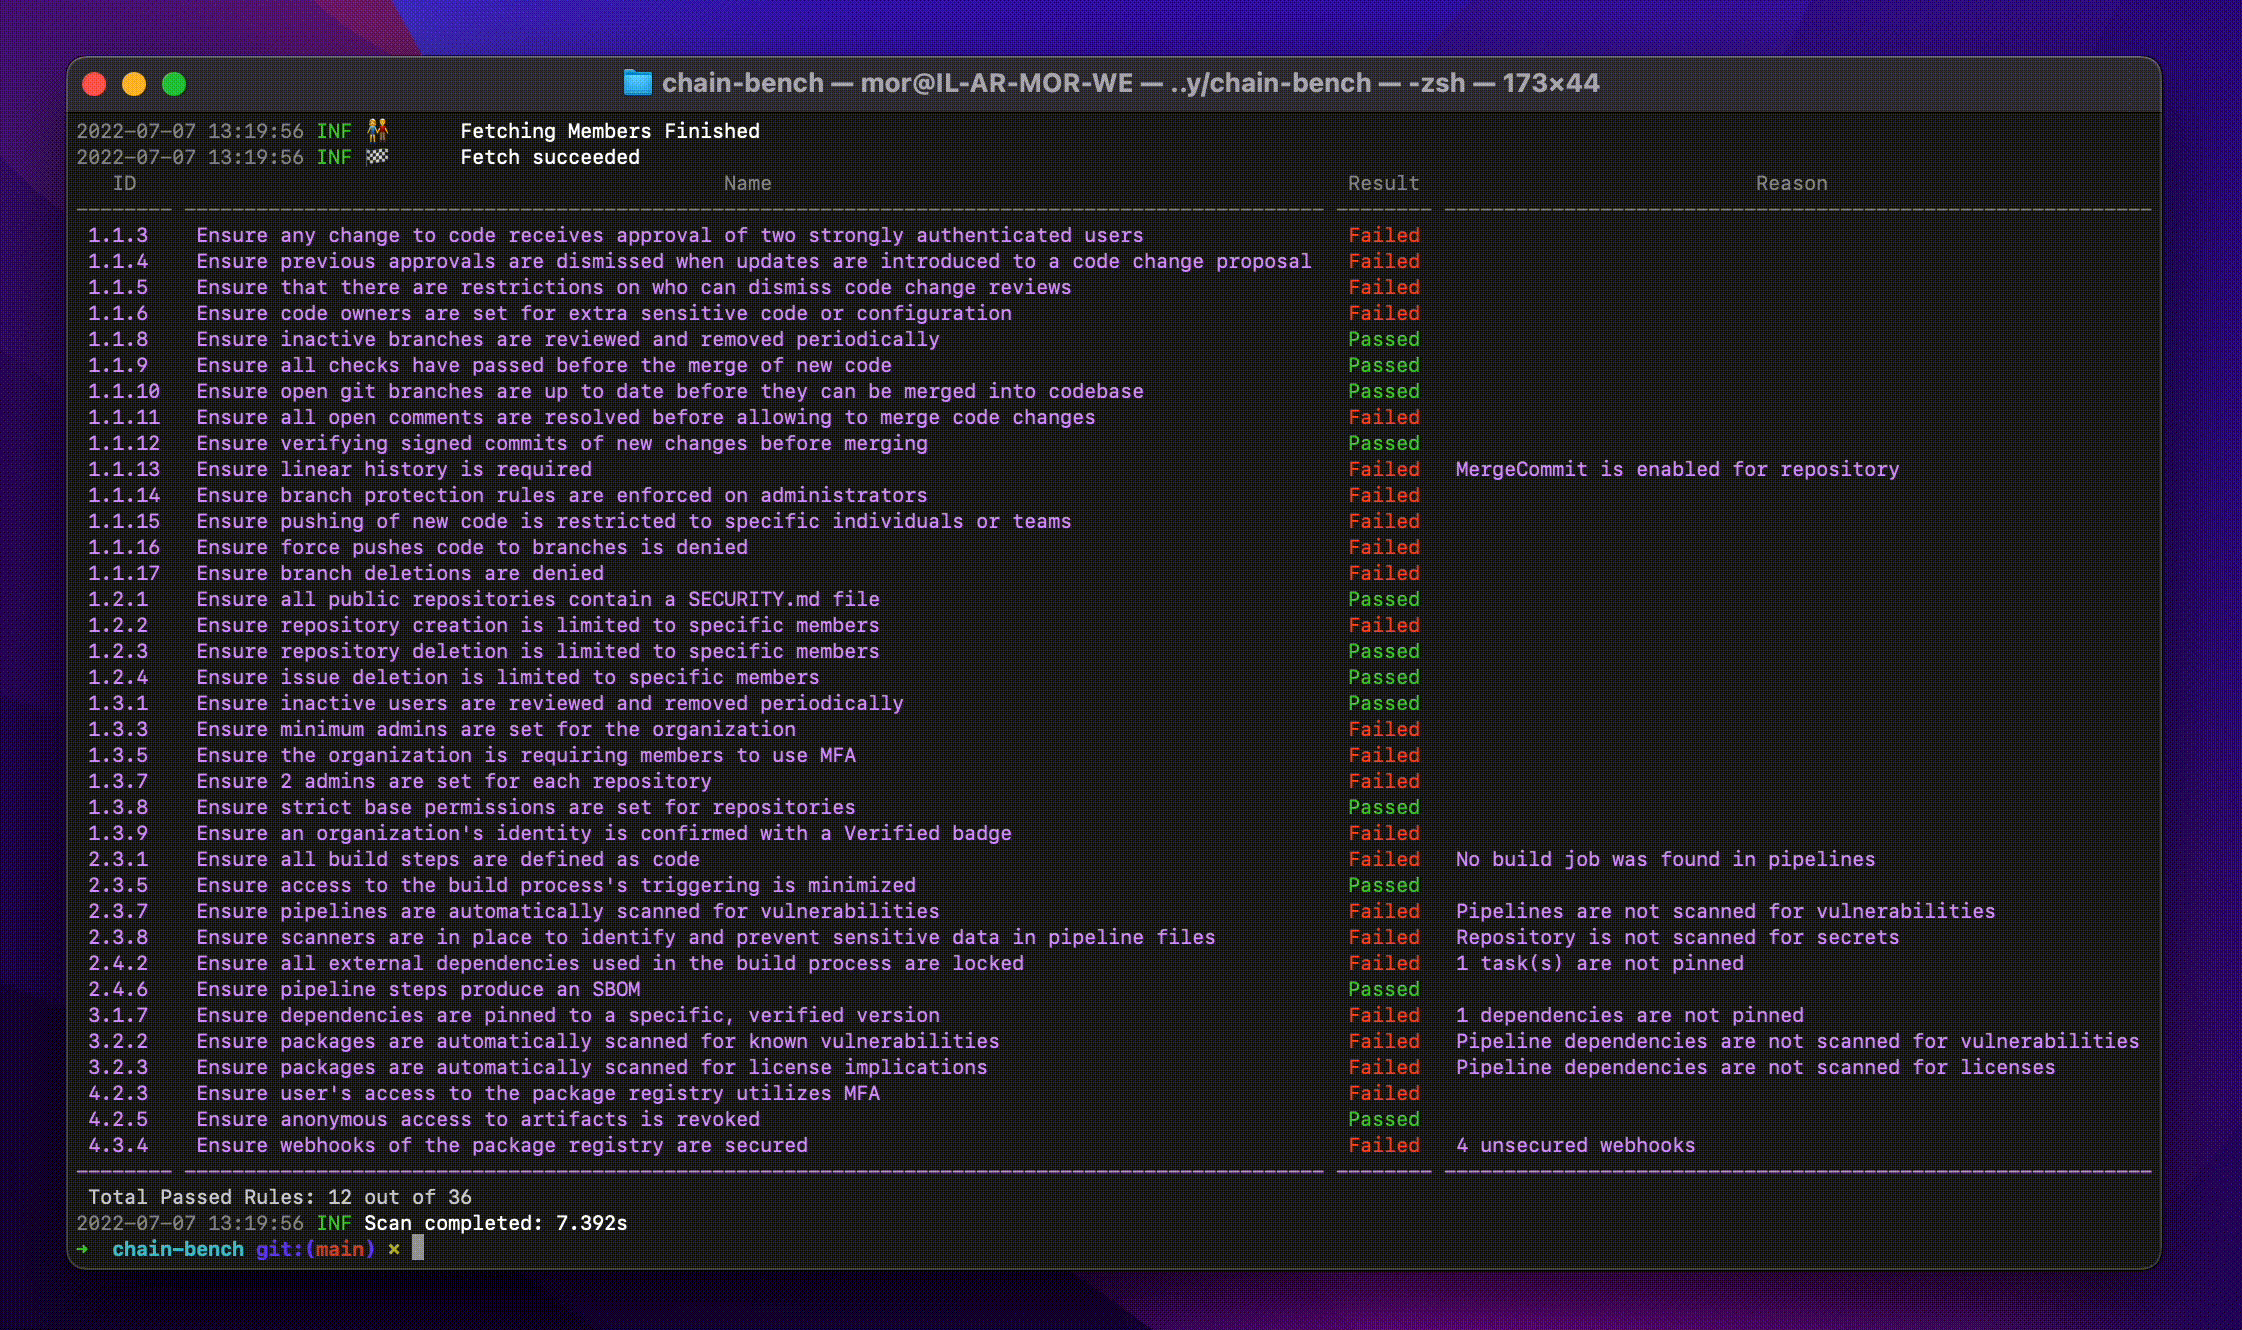 aquasecurity/chain-bench
Audits software supply chain security compliance against the CIS benchmark, scanning SCM settings, branch protections, dependencies, and CI/CD…
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
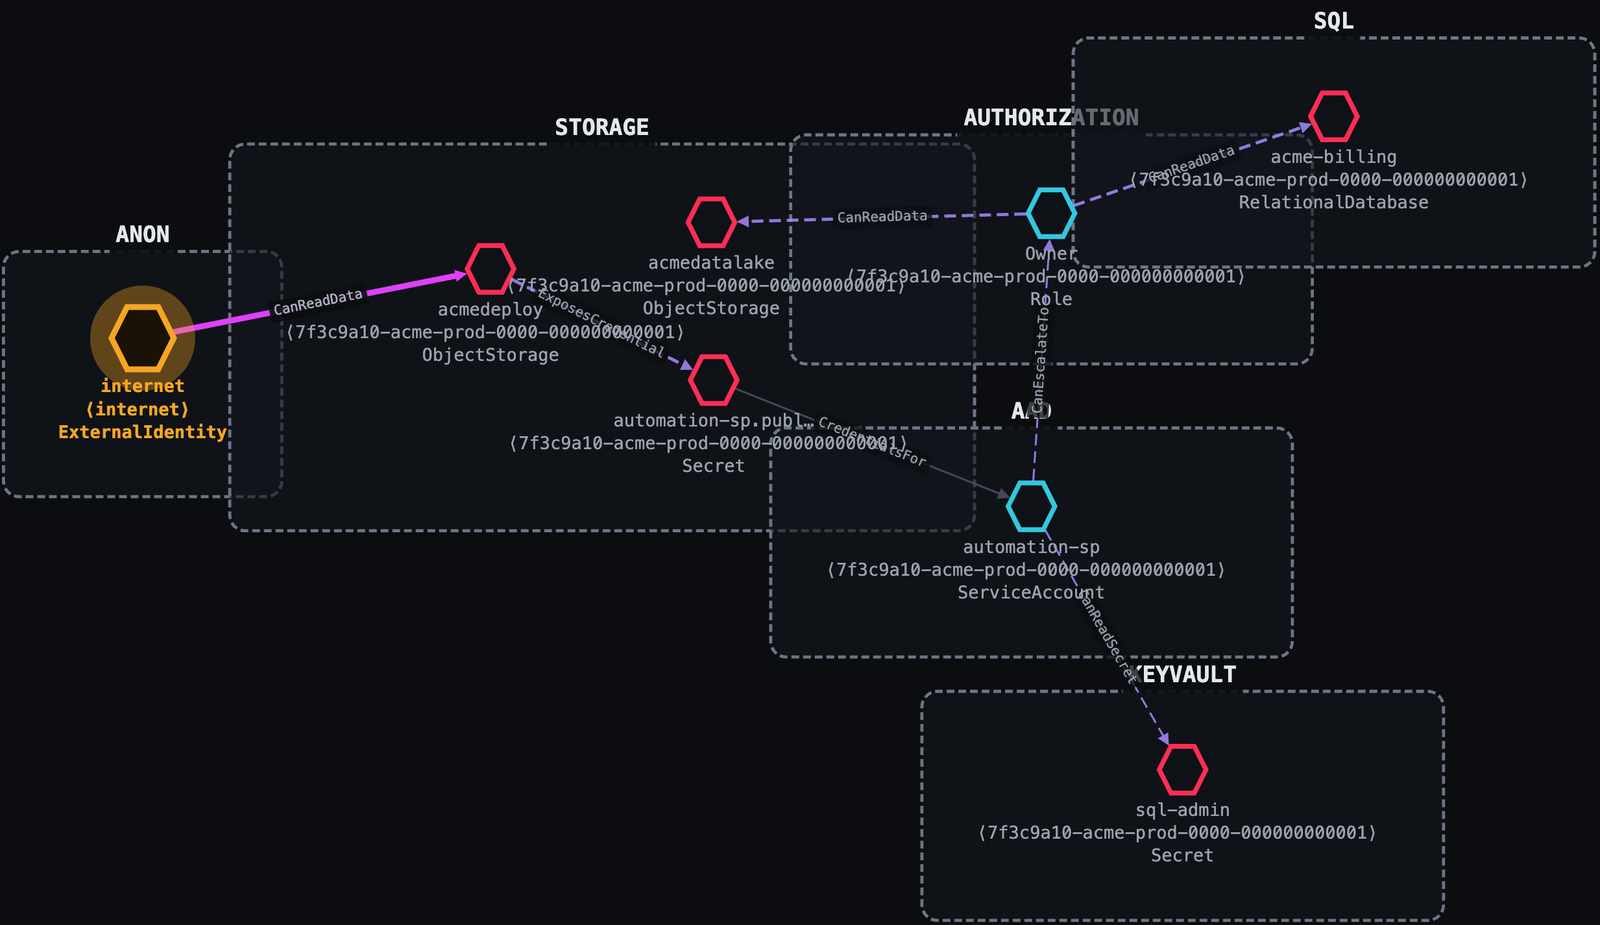 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 master-of-servers/mose
Post exploitation tool for configuration management servers.
 nicholasjackson/cnitch
Container Snitch checks running processes under the Docker Engine and alerts if any are found to be running as root
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
 sreckoskocilic/envocabulary
Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…
 krisiasty/vcheck
Vulnerability detection and mitigation tool for Copy Fail and Dirty Frag bugs (CVE-2026-31431, CVE-2026-43284, CVE-2026-43500)
 ziad-hsn/cpra
CPRA is a high-performance infrastructure monitoring system designed for platform teams managing large-scale microservice architectures. Built on…
 realityone/cve-2026-42945-scan
Scan your NGINX configuration to determine whether it is affected by CVE-2026-42945.
 effiesec/copy-fail-cve-2026-31431
Passive Linux host scanner that classifies exposure to CVE-2026-31431 via kernel version, distro changelog, module status, and AF_ALG reachability,…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…