
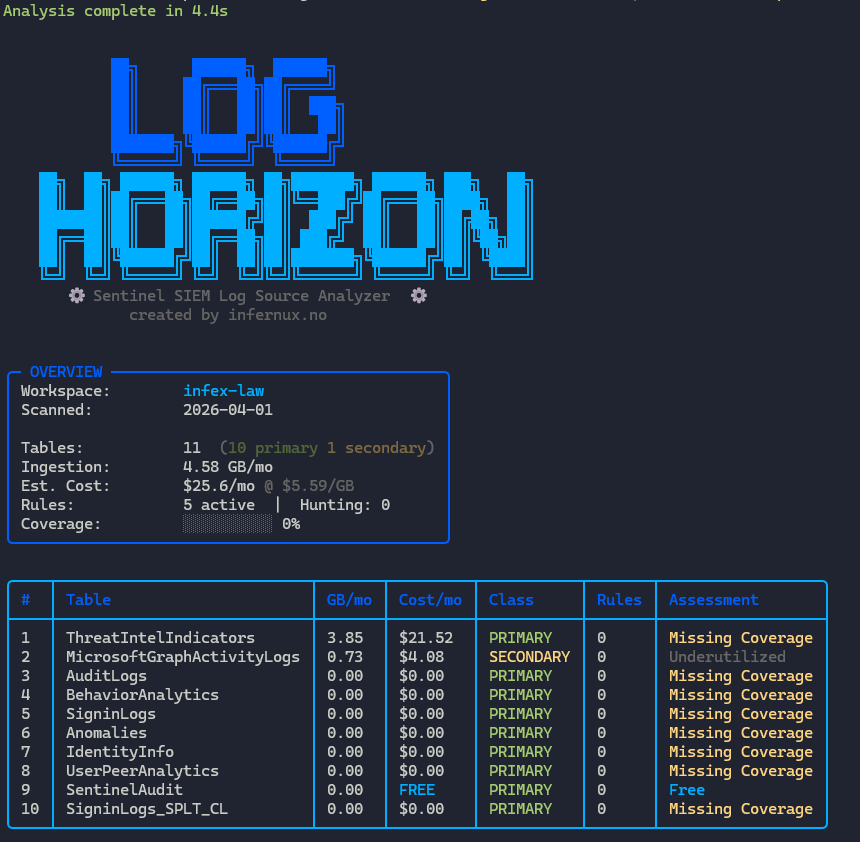
log-horizon
 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
cloud-infrastructure-securitycloud-securityconfiguration-auditing+4
313 days ago
lnfernux/log-horizonMicrosoft Sentinel SIEM Log Source Analyzer
 ovh/the-bastion
Authentication, authorization, traceability and auditability for SSH accesses.
 everest90909/yellowkey-winre-remediation
PowerShell-based Intune remediation package that detects and removes the vulnerable autofstx.exe BootExecute entry from offline WinRE images, then…