
dockerscan
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
cloud-securityconfiguration-auditingcontainer-security+4
cr0hn/dockerscanThe Most Comprehensive Docker Security Scanner
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandbox
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 nationwide-group-oss/cryptoptic
CodeQL-based scanner that inventories cryptographic function calls across repositories and GitHub organizations, producing a Cryptographic Bill of…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 ossf/allstar
GitHub App to set and enforce security policies
 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
 schroeder-sys/pantheon-souverainete
Infrastructure cloud modulaire, redondante et 100% souveraine pour s'affranchir des GAFAM. Guides techniques, architecture Zero-Trust et chiffrement…
 hackervlogofficial/cve-2026-23918
This is a proactive tool for security auditing. For your GitHub repository, you’ll want a description that highlights its safety (non-intrusive) and…
 isagoakira/ghes-cve-scanner
Scans GitHub Enterprise Server instances for CVE-2026-3854 and CVE-2026-4821, providing version-based detection with batch scanning and multiple…
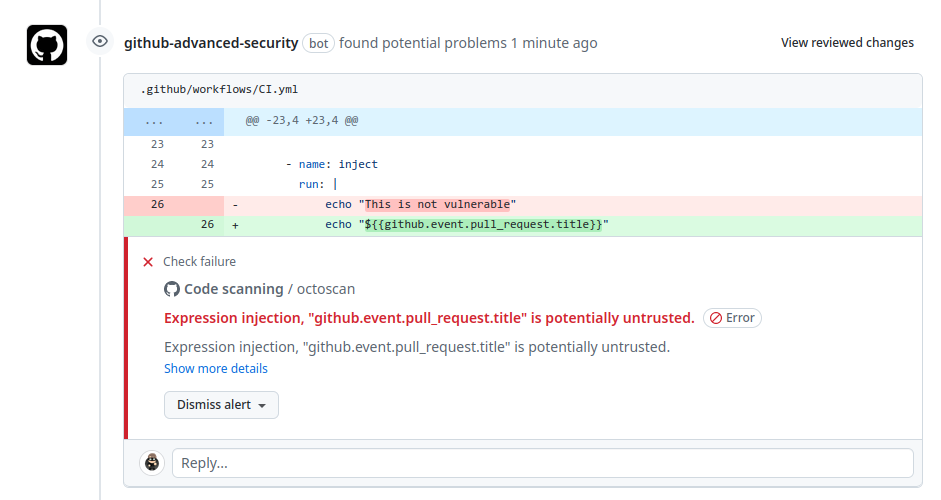 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.
 plutosecurity/mcpwnfluence
Information about CVE-2026-27825 & CVE-2026-27826 discovered by Pluto Security and a bash script for identifying vulnerable mcp-atlassian instances…
 mf-labs/witcher
Managing GitHub Advanced Security (GHAS) Controls at Scale
 legit-labs/legitify
Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets
 tindersec/gh-workflow-auditor
Script to audit GitHub Action Workflow files for potential vulnerabilities.