

fad-checker
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
code-analysisconfiguration-auditingdefensive-tools+6
1
9pings/fad-checkerBuildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
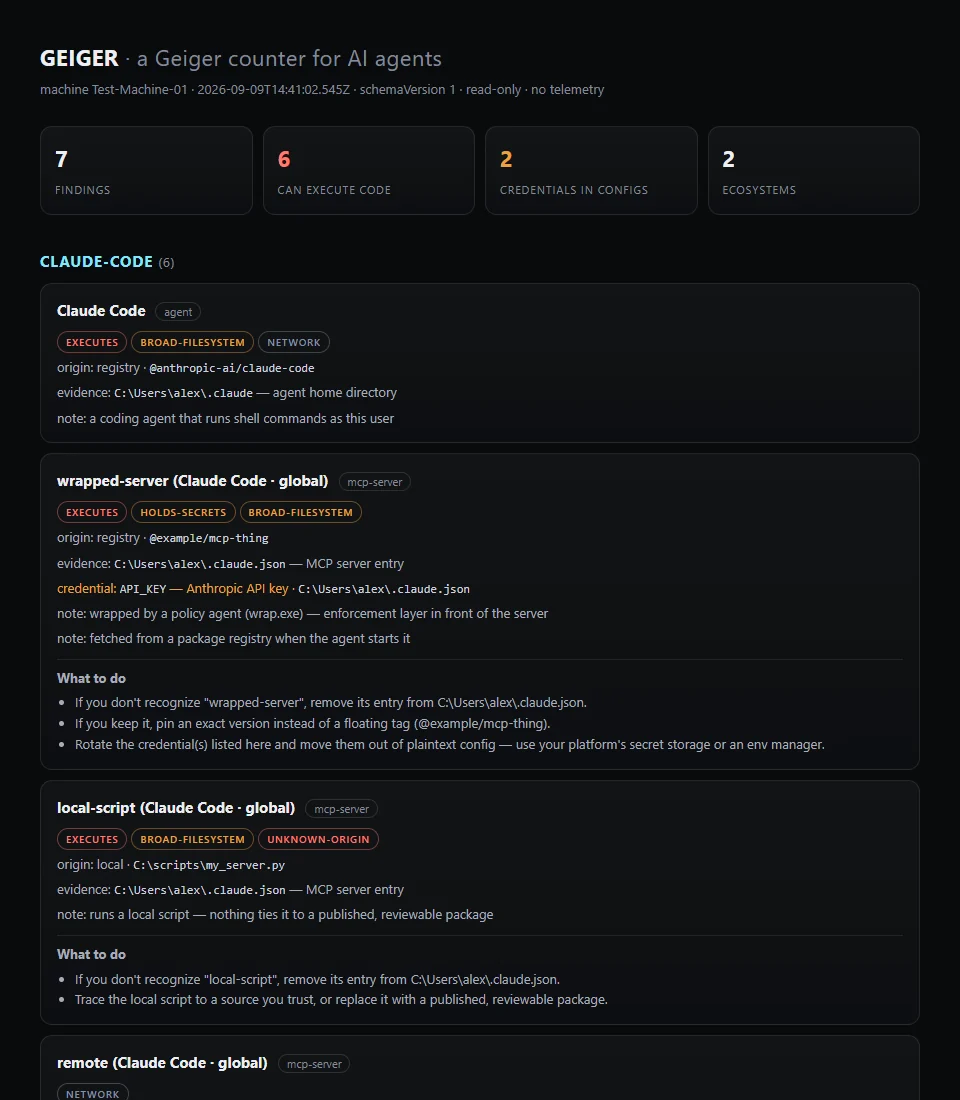 atomburstofficial/geiger
Read-only CLI that inventories AI agents, MCP servers, plugins, and extensions on a machine, reporting their capabilities and exposure with…
 wavesman/cve-2026-31431-fleet-remediator
Fleet-scale CVE-2026-31431 audit and remediation orchestrator for Linux hosts via SSH, with strict host-key verification and multi-format reporting.
 atlassian/bitbucket-iac-scan
Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.
 korben00/no-gdid
Read, understand and silence the Windows GDID device identifier (the ID that tracked a hacker through a VPN). Verified on a real Win11 VM. Honest: it…
 ustayready/outpost
AWS Testing and Reporting Management Tool
 kitskater/legacyshield-cve-2017-0144
Defensive Windows security application providing compensating controls for CVE-2017-0144 (EternalBlue/MS17-010) through SMB monitoring, attack…
 grupooruss/cve-2024-6387
Python script to scan and secure SSH configurations against the CVE-2024-6387 race condition vulnerability, with automated LoginGraceTime adjustment…
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…
 titus-soc/-cve-2024-3094-vulnerability-checker-fixer-public
A lightweight utility designed to detect and remediate systems affected by CVE-2024-3094, a critical vulnerability impacting [insert affected…
 gagaltotal/cve-2026-42945-nginx-rift-toolkit
Automated toolkit for scanning, exploiting, and patching CVE-2026-42945 (critical RCE in nginx). Includes network scanner, heap spray exploit, and…
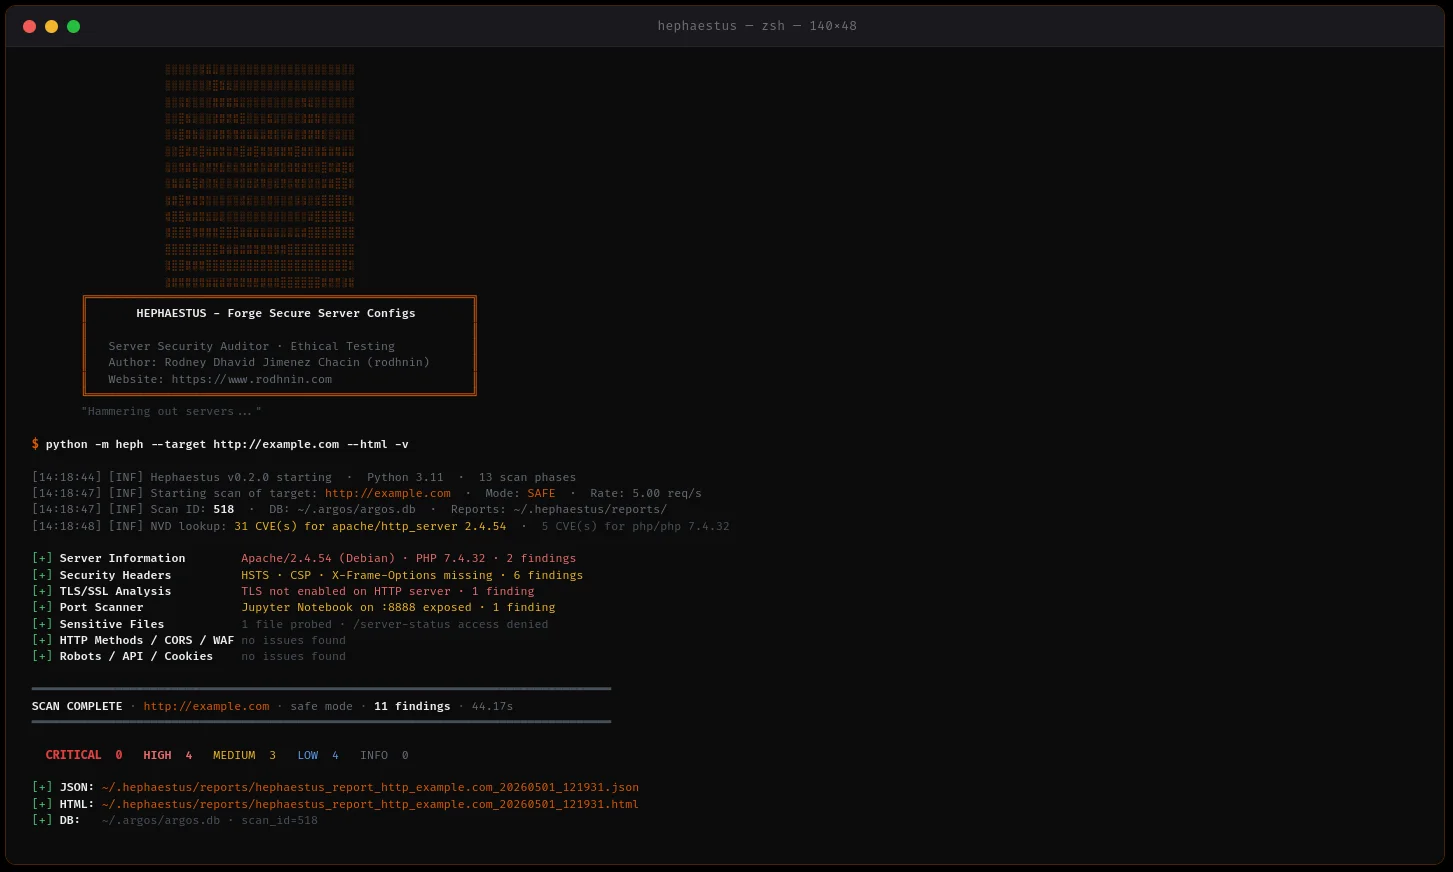 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
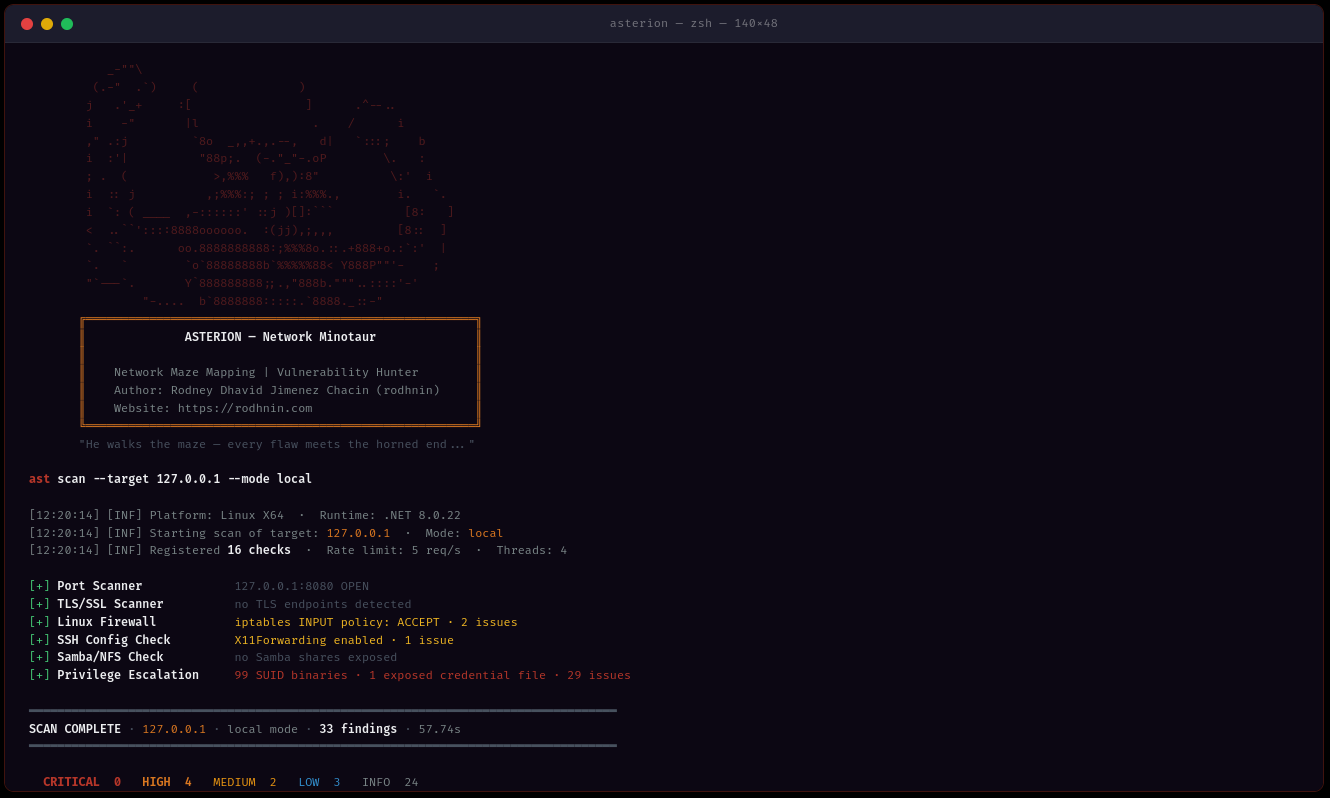 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 cyb3rint3l-labs/serversecurityaudit
PowerShell-based Windows Server Security Audit Engine by Cyb3rint3l Labs. Measures alignment with the NIS2 directive and maps findings to MITRE…
 lateralblast/lunar
A UNIX security auditing tool based on several security frameworks
 trimstray/otseca
Open source security auditing tool to search and dump system configuration. It allows you to generate reports in HTML or RAW-HTML formats.
 tmobile/pacbot
PacBot (Policy as Code Bot)
 hubblestack/hubble
Hubble is a modular, open-source security compliance framework. The project provides on-demand profile-based auditing, real-time security event…