

runeward
 runewardd/runeward
Governed execution cells for AI agents.
ai-securityauthentication-authorizationcloud-security+7
1
runewardd/runewardGoverned execution cells for AI agents.
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 xiaoqimikko/jetty-line-check
CVE-2026-2332 and 4 more 2026 Jetty CVEs: which does your Jetty (or Spring Boot) build hit, and does the fixed version Jetty names even exist on…
 nicmx/fort-validator
RPKI Relying Party and RTR server that validates BGP route origin authorizations and serves validated data to routers over the RTR protocol.
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 disrex-group/stylesmuggler-adobe-patches
composer require delivery of Adobe's official APSB26-146 (CVE-2026-75650) fix for Magento, via cweagans/composer-patches. Auto-selects the patch for…
 safeagent-beihang/clawguard
Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…
 dev-sec/puppet-os-hardening
This puppet module provides numerous security-related configurations, providing all-round base protection.
 xiaoqimikko/netty-http2-check
Offline Java tool that scans jars and versions to determine exposure to seven netty-codec-http2 CVEs, recommending the single patched version that…
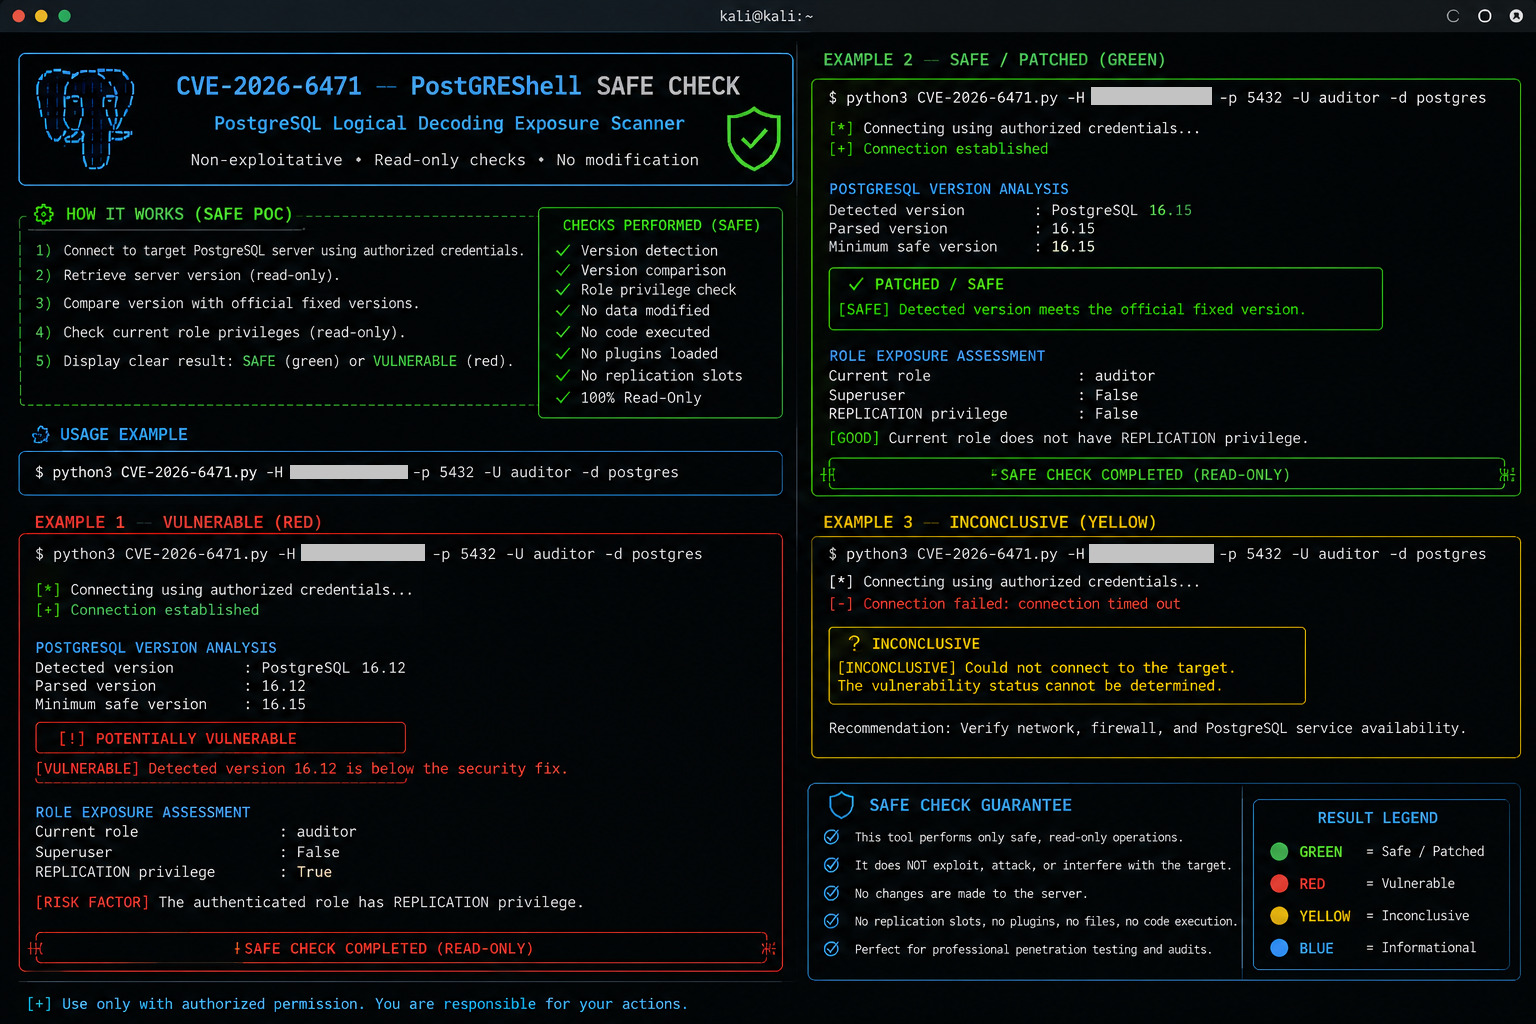 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…
 xcoy0te/cve-2026-83548-checker
Non-intrusive detector for SonicWall SMA 1000 exposure to CVE-2026-83548/-83549 (version/patch-state check; no exploitation)
 xiaoqimikko/thymeleaf-check
Offline checker for Thymeleaf CVE-2026-40477 / CVE-2026-41901 — tells you which of the two CVSS 9.0 SSTI flaws you are exposed to, and whether your…
 tcollins-hashicorp/vault-cve-2026-5006-audit
Audit and educational toolkit for CVE-2026-5006, a Vault templated-policy slash-injection vulnerability. Includes a read-only audit script generating…
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
 xiaoqimikko/tomcat-line-check
CVE-2026-24880: does Apache's upgrade advice actually apply to your Tomcat? Detects the fix by class presence, not version comparison. Covers…