
enumerate-iam
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
authentication-authorizationcloud-securityconfiguration-auditing+6
1.3k
andresriancho/enumerate-iamEnumerate the permissions associated with AWS credential set
 thomaspoppelgaard/netscaler-ctx697096-checker
Read-only checker for Citrix NetScaler CTX697096 (CVE-2026-88771–88778): verifies build, CVE preconditions and upgrade risks, and sweeps public IoCs…
 nu11secur1ty/cisco
Security auditing toolkit for Cisco network devices, focusing on configuration review, vulnerability detection, and penetration testing of enterprise…
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 stillbigjosh/kube-reaper
Scans Kubernetes clusters from any identity, flags dangerous permissions, and chains them into multi-step escalation paths to cluster compromise.
 yellowkeybitlocker-cve/yellowkey-bitlocker-cve-2026-45585
YellowKey BitLocker recovery audits CVE-2026-45585: yellowkey github, TPM, recovery key backup. Windows 10/11 CLI GUI, portable audit tool for…
 itskill-jp/wordpress-upgrade-check
Read-only check of every WordPress core version on a server. Flags CVE-2026-87902 (fixed in 7.1.2 and backports), auto-updates turned off, and…
 furkankayapinar/cve-2026-94127
Read-only defensive detector for CVE-2026-94127 in F5 BIG-IP APM. Fingerprints hosts, checks versions via iControl REST, and verifies OAuth…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 fauxrougee/smartscanner-source
Web vulnerability scanner built with C++17 and Qt 6, featuring a GUI, CLI, configurable crawling, and JSON reports. Reconstructed for educational…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
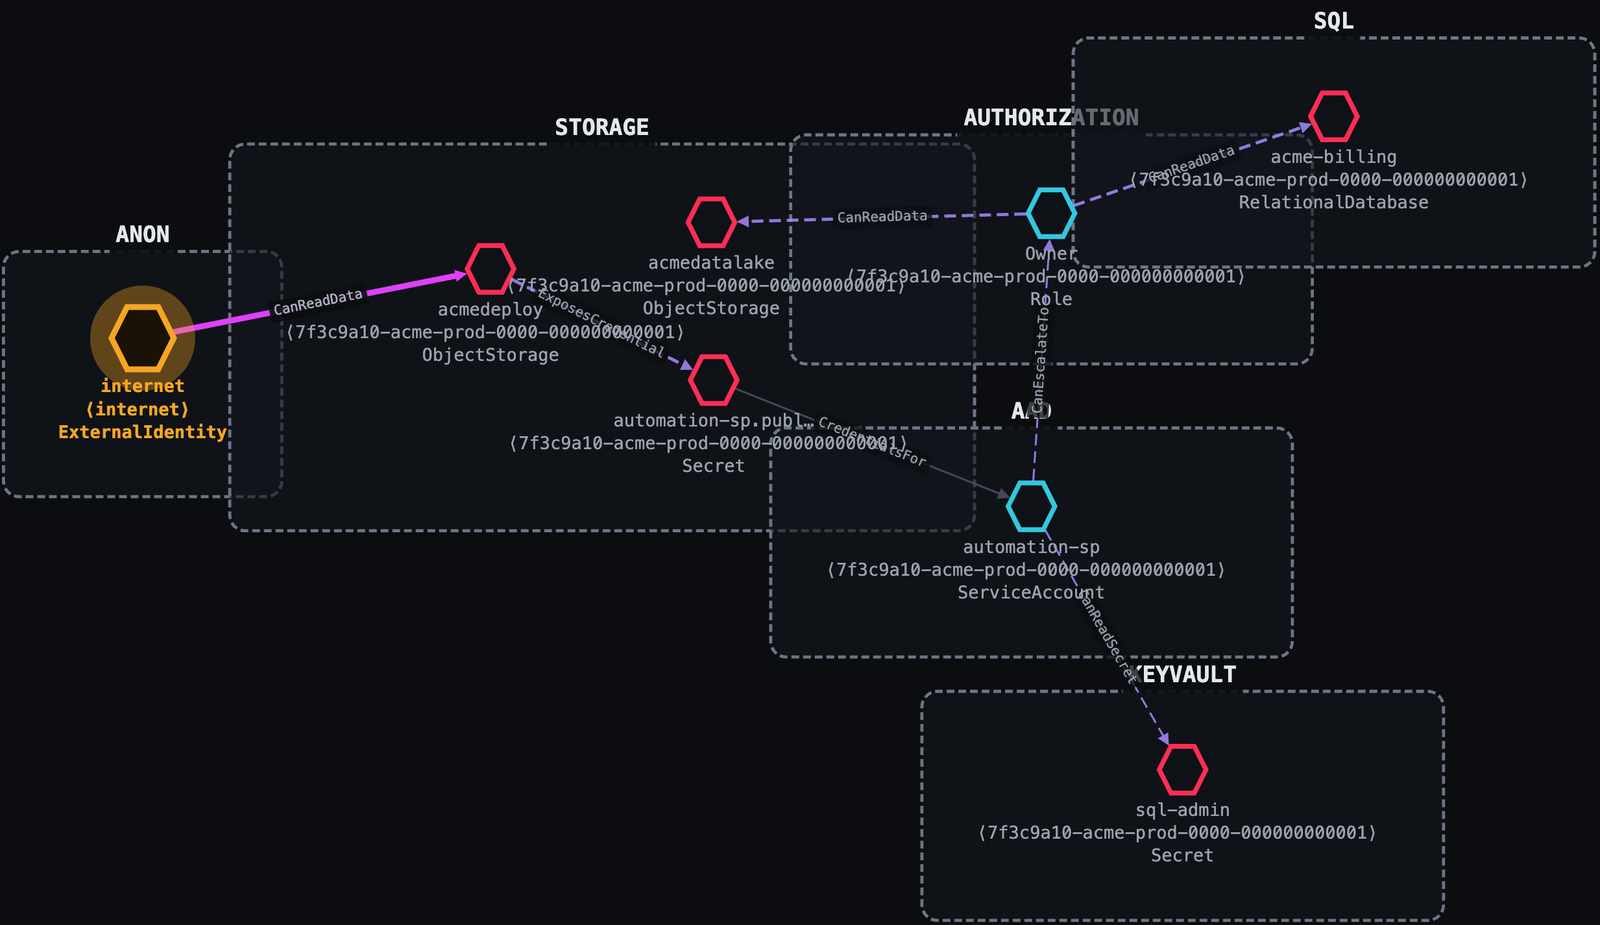 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 xiaoqimikko/netty-resolver-dns-check
Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable
 ivankovic/stop-bots
Automate stopping bad bots from accessing your server
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 nicmx/fort-validator
RPKI Relying Party and RTR server that validates BGP route origin authorizations and serves validated data to routers over the RTR protocol.
 xcoy0te/cve-2026-83548-checker
Non-intrusive detector for SonicWall SMA 1000 exposure to CVE-2026-83548/-83549 (version/patch-state check; no exploitation)