
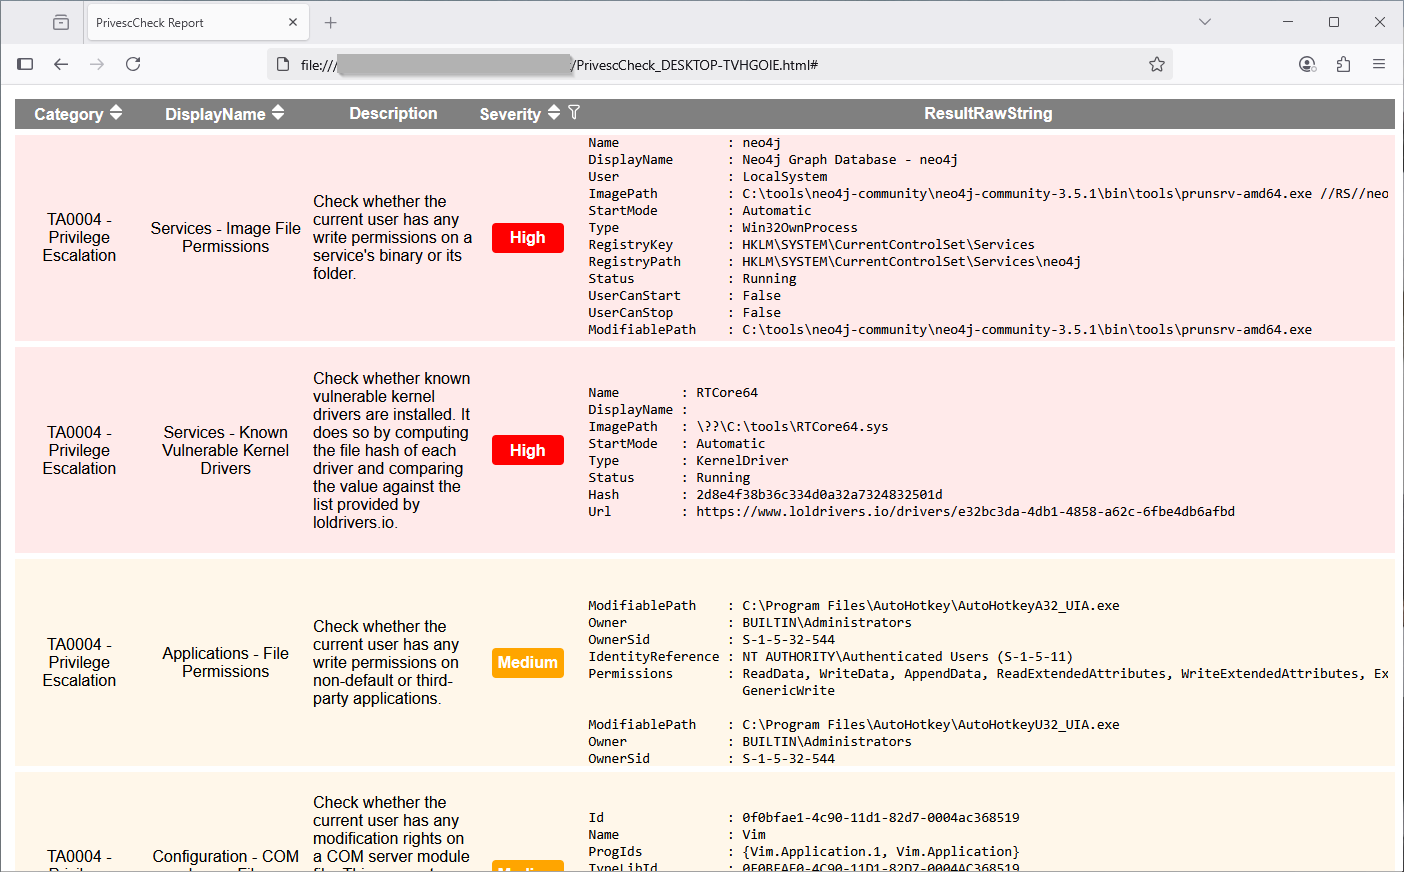
PrivescCheck
 itm4n/privesccheck
Privilege Escalation Enumeration Script for Windows
configuration-auditinginformation-gatheringpenetration-testing+3
4.0k5 days ago
itm4n/privesccheckPrivilege Escalation Enumeration Script for Windows
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
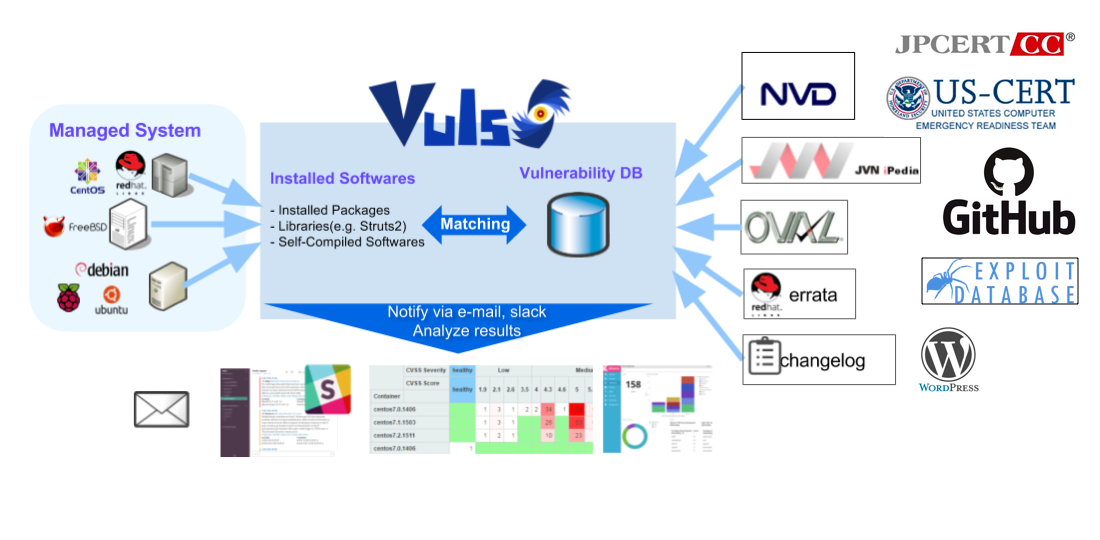 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 otissymbos/cve-2013-3900-wintrustverify
Powershell script that checks for cert padding in the Windows Registry and adds it if it does not exist. Meant to resolve the WinTrustVerify…
 vighnesh91/infrapulse-core
A high-fidelity, read-only internal network security assessment toolkit for Linux and Windows infrastructure. Employs a zero-mutation, default-deny…
 cloudquery/cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 microsoft/mxc
Policy-driven, layered isolation and containment
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
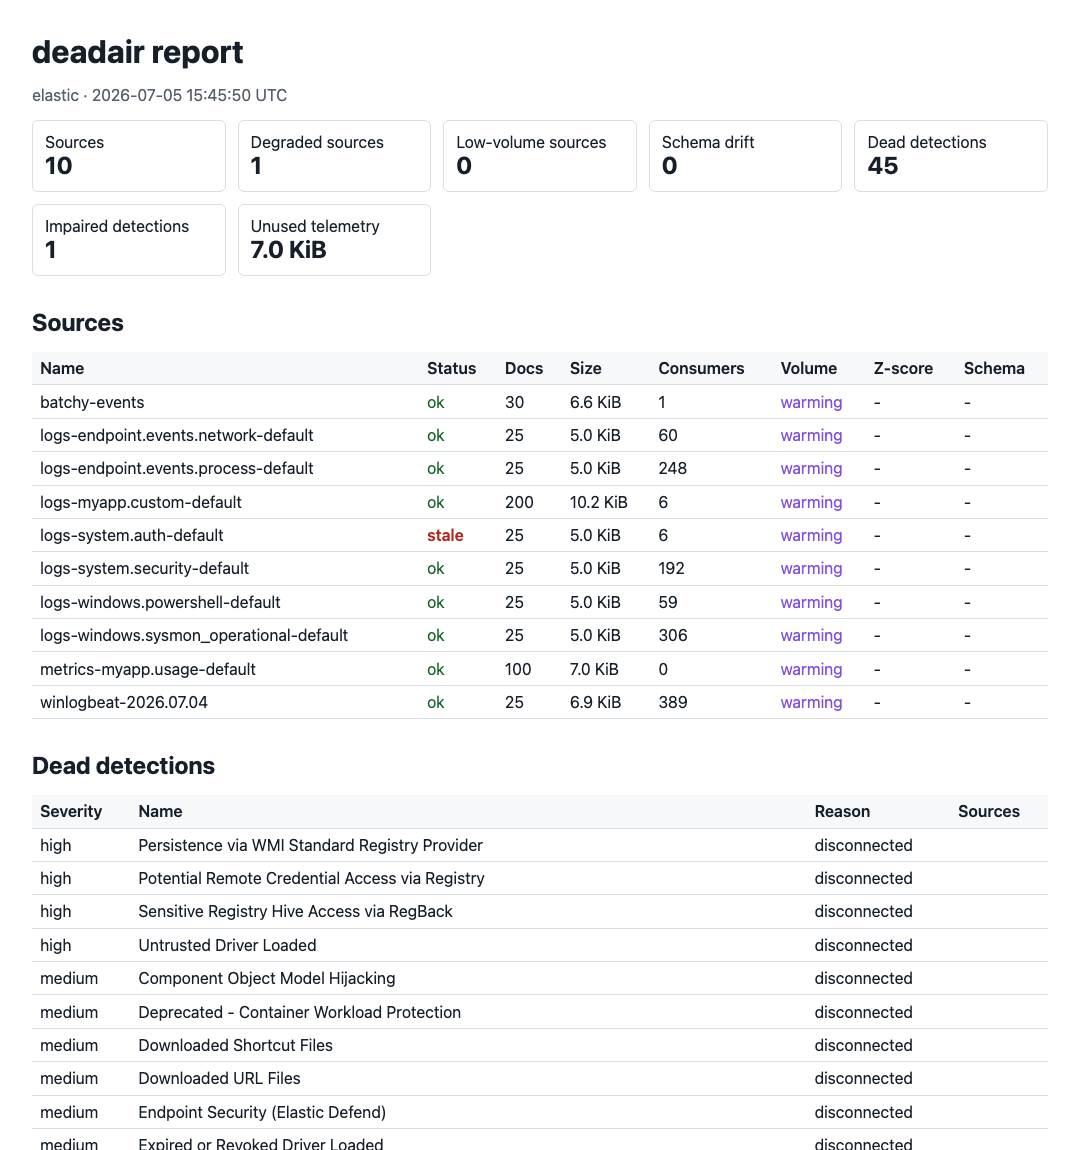 big-comfy/deadair
Finds the detection rules in your SIEM that are running blind
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 swiftonsecurity/sysmon-config
Commented Sysmon configuration template for high-quality Windows event tracing, threat hunting, and incident response. Designed as a tutorial for…