ndaal_public_auditd
Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Best-practice Linux Auditd rule set with 14,956 MITRE ATT&CK-mapped rules, Ansible deployment role, and lint/test tooling for security monitoring and…

Comprehensive set of over 1500 AppArmor profiles to confine Linux system processes, desktops, and services, with support for multiple distributions…

GitHub App to set and enforce security policies

Enumerate the permissions associated with AWS credential set

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

The Symfony PHP framework

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

A Linux Auditd rule set mapped to MITRE's Attack Framework

Best Practice Auditd Configuration

provides a Firewall Manager API designed to centralize and streamline the management of firewall configurations

This chef cookbook provides security configuration for mysql.

Trace every shell environment variable to its exact file and line origin. Audit shell configs for dead entries, duplicates, and orphaned files across…

Kubernetes RBAC static analysis & visualisation tool

Blue Team detection lab created with Terraform and Ansible in Azure.

MDE relies on some of the Audit settings to be enabled

Terraform module to set up your AWS account with the secure baseline configuration based on CIS Amazon Web Services Foundations and AWS Foundational…

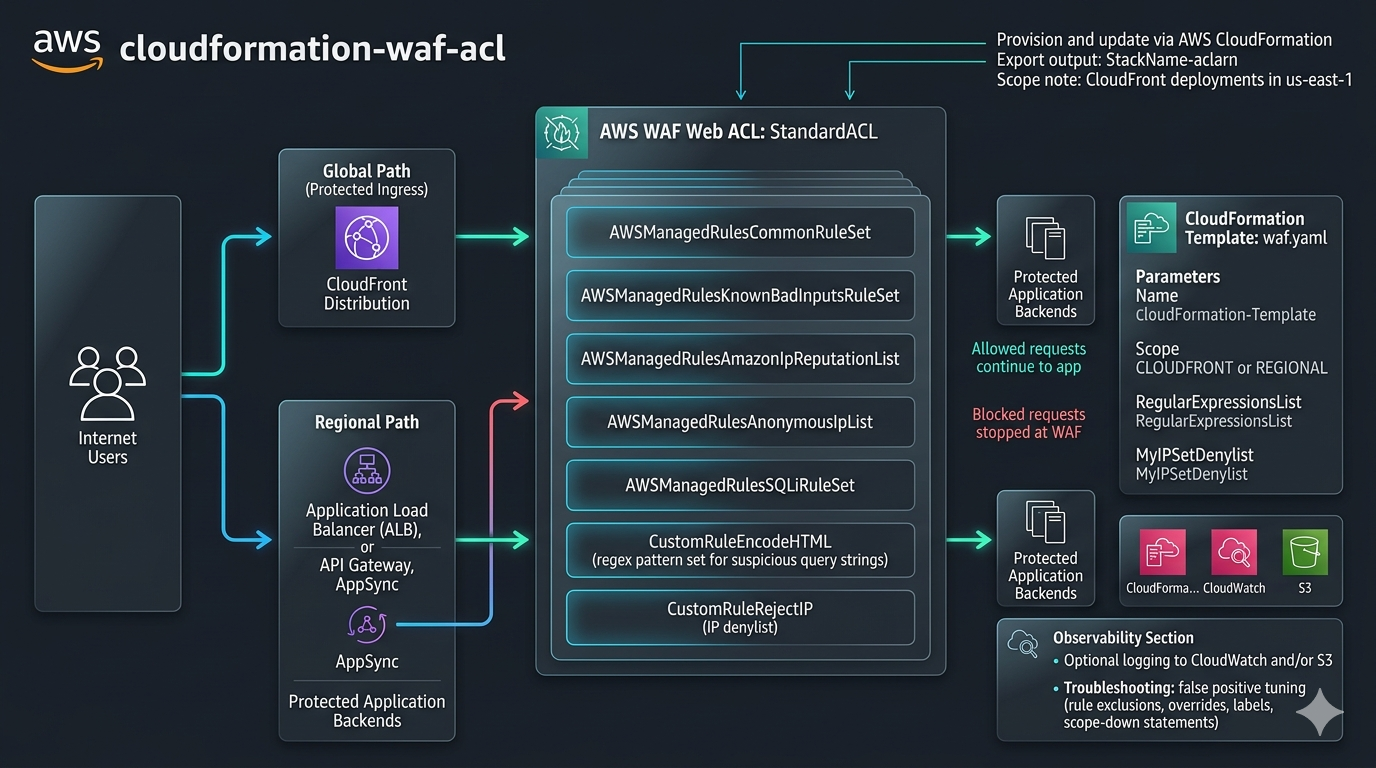
An AWS CloudFormation template used to provision and manage AWS WAFv2 resources, including a Web ACL, managed rule groups, a custom regex pattern…

The remediation script should set the reg entries described in https://msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36884 . The detection…